
What are GitHub organization-level code security configurations primarily used for?
Select an answer to reveal the explanation.
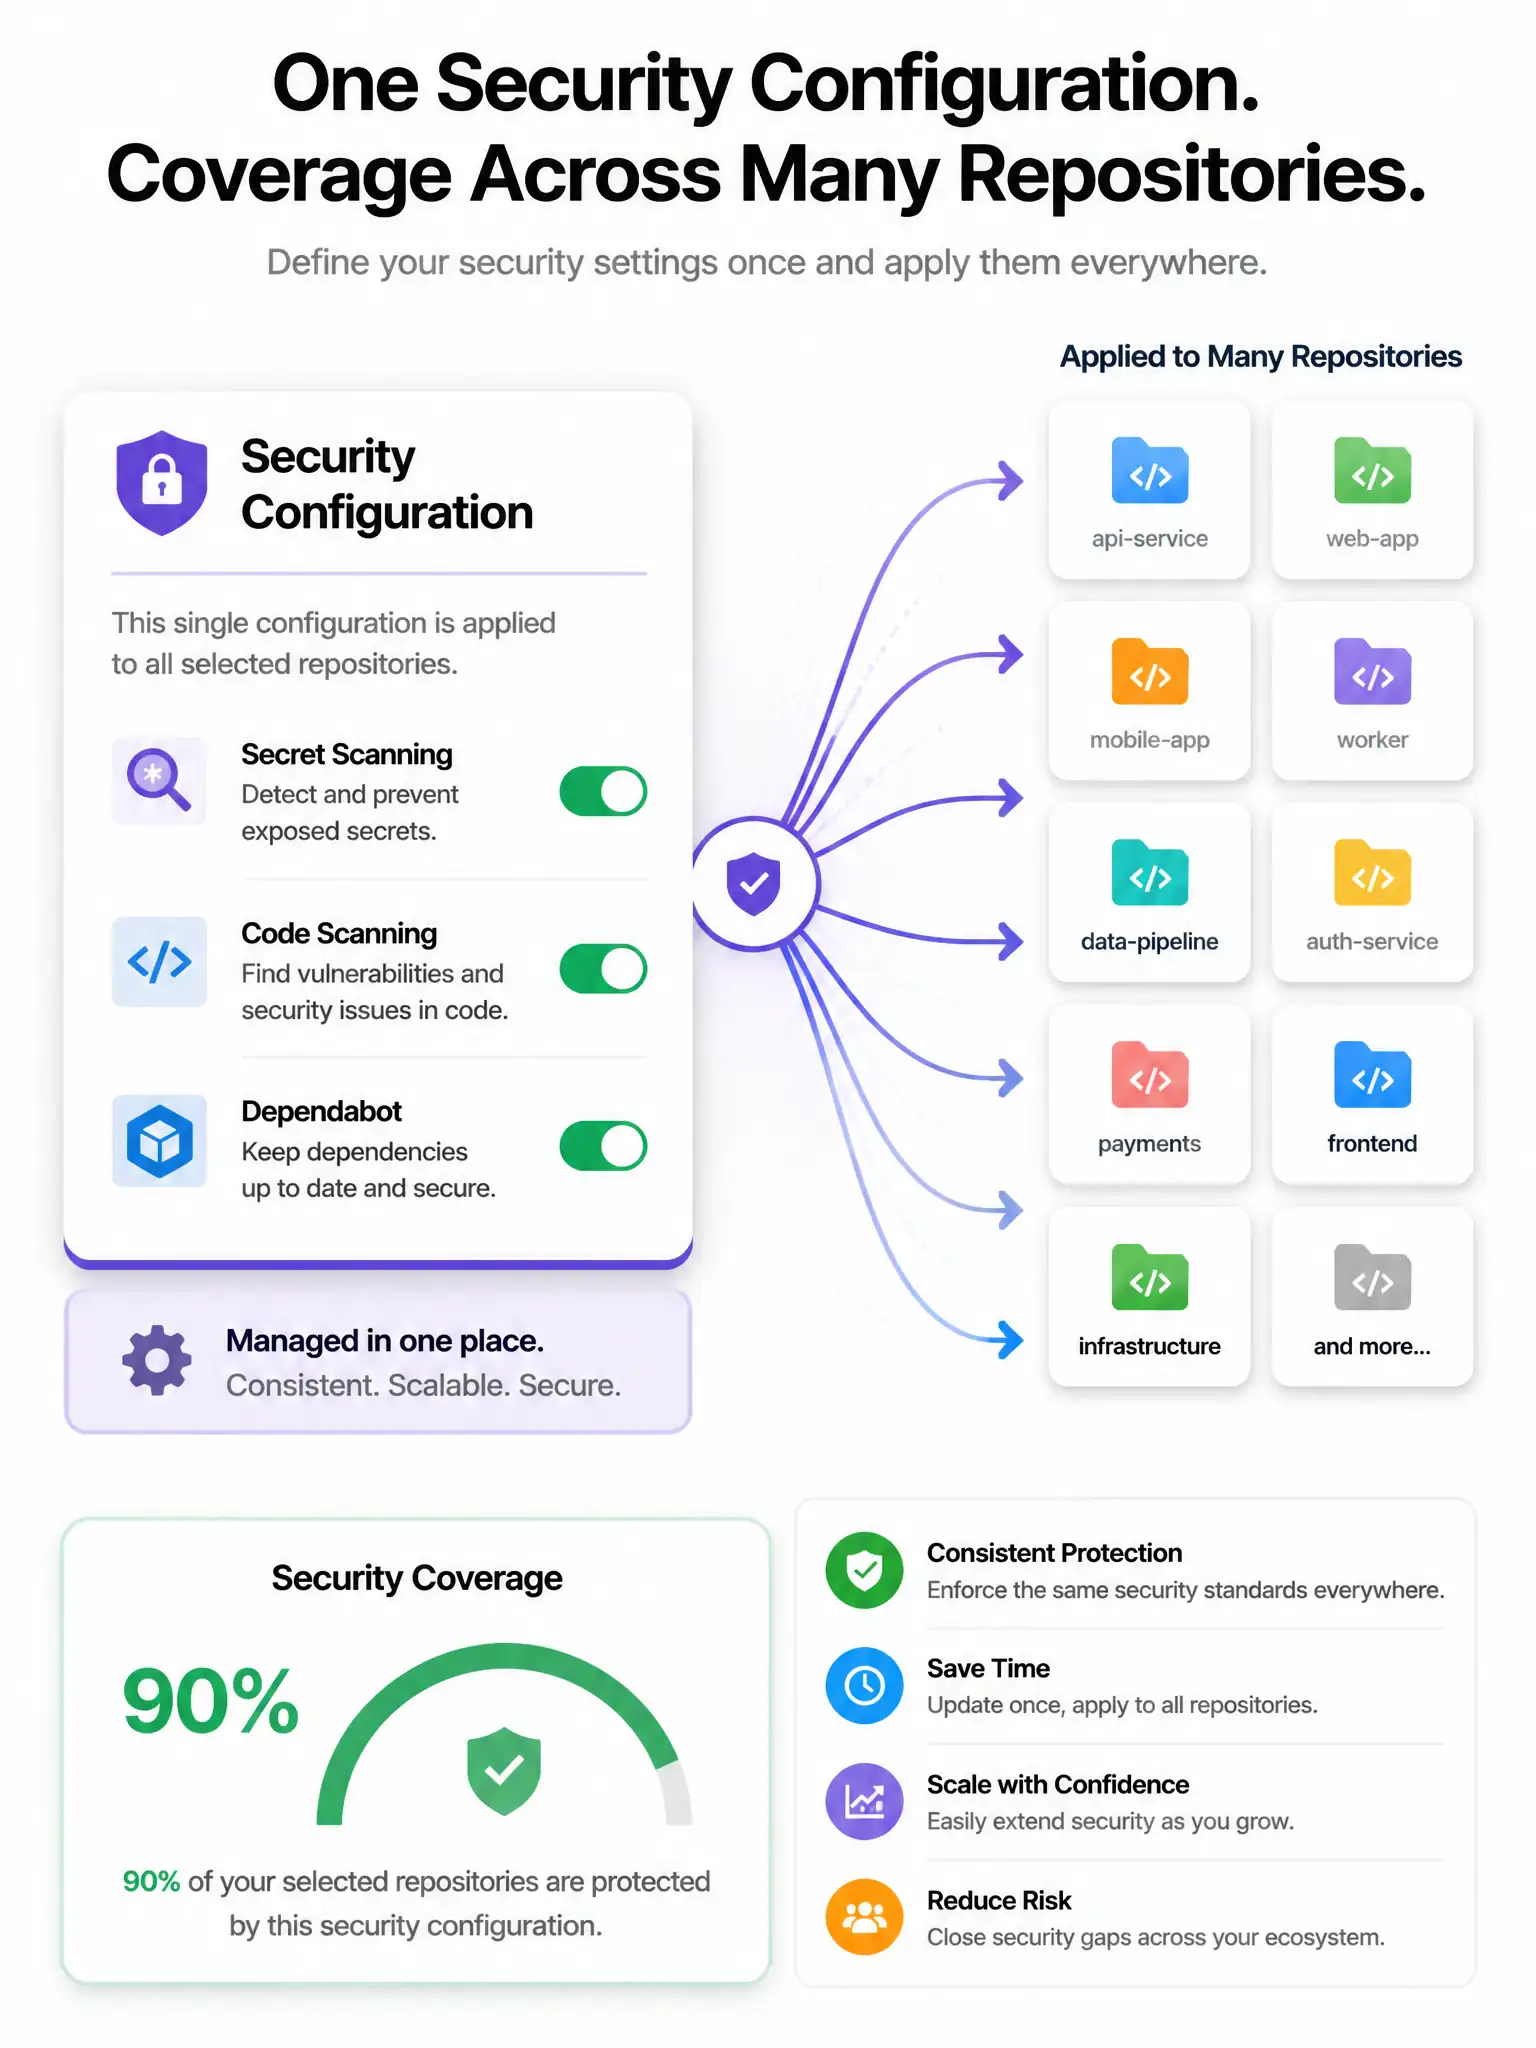
Short Explanation
Security configurations are the 'apply this security posture to a bunch of repos' control plane — code scanning, secret scanning, Dependabot-related knobs, and friends — without clicking fifty repo settings pages. You use them to enable Advanced Security features consistently at org scale. They aren't for branch renames, Pages billing, or SMTP.
Full Explanation
The correct answer is applying consistent Advanced Security-related feature enablement across many repositories. Organization security configurations let administrators define a security posture (for example secret scanning, push protection, code scanning, Dependabot options as available) and attach it to repositories at scale, including enforcement patterns depending on product capabilities. The option about replacing all branch names with security-themed defaults only is incorrect because branch naming is not the purpose of org security configurations. The option about billing only for GitHub Pages bandwidth is unrelated billing. The option about configuring SMTP relay hosts for GHES is a GHES appliance concern, not org security configurations. Use configurations to establish baselines for production repos, monitor coverage gaps in security overview, and separate experimental repos if needed.