
When SAML single sign-on is enforced for an organization, what additional step may users face when performing sensitive account or organization actions?
Select an answer to reveal the explanation.
Short Explanation
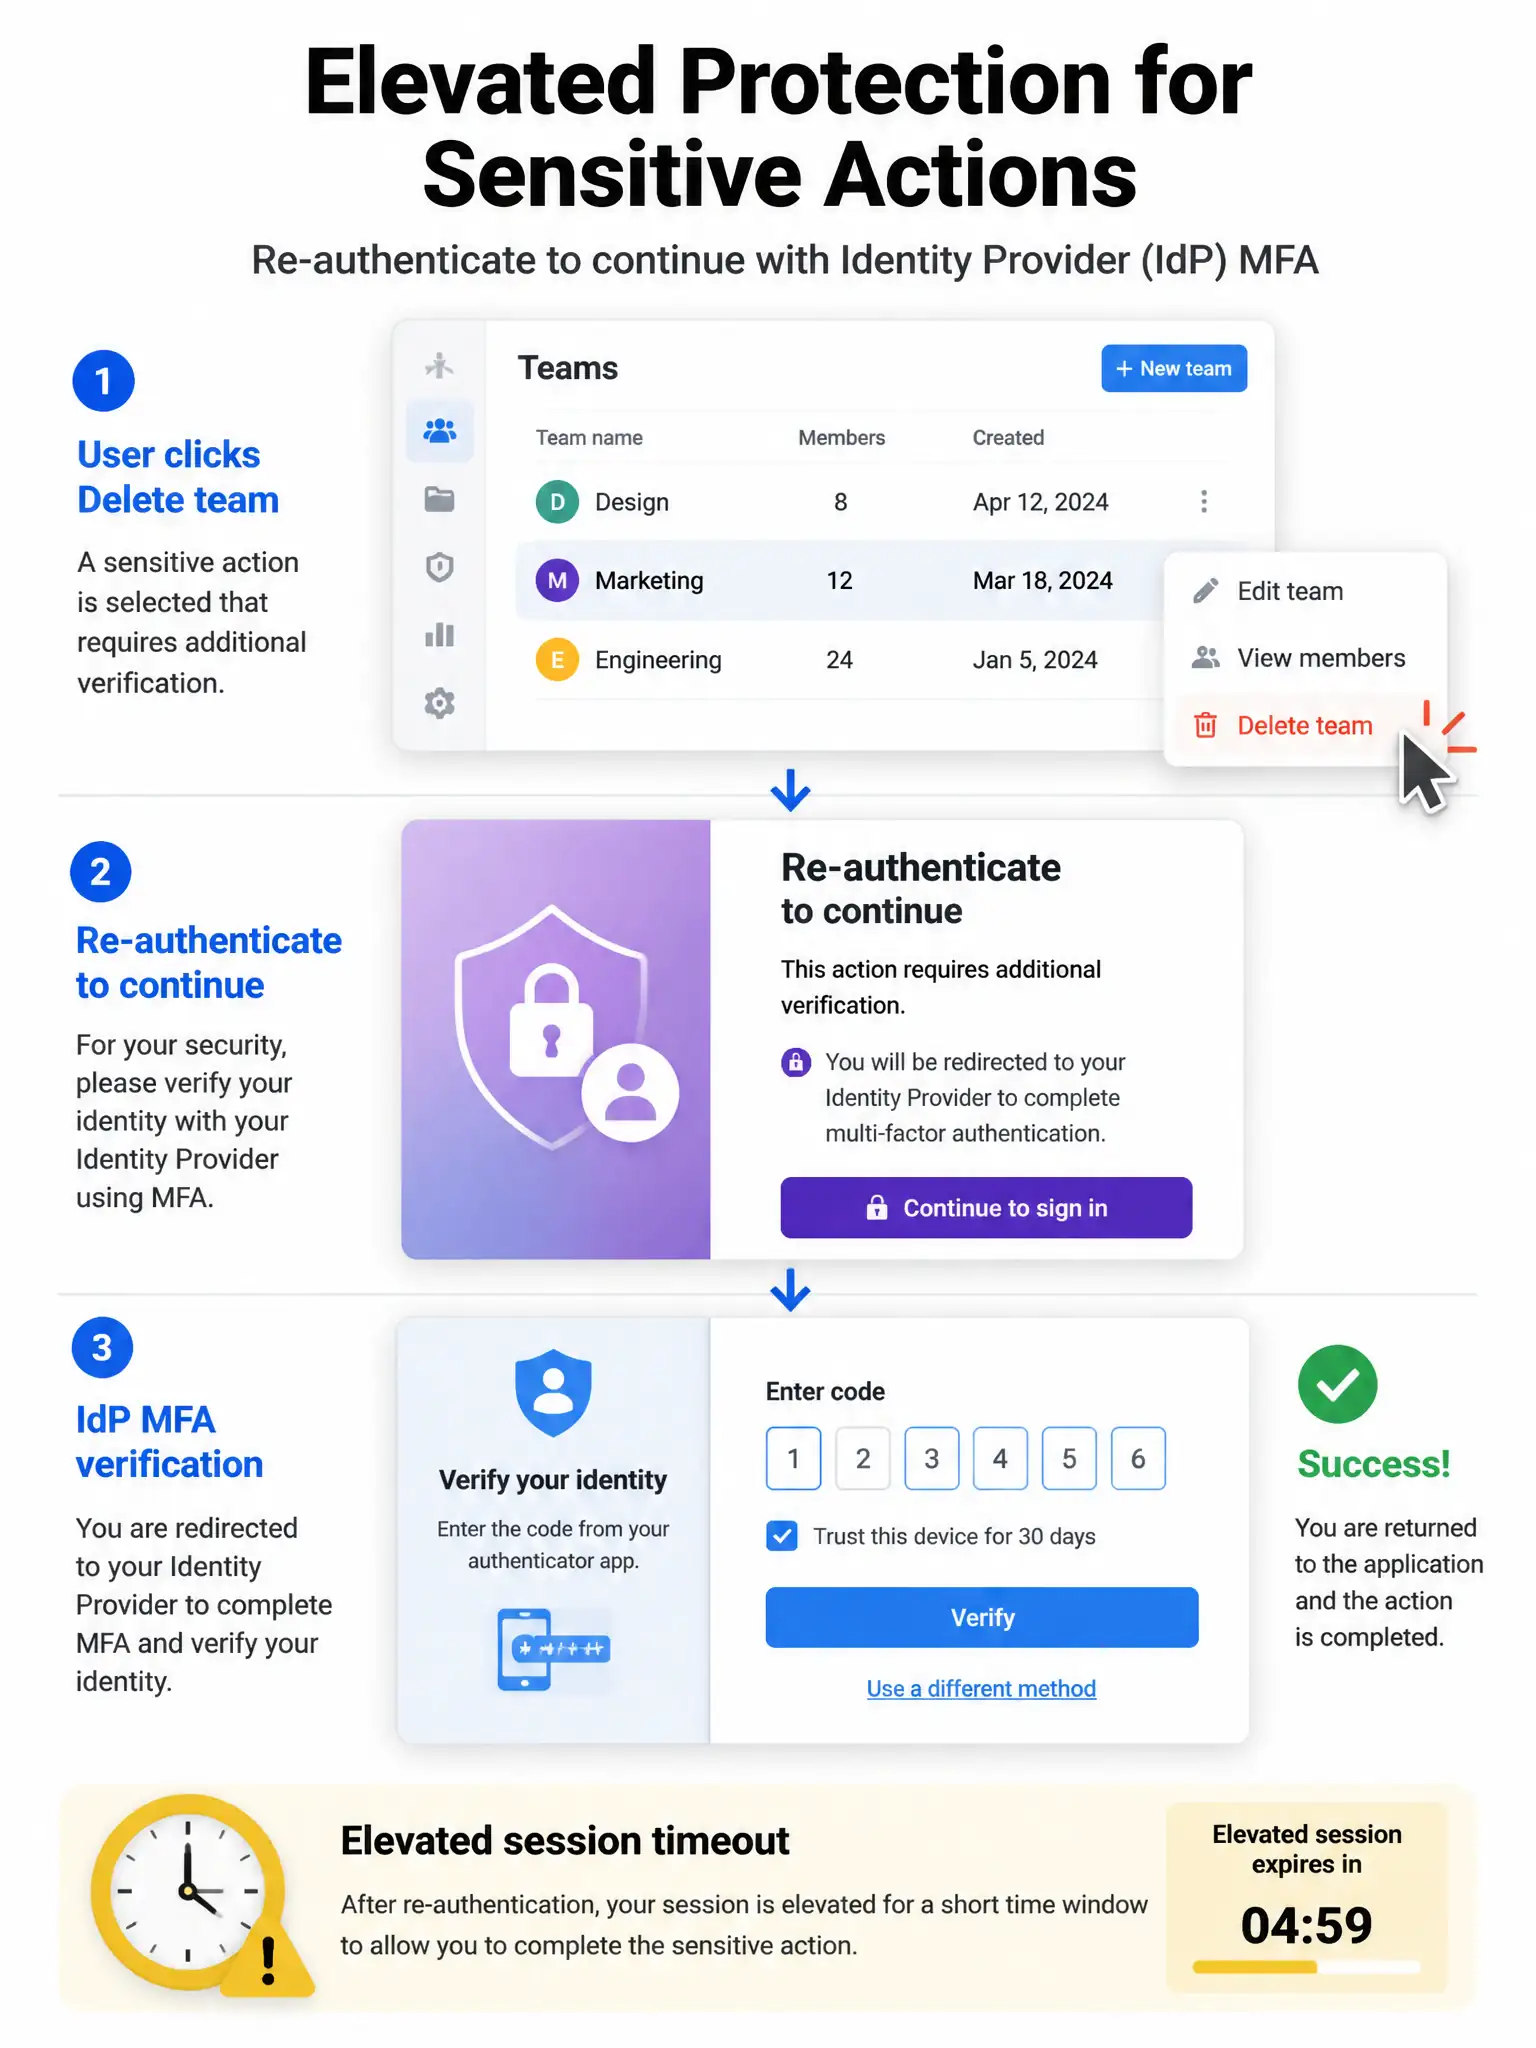
When you do sensitive account or organization actions, you may have to re-authenticate or confirm your SAML session. It's a prove-it's-you check, not hourly token deletion or team loss.
Full Explanation
The correct answer is that users may need to re-authenticate or confirm an elevated SAML session before privileged actions. GitHub uses elevated session / sudo-style challenges and SAML-related re-authentication patterns so that high-impact changes require a fresh proof of identity. The claim that GitHub permanently deletes personal access tokens each hour is incorrect as standard behavior. The claim that all repositories convert to internal visibility automatically is unrelated to SAML enforcement side effects. The claim that users lose team membership until a support ticket is filed is incorrect; support tickets are not required for routine re-authentication. Admins should ensure IdP session lifetimes and MFA policies align with user experience expectations and document break-glass owner accounts carefully.