
What does uploading an SSH certificate authority (CA) to a GitHub organization enable administrators to do?
Select an answer to reveal the explanation.
Short Explanation
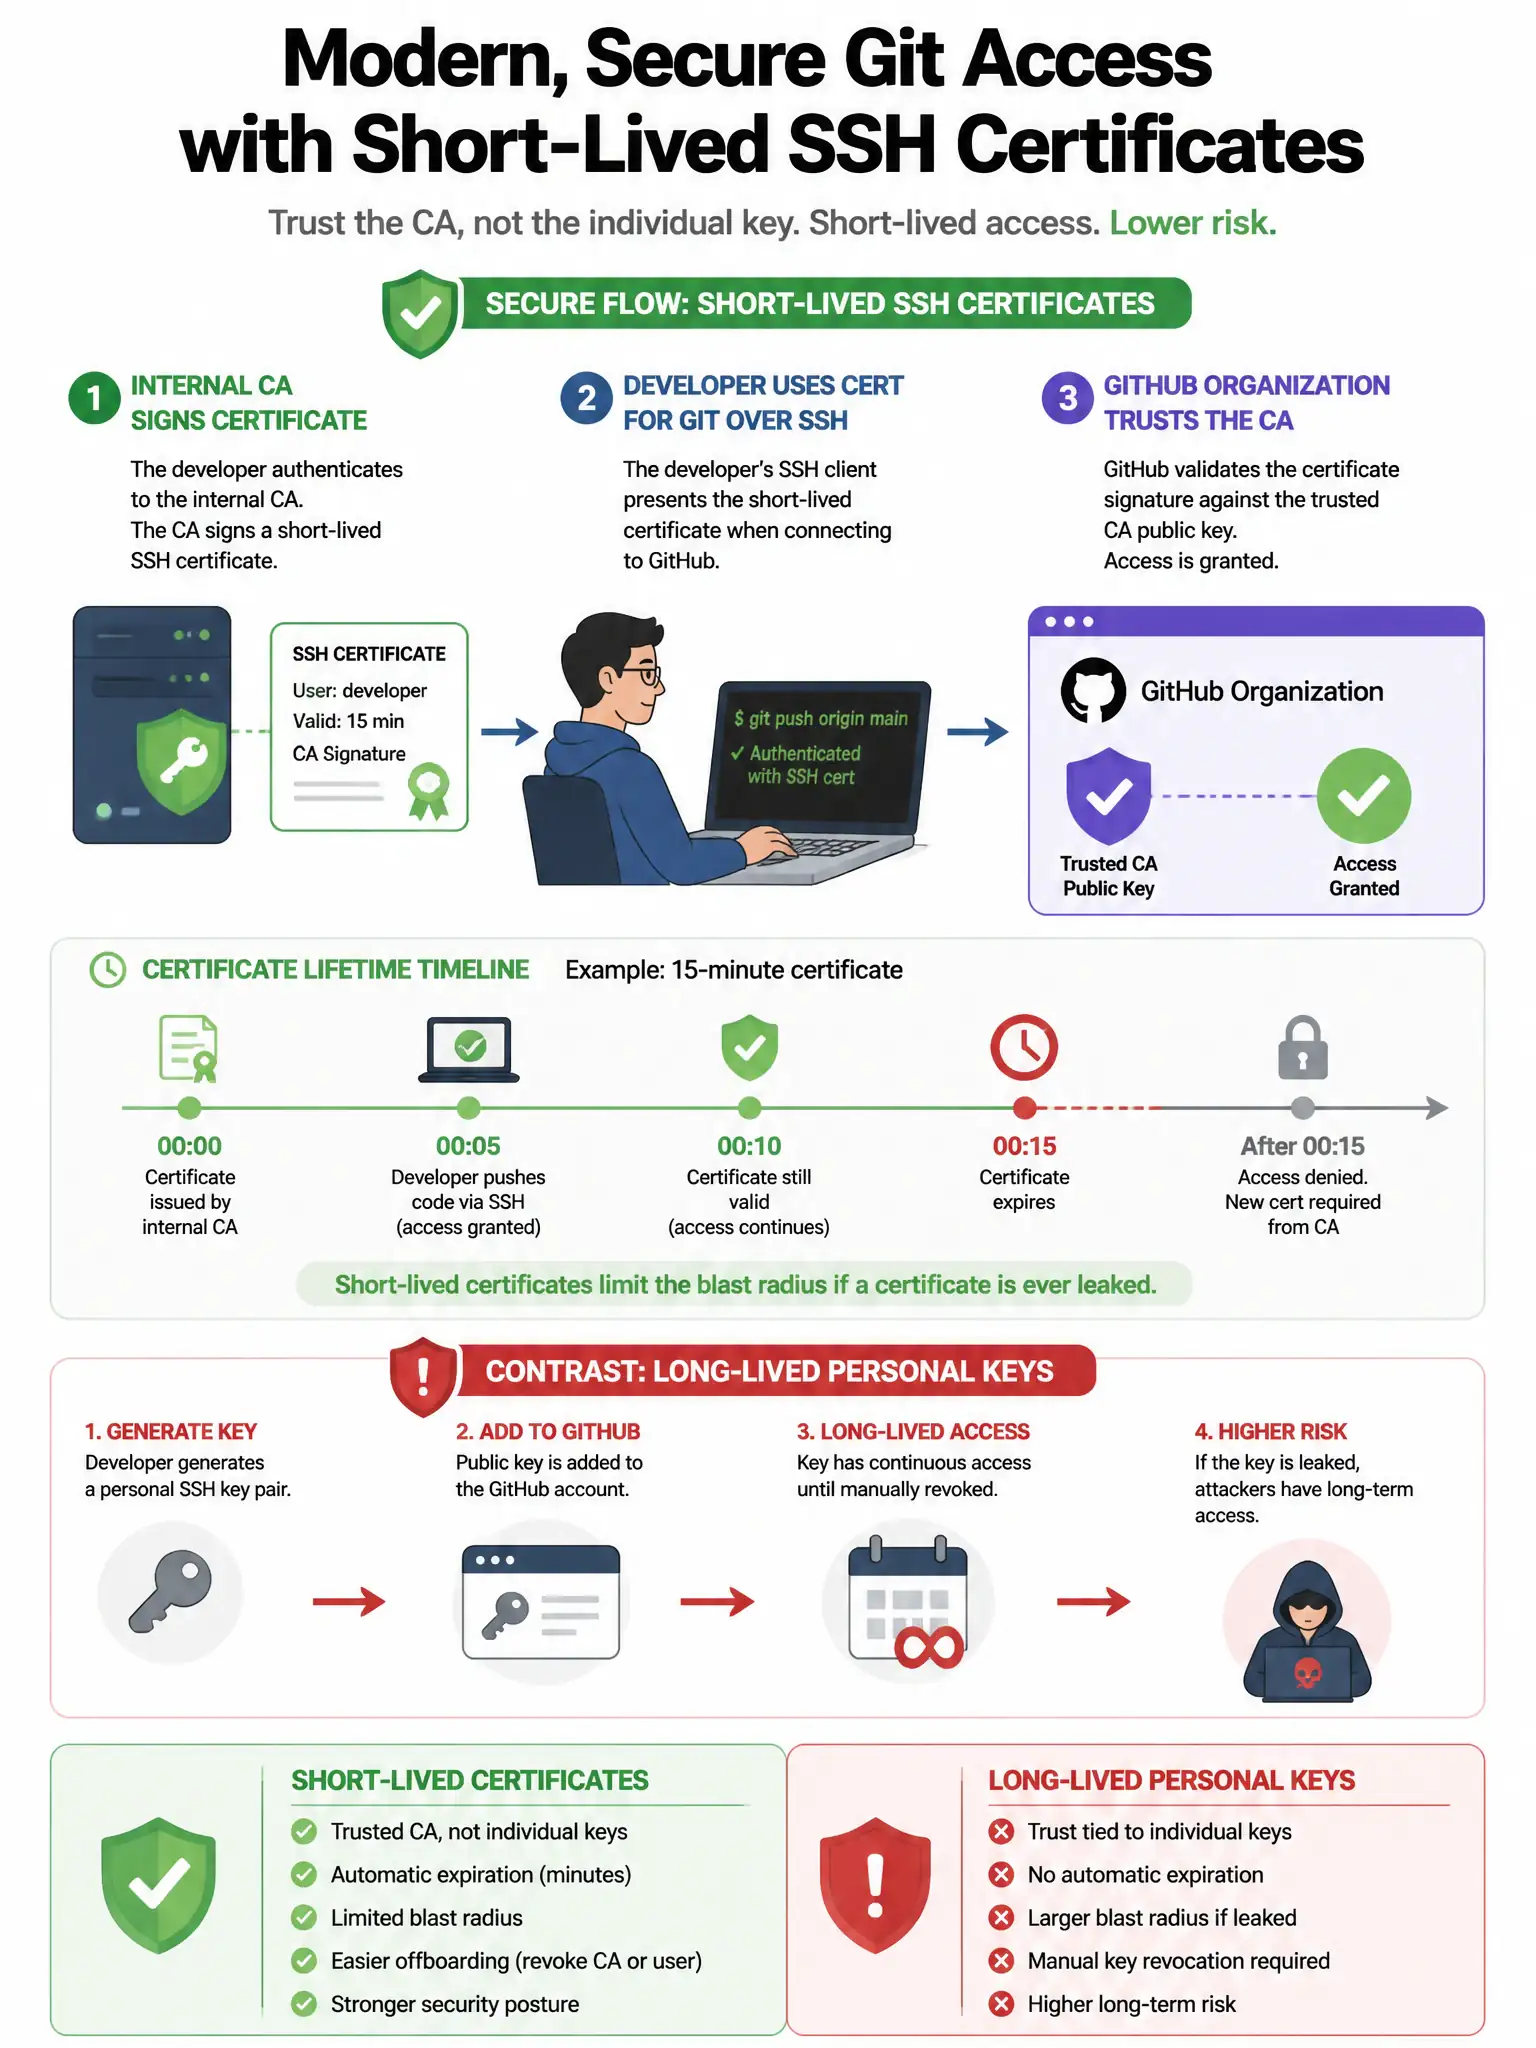
Uploading an SSH CA lets you issue short-lived SSH certificates for members instead of making everyone upload long-lived personal keys. It’s about central key lifecycle, not making repos public, swapping GHES TLS certs, or disabling audit logs.
Full Explanation
The correct answer is issuing short-lived SSH certificates that members use instead of uploading personal SSH public keys. Organization SSH certificate authorities let enterprises integrate with internal certificate issuance so Git SSH authentication uses managed, expiring credentials and supports central key lifecycle. Forcing all repositories to become public is unrelated. Replacing HTTPS TLS certificates on the GHES Management Console automatically confuses user Git SSH CAs with appliance TLS certificates. Disabling audit logging for SSH operations is false; SSH CA usage does not disable auditing. Operationally, protect the CA private key offline or in HSM-backed systems, monitor issuance, pair issuance with short TTLs and automated issuance from your identity platform, and revoke by rotating CAs when compromise is suspected.