
An enterprise wants to use OpenID Connect (OIDC) for enterprise SSO instead of SAML. What is a primary administrative characteristic of OIDC enterprise SSO on GitHub?
Select an answer to reveal the explanation.
Short Explanation
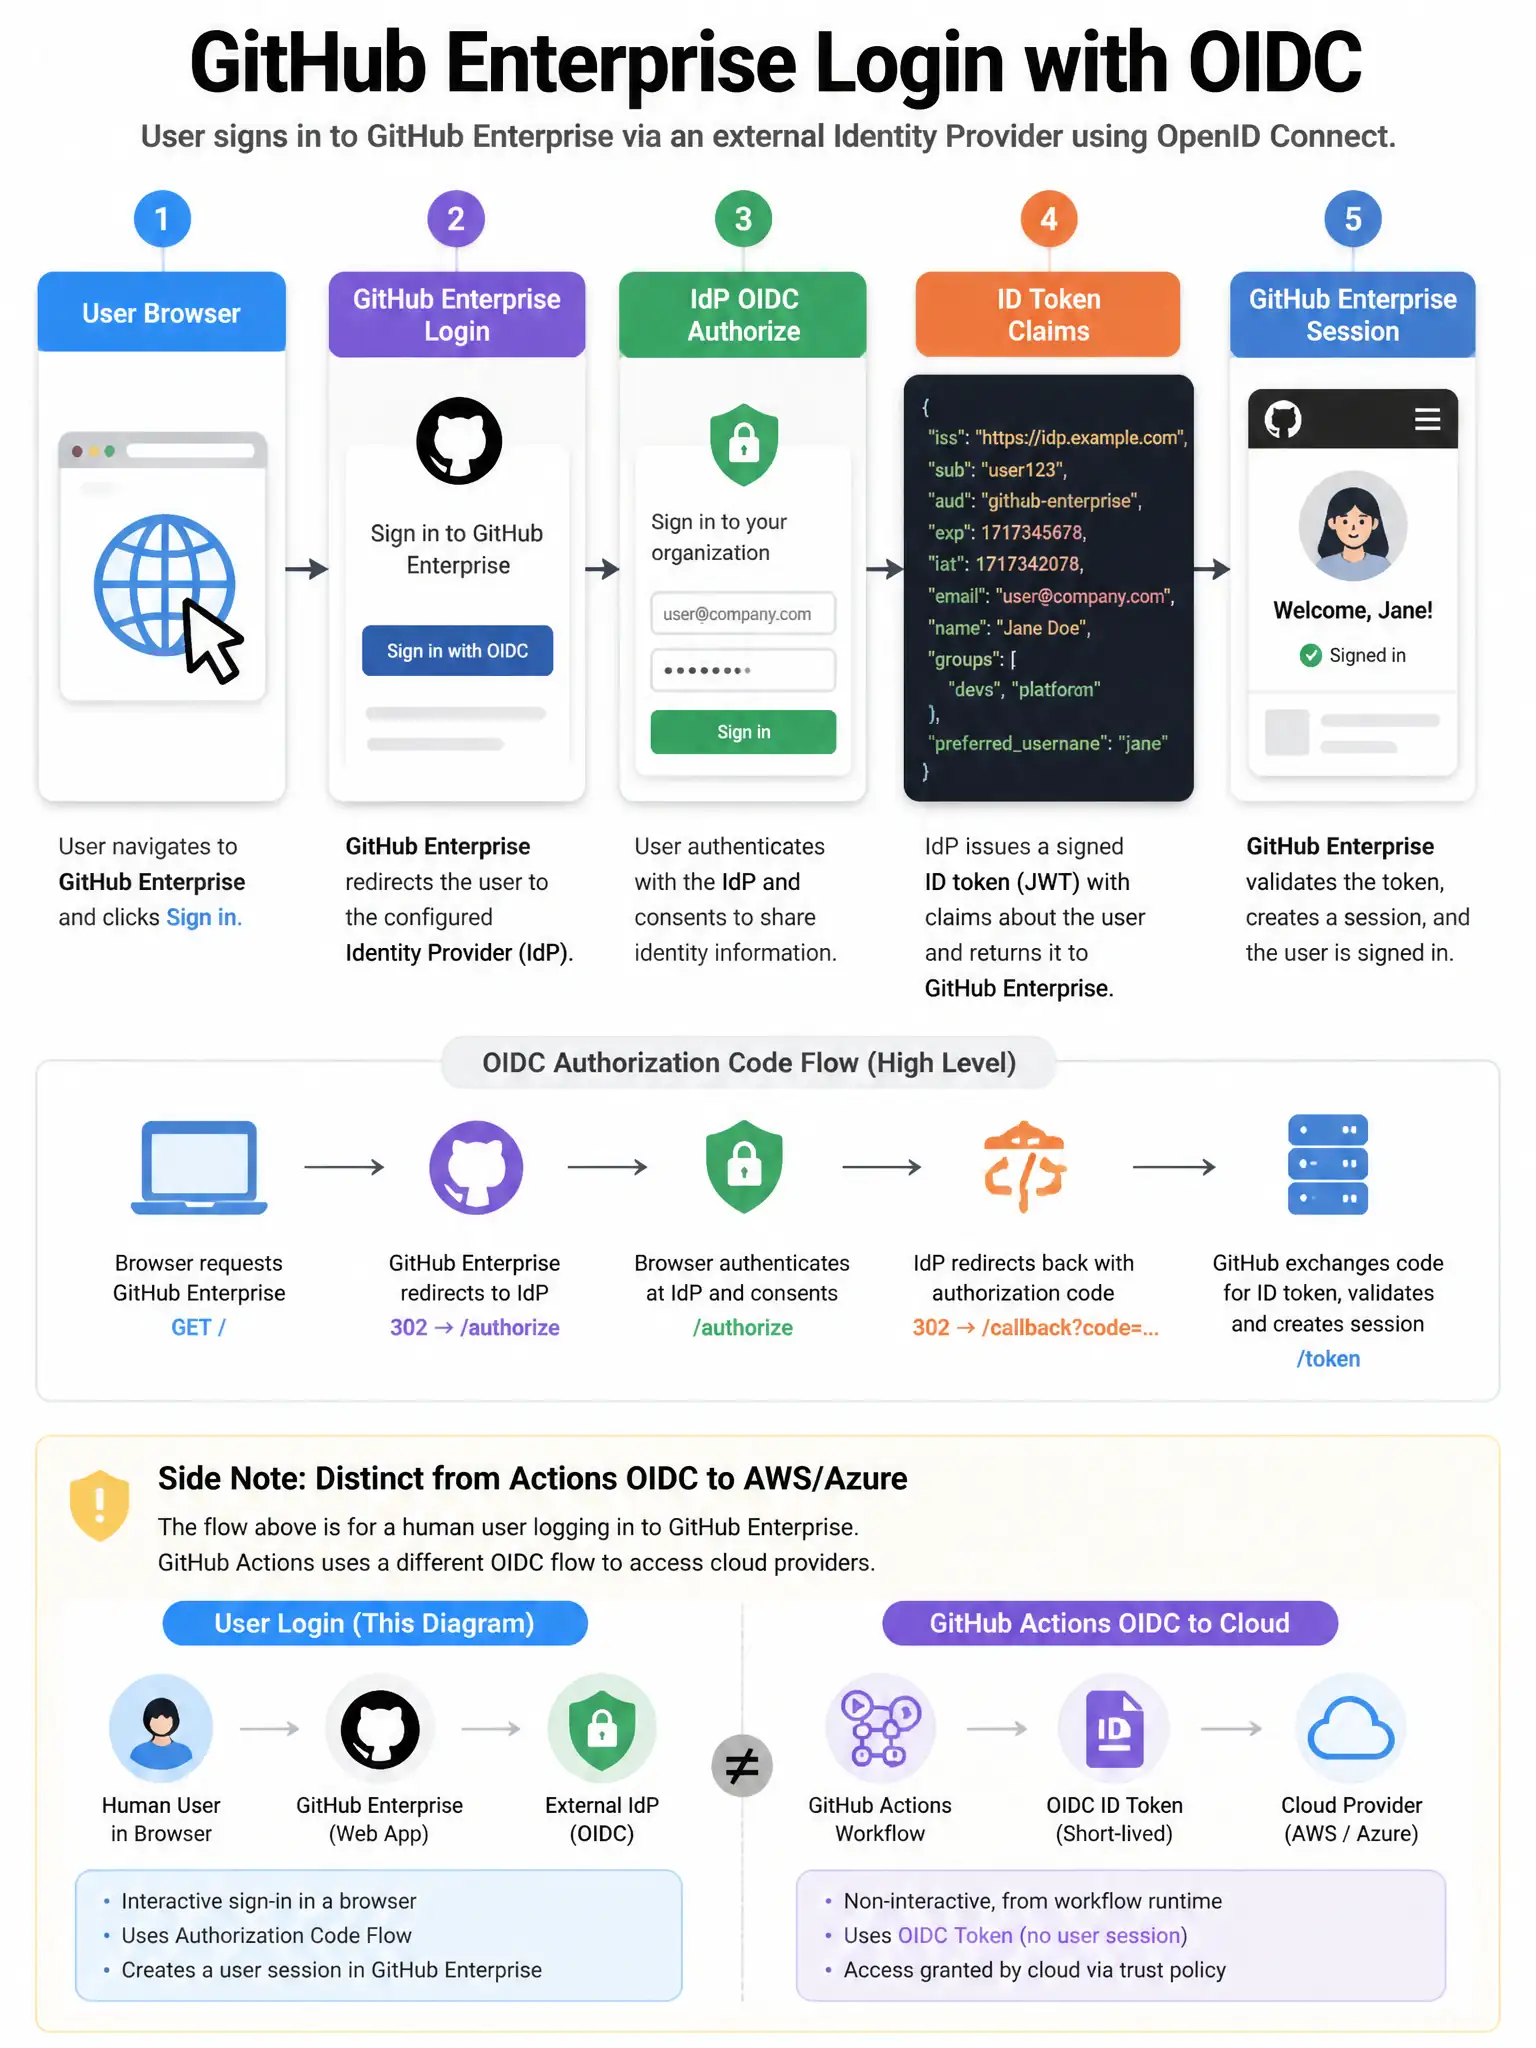
You get OIDC enterprise SSO by federating login through your IdP with OAuth/OIDC instead of SAML assertions. It’s still for people signing in under enterprise policy, not just Actions runners. You still handle org membership, GitHub Apps, and authorization separately.
Full Explanation
The correct answer is that OIDC enterprise SSO federates interactive enterprise authentication via OIDC with an identity provider rather than relying on SAML assertions for that enterprise login path. Enterprises choose OIDC or SAML based on IdP capabilities and security standards; both are authentication federation options at enterprise scope when supported for the account type. The option saying it can only authenticate GitHub Actions runners is wrong because it confuses enterprise user SSO with GitHub Actions OIDC for cloud provider roles. The option saying it requires disabling all GitHub Apps permanently is false; GitHub Apps remain independent. The option saying it replaces the need for any organization membership is false; authentication method does not eliminate organization membership models. Admins should pilot claims mapping, session behavior, and break-glass access before forcing the enterprise to OIDC-only login.