
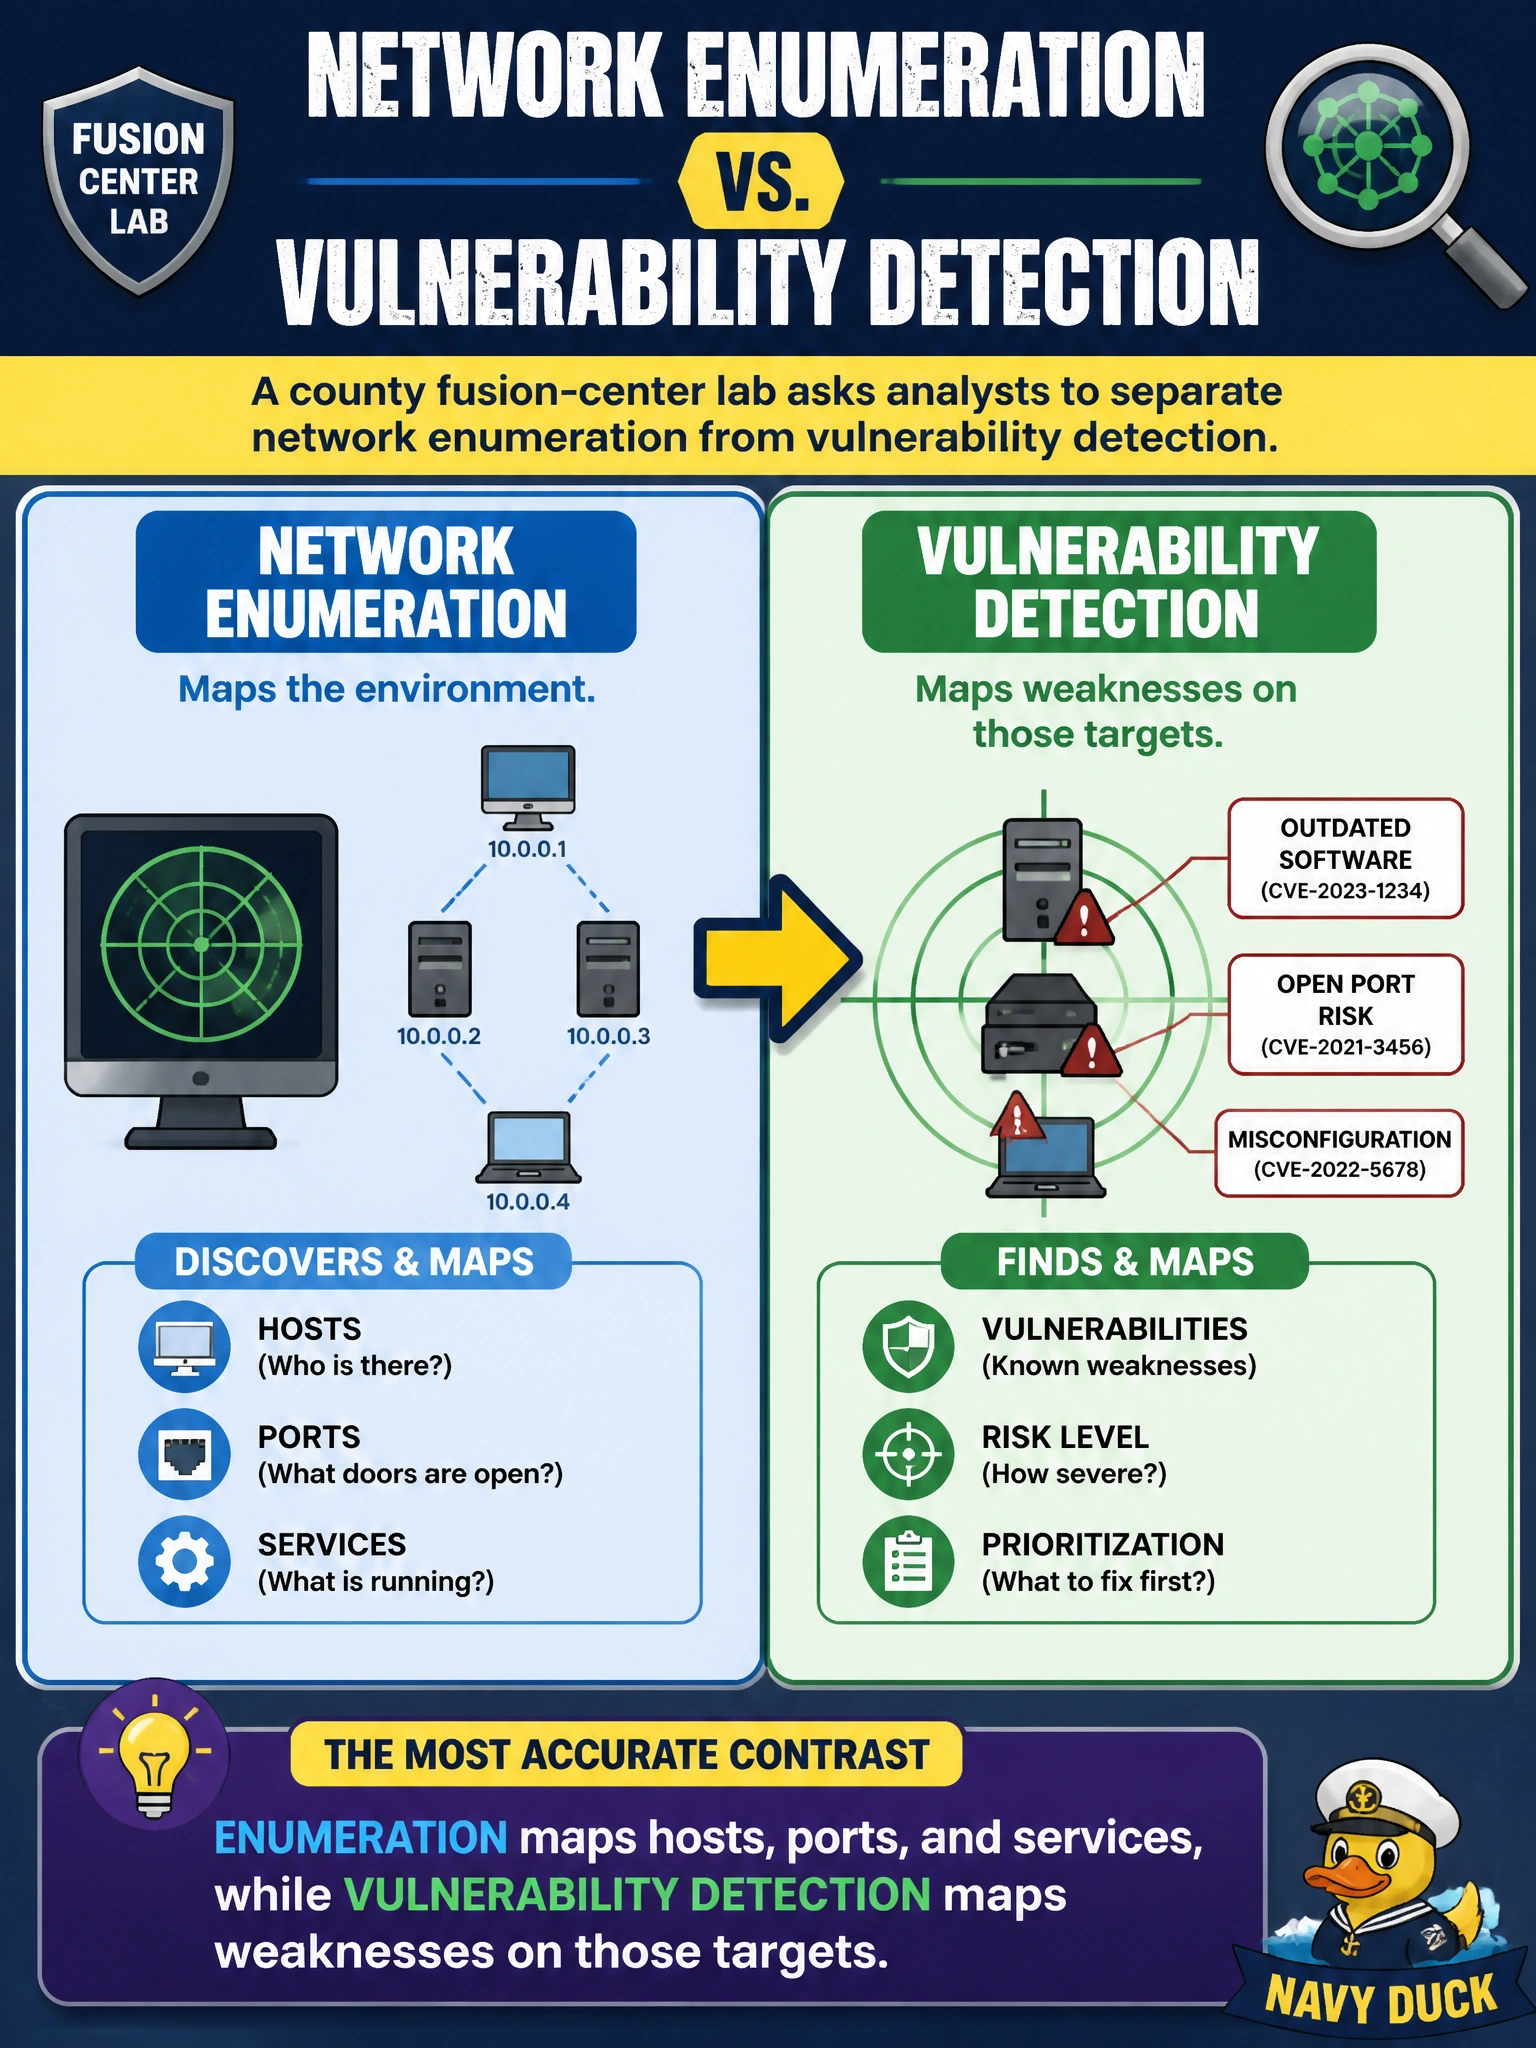
A county fusion-center lab asks analysts to separate network enumeration from vulnerability detection. Which contrast is most accurate?
Select an answer to reveal the explanation.
Short Explanation
Enumeration is the 'who is listening where' map. Vulnerability detection is the 'what is broken on those doors' list. Mixing them up is like confusing a street directory with a building-inspection report.
Full Explanation
For a county fusion-center lab, separating network enumeration from vulnerability detection clarifies what each phase contributes to municipal situational awareness. Enumeration maps hosts, ports, and services—the attack-surface directory of what is listening and where. Vulnerability detection then maps weaknesses on those targets—missing patches, insecure configurations, exposed services that scanners or authenticated checks can score. Keeping the contrast accurate prevents fusion analysts from mistaking a service inventory for a risk inventory or treating a CVSS list as a complete network map.
The option that says enumeration only rates CVSS scores while vulnerability detection only lists open ports reverses the concepts and would mis-train analysts on both tooling and reporting. Claiming enumeration replaces vulnerability scanners when AI agents summarize Nmap XML confuses artifact summarization with detection methodology: an AI write-up of port data still is not a vulnerability assessment. Saying vulnerability detection maps hosts and services while enumeration maps missing patches also swaps the definitions and would produce incorrect lab procedures and ROE language.
Exam caveat: vendors and curricula sometimes blur recon terminology. On GOAA-aligned items, prefer the operational split—enumeration discovers and describes reachable assets and services; vulnerability detection evaluates weakness on that map—regardless of whether an AI agent later drafts the narrative.
Operational check: in fusion-center runbooks, label outputs explicitly (enumeration inventory vs. vulnerability findings), require that vuln tickets cite enumerated targets, and reject AI summaries that claim CVEs for hosts that never appeared in the enumeration baseline.