
A transit architecture review asks which AI platform pattern best supports private on-prem inference for an OT-adjacent security lab. Which answer fits?
Select an answer to reveal the explanation.
Short Explanation
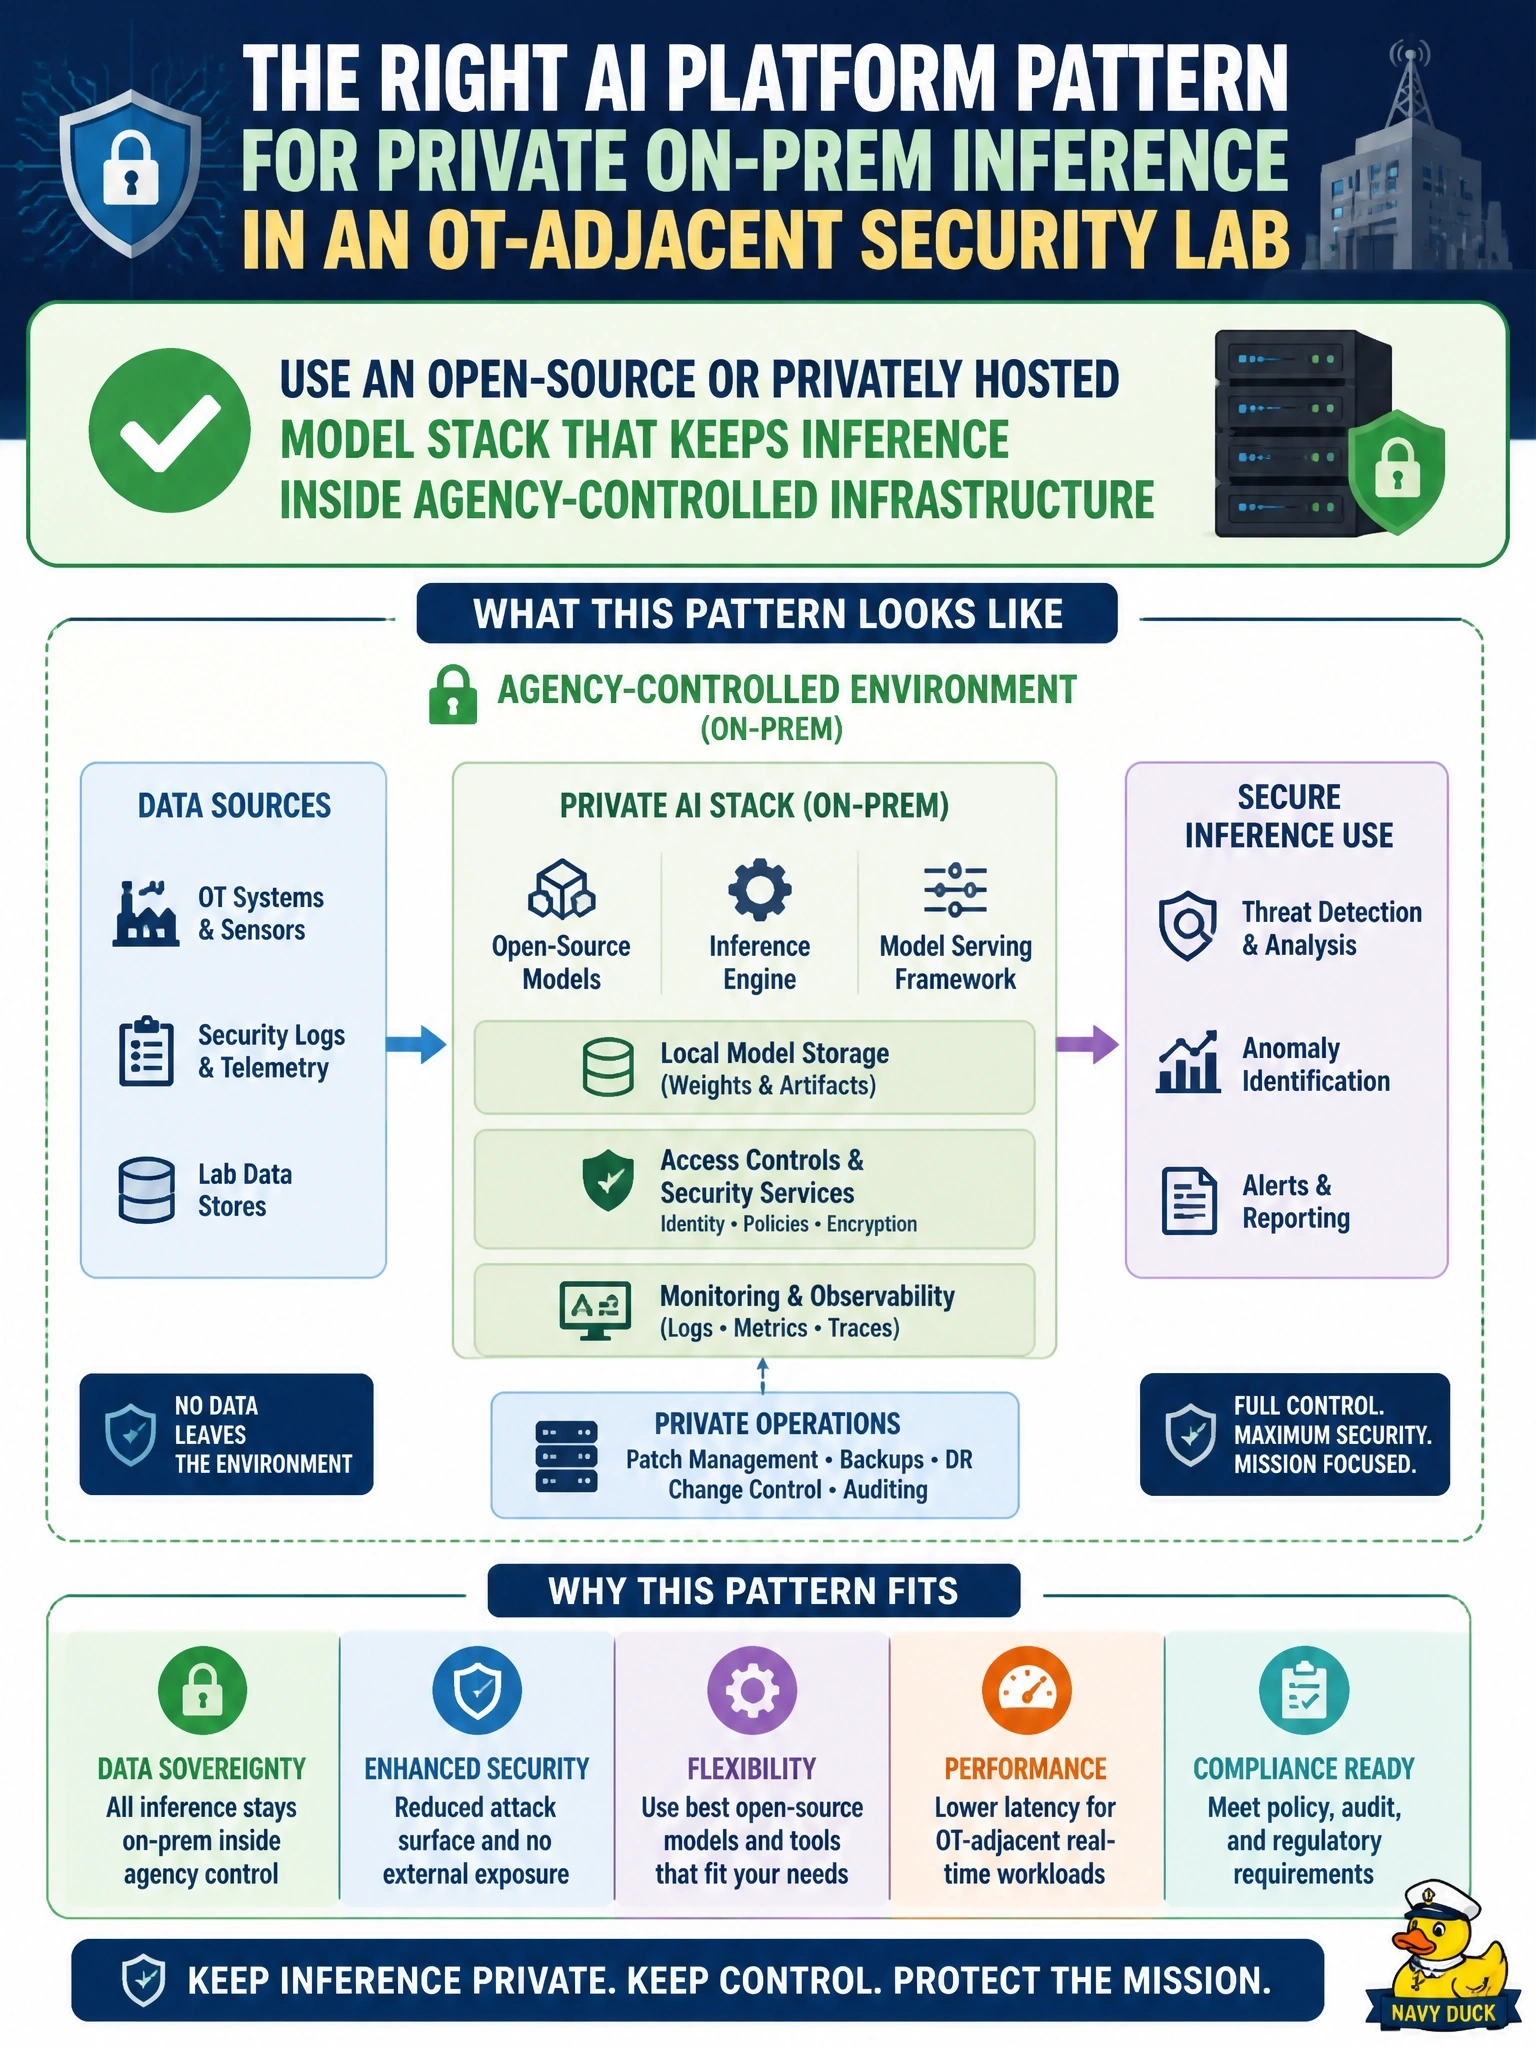
OT-adjacent labs usually want the brains in the building, not on a random public chatbot. You want private or open-source on-prem inference so sensitive diagrams stay off the open internet.
Full Explanation
A transit architecture review asking which AI platform pattern best supports private on-prem inference for an OT-adjacent security lab should select an open-source or privately hosted model stack that keeps inference inside agency-controlled infrastructure. OT-adjacent diagrams, PLC references, and defensive configs must not ride consumer chat paths; private inference preserves confidentiality and aligns with segmented lab design. Exclusive reliance on social-media image filters for threat modeling fails confidentiality and capability needs for OT security analysis. Using only a public consumer chatbot with no enterprise controls exposes sensitive prompts and lacks municipal governance. Mandating upload of all OT network diagrams to an unmanaged personal account is an OPSEC and policy violation, not an architecture pattern. Exam caveat: OT-adjacent municipal labs prioritize private/on-prem inference; public consumer chat and personal-account uploads are anti-patterns. Operational check: stand up an approved on-prem or VPC-isolated model endpoint for the OT lab, block outbound paste of diagrams to public LLMs via DLP and policy, inventory which workloads still need commercial APIs under contract, and review architecture with OT and CISO stakeholders before connecting any lab assistant to production SCADA networks.