
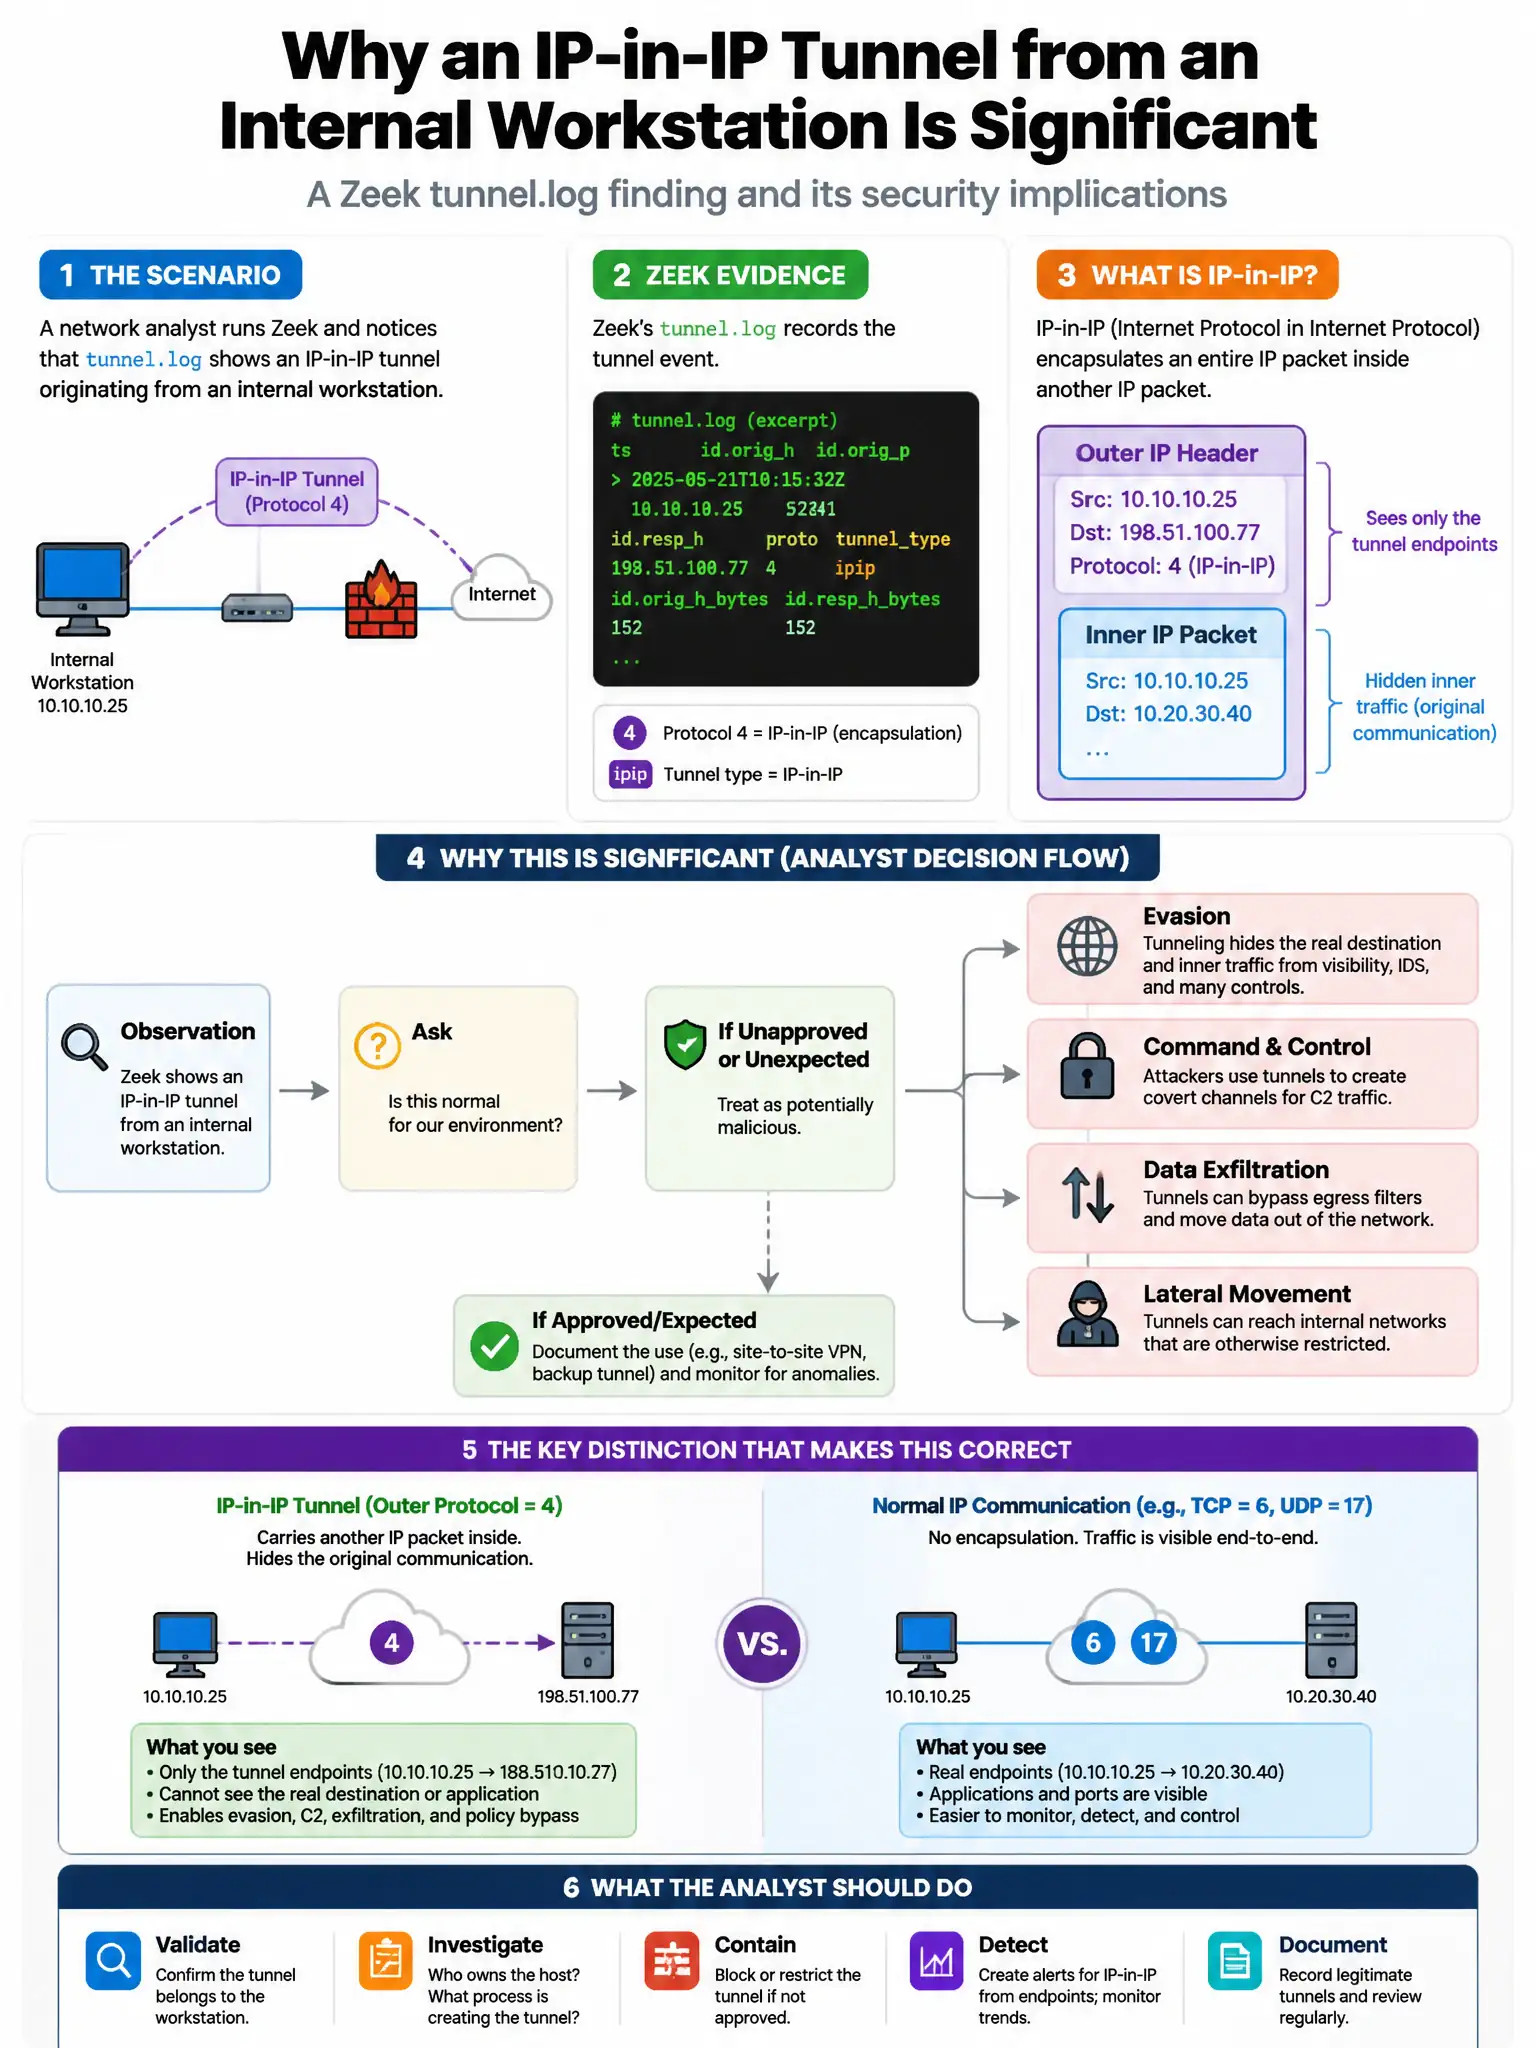
A network analyst runs Zeek and notices that the tunnel.log shows an IP-in-IP tunnel originating from an internal workstation. Why is this significant from a security perspective?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you should care because an unauthorized IP-in-IP tunnel from a workstation can be a covert channel used to slip past security controls. Workstations don't normally need to originate IP-in-IP tunnels, so that's suspicious.
Full Explanation
The correct answer is the option saying an unauthorized IP-in-IP tunnel from a workstation could indicate a covert communication channel used to bypass network security controls. Unauthorized tunneling protocols from workstations — especially IP-in-IP — can indicate malware establishing covert channels to bypass security controls; workstations have no legitimate business reason to originate IP-in-IP tunnels. The option claiming IP-in-IP tunneling is a standard VPN protocol used by all corporate VPN clients is wrong because they typically use SSL VPN (HTTPS-based) or IPsec, not raw IP-in-IP. The option saying Zeek logs IP-in-IP tunnels as informational entries with no security significance is wrong because unauthorized tunnel.log entries from workstations should be treated as suspicious and investigated, not informational. The option stating IP-in-IP tunneling is required for IPv6 compatibility on IPv4 networks and is expected is wrong because 6in4 (IPv6 over IPv4) is a specific transition technology with defined uses; arbitrary IP-in-IP from a workstation is not a standard transition mechanism.