
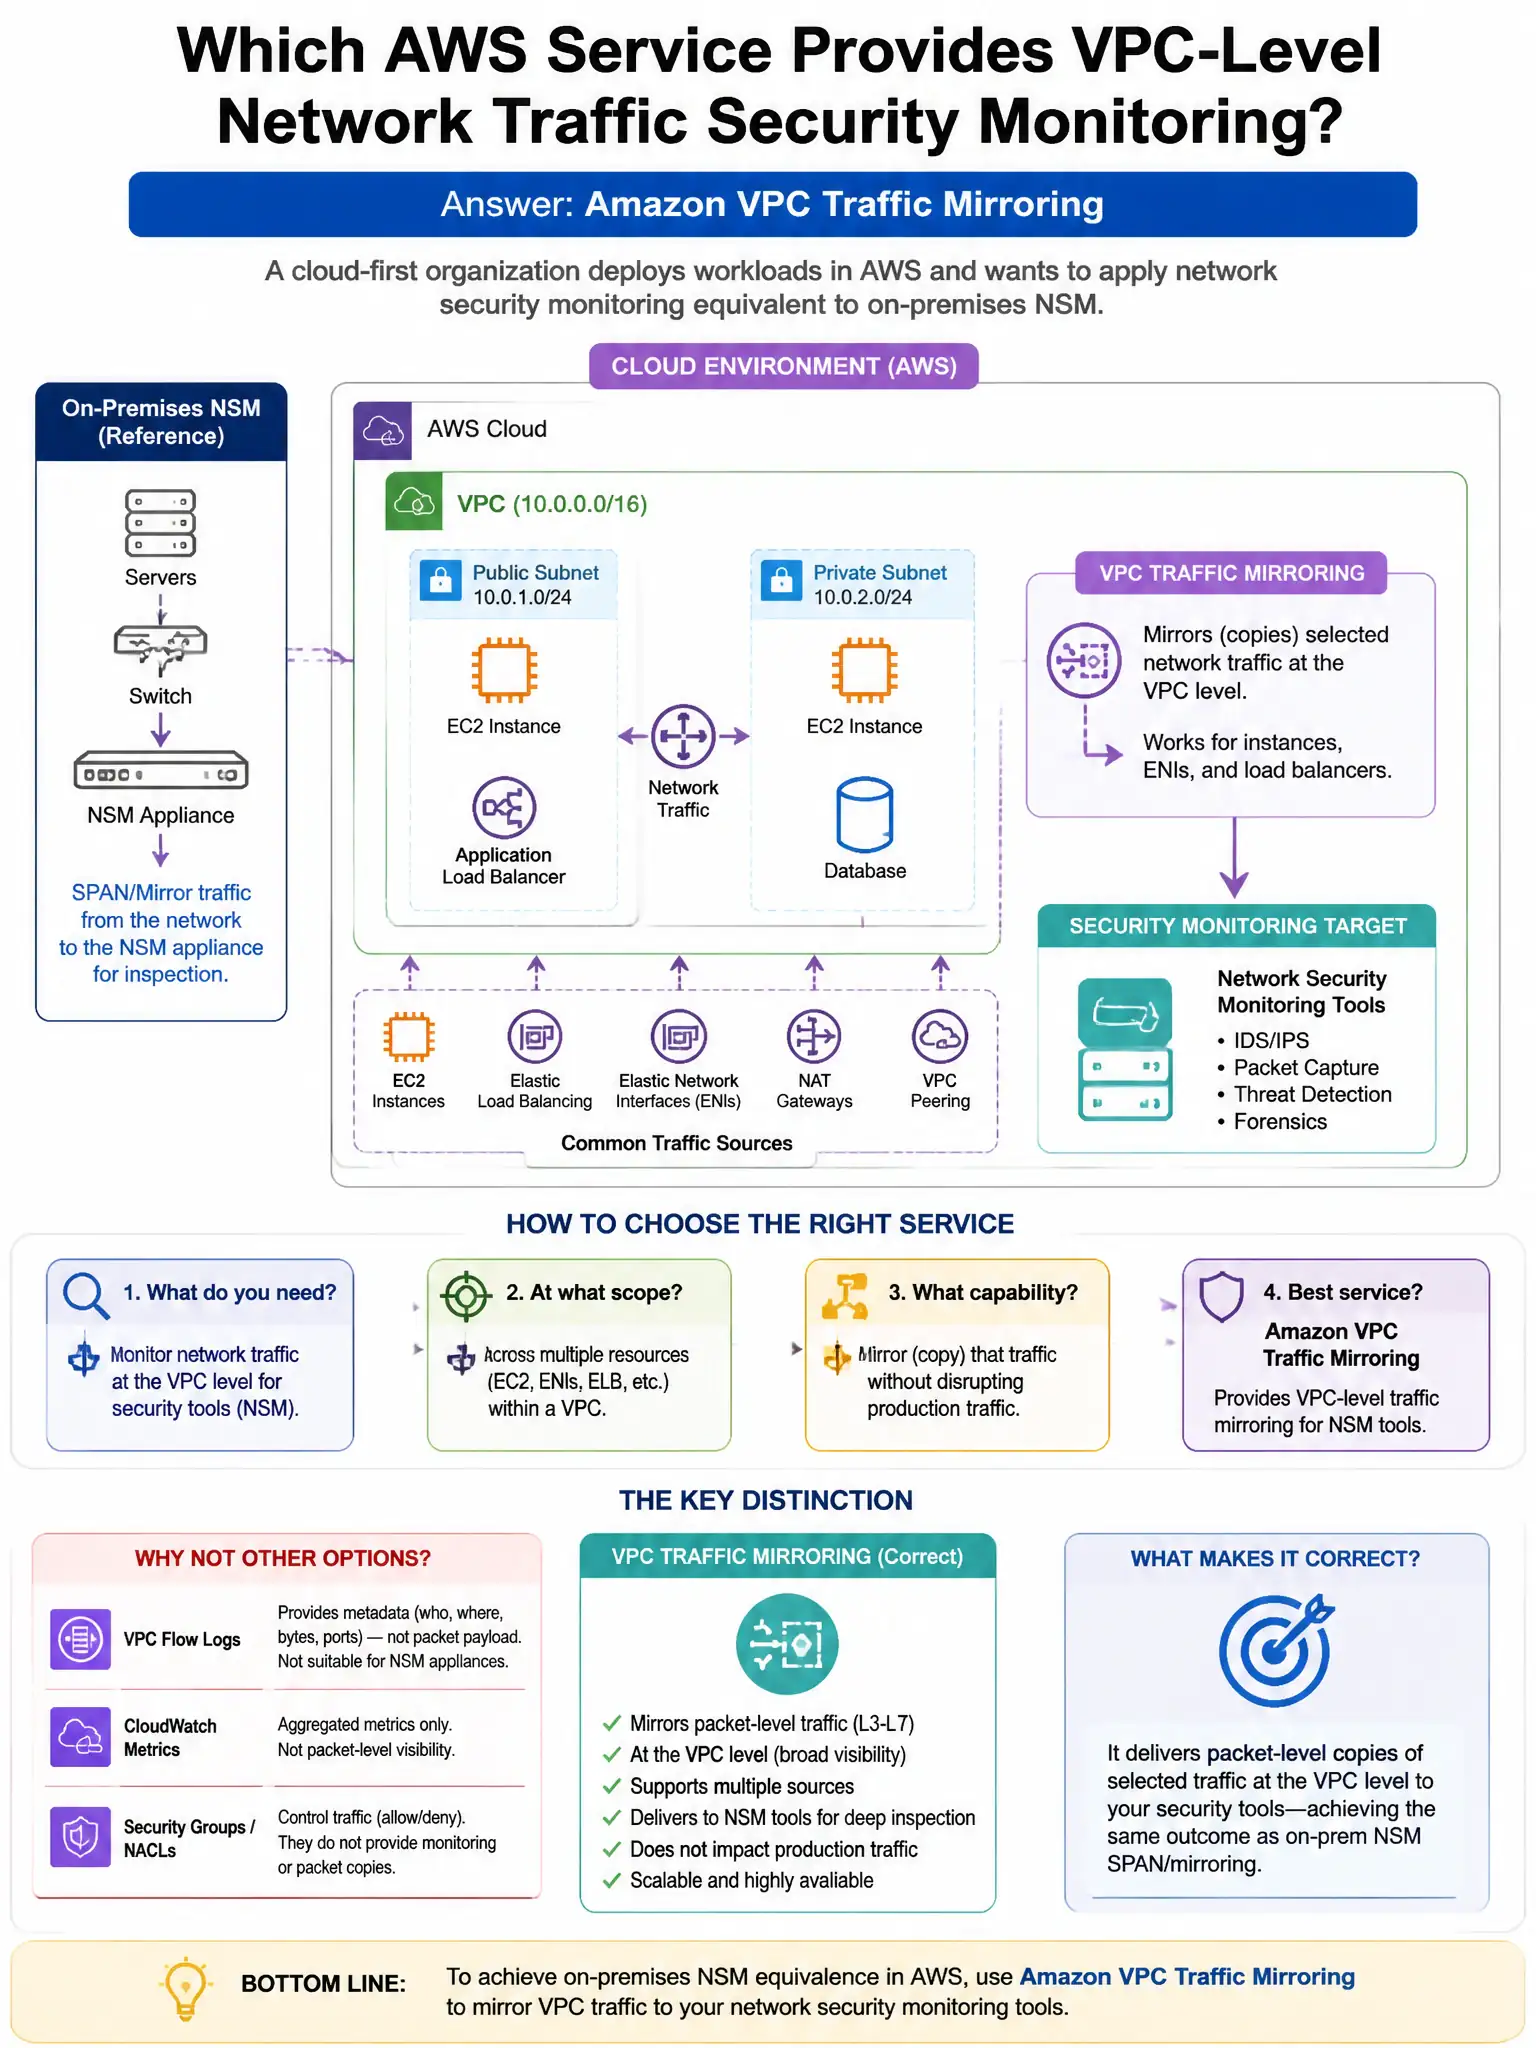
A cloud-first organization deploys workloads in AWS and wants to apply network security monitoring equivalent to on-premises NSM. Which AWS service provides VPC-level network traffic visibility for analysis?
Select an answer to reveal the explanation.
Short Explanation
You want VPC Flow Logs because they capture network flow metadata—source IP, destination IP, ports, protocol, bytes, and action—for traffic traversing VPC network interfaces. That gives you east-west and north-south visibility for NSM analysis, like NetFlow on-premises.
Full Explanation
VPC Flow Logs capturing network connection metadata (5-tuple, bytes, action) for all traffic in the VPC is correct because VPC Flow Logs capture network flow metadata (source IP, destination IP, ports, protocol, bytes, action) for traffic traversing VPC network interfaces, enabling NSM analysis of east-west and north-south traffic patterns equivalent to on-premises NetFlow analysis. The option describing AWS CloudTrail for API call logging is wrong because CloudTrail logs AWS API calls (management plane) not network traffic flows within the VPC. The option describing AWS Config for resource configuration change tracking is wrong because AWS Config tracks resource configuration changes (security groups, IAM policies) not network traffic flow data. The option describing AWS GuardDuty for managed threat detection without requiring flow logs is wrong because GuardDuty consumes VPC Flow Logs (among other sources) and provides managed anomaly detection, but the question asks for the fundamental visibility service; GuardDuty doesn't work without the underlying flow log data.