
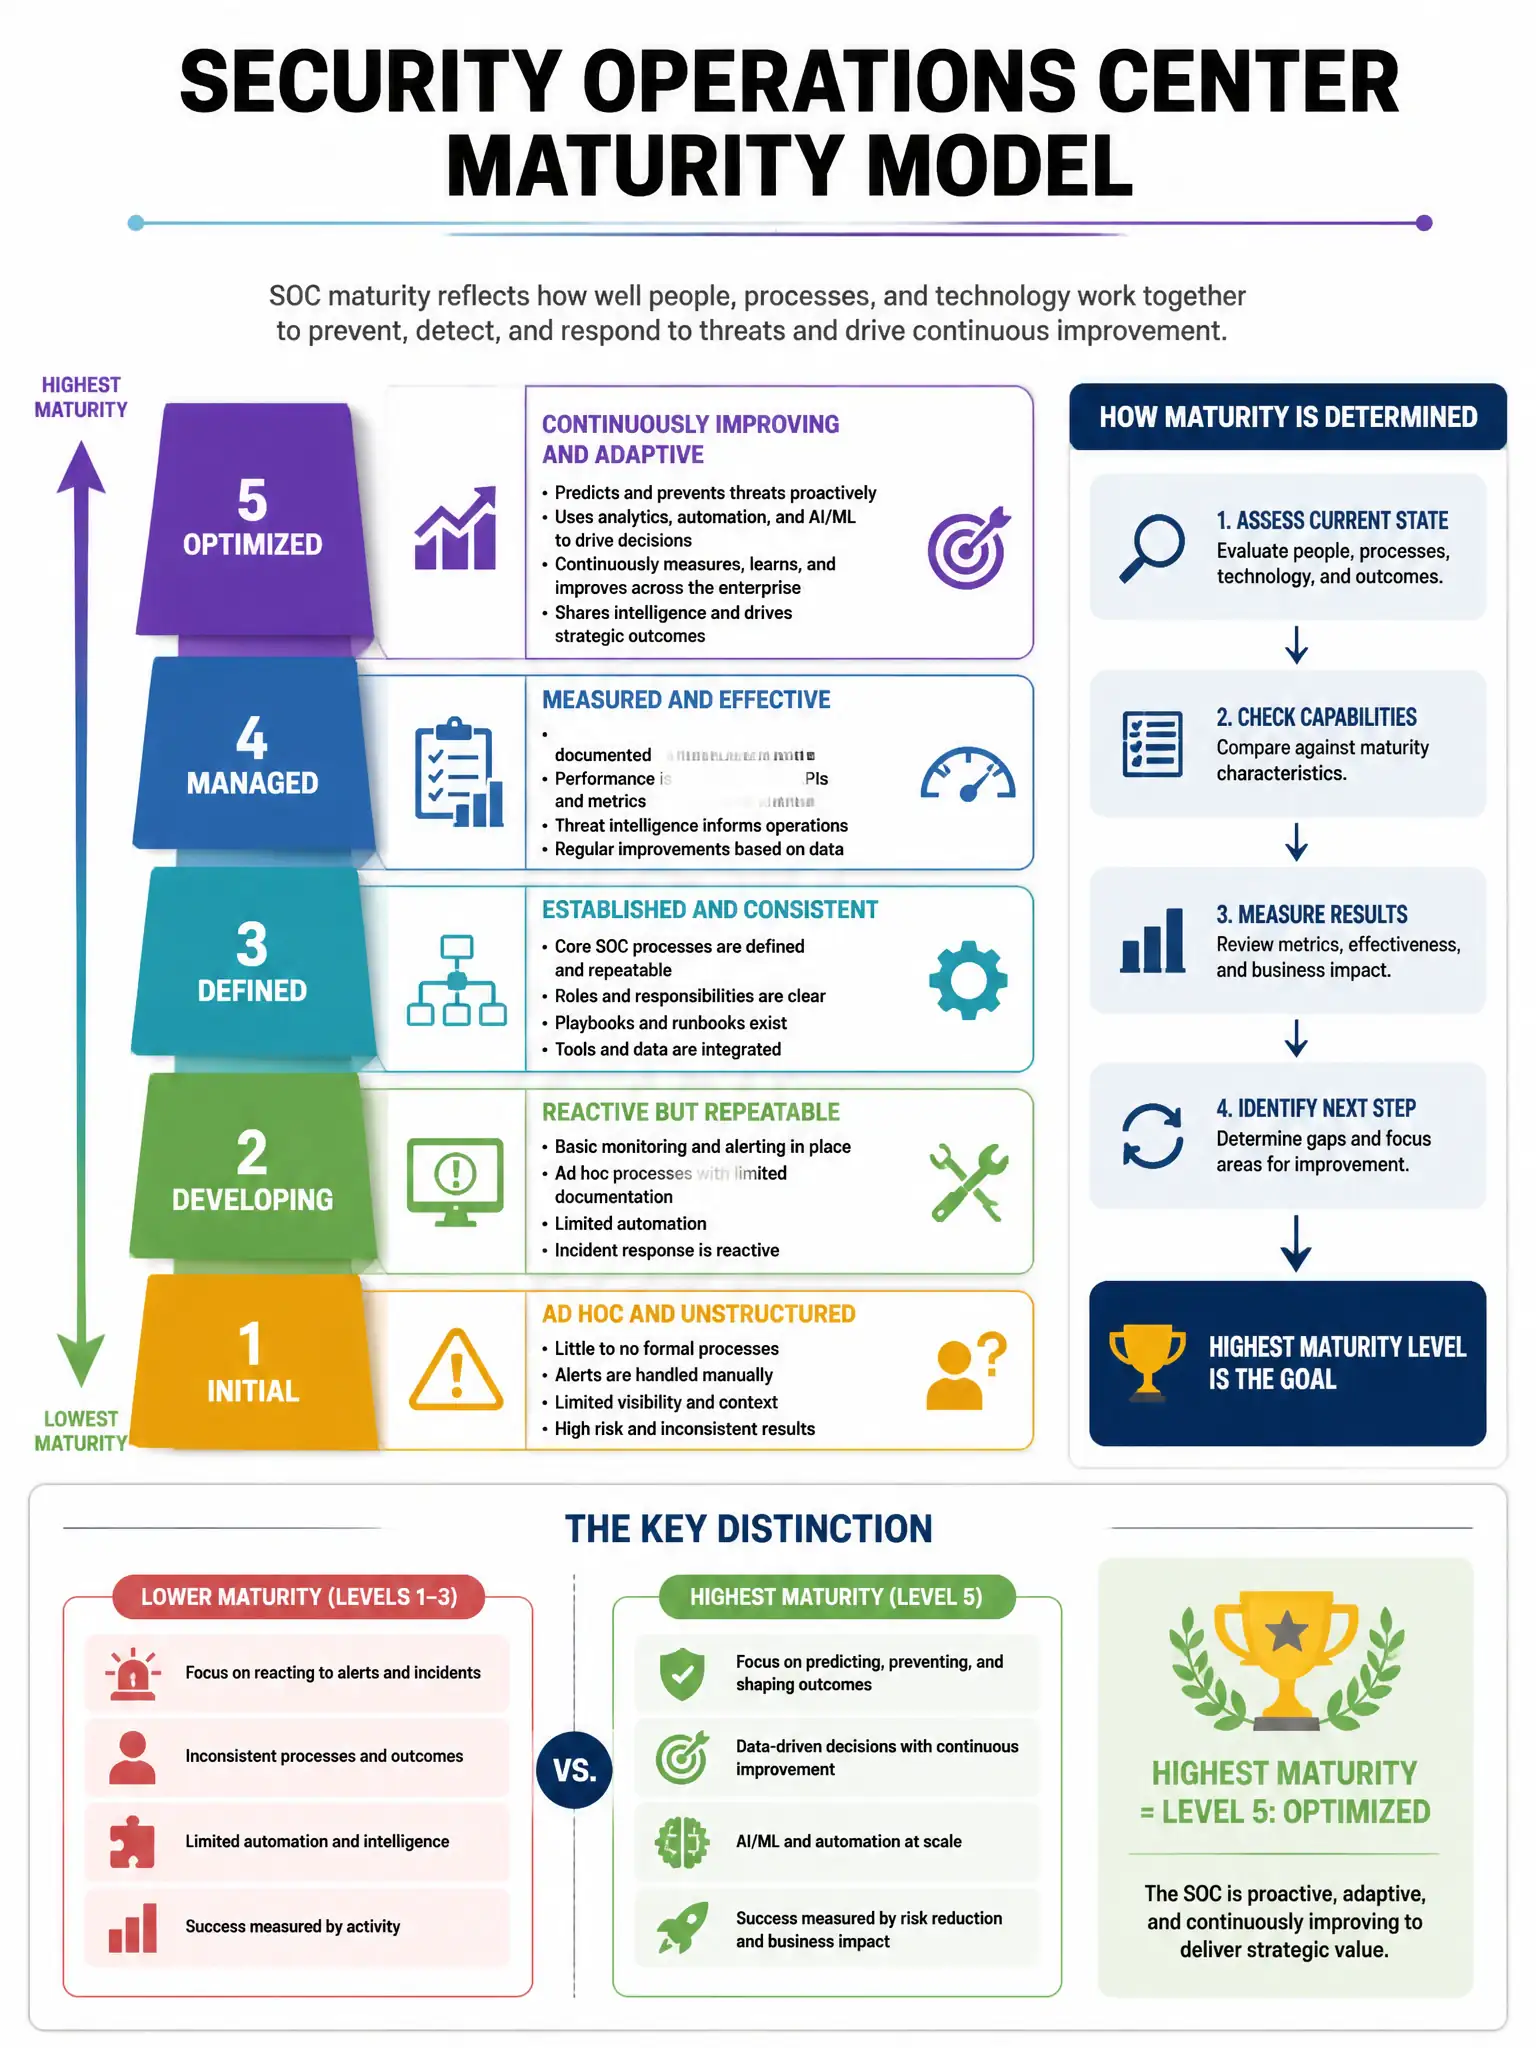
An organization wants to implement a Security Operations Center maturity model. Which capability represents the highest maturity level?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're looking for the capability that shows your SOC isn't just waiting for alerts. Threat hunting and adversary simulation push you to find attackers before tools catch them and prove your defenses work through purple team exercises. That's the highest maturity level.
Full Explanation
Threat hunting and adversary simulation is correct because the highest SOC maturity levels involve proactive threat hunting (finding attackers before automated tools alert) and adversary simulation/purple teaming (continuously validating and improving detection controls), requiring deep expertise and sophisticated analytical capabilities. Reactive monitoring - responding to alerts generated by existing tools is wrong because reactive monitoring is the lowest maturity level - simply responding to automated alerts. Log collection from all network devices and endpoints is wrong because log collection is a foundational capability required at the lowest maturity levels. Ticketing system integration with the SIEM for alert tracking is wrong because SIEM-ticketing integration is a basic operational efficiency improvement, not an advanced capability.