
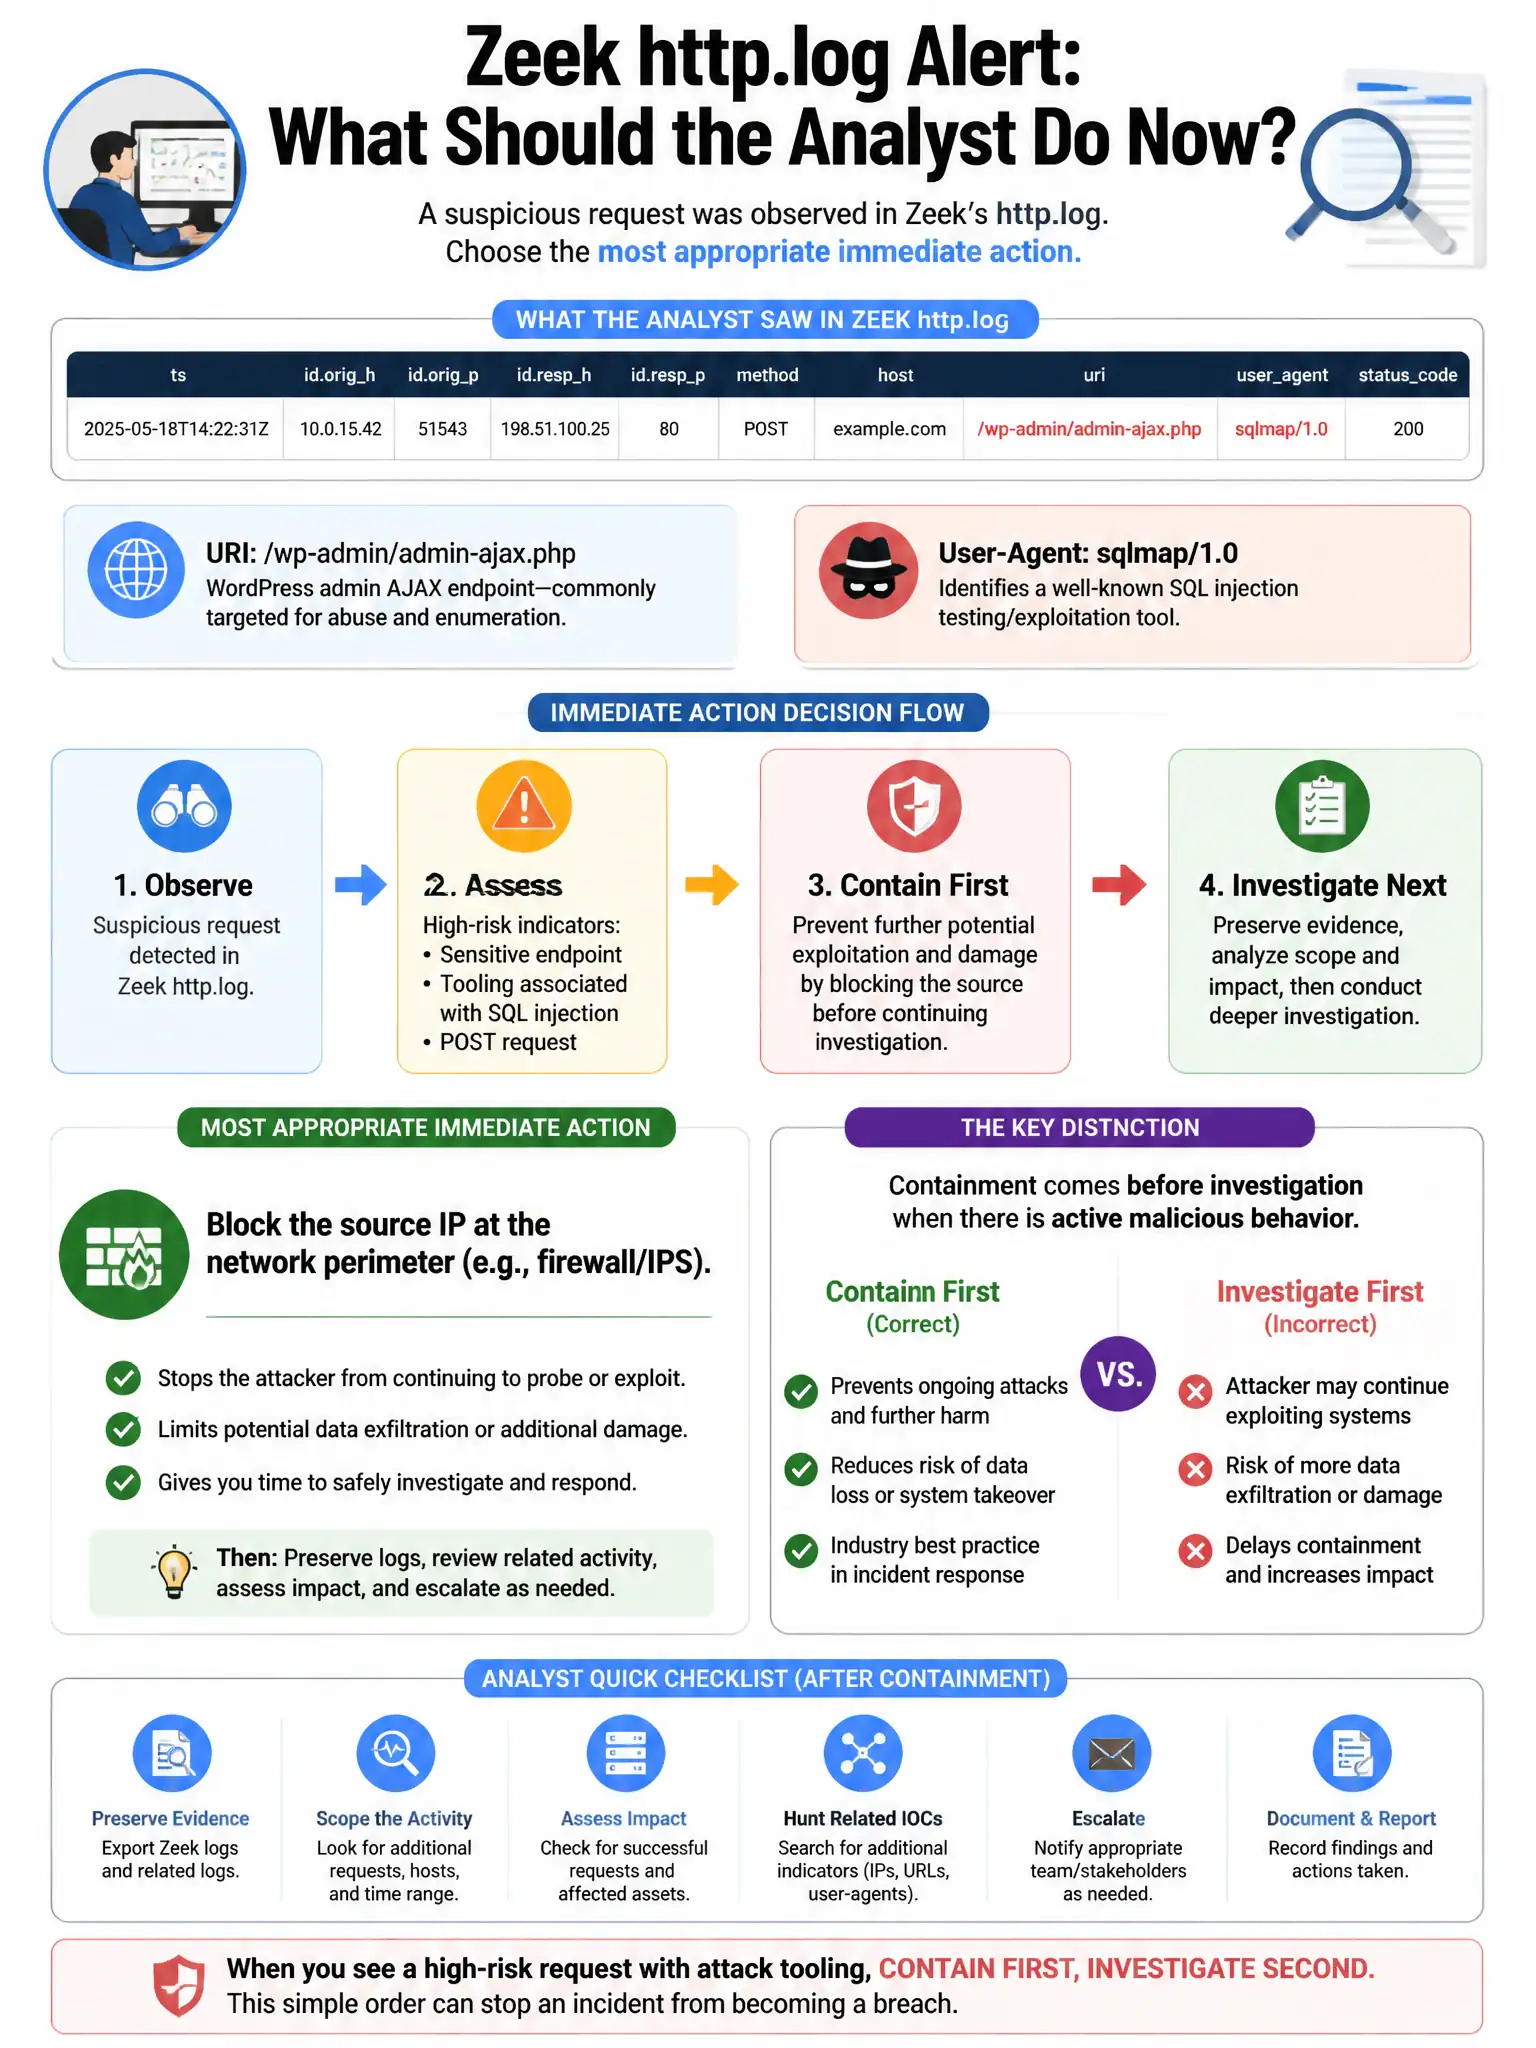
An analyst uses Zeek's http.log and notices a request where uri is '/wp-admin/admin-ajax.php' and user_agent is 'sqlmap/1.0'. What is the most appropriate immediate action?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to check whether this sqlmap request is part of an authorized penetration test. If it isn't, treat it as an active SQL injection attempt against the WordPress admin interface and escalate it.
Full Explanation
The correct action is to investigate whether this represents an authorized penetration test; if not, treat it as an active SQL injection attack against a WordPress admin interface and escalate. sqlmap is an automated SQL injection tool, and requests from it to the WordPress admin interface indicate either an authorized penetration test or an active attack. The first step is checking whether a pentest is authorized before escalating as a security incident. The option to ignore it because sqlmap is a legitimate testing tool is wrong because while sqlmap can be used by authorized testers, its presence requires verification; ignoring it risks missing a real attack. The option to block the user agent string 'sqlmap' at the web application firewall globally is wrong because blocking the user agent globally is a reactive control but does not address whether the attack succeeded or whether other attack tools are being used with different user agents. The option to restart the web server to clear any injected SQL commands is wrong because restarting the web server does not reverse SQL injection if the database has already been accessed or modified.