
A security team is implementing network security monitoring and must decide where to place IDS/IPS sensors relative to NAT boundaries. What monitoring blind spot does NAT create for an IDS sensor placed outside the NAT boundary?
Select an answer to reveal the explanation.
Short Explanation
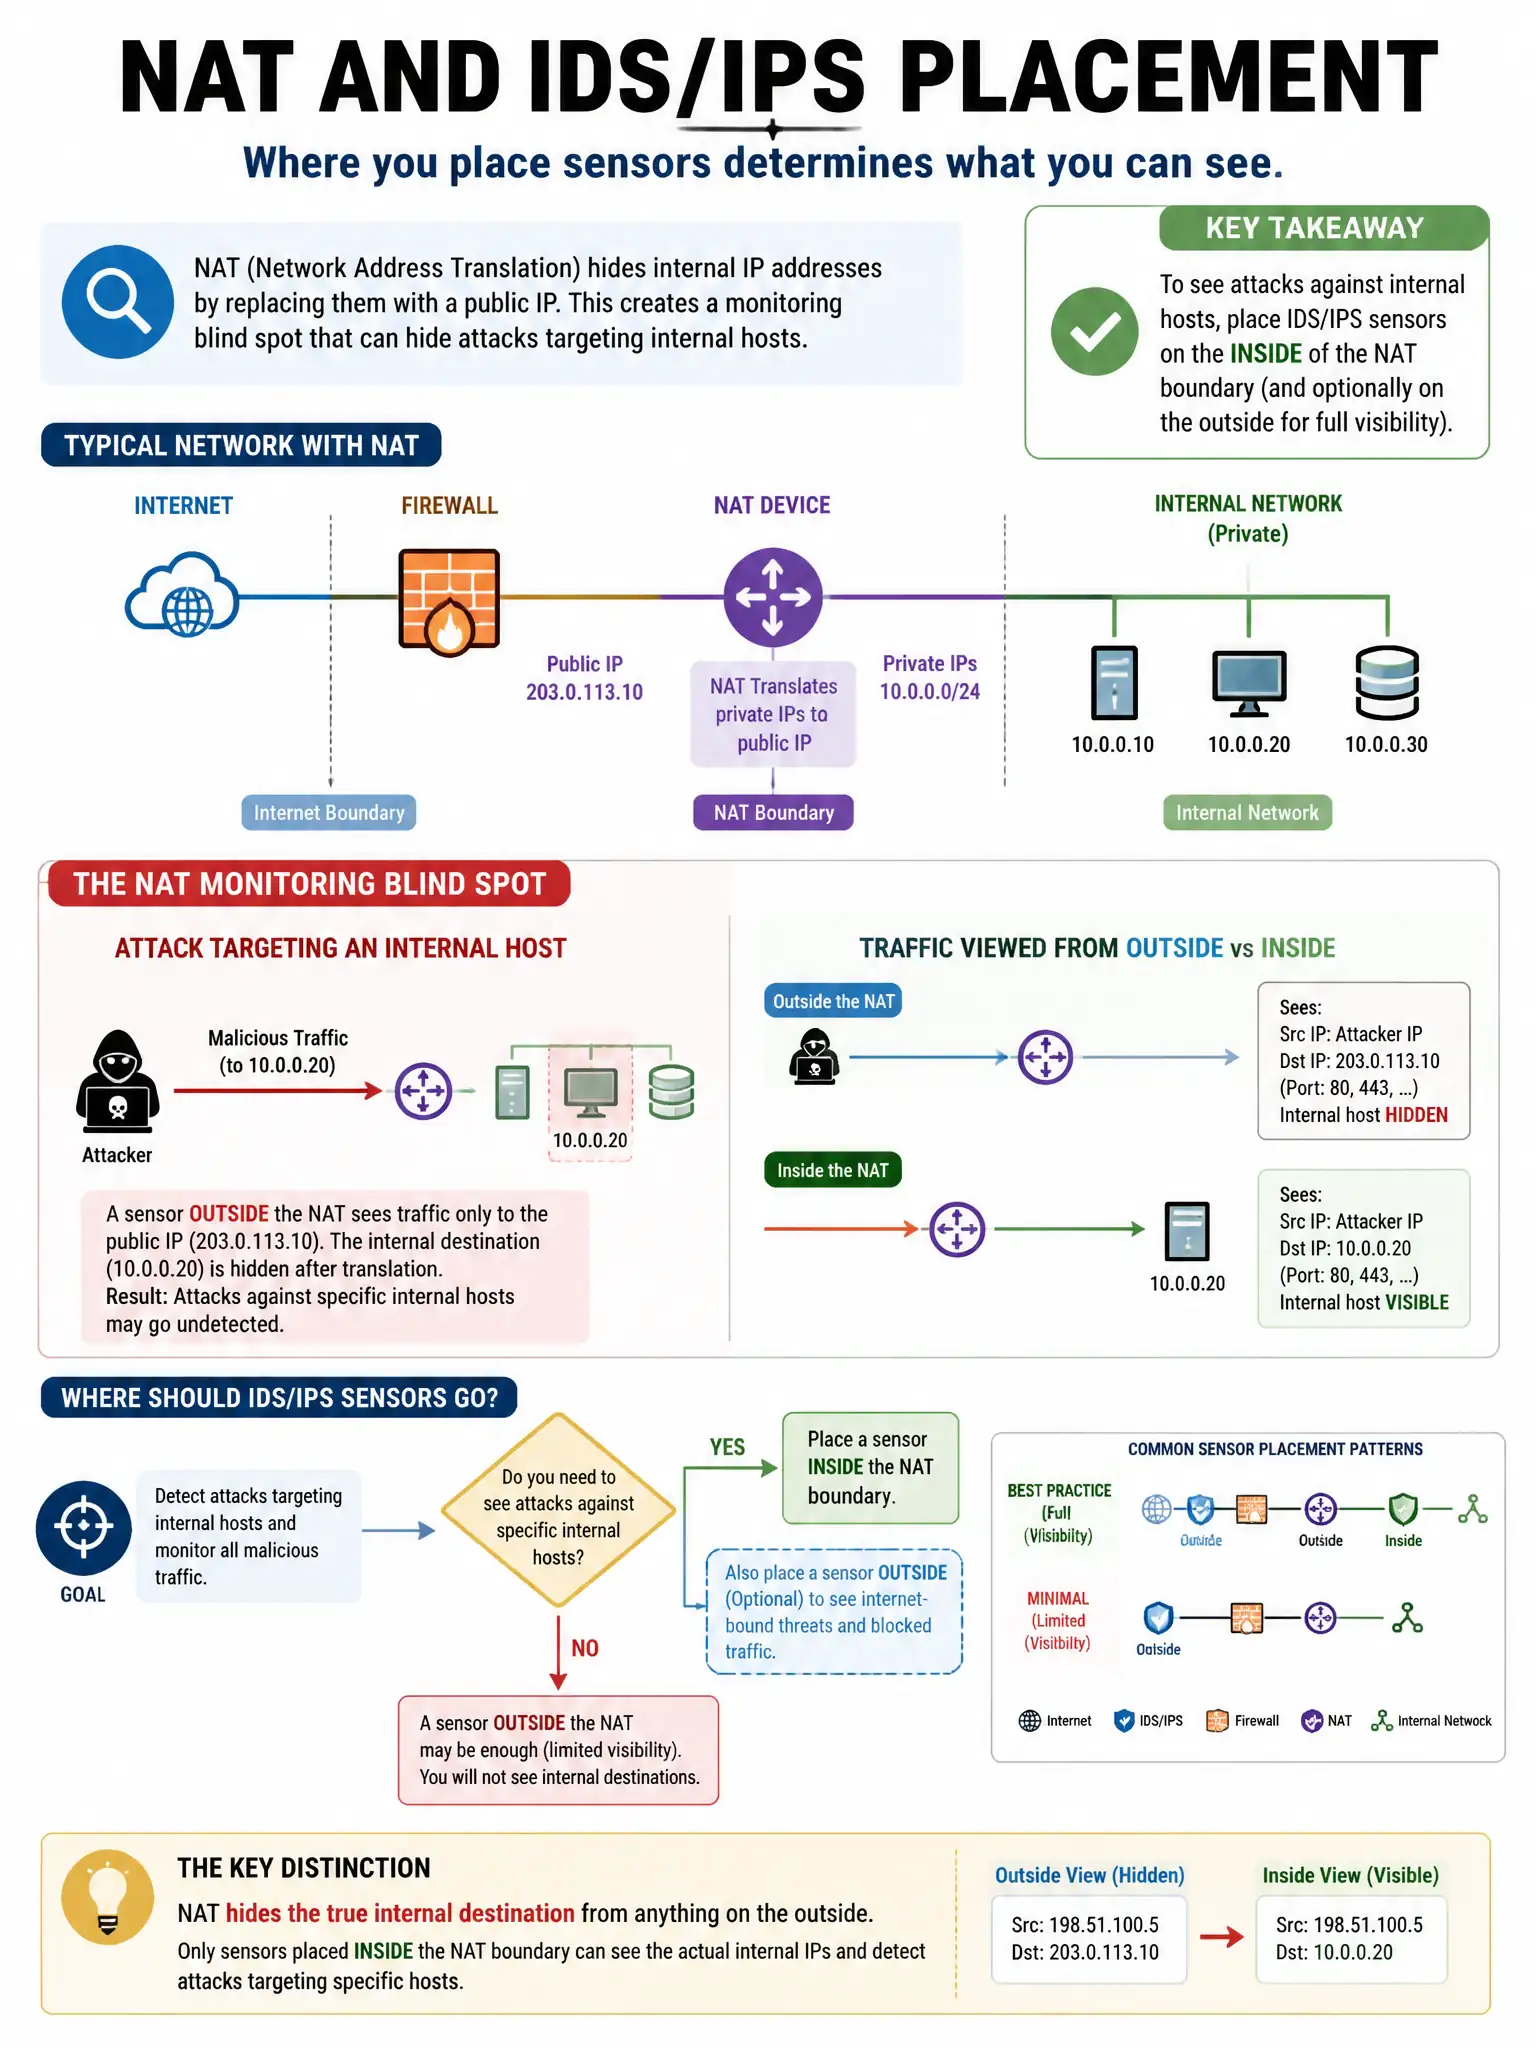
Here's the deal — when NAT translates internal private IPs to a shared public IP, an IDS outside the NAT boundary sees all traffic as coming from that public IP. You lose the ability to identify which specific internal host generated the traffic unless you correlate with NAT translation logs.
Full Explanation
The correct answer is the statement that an IDS outside NAT sees only the NAT public IP for all internal hosts, making it impossible to attribute traffic to specific internal hosts without correlation with NAT logs. NAT translates internal private IPs to a shared public IP; an IDS outside NAT sees all traffic as originating from the public IP, losing the ability to identify which specific internal host generated the traffic without correlating with firewall NAT translation logs. The choice about encrypted TLS traffic is wrong because TLS visibility depends on decryption capability, not NAT placement. The choice about ICMP traffic is wrong because ICMP is NATted along with other traffic and is visible to the sensor; NAT does not specifically block ICMP visibility. The choice about misidentifying UDP traffic as TCP is wrong because NAT operates at Layer 3 and does not change Layer 4 protocol type.