
An organization wants to implement the principle of least privilege on Windows workstations. Currently, all users are local administrators. What is the primary security risk of this configuration and the recommended change?
Select an answer to reveal the explanation.
Short Explanation
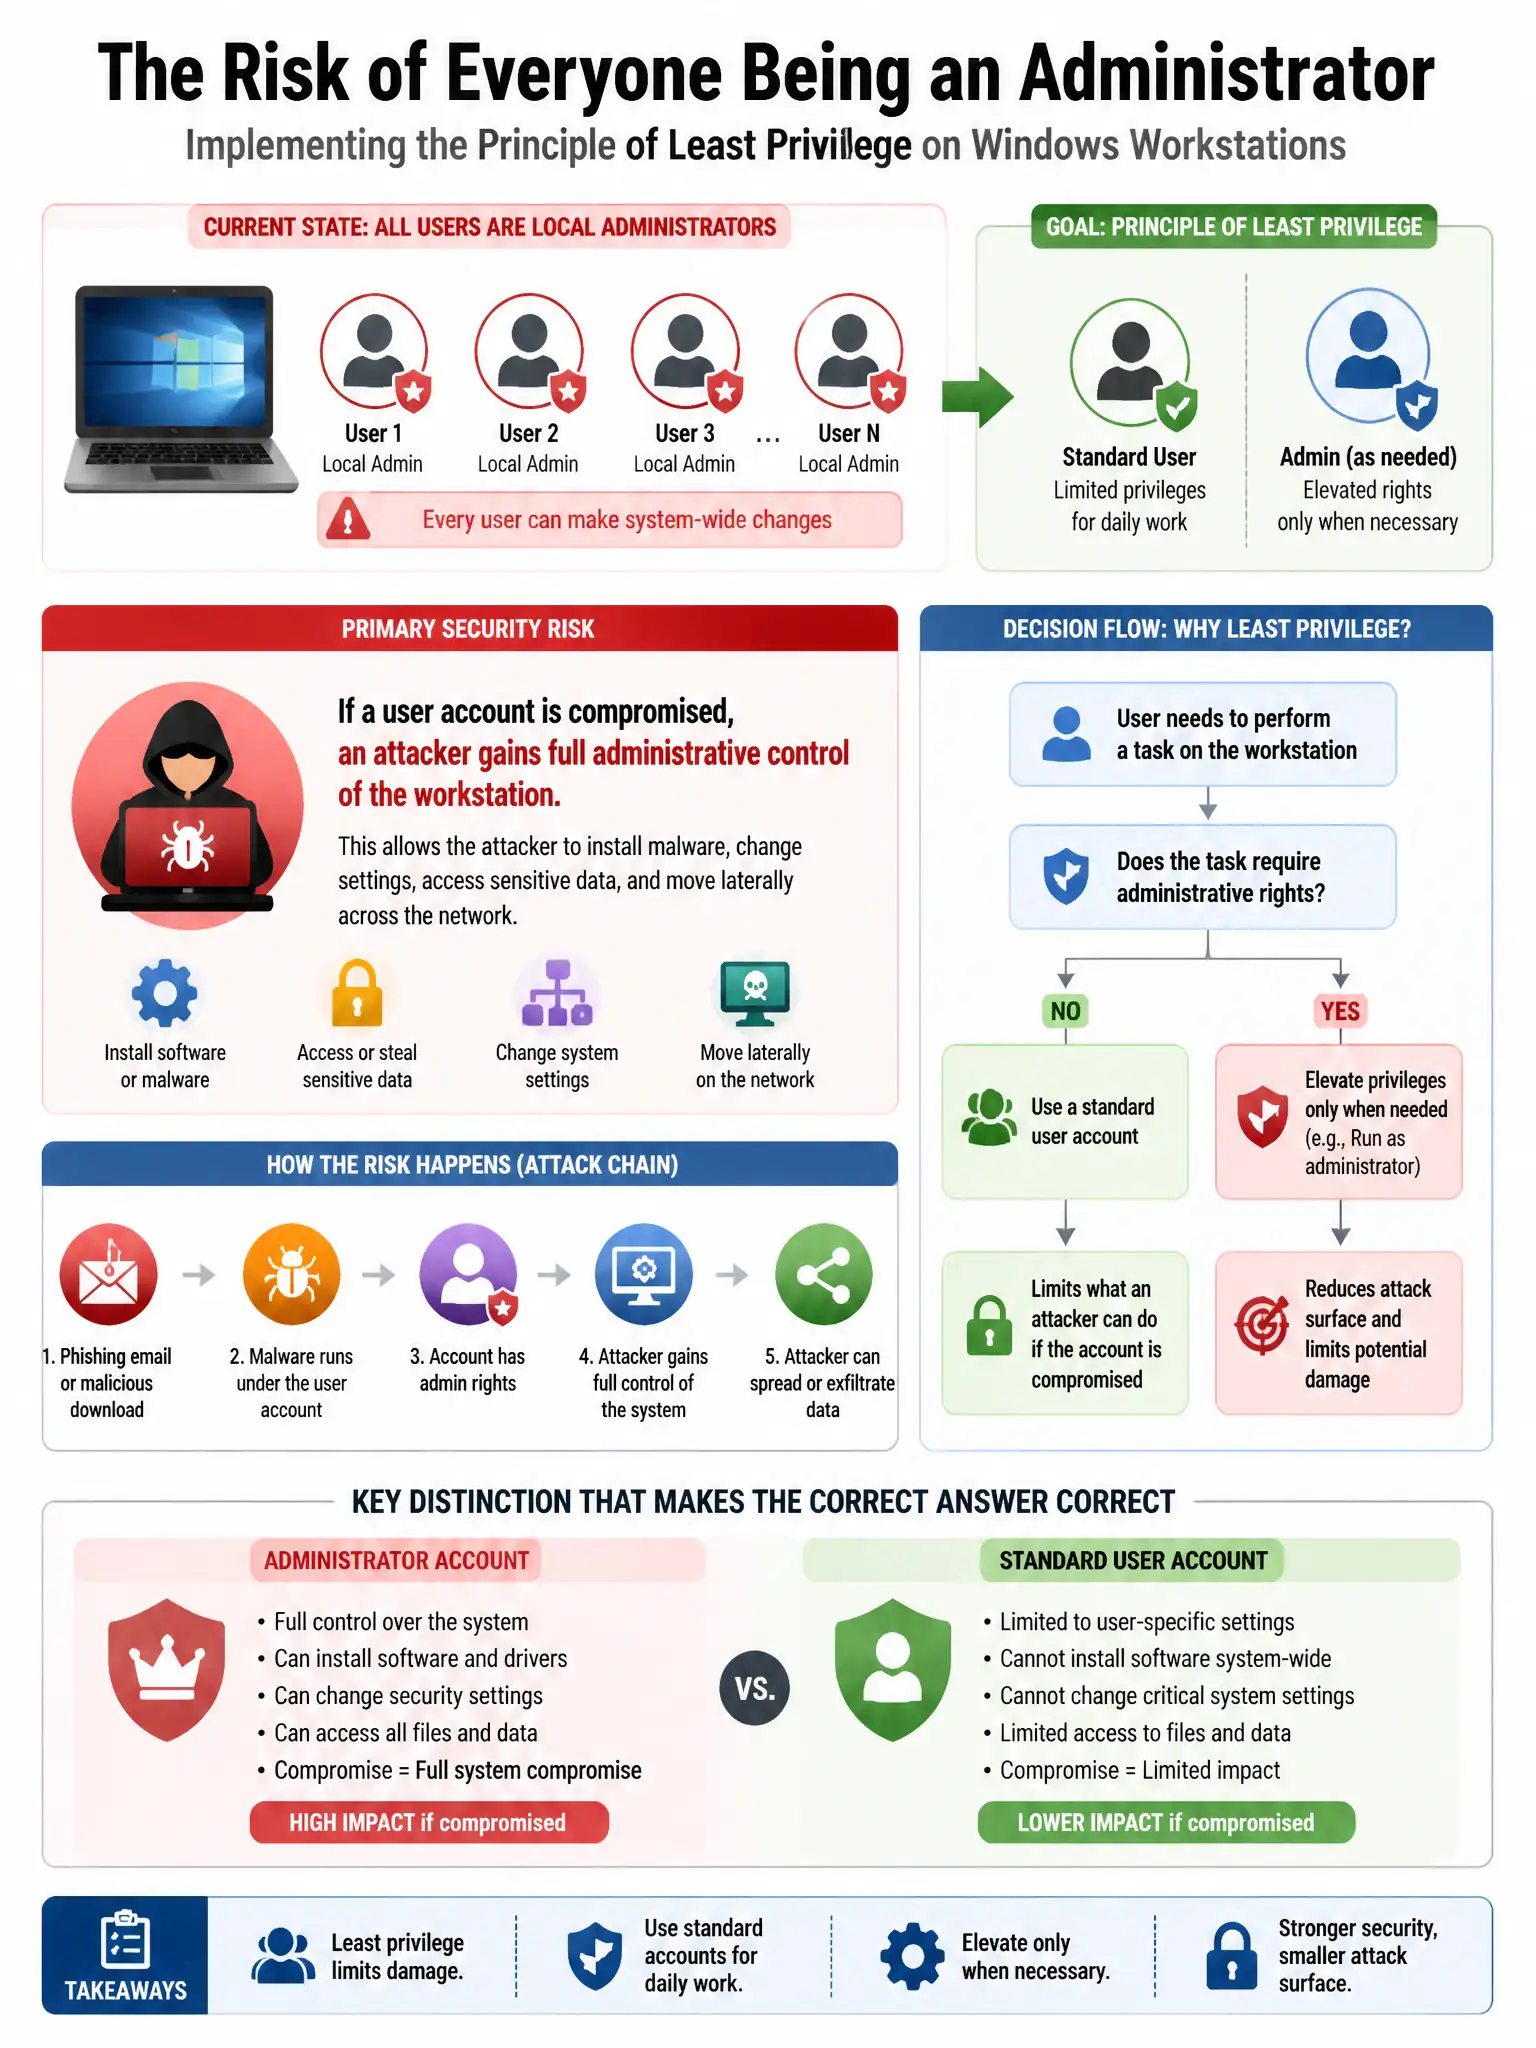
Here's the deal — local administrator rights let malware or attackers install software, modify system settings, disable security controls, and dump credentials. You should remove users from the local Administrators group and run them as standard users to limit the blast radius.
Full Explanation
The correct choice says local administrator rights allow malware or attackers to install software, modify system settings, and disable security controls, and users should be removed from the local Administrators group and run as standard users. Local administrator rights allow code, including malware, to install persistent services, modify the registry, disable security tools, and dump credentials; removing users from the local Administrators group and running them as standard users dramatically limits malware impact. The option saying local administrators cannot join the domain and users should be moved to Domain Admins is wrong because local administrator accounts are separate from domain accounts, standard users can join domain-joined workstations, and Domain Admins grants excessive privilege. The option saying local admin rights are required for all Windows applications is wrong because modern Windows applications are designed to run as standard users; apps needing admin rights should use UAC elevation prompts or be managed separately. The option saying risk is minimal because local admin rights do not affect network-level security is wrong because local admin rights enable credential theft and security control bypass, risking broader compromise.