
A security operations team wants to reduce noise in their SIEM by implementing log source normalization. What does normalization accomplish?
Select an answer to reveal the explanation.
Short Explanation
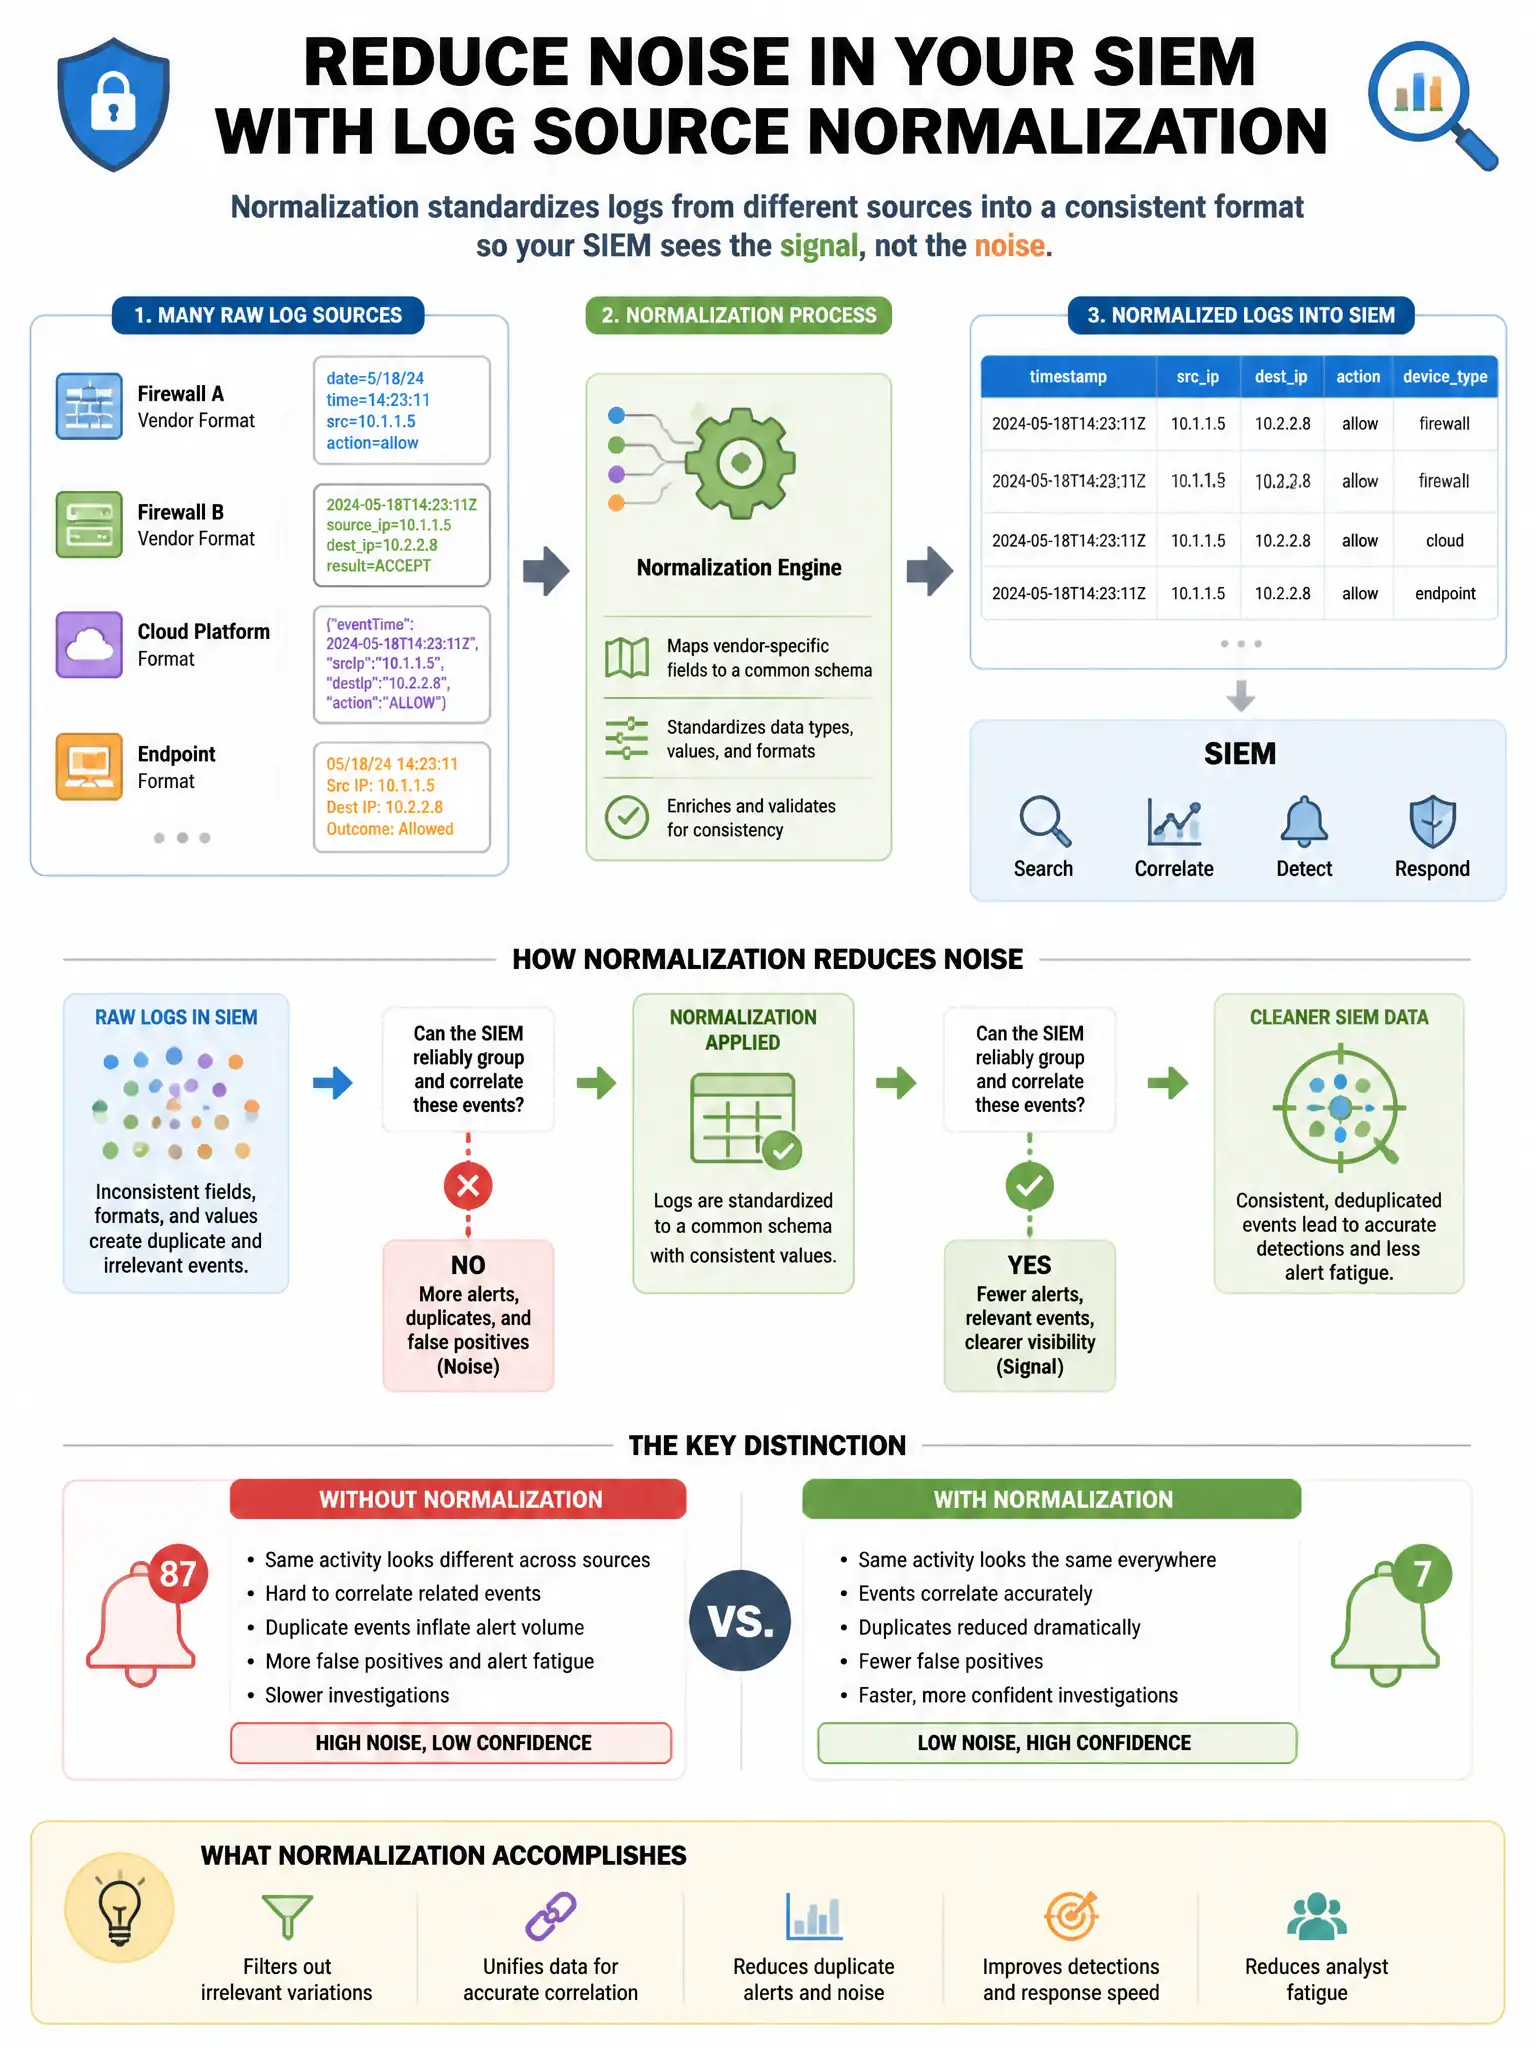
Here's the deal — normalization maps different vendor log formats into a common schema with consistent field names, so one correlation rule can work across firewall, IDS, and endpoint logs. It doesn't encrypt, compress, or filter logs; it standardizes the data.
Full Explanation
Mapping diverse log formats from different vendors into a common schema with consistent field names is correct because different vendors use different field names for the same concepts (e.g., 'src_ip', 'source_address', 'SourceIP' all mean the same thing); normalization maps these to a consistent Common Information Model (CIM) or similar schema so a single correlation rule works across firewall, IDS, and endpoint logs simultaneously. Encrypting all log data before storage to protect sensitive fields is wrong because normalization is about data schema transformation, not encryption; encryption is a separate storage security concern. Compressing log data to reduce storage costs is wrong because normalization may or may not affect storage size; its purpose is field consistency, not compression. Filtering out all informational log events to reduce volume is wrong because normalization transforms data format; filtering is a separate process that may be applied independently.