
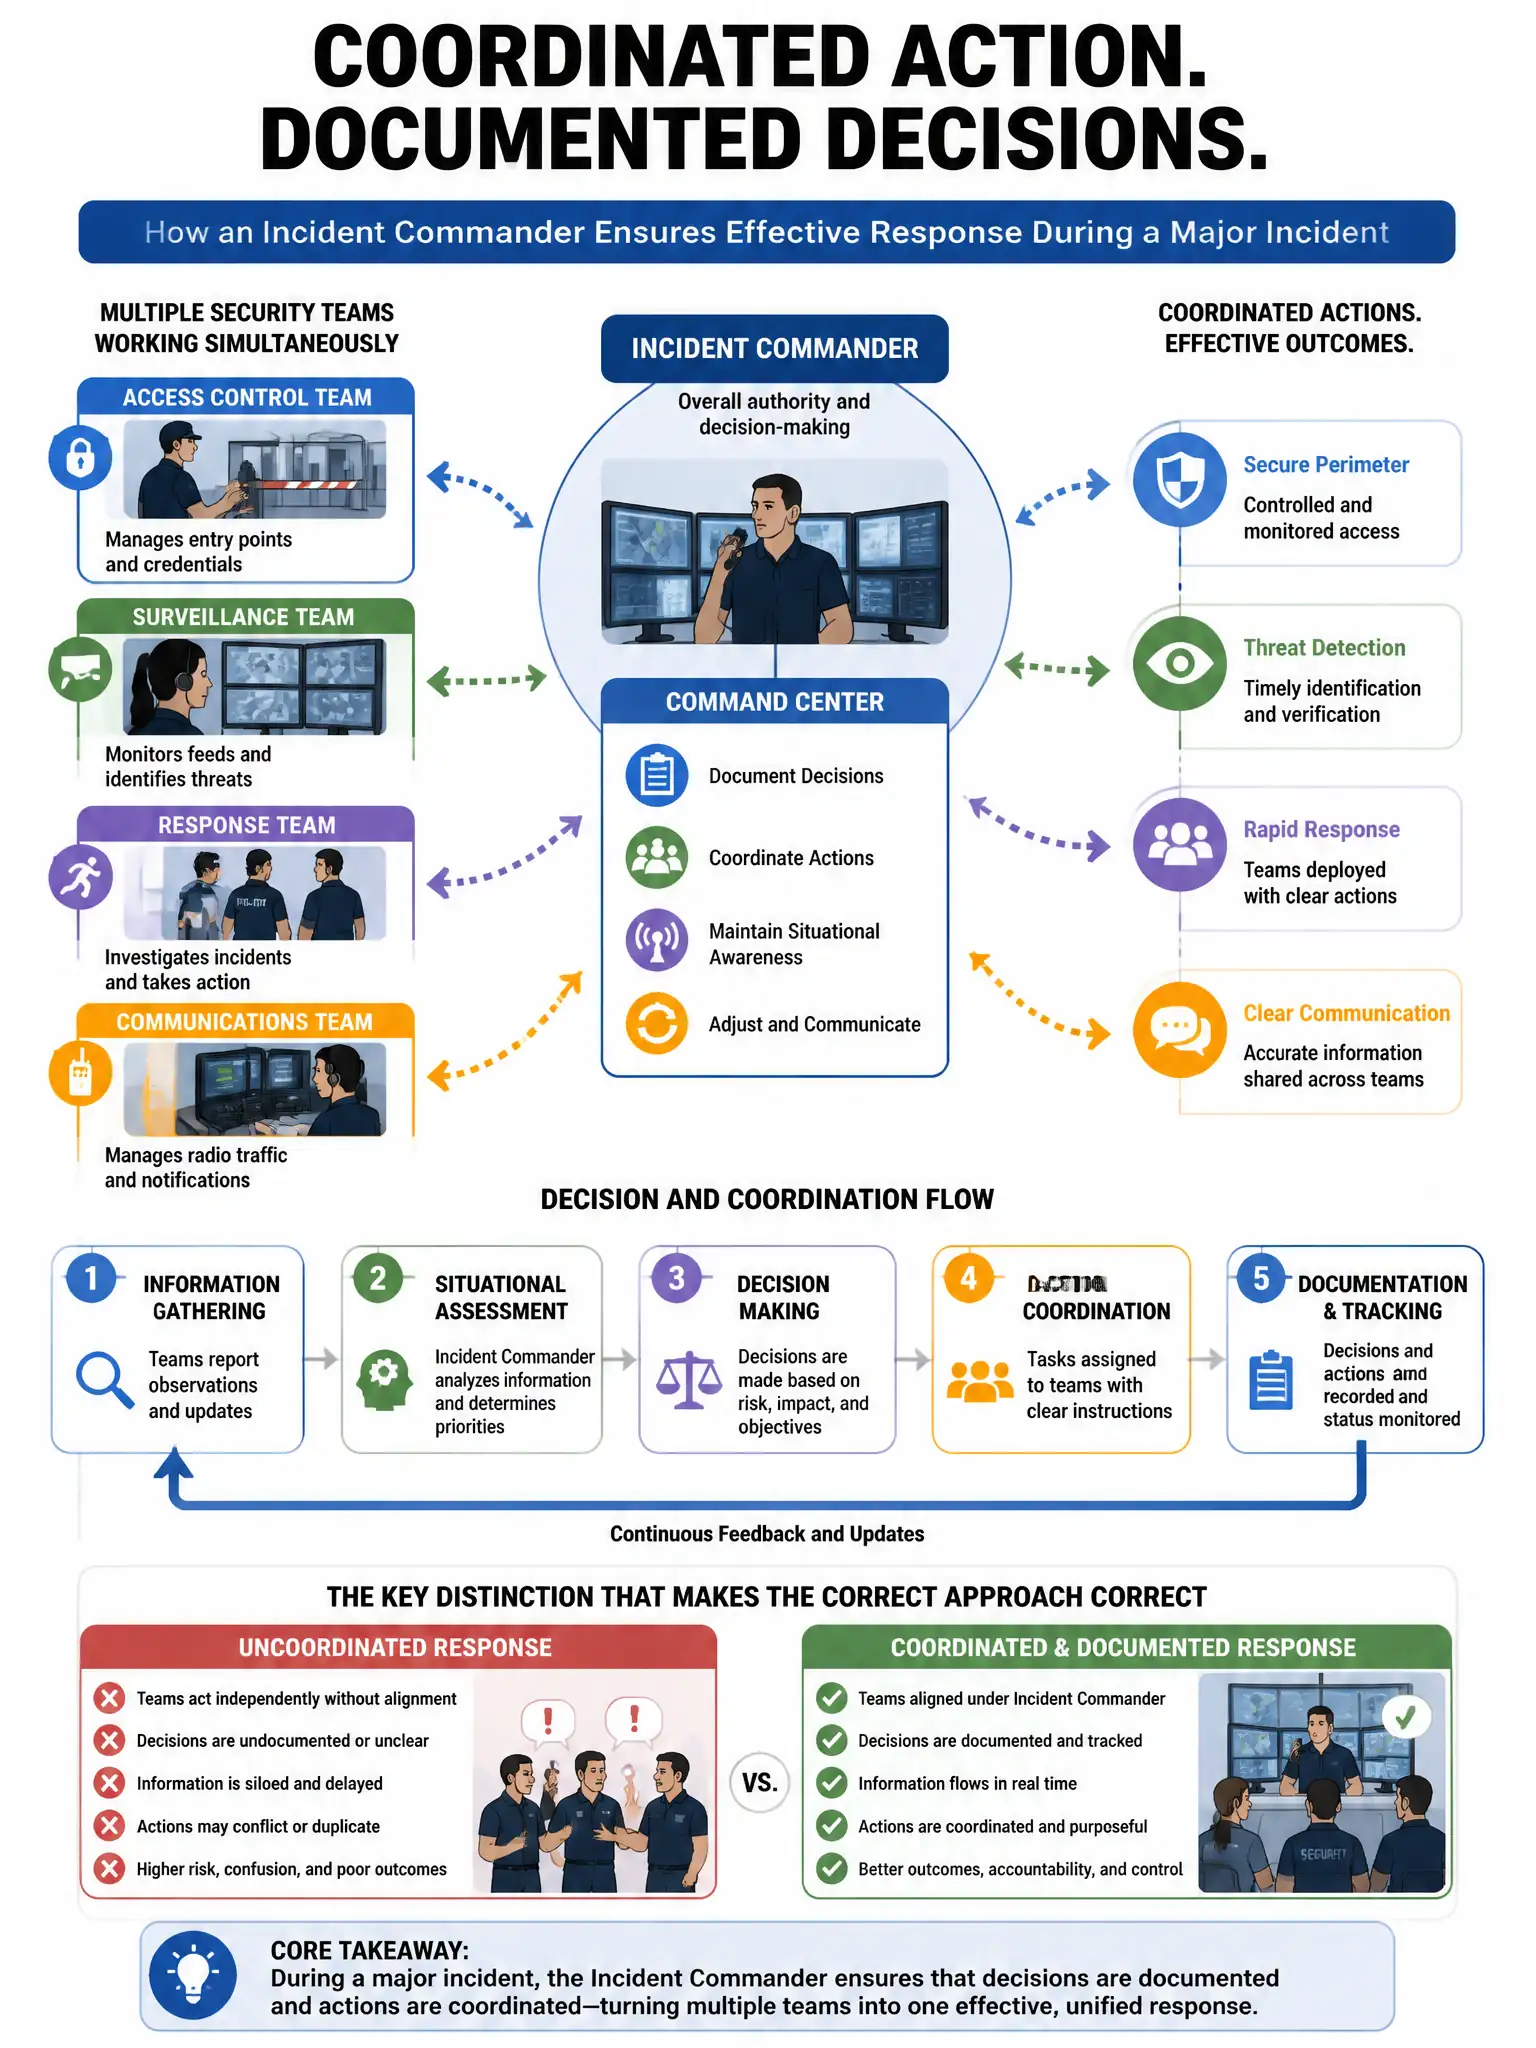
During a major incident, multiple security teams are working simultaneously. The incident commander wants to ensure that decisions are documented and actions are coordinated. Which document serves as the central record of all incident actions, decisions, and timestamps?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need the incident logbook or case management system because it captures every action, observation, and decision with timestamps during active response. That timestamped chronological record keeps multiple teams coordinated, accountable, and able to reconstruct the response timeline.
Full Explanation
The incident logbook or case management system is correct because it captures every action, observation, and decision with timestamps during active response — essential for coordination between teams, accountability, and reconstruction of the response timeline. The incident response policy document is wrong because it is a procedural document created before incidents; it guides response but does not record real-time actions. The lessons-learned report written after incident closure is wrong because it is a post-incident document created after closure, not a real-time action log. The SIEM alert queue showing all triggered alerts is wrong because it shows detection alerts but does not capture analyst actions, decisions, or narrative context.