
An organization's security policy requires that all network devices use encrypted management protocols. Which statement correctly distinguishes Telnet from SSH for device management?
Select an answer to reveal the explanation.
Short Explanation
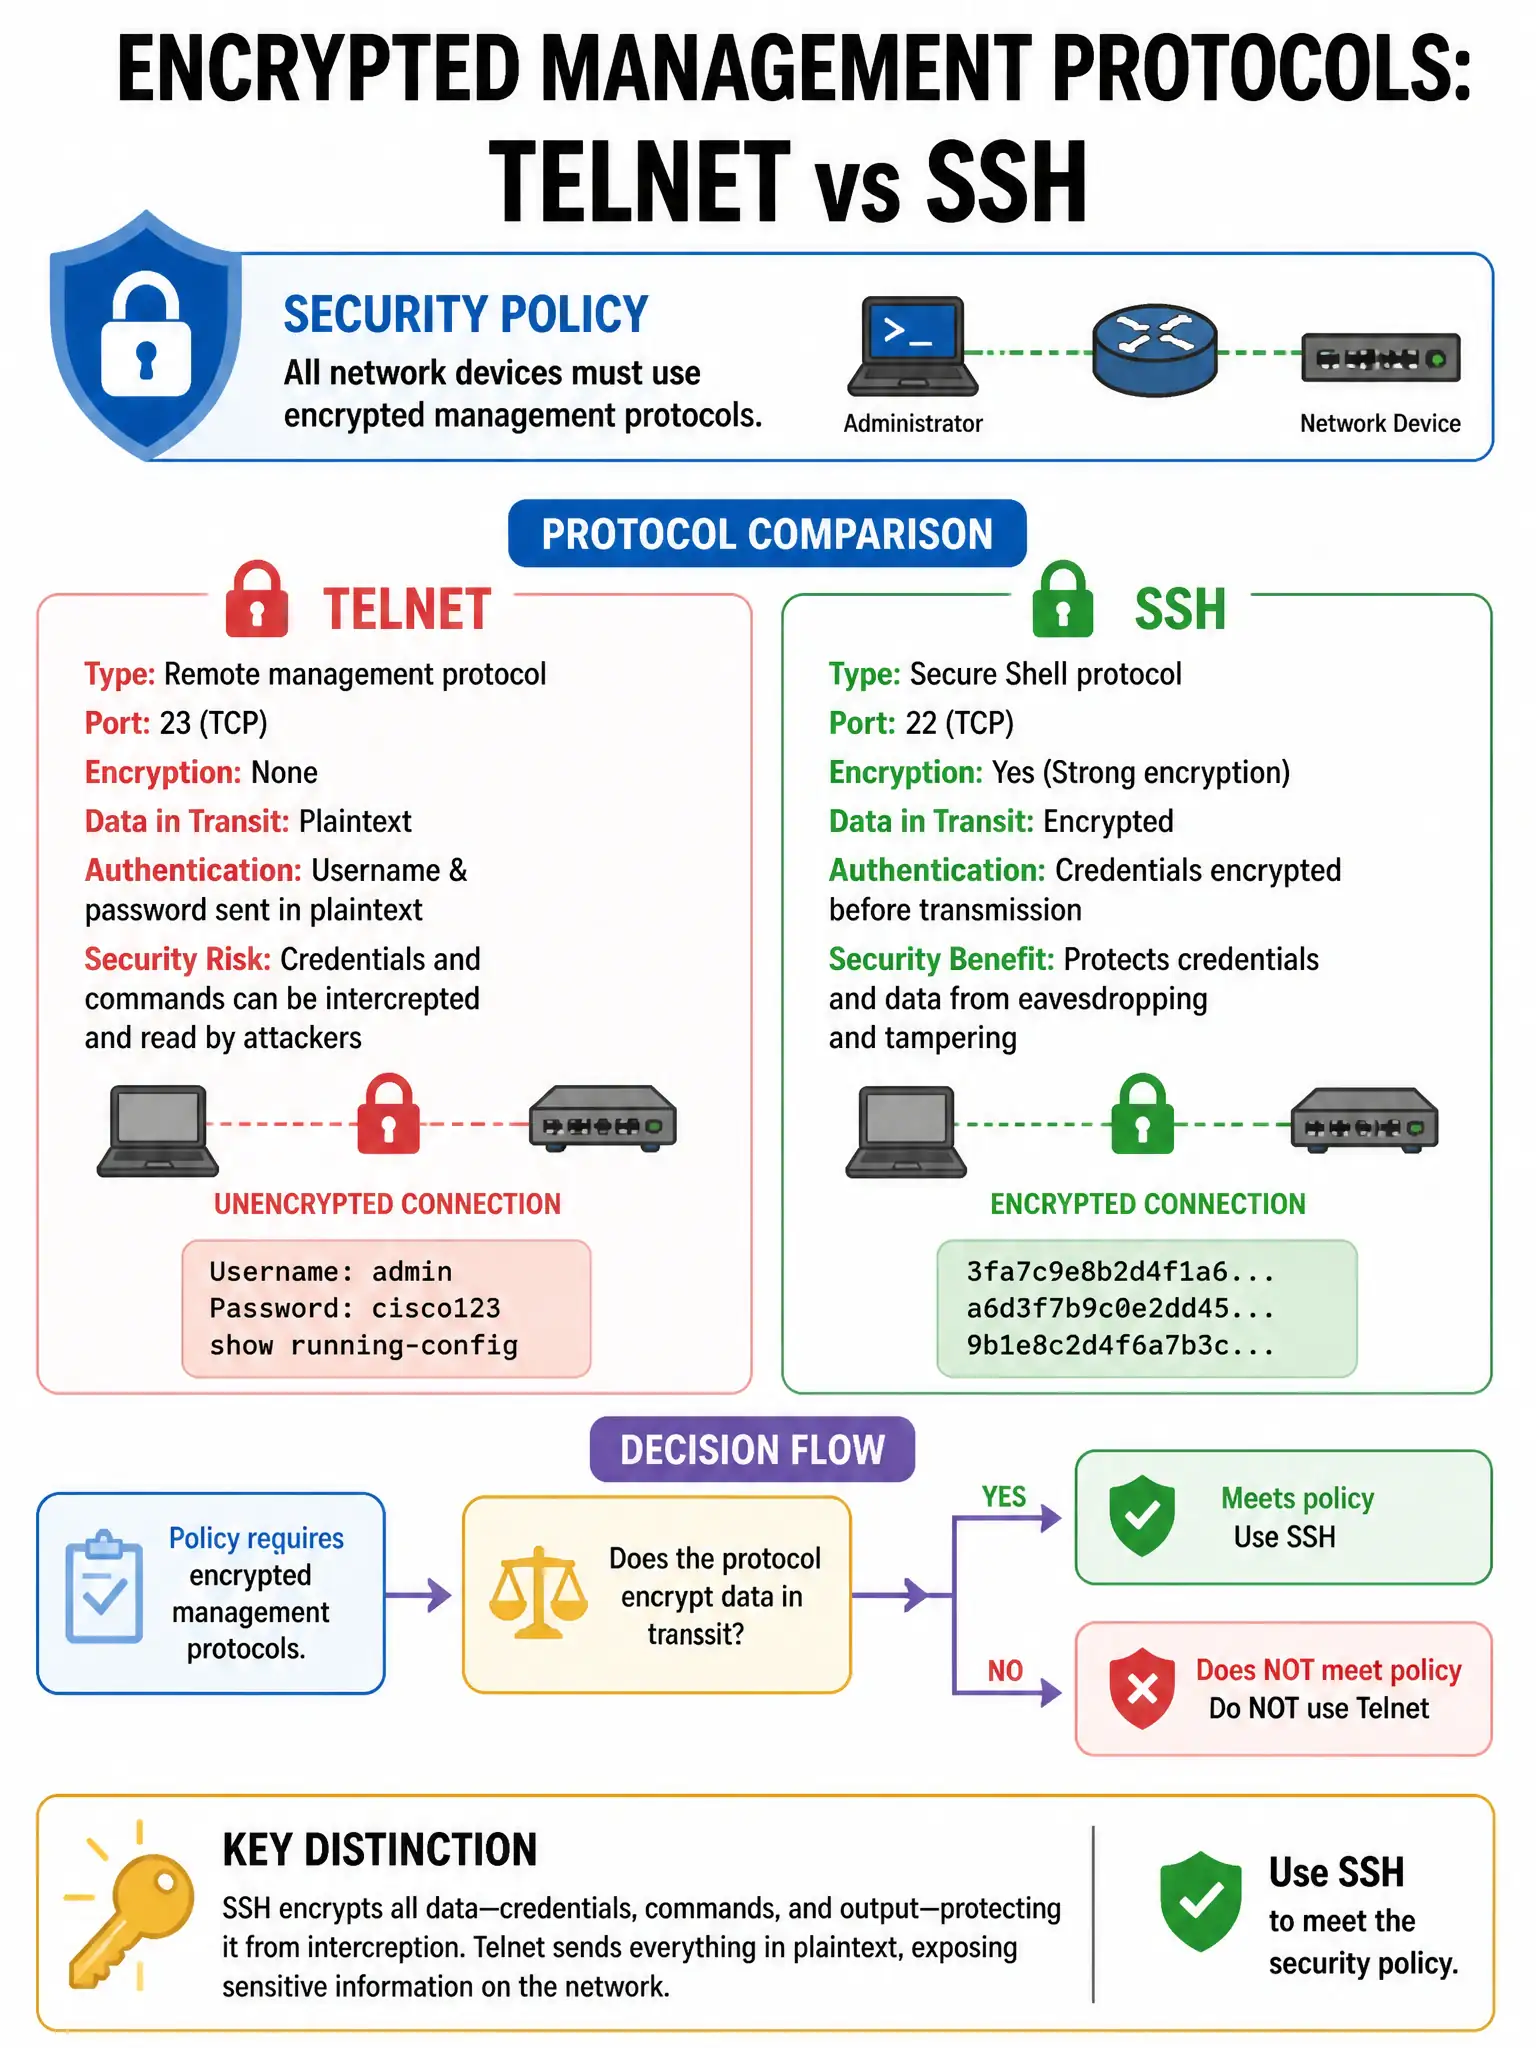
Here's the deal — Telnet sends everything, including usernames and passwords, in cleartext, so anyone sniffing the network can grab them. SSH encrypts authentication and session data using strong key exchange, which is why you use it for management.
Full Explanation
Correctly, Telnet transmits all data, including credentials, in cleartext, while SSH provides encrypted authentication and session data with strong key exchange. Telnet sends usernames, passwords, and commands as plaintext, so anyone with network access can capture credentials via packet sniffing; SSH encrypts the entire session, including credentials, using public-key cryptography. The claim that Telnet uses port 23 and encrypts credentials but not session data is wrong because Telnet encrypts nothing; it is a plaintext protocol from credentials to every typed character. The claim that both protocols encrypt data, with SSH adding compression, is wrong because Telnet does not encrypt data; that is the fundamental security difference. The claim that Telnet is deprecated and no longer supported on modern devices is wrong because Telnet is still supported on many devices; it is deprecated for security reasons but not removed from all equipment.