
A security team is evaluating network access control solutions. What is the primary limitation of using only MAC address filtering for network access control?
Select an answer to reveal the explanation.
Short Explanation
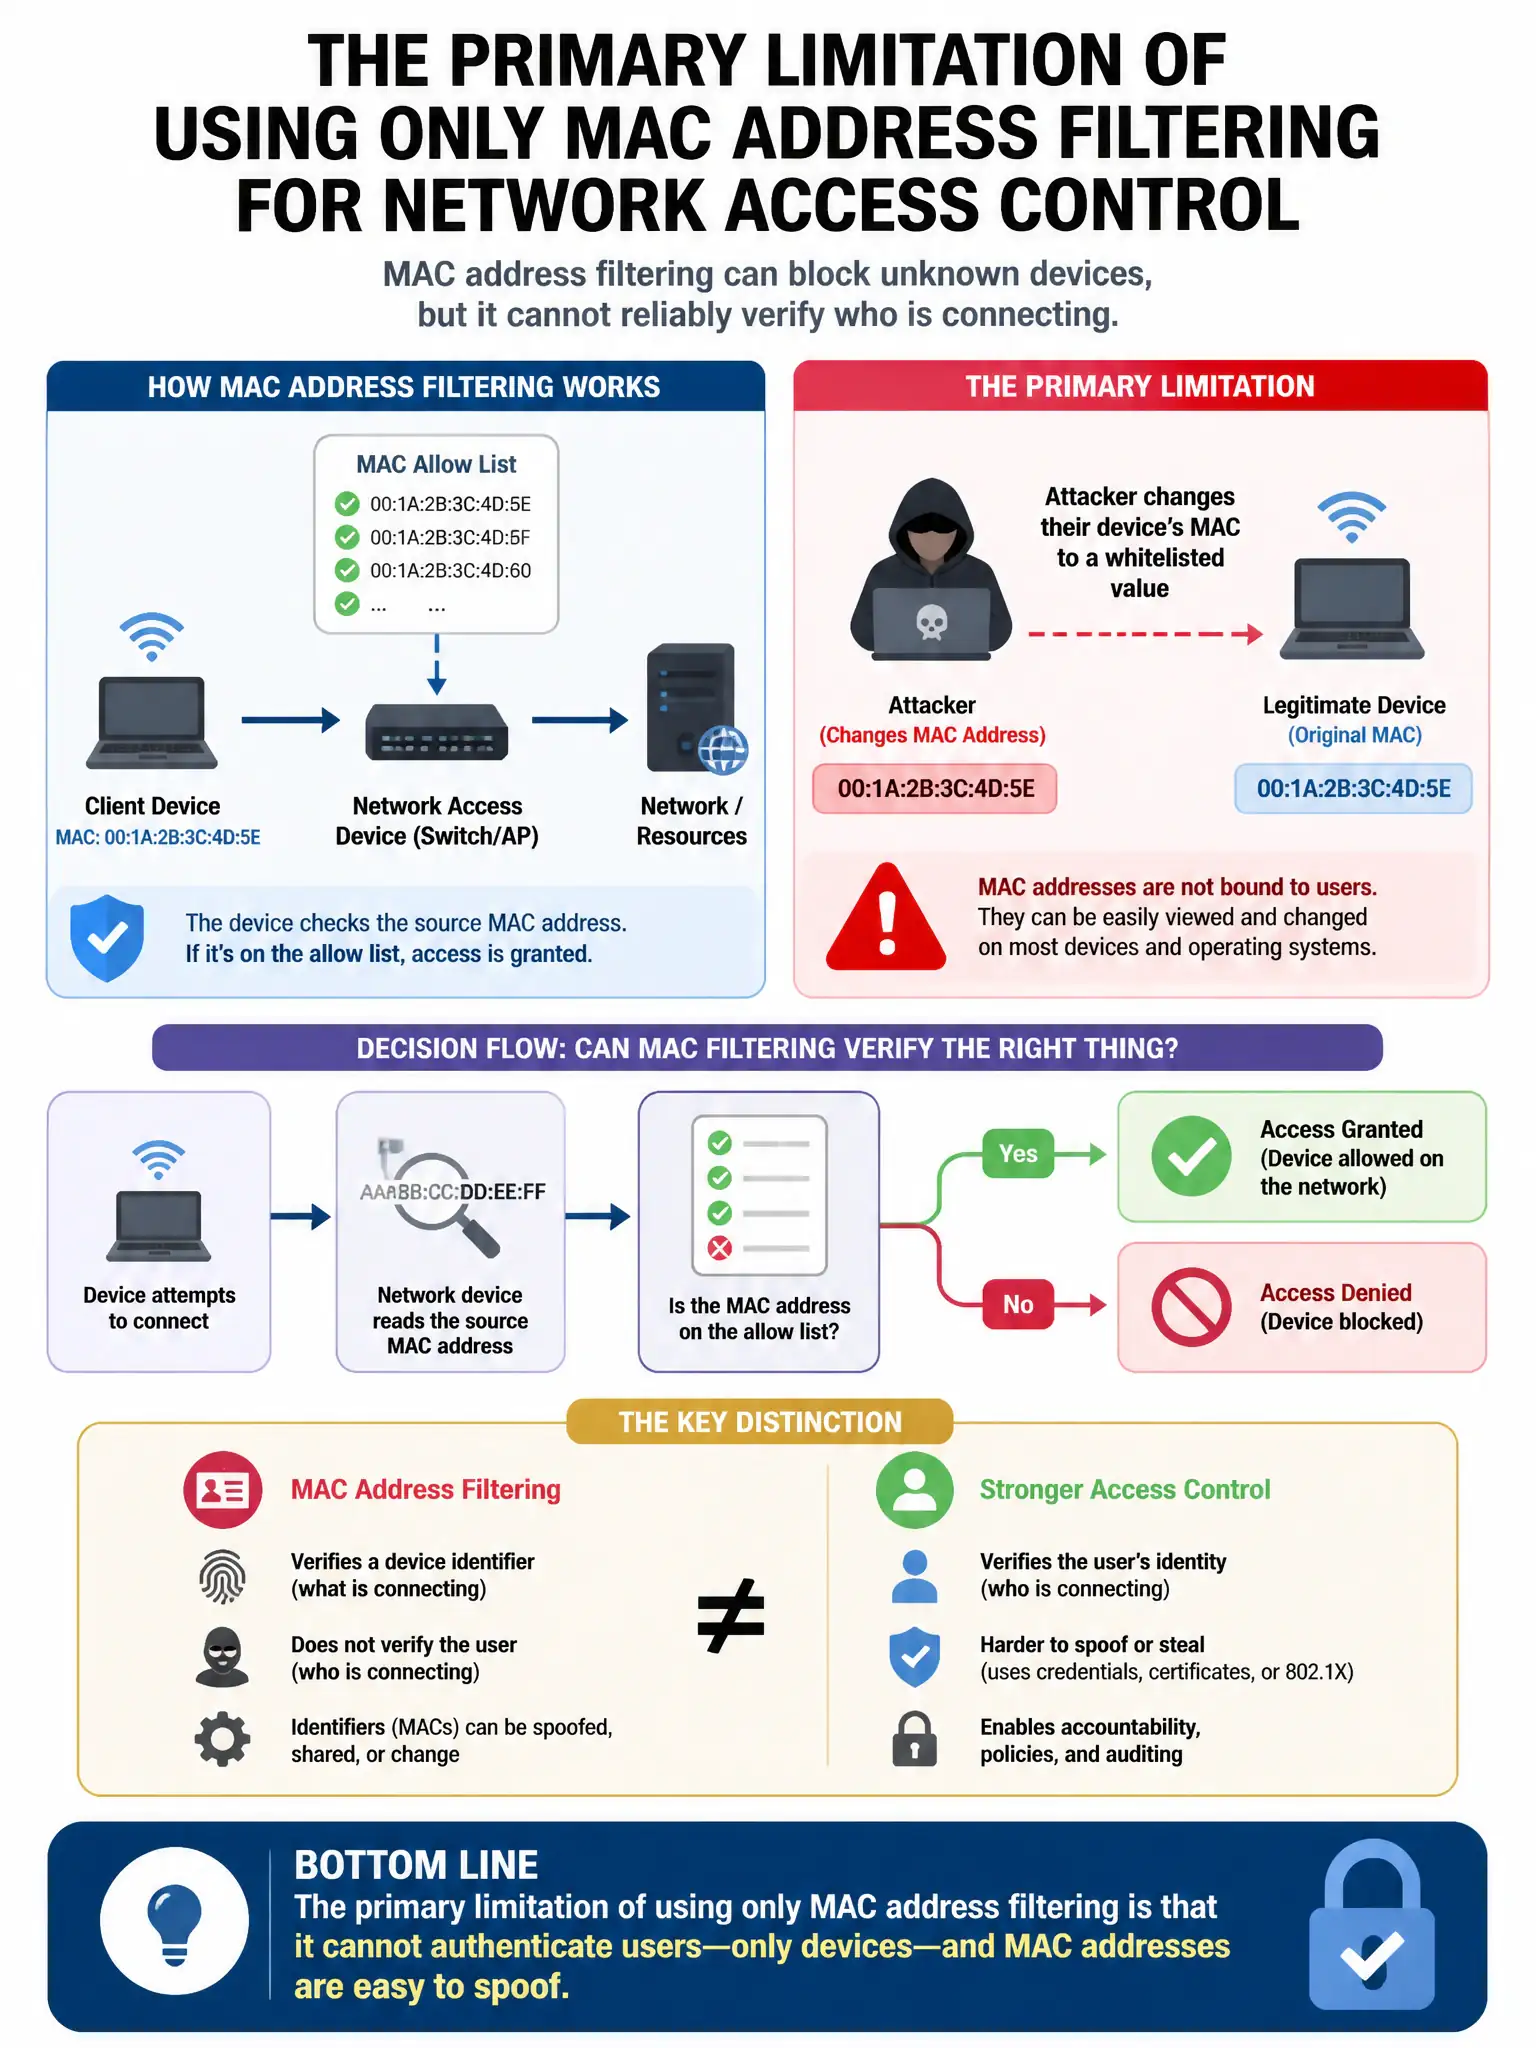
Here's the deal — MAC filtering fails because MAC addresses are sent in cleartext in Ethernet frames, so an attacker can sniff a legitimate device's MAC and spoof it to get through. You can't trust a MAC address as a real access control.
Full Explanation
MAC addresses can be easily spoofed by an attacker who captures a legitimate device's MAC address from network traffic. MAC addresses are transmitted in cleartext in Ethernet frames, so an attacker can capture a legitimate device's MAC address using passive sniffing and then configure their own NIC to use that MAC address, bypassing MAC-based filtering. The option claiming MAC address filtering requires expensive hardware upgrades to all network switches is wrong because MAC filtering is a standard switch feature requiring no special hardware upgrades. The option claiming MAC address filtering is incompatible with IPv6 networks is wrong because MAC addresses operate at Layer 2 and function the same way regardless of IPv4 or IPv6 at Layer 3. The option claiming MAC address filtering requires a RADIUS server for each network segment is wrong because simple MAC filtering can be done with static tables on the switch itself; RADIUS integration is optional for advanced dynamic port authentication.