
An organization is designing its network security architecture and the CISO requires separation between the management plane of network devices and the data plane. What does this separation achieve?
Select an answer to reveal the explanation.
Short Explanation
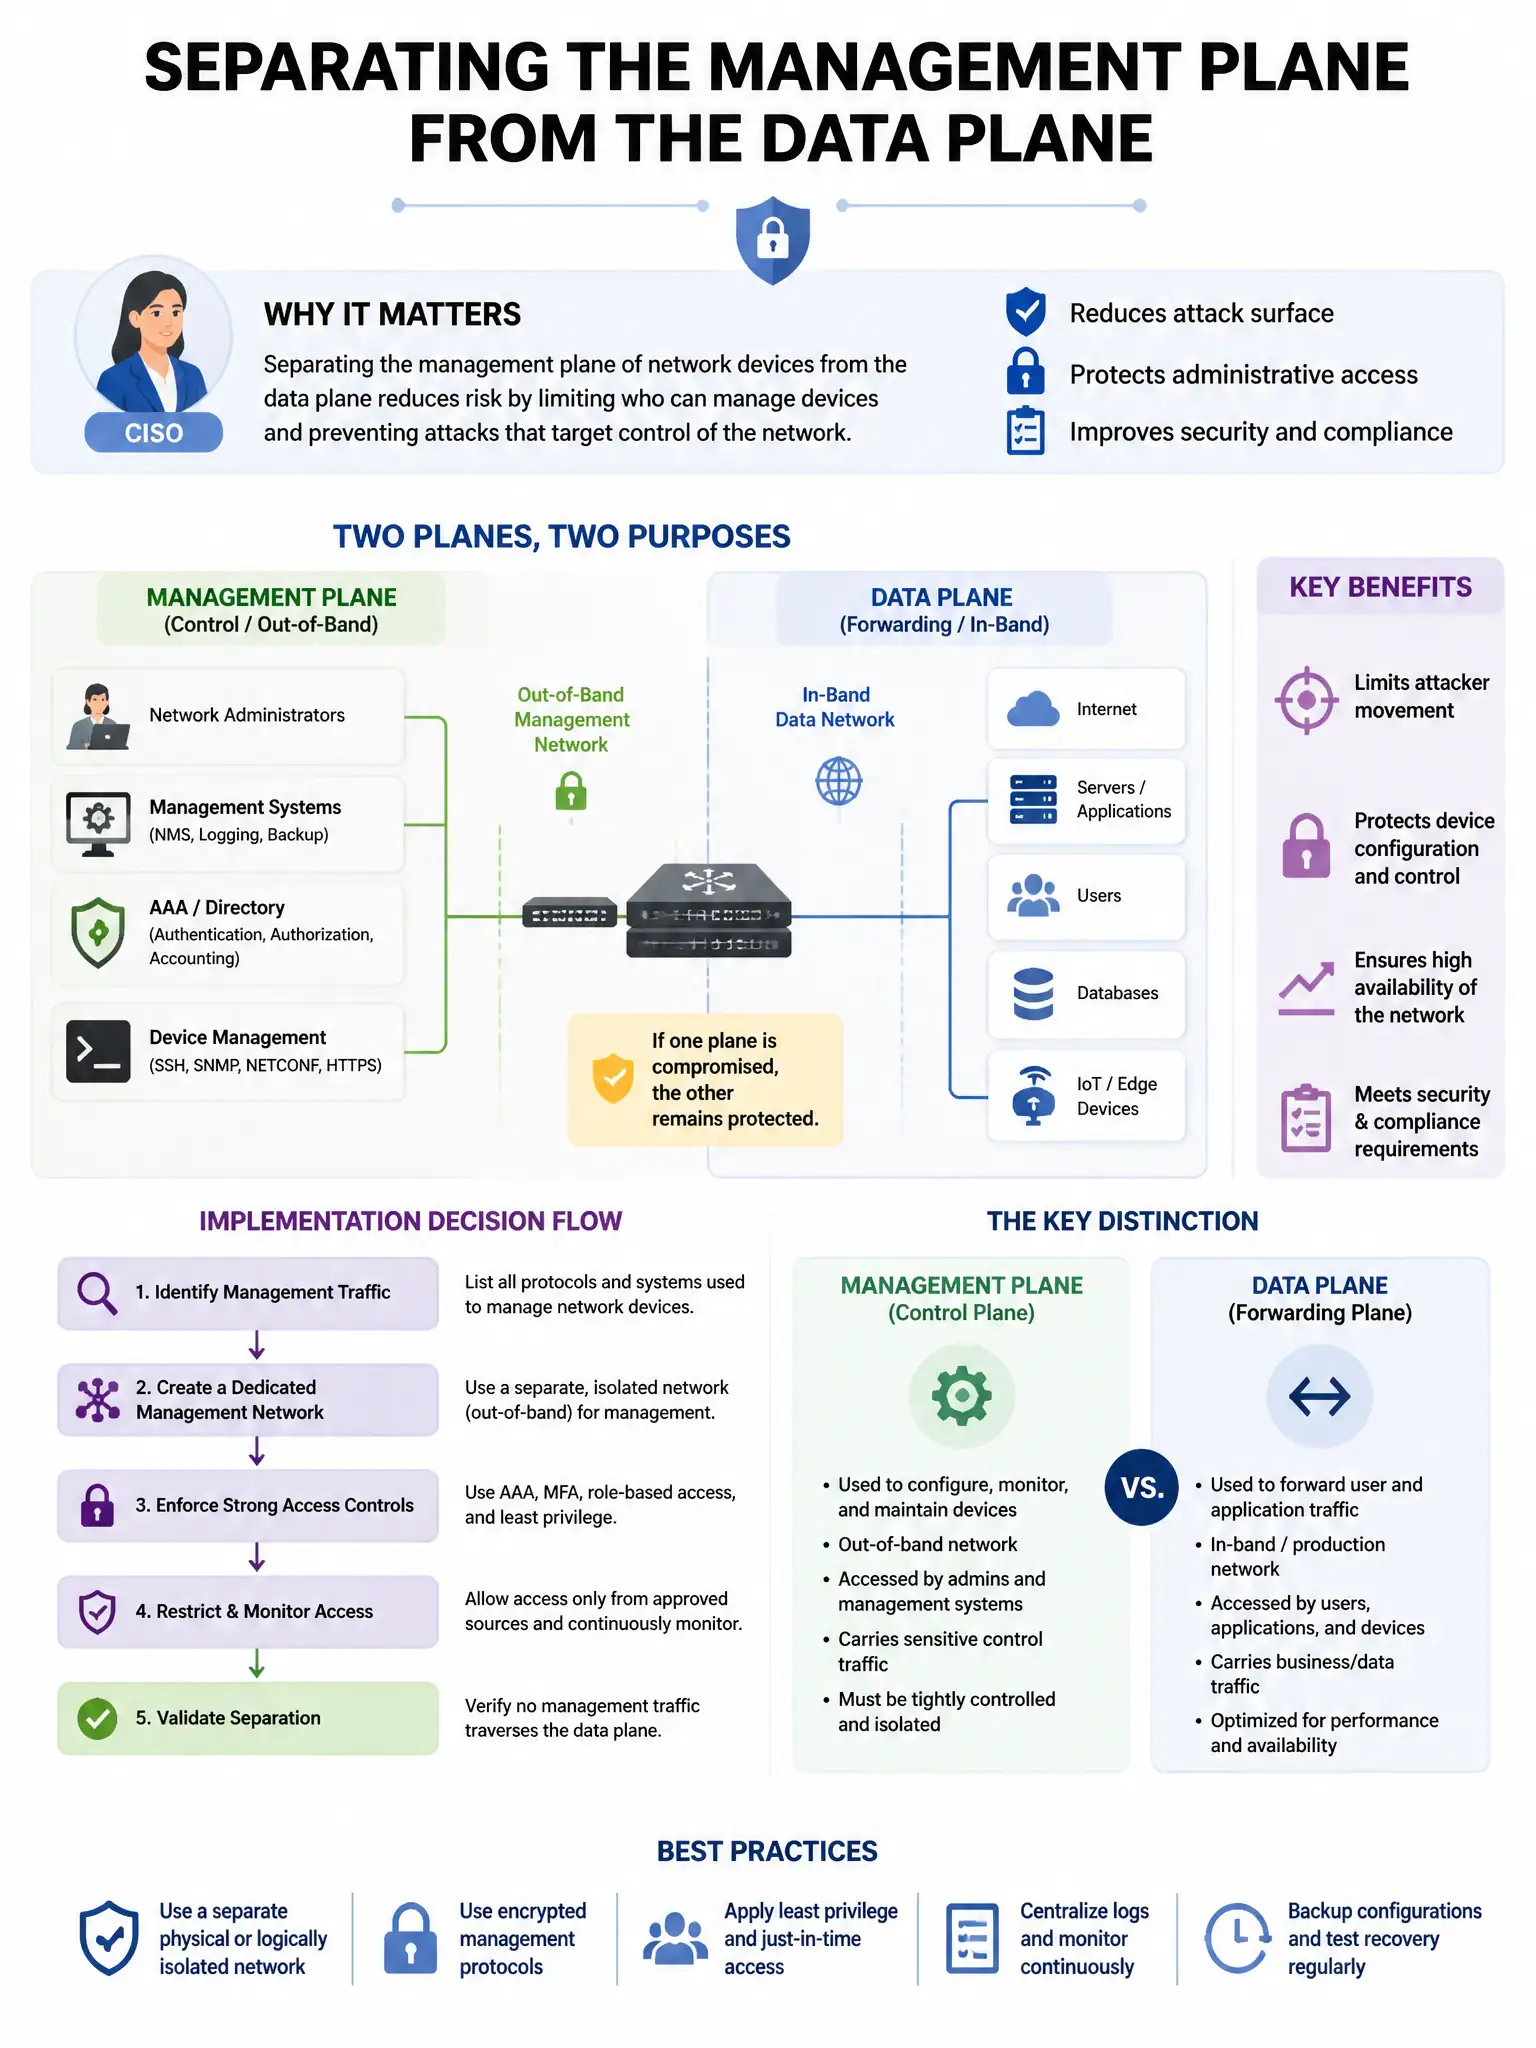
Here's the deal — you separate the management plane from the data plane so management traffic like SSH, SNMP, and logging rides a dedicated out-of-band path. That way, even if production traffic is compromised, attackers can't reach device management.
Full Explanation
Separating the management plane from the data plane ensures that management traffic such as SSH, SNMP, logging, and console access uses a dedicated out-of-band path, so compromise of data-plane traffic does not affect device management. The throughput claim is wrong because plane separation is a security architecture decision, not a performance optimization. The cheaper hardware claim is wrong because plane separation may require additional management infrastructure, potentially increasing cost. The faster forwarding claim is wrong because modern network hardware already achieves data-plane performance through ASIC forwarding regardless of management plane separation.