
A security engineer is deploying a SIEM and needs to onboard Windows Domain Controller logs. Which Windows Security event category must be enabled via Group Policy to capture user account management events such as group membership changes?
Select an answer to reveal the explanation.
Short Explanation
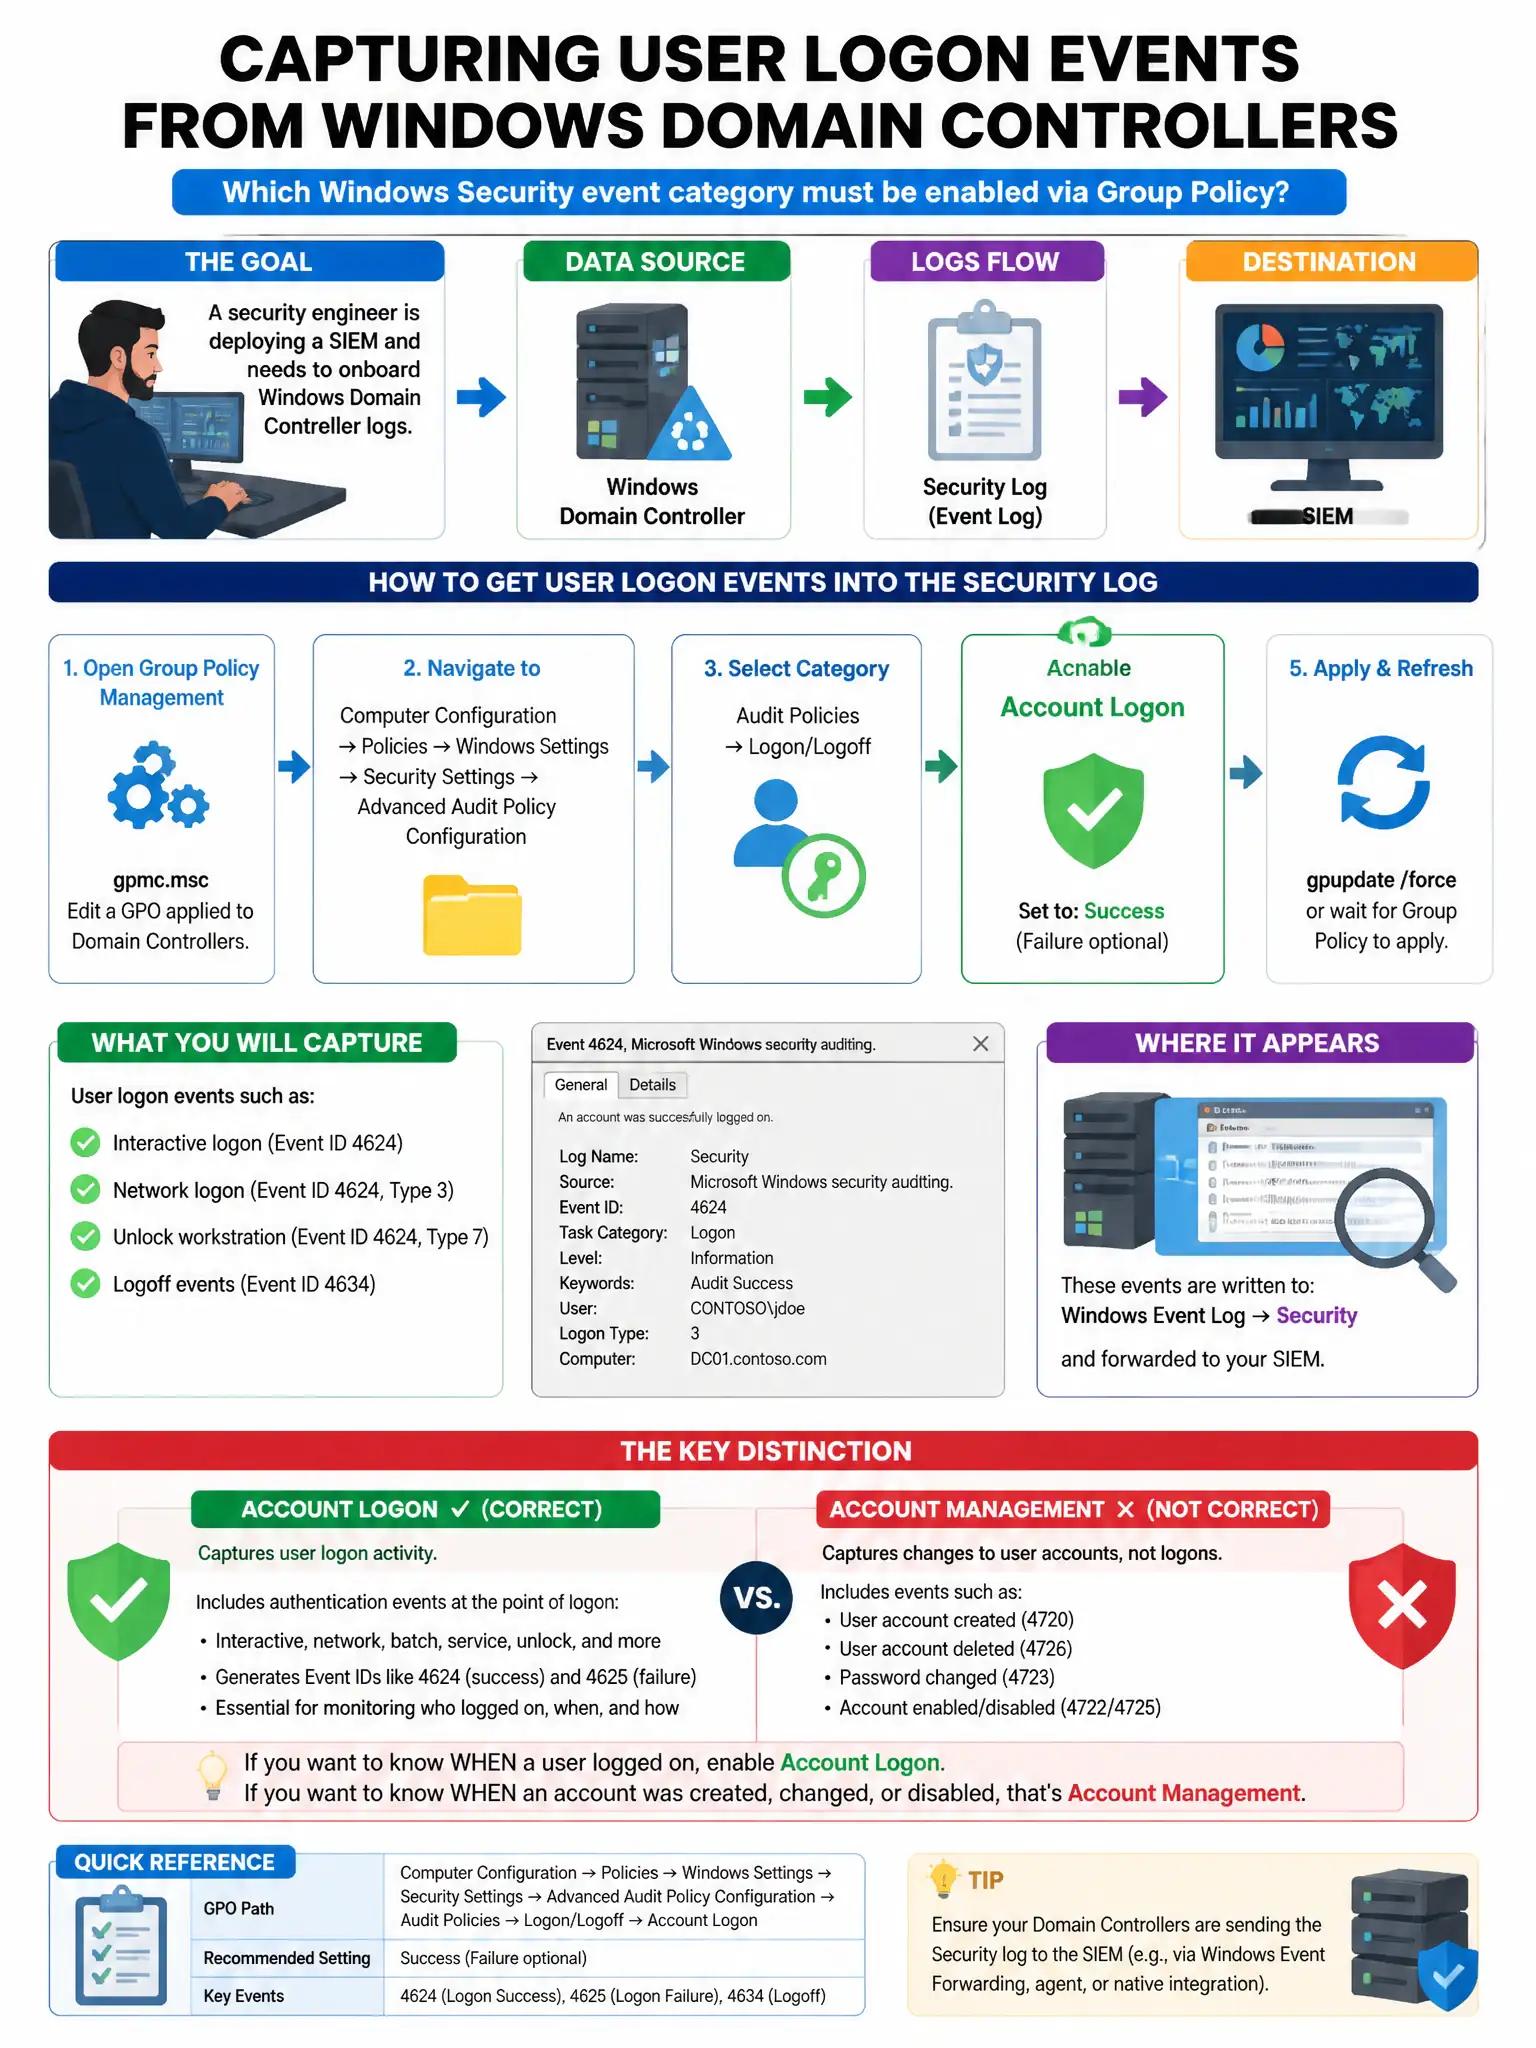
Here's the deal — enable Audit Account Management under the Account Management audit policy category because it captures user account and group changes, including group membership additions, account creation, and account deletion. The other categories track process launches, logons, or object access, not account management.
Full Explanation
Audit Account Management under the Account Management audit policy category is correct because it generates events for user account and group changes including event 4728/4732 for group membership additions, event 4720 for account creation, and event 4726 for account deletion, which are captured under the Account Management audit category in Group Policy. Audit Process Creation under Detailed Tracking is wrong because it generates event 4688 for process launches, not account management events. Audit Logon Events under the Logon/Logoff category is wrong because it captures authentication events such as 4624 and 4625, not account management changes. Audit Object Access under the Object Access category is wrong because it captures file, registry, and Security Account Manager object access attempts, not account management operations.