
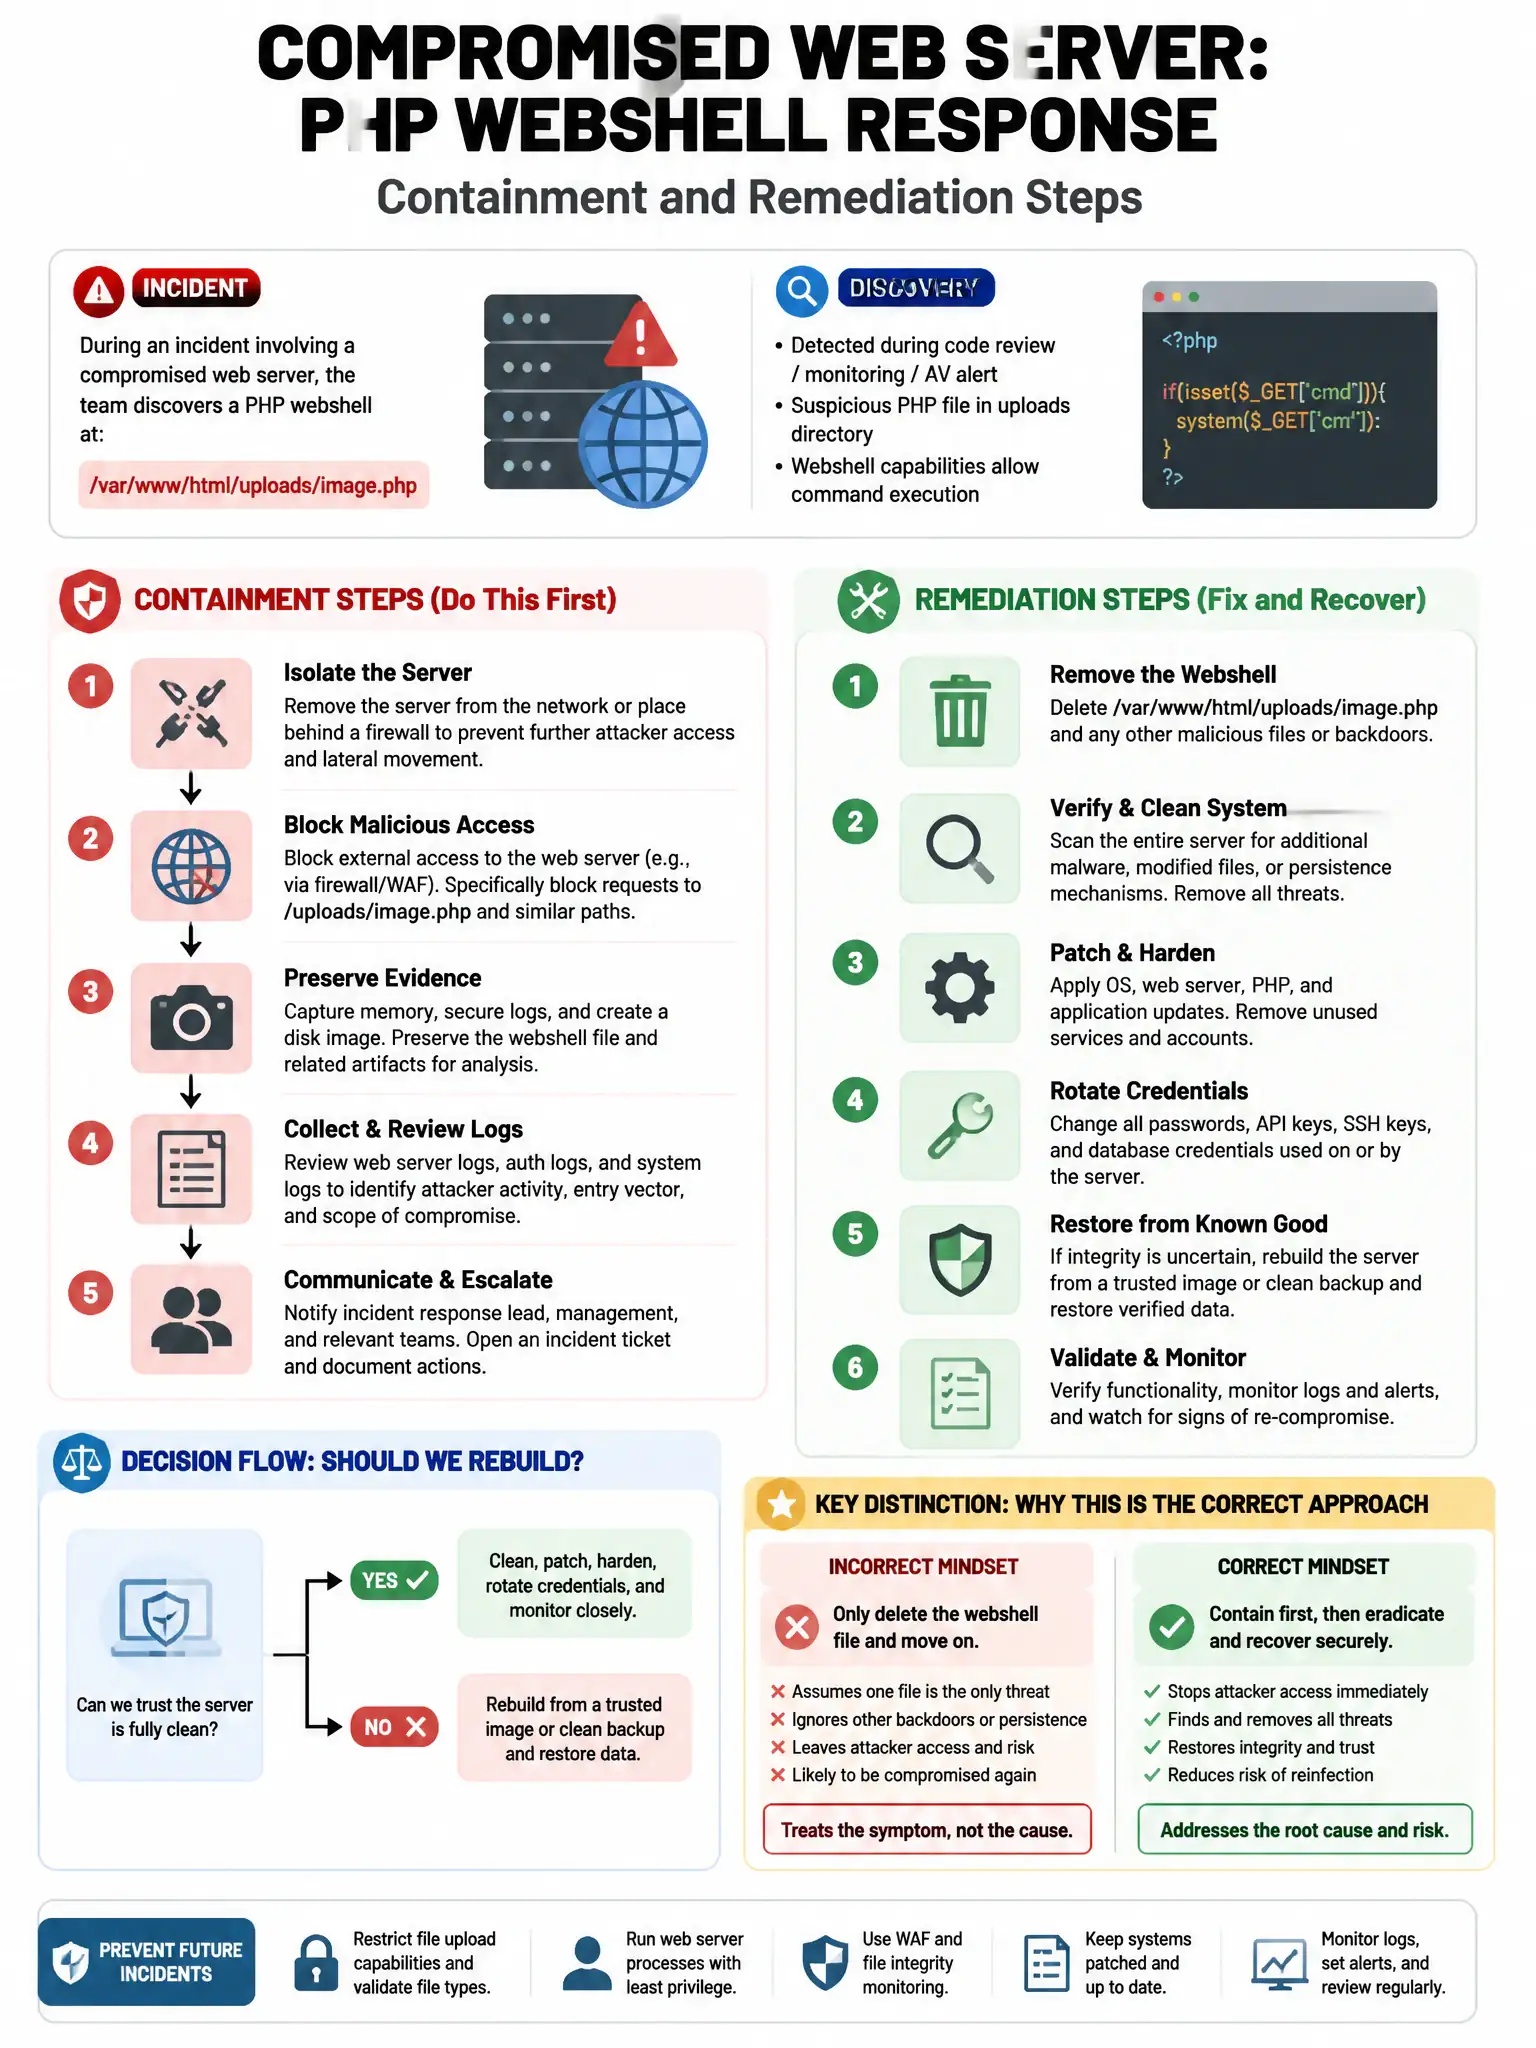
During an incident involving a compromised web server, the team discovers a PHP webshell at '/var/www/html/uploads/image.php'. What containment and remediation steps are required?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to isolate the server, preserve evidence, find how the webshell got uploaded, remove it, patch the upload flaw, and hunt for persistence. Just deleting the file leaves the door open and can wipe forensic clues.
Full Explanation
The correct path is to isolate the server, preserve forensic evidence, identify how the webshell was uploaded (the initial access vector), remove the webshell, patch the upload vulnerability, and review for additional persistence mechanisms. Proper remediation requires understanding the full attack chain — how the webshell was uploaded (often an unrestricted file upload vulnerability), whether the attacker established additional persistence, and patching the root cause — not just removing the visible artifact. The delete-only option is wrong because deleting the webshell without identifying the upload vulnerability leaves the system re-exploitable; it also destroys evidence before forensic analysis. The change-port option is wrong because changing the listening port only obscures the service temporarily; the webshell and underlying vulnerability remain. The rename-and-monitor option is wrong because leaving a webshell active for intelligence gathering without proper controls puts the organization at continued risk and may violate legal obligations.