
A penetration tester discovers a Linux system running Sudo version 1.8.x and attempts 'sudo -u#-1 /bin/bash'. What vulnerability does this exploit?
Select an answer to reveal the explanation.
Short Explanation
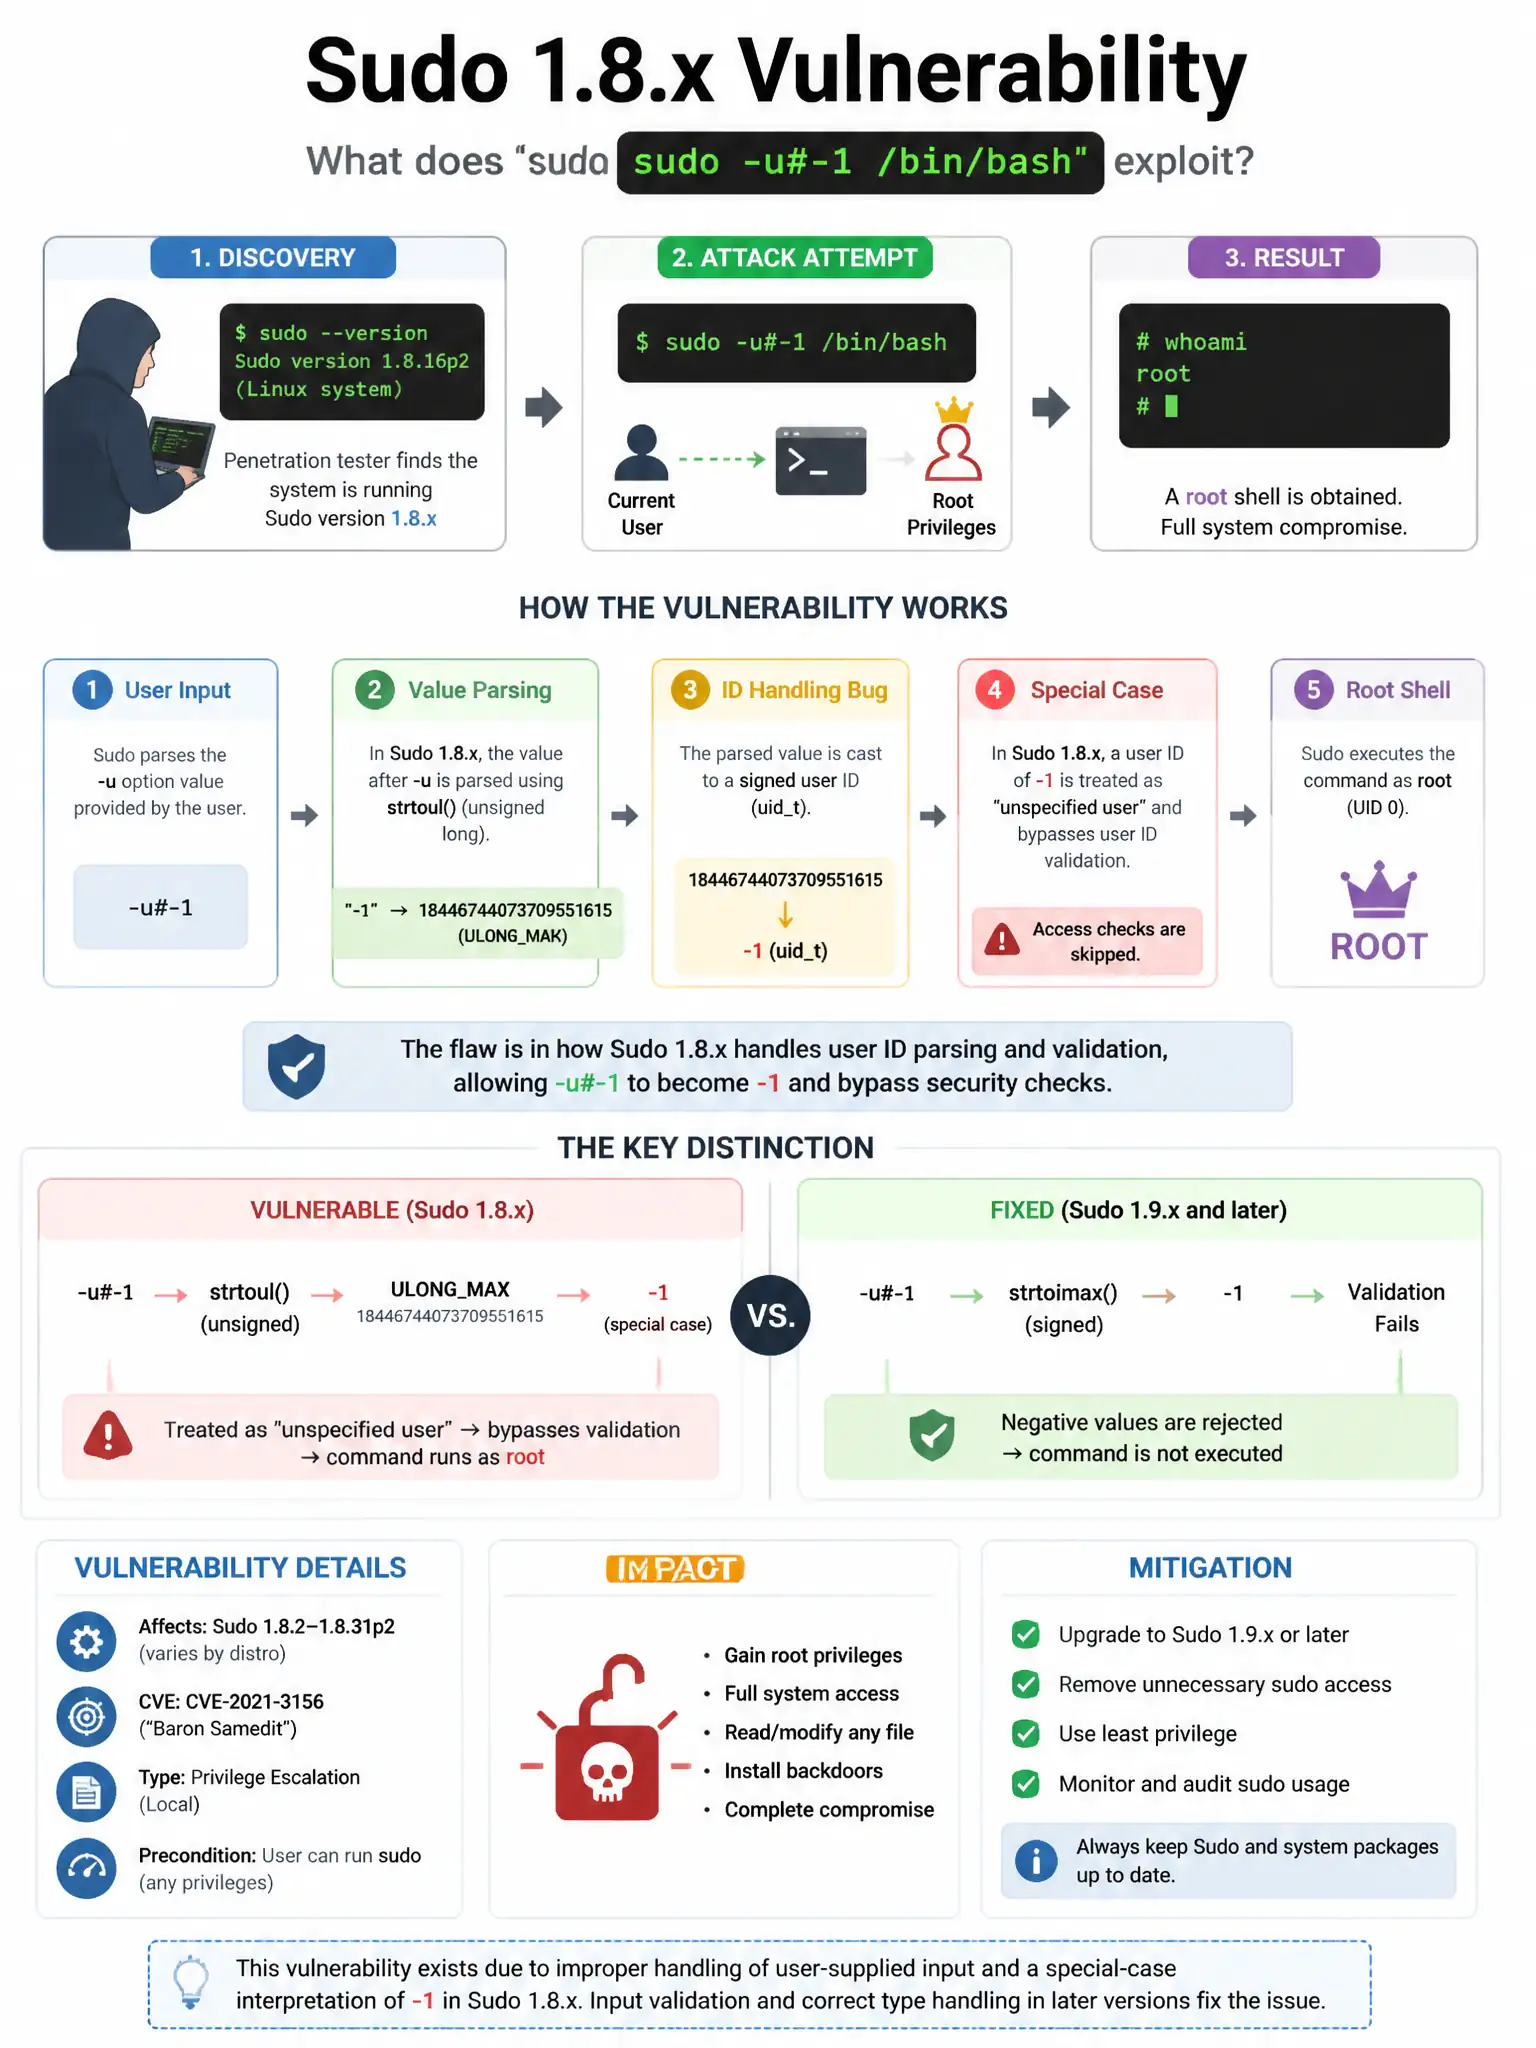
Here's the deal — the Sudo bypass vulnerability is right because specifying UID -1 or 4294967295 can wrap to root and slip past sudo policies that block root. You're exploiting sudo's UID parsing, not the kernel, PAM, or a SUID bit.
Full Explanation
The correct answer is the Sudo bypass vulnerability, CVE-2019-14287, where specifying UID -1 or 4294967295 allows a user to run commands as root even when sudo policy restricts root execution. It works because UID -1 wraps around to UID 0/root in unsigned integer arithmetic, bypassing sudo policies that explicitly exclude root execution and allowing privilege escalation. The Linux kernel privilege escalation via Dirty Cow is wrong because Dirty Cow is a kernel race condition vulnerability in memory copy-on-write, not a Sudo bypass. The PAM authentication bypass option is wrong because this is not a PAM bypass; it exploits how Sudo handles UID conversion. The SUID bit on /bin/bash option is wrong because the exploit targets Sudo's UID parsing, not a SUID bit on bash.