
A Linux system administrator wants to implement mandatory access control (MAC) to enforce security policies on running processes, preventing privilege escalation even if a process is compromised. Which technology implements this?
Select an answer to reveal the explanation.
Short Explanation
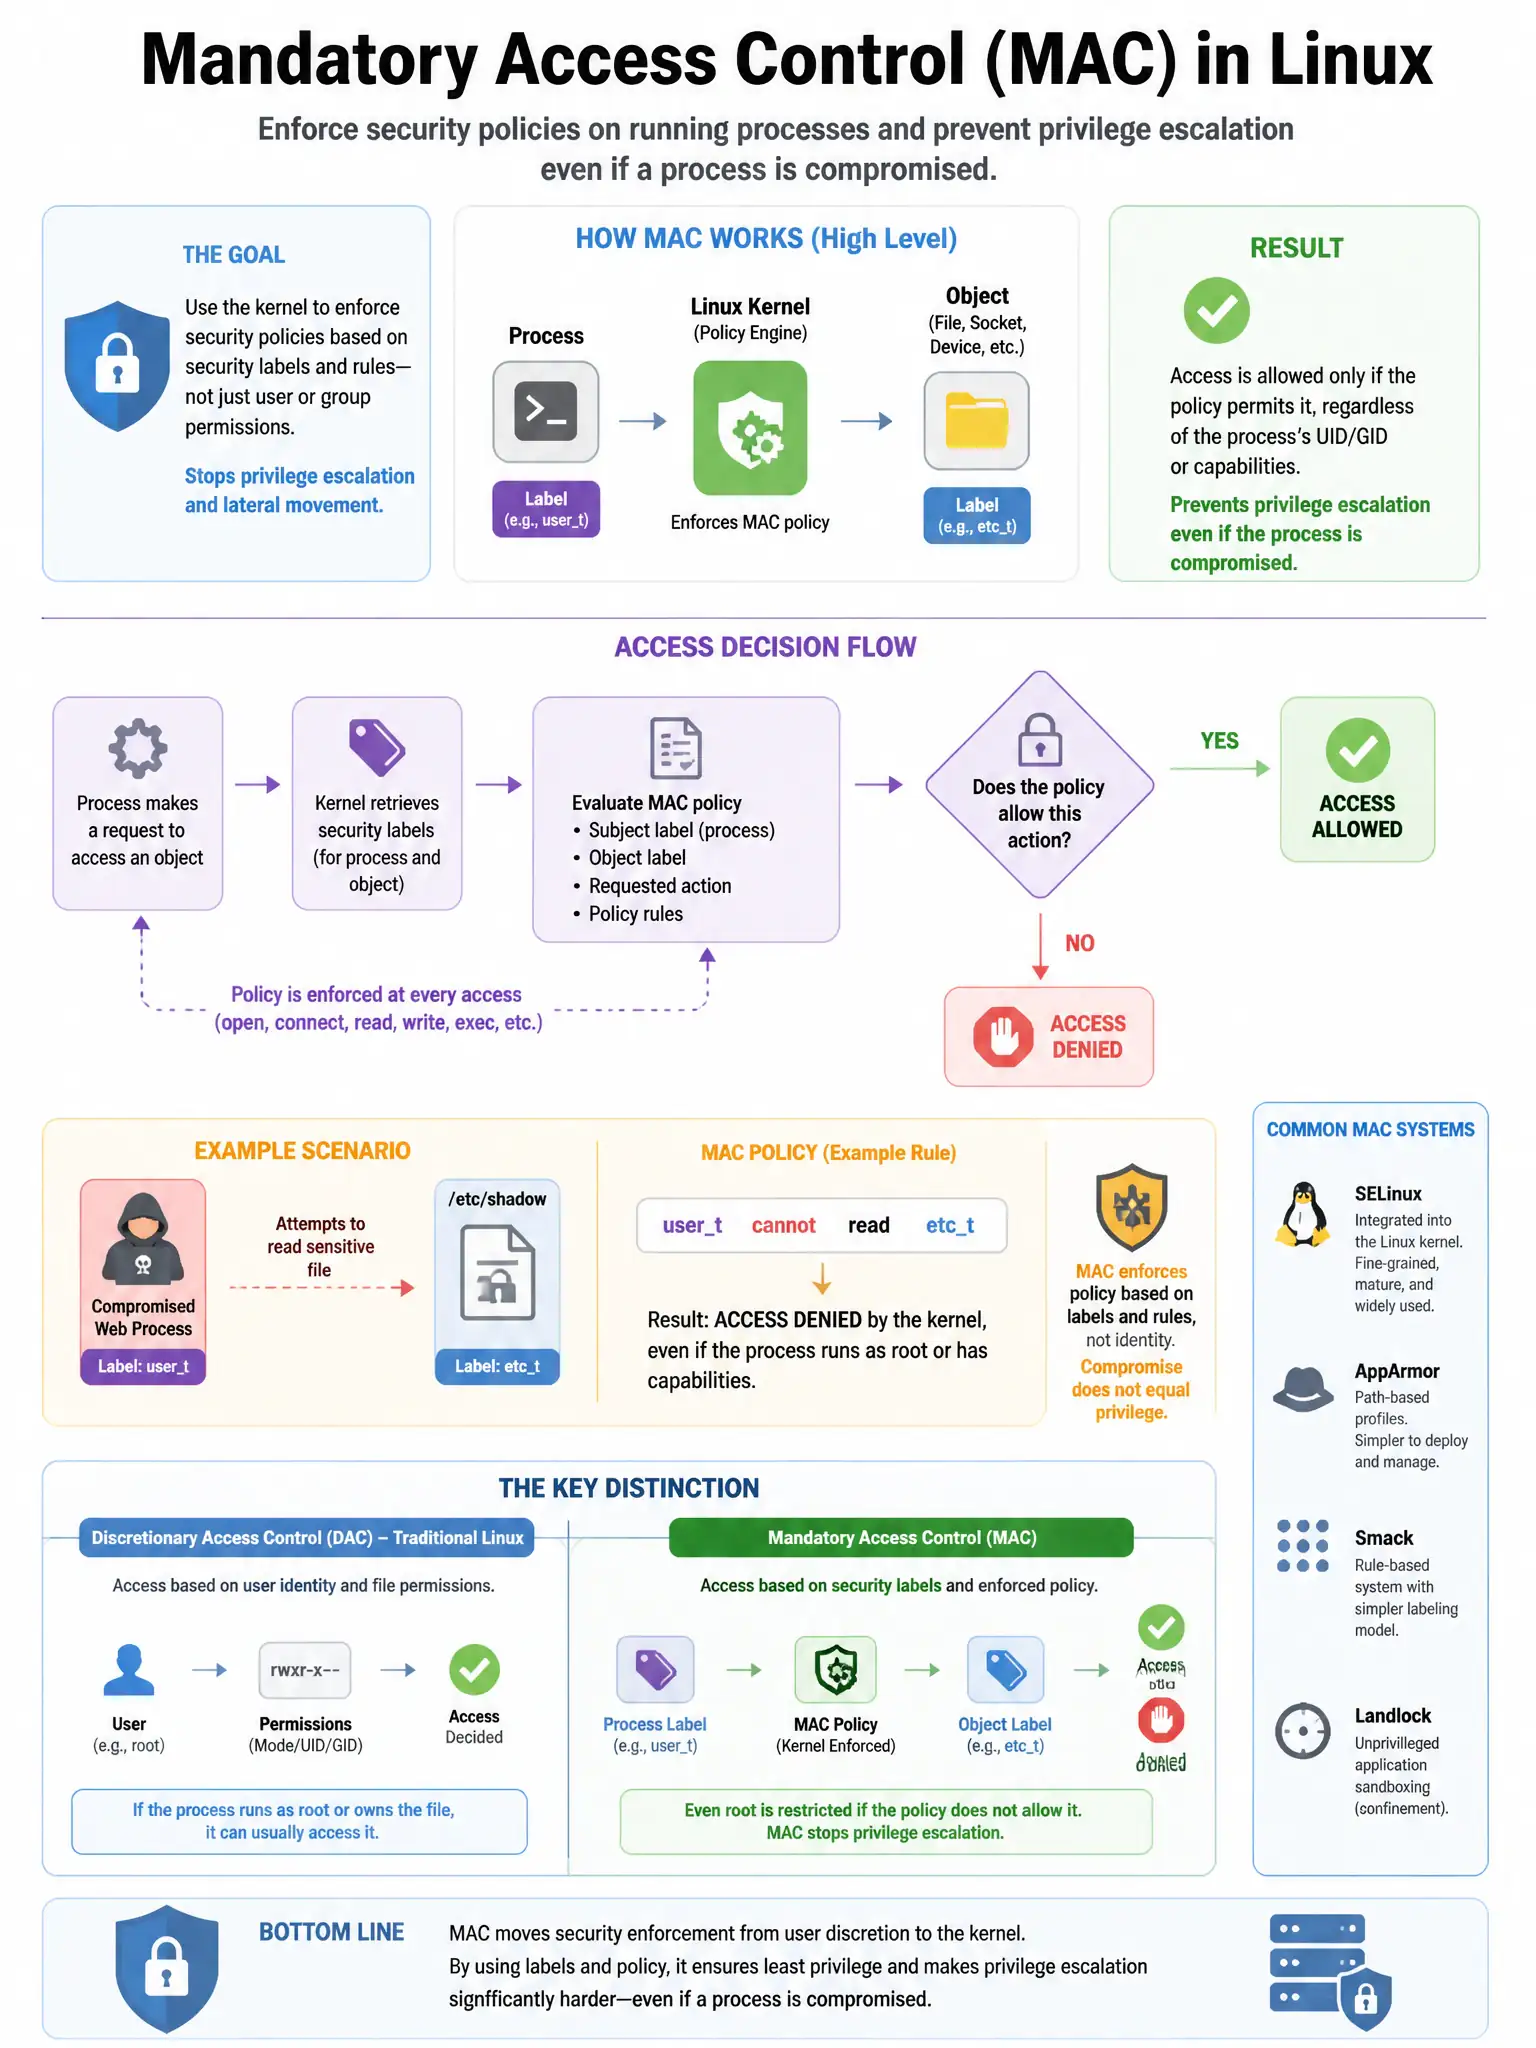
Here's the deal — you need SELinux or AppArmor because they implement MAC, letting admin-defined policy constrain each process's access even if the process is compromised. File permissions and ACLs are DAC, so a compromised owner process can still bypass them.
Full Explanation
SELinux (Security-Enhanced Linux) or AppArmor enforcing security policy profiles that constrain what processes can access is correct because they implement MAC, where security policies defined by administrators (not the process owner) enforce what resources each process can access, limiting the damage from compromised processes regardless of their runtime user. Discretionary access control (DAC) via file permissions and ACLs is wrong because DAC relies on the object owner setting permissions; a compromised process running as the owner can bypass DAC controls. sudo configuration with NOPASSWD for specific commands is wrong because sudo controls command execution elevation, not what a running process can access during execution. PAM (Pluggable Authentication Modules) for authentication policy is wrong because PAM handles authentication module configuration, not runtime process access controls.