
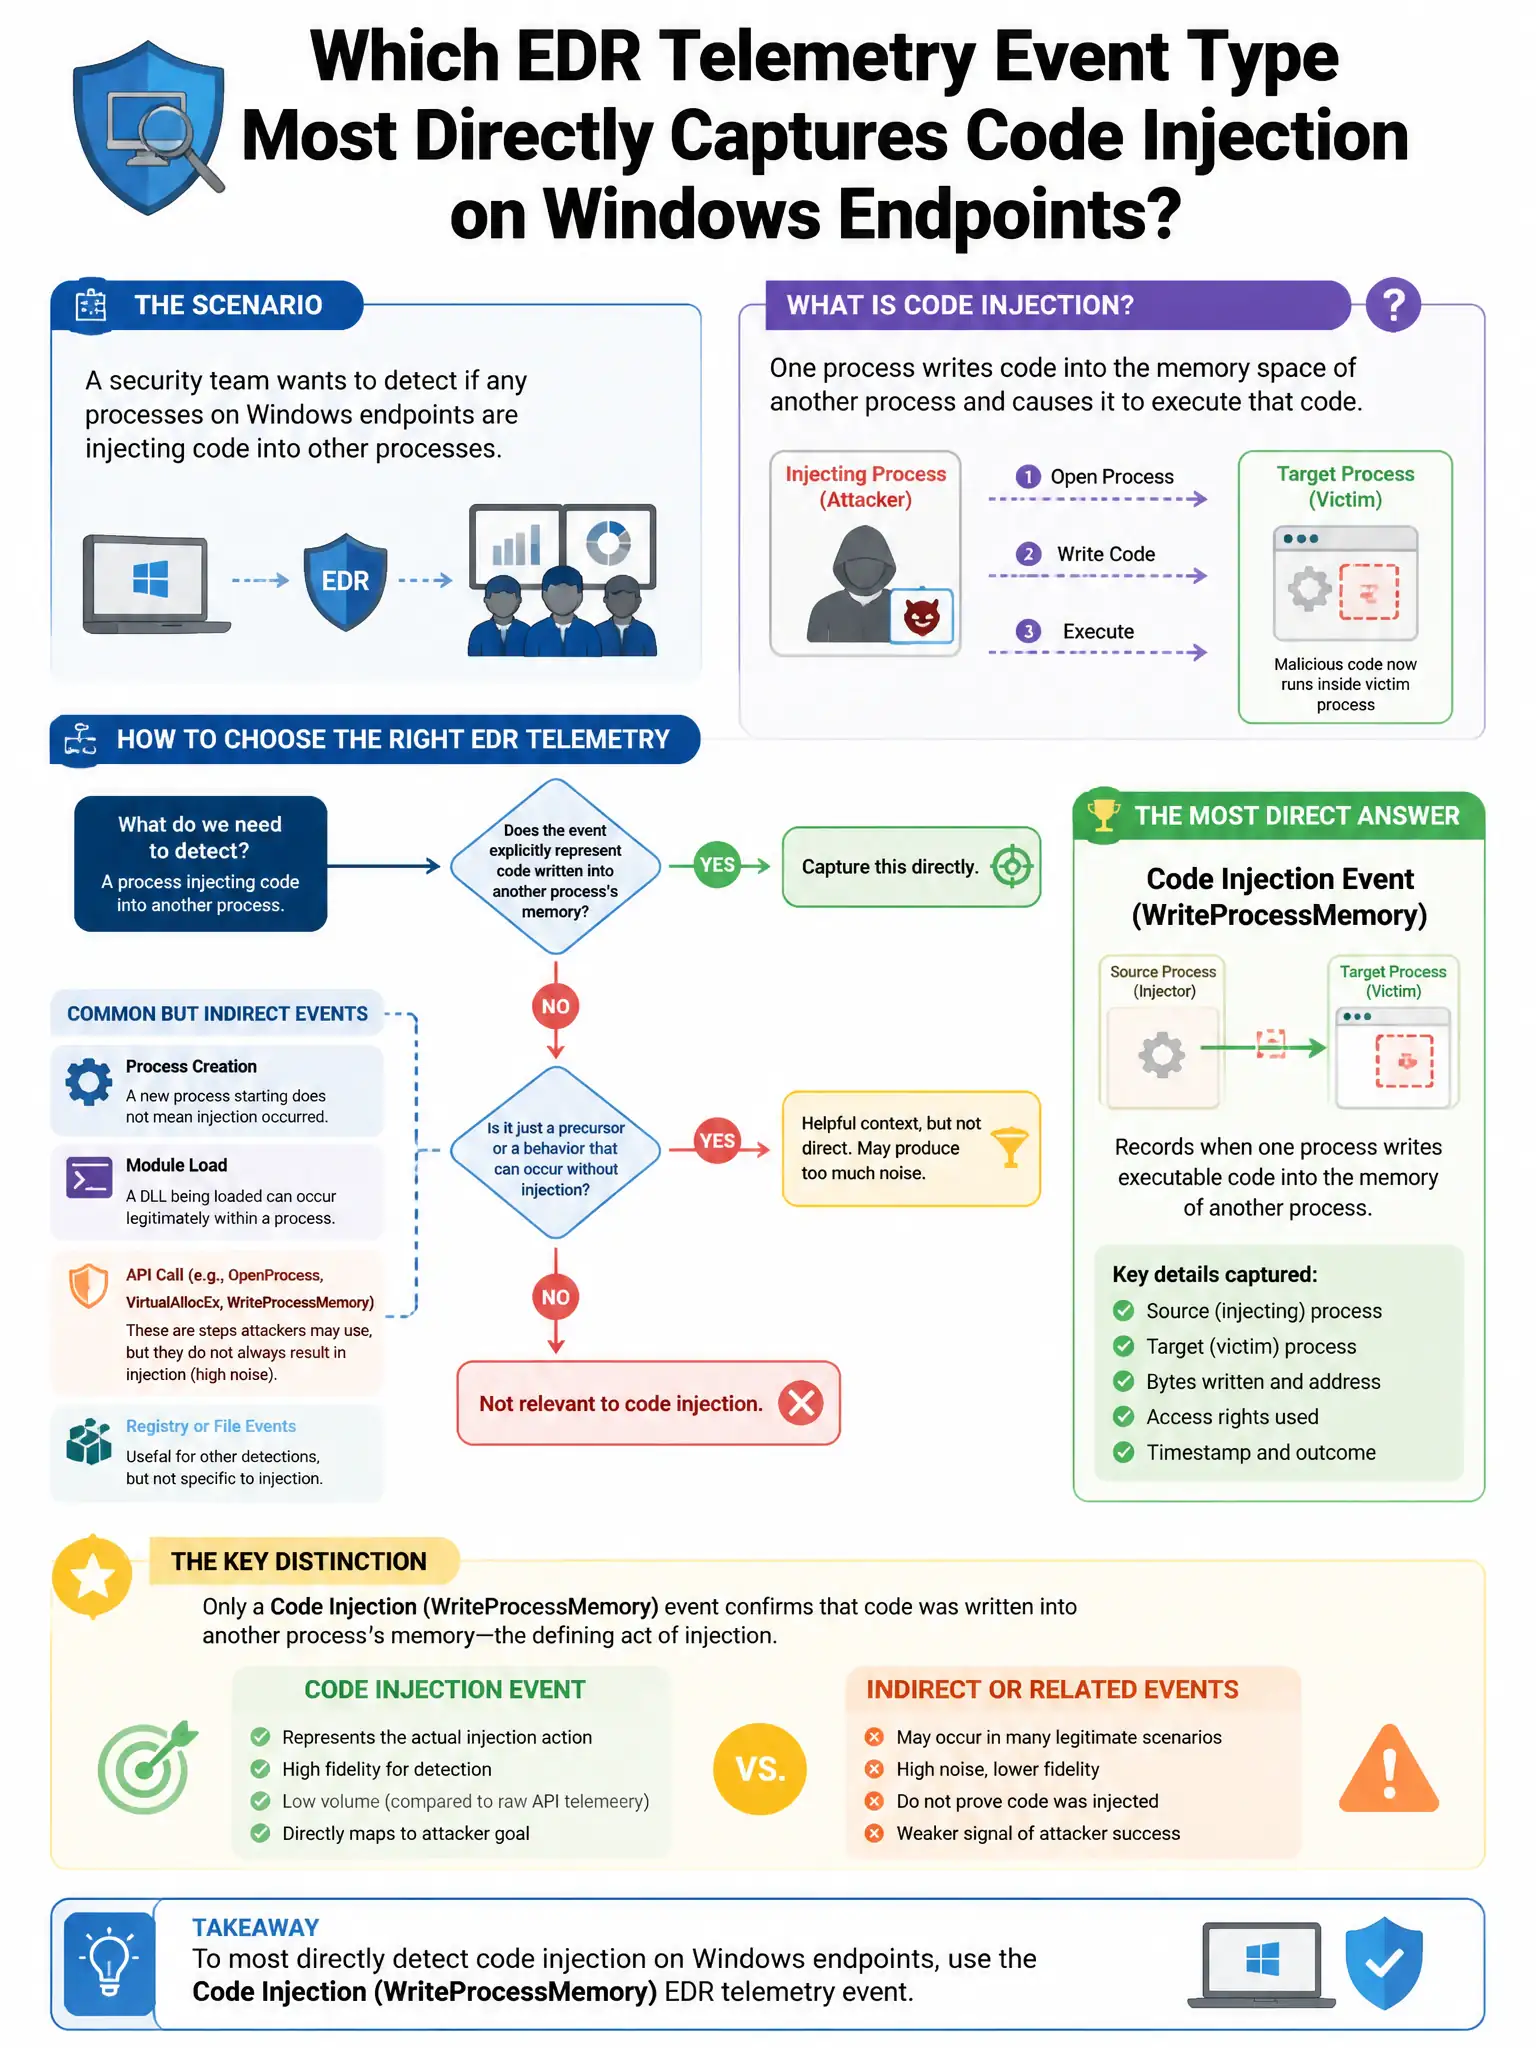
A security team wants to detect if any processes on Windows endpoints are injecting code into other processes. Which EDR telemetry event type most directly captures this activity?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want telemetry that catches the actual injection mechanics. When a process opens another process and writes into its memory, that's the direct signal of code injection.
Full Explanation
The correct choice is process open (OpenProcess) and cross-process memory write API calls targeting other process address spaces, because process injection requires the injecting process to call OpenProcess to gain a handle to the target, then VirtualAllocEx and WriteProcessMemory to write code into the target's memory space; EDR telemetry capturing these API calls directly surfaces injection attempts. File creation events for new executables dropped to disk are wrong because file creation events capture files written to disk; fileless injection does not necessarily involve file creation. Registry modification events under HKLM\SOFTWARE are wrong because registry modifications may accompany some persistence techniques but do not directly capture process injection. Network connection events showing outbound connections are wrong because network connections may indicate C2 communication after injection but do not reveal the injection activity itself.