
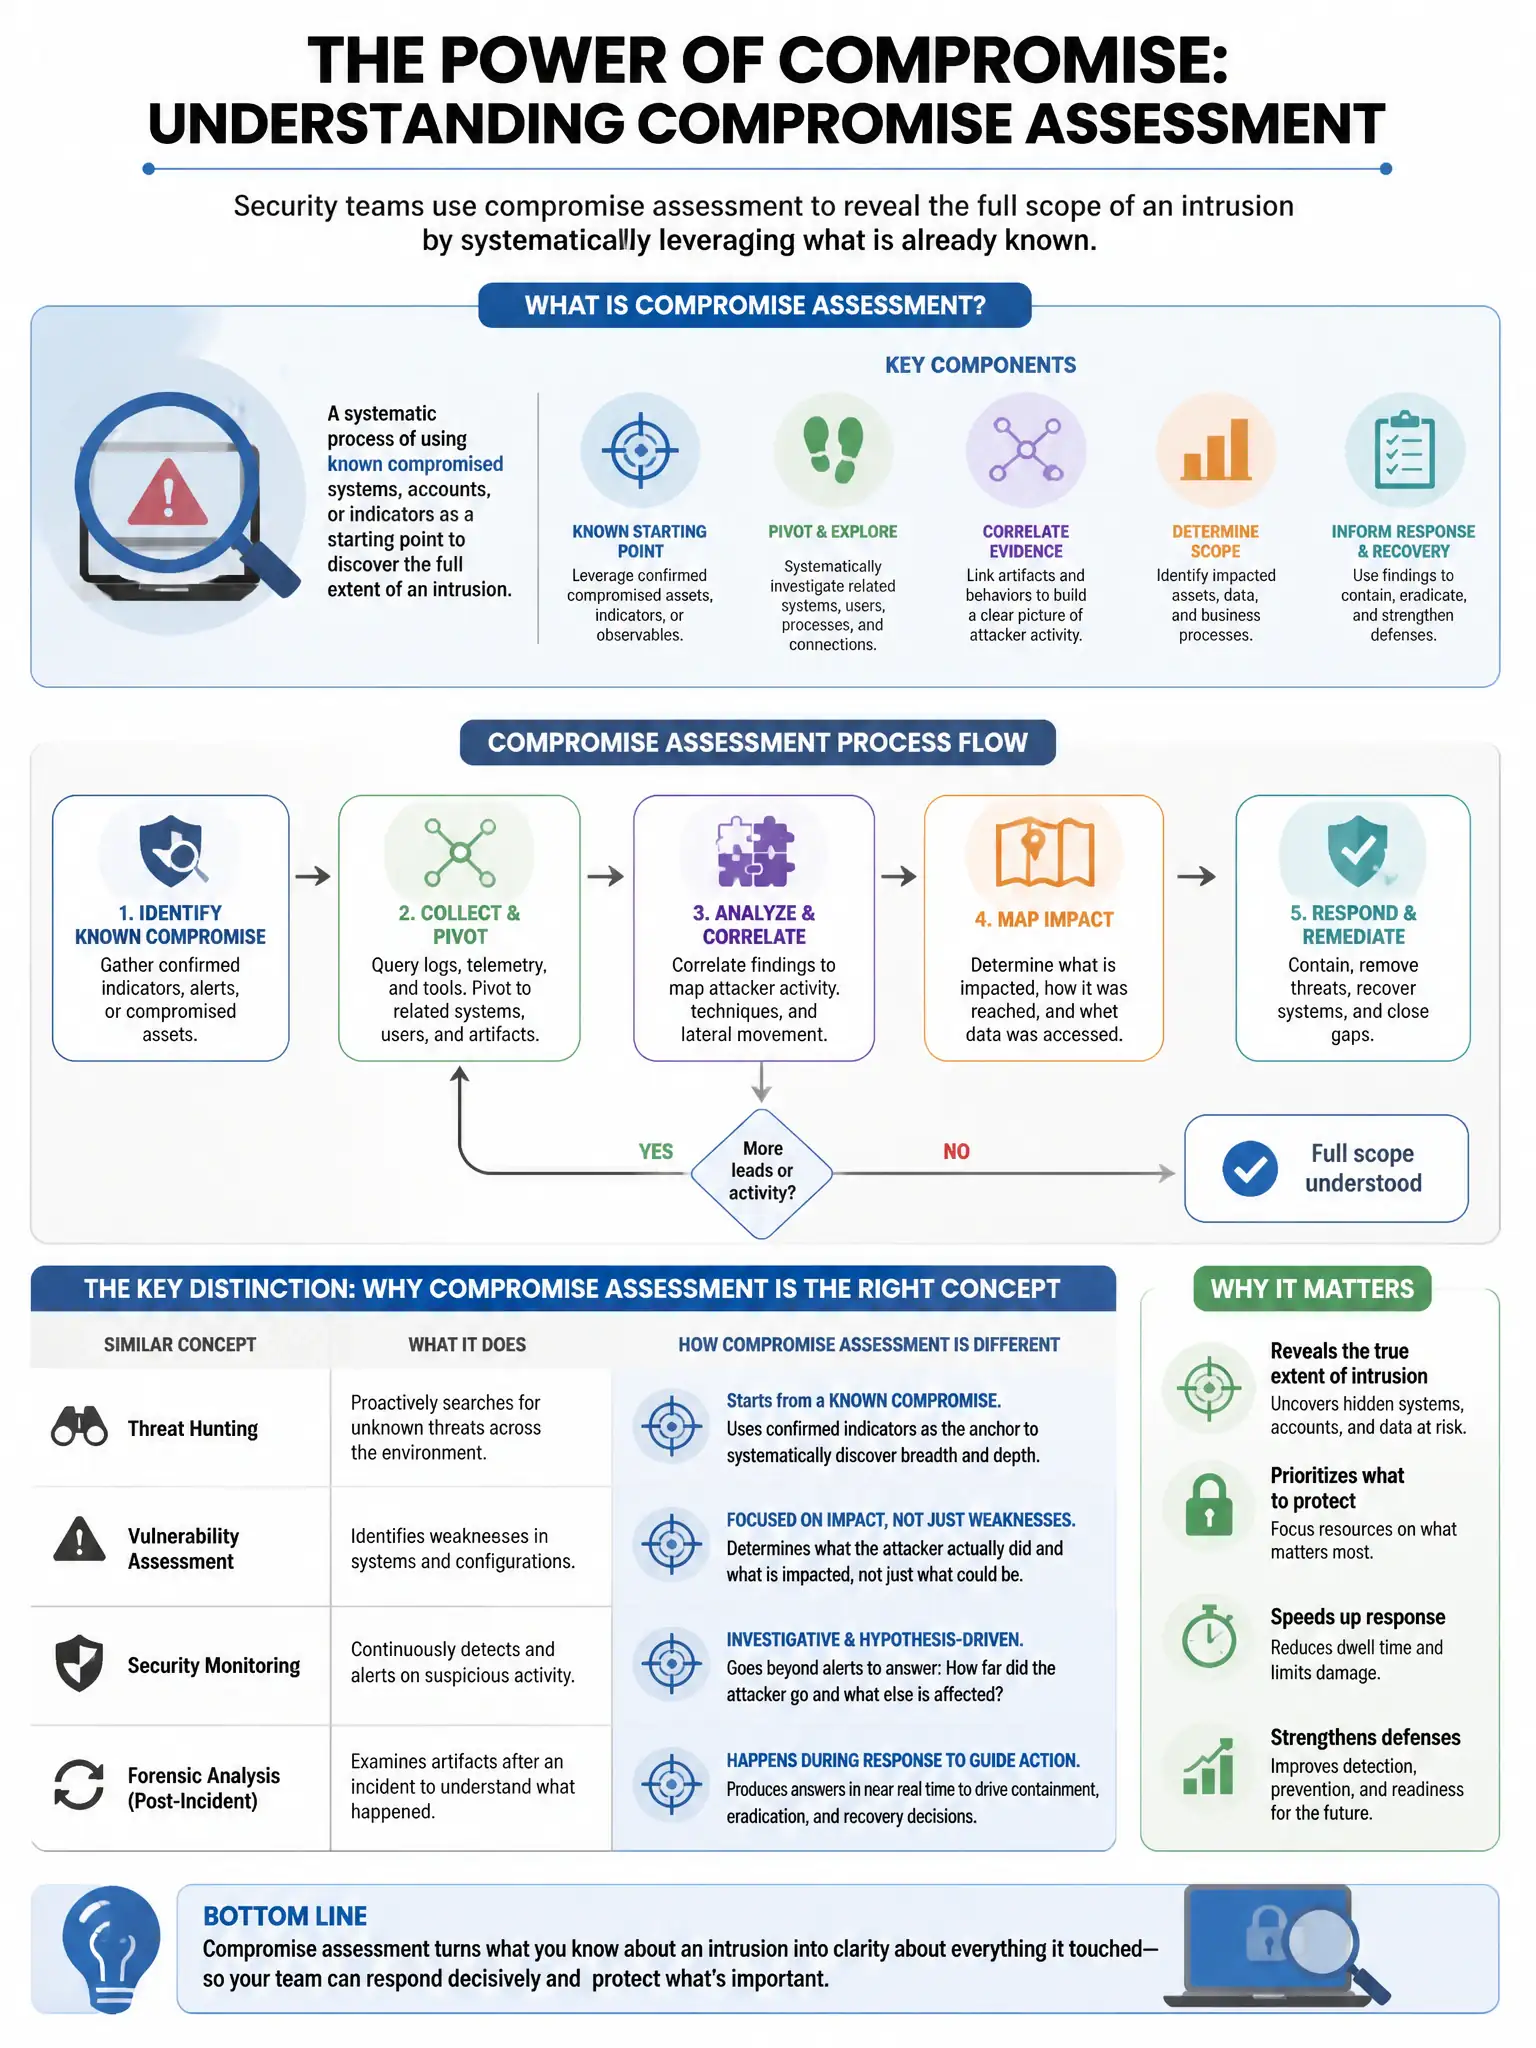
A security team is performing incident response and wants to understand the full scope of an intrusion. Which concept describes the systematic process of using known compromised systems to identify additional compromised infrastructure?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need indicator pivoting because it uses artifacts from confirmed compromises, like hashes, IPs, domains, registry keys, and filenames, to hunt for the same indicators on other systems. That's how you reveal the full scope of the intrusion.
Full Explanation
Indicator pivoting is correct because it uses artifacts from confirmed compromises (hashes, IPs, domains, registry keys, filenames) to search for the same indicators on other systems, revealing the full scope of the intrusion. Threat modeling is wrong because it's a proactive design activity to identify potential threats before an incident. Vulnerability chaining is wrong because it's an offensive technique where multiple lower-severity vulnerabilities are combined for greater impact. Adversary emulation is wrong because it's a red team technique that simulates specific threat actors, not an incident response scoping method.