
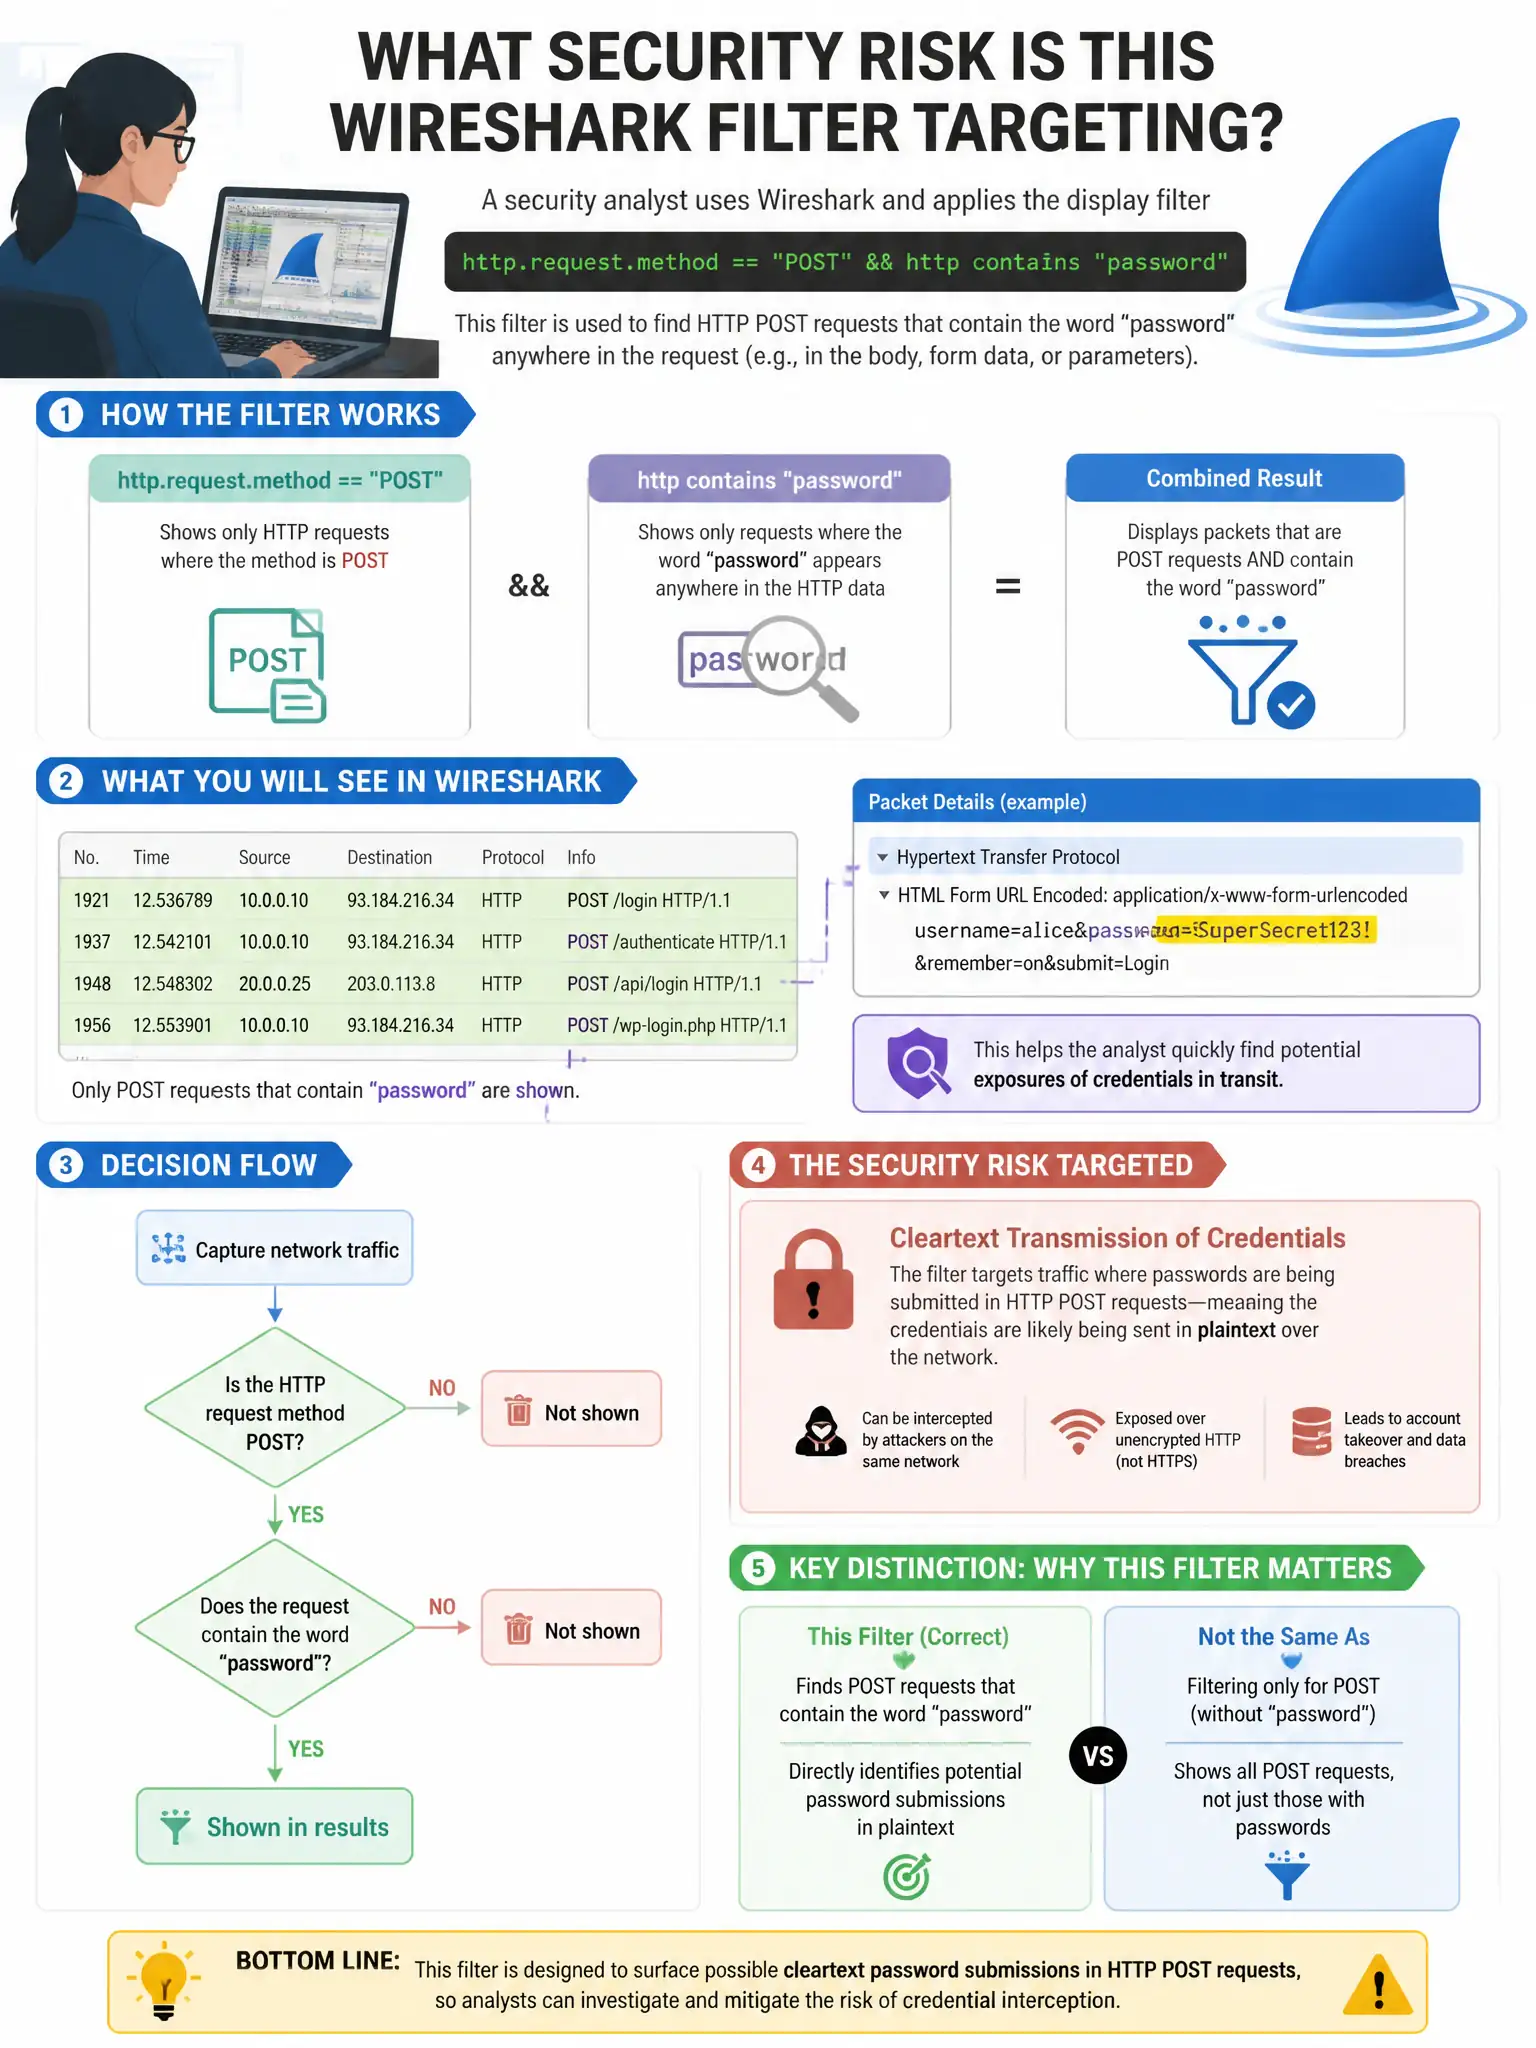
A security analyst uses Wireshark and applies the display filter http.request.method == "POST" && http contains "password". What is the security risk this filter is attempting to identify?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — this filter catches HTTP POST requests that contain 'password', so you're seeing cleartext credentials being sent in web forms over unencrypted HTTP. That's a critical risk because anyone sniffing the traffic can read the login data.
Full Explanation
The correct answer is cleartext credential transmission in HTTP POST forms over unencrypted HTTP because the filter captures HTTP POST requests containing the string 'password', which could reveal credentials submitted through web forms over unencrypted HTTP — a critical security risk exposing credentials to eavesdroppers. The SQL injection payloads in HTTP GET parameters option is wrong because SQL injection typically appears in GET or POST parameters but the filter is specifically looking for the word 'password', not SQL syntax. The Cross-site scripting (XSS) payloads in web responses option is wrong because XSS payloads appear in server responses, not POST request bodies. The HTTP response splitting attacks in server replies option is wrong because HTTP response splitting is found in server responses, not client POST requests.