
An NSM analyst wants to identify hosts that may be participating in a DGA (Domain Generation Algorithm) botnet. Which combination of Zeek log fields most effectively identifies DGA activity?
Select an answer to reveal the explanation.
Short Explanation
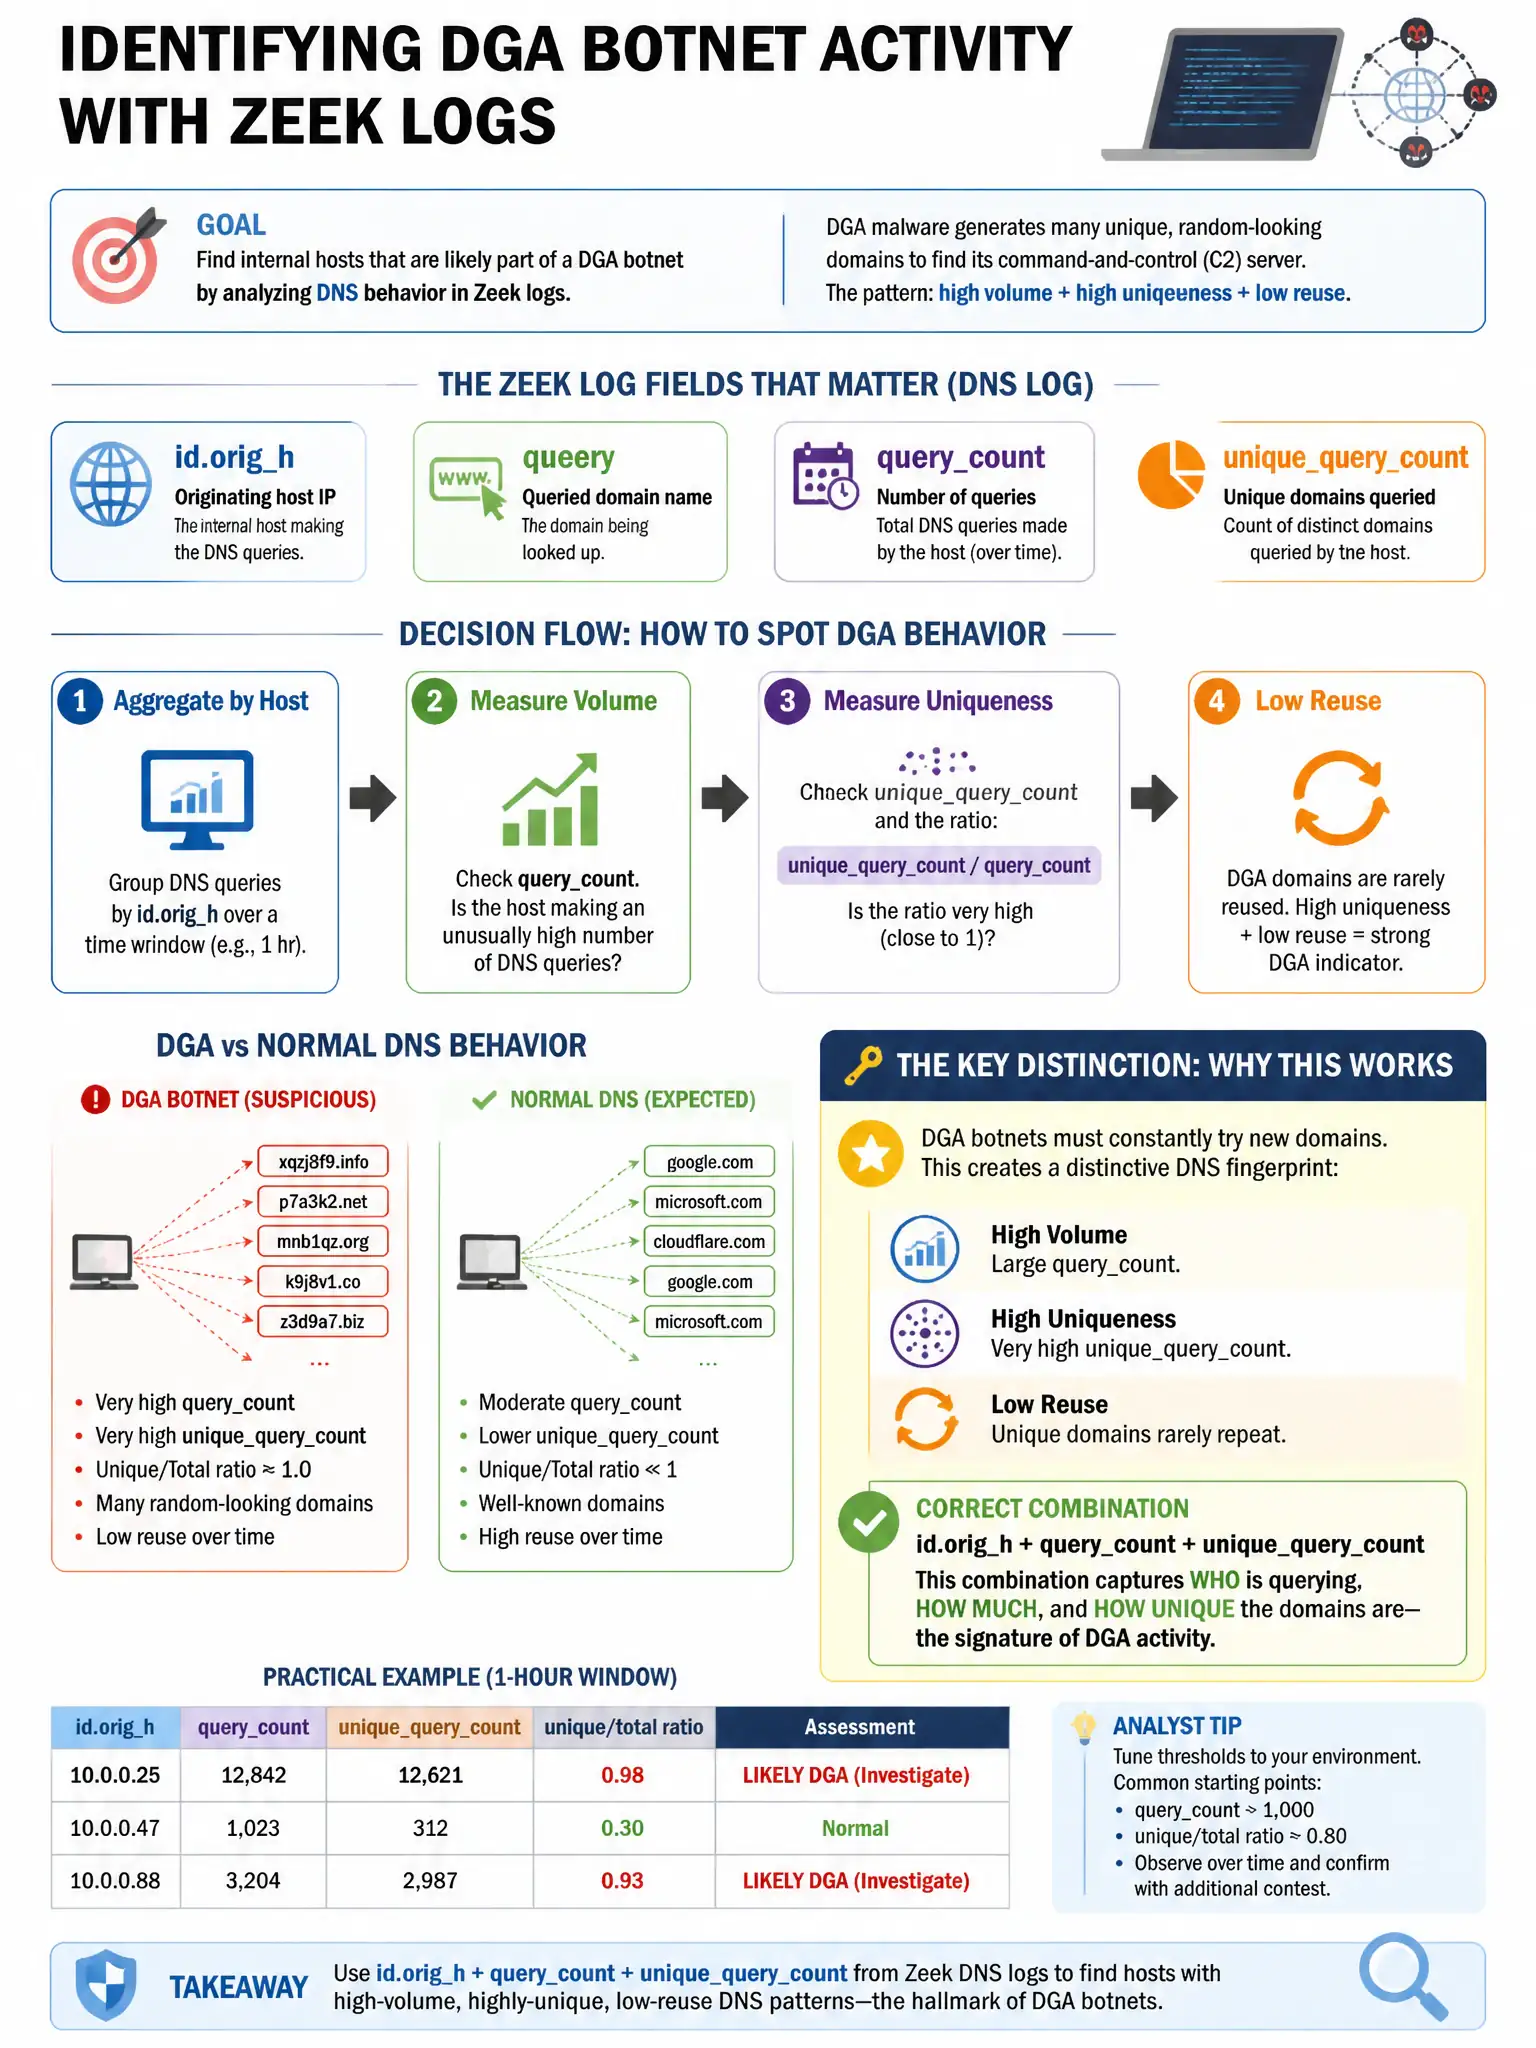
Here's the deal — you want to catch a flood of NXDOMAIN responses in dns.log tied to high-entropy or randomly structured domain names. DGA malware generates lots of pseudo-random domains and keeps querying until one hits an active command-and-control server, so that combo is your tell.
Full Explanation
The correct combination is a high number of NXDOMAIN responses from dns.log, combined with high-entropy or randomly structured domain names. DGA malware generates many pseudo-random domain names and queries them until one resolves to an active command-and-control server; this produces a high volume of NXDOMAIN responses and domains with high lexical entropy or random character patterns in dns.log. Large orig_bytes values in conn.log combined with long connection durations are wrong because they suggest data exfiltration, not DGA activity. HTTP POST requests to domains with low Alexa rankings in http.log are wrong because they may indicate suspicious web activity but are not characteristic of DGA. SSL certificates with expiration dates more than 2 years in the future in ssl.log are wrong because they are a certificate hygiene issue but do not indicate DGA.