
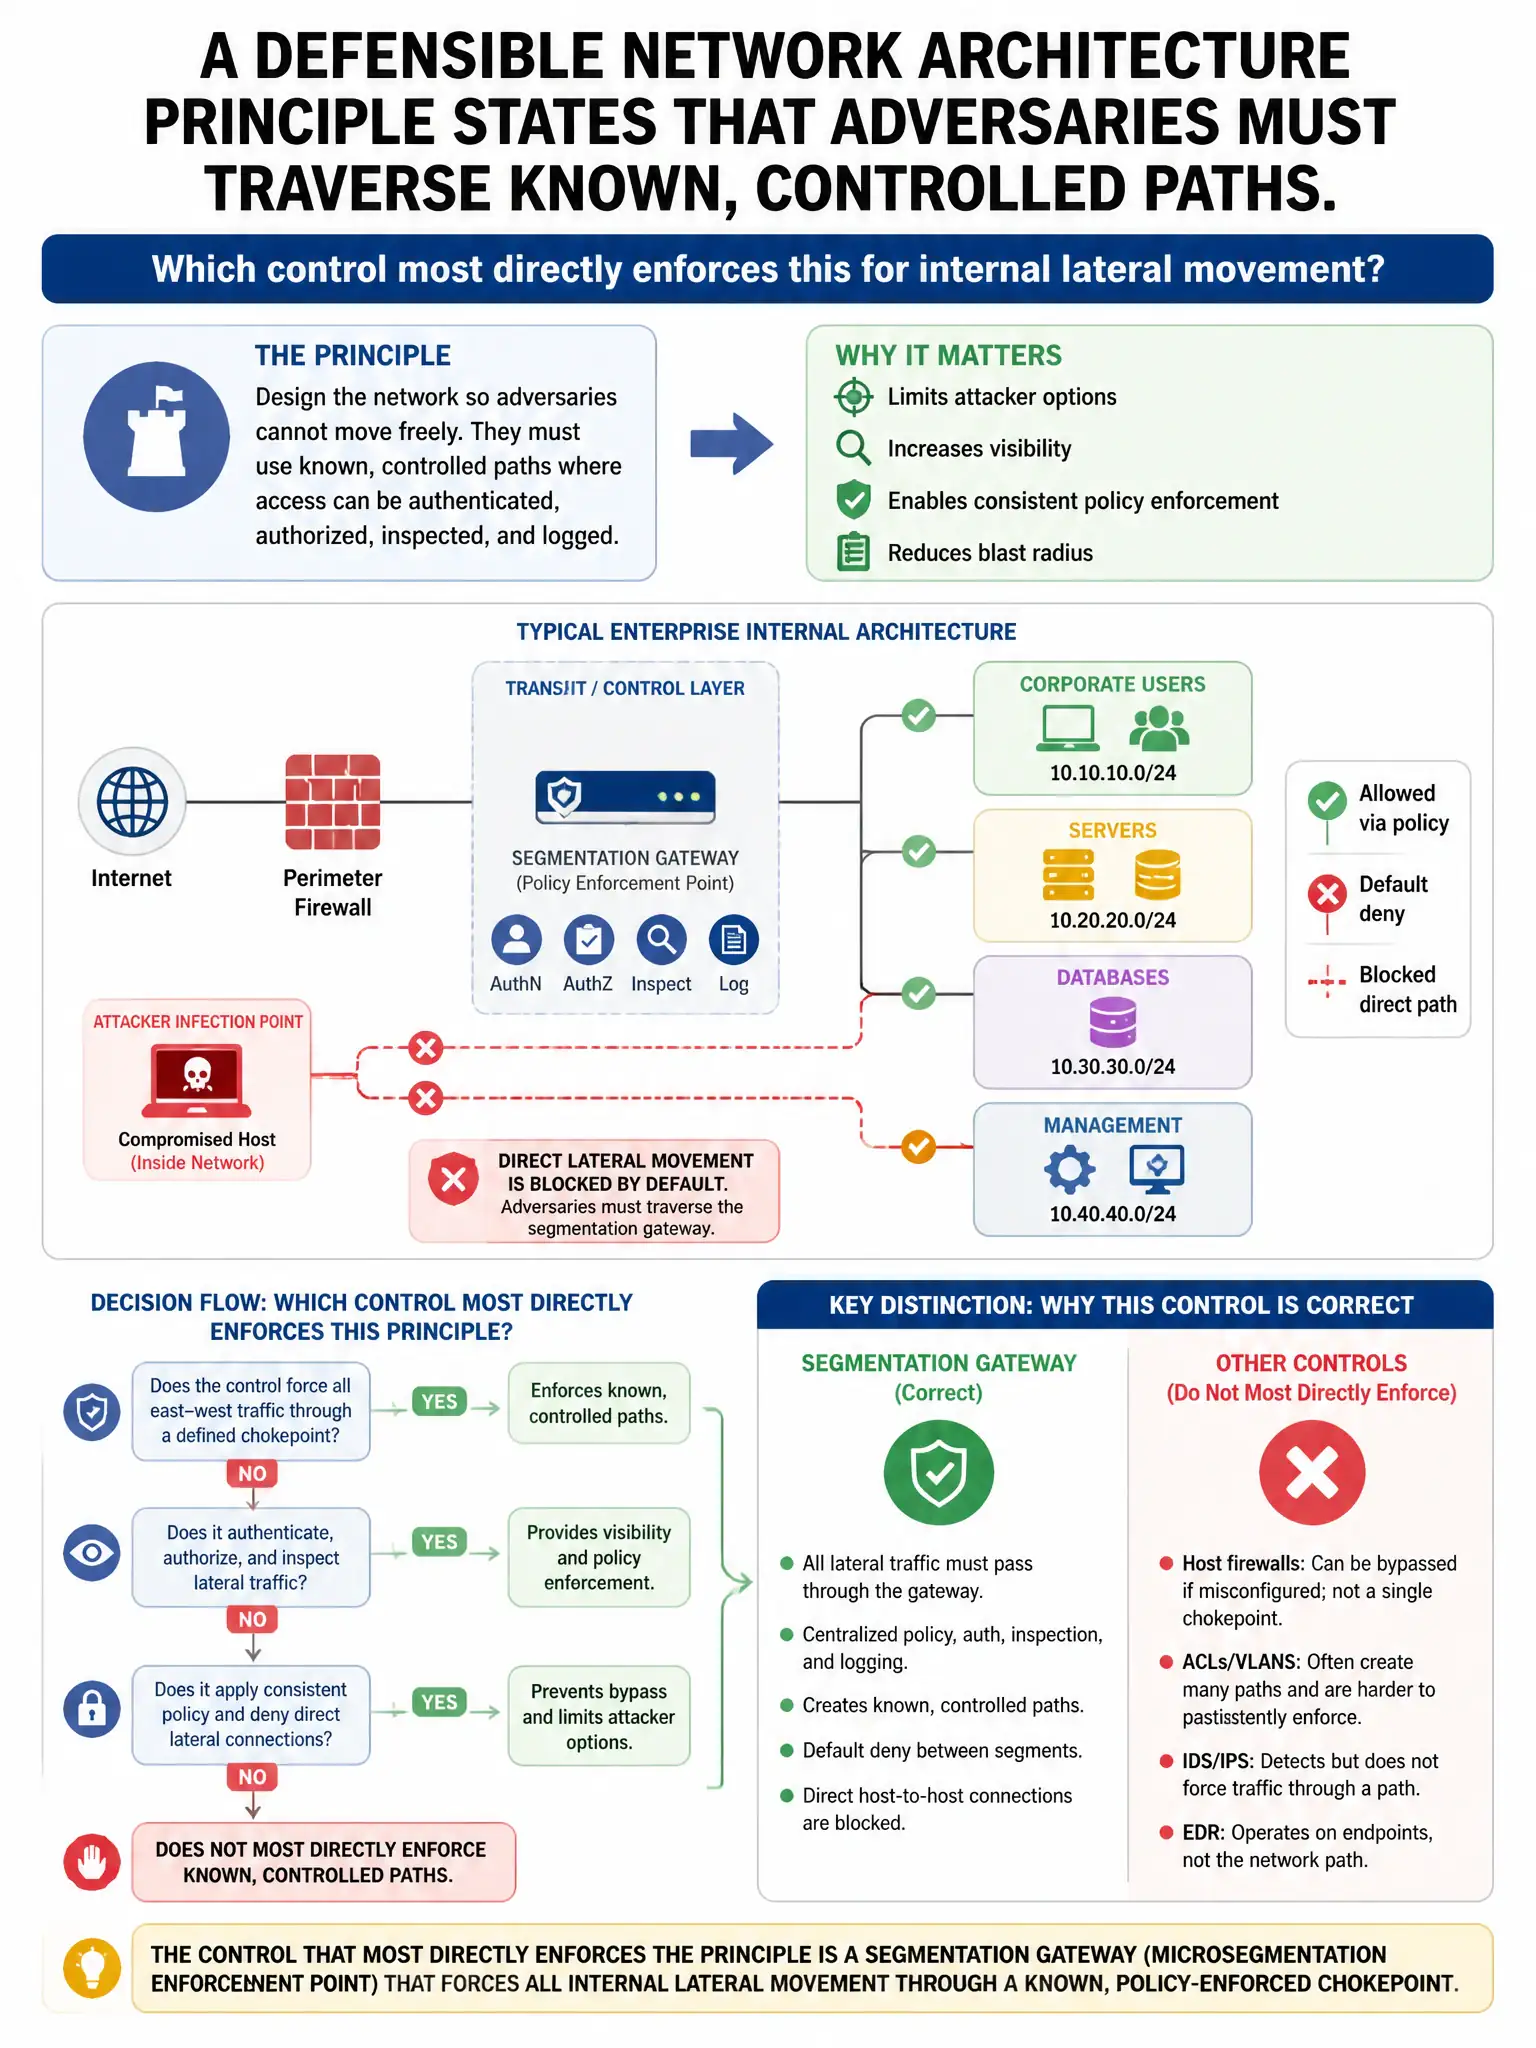
A defensible network architecture principle states that adversaries must traverse known, controlled paths. Which control most directly enforces this for internal lateral movement?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — internal segmentation with firewall choke points between critical security zones is right because it forces lateral movement through known, controlled paths you can inspect, detect, and block.
Full Explanation
Internal network segmentation with firewall choke points between all critical security zones is correct because it forces lateral movement attempts through controlled inspection points, allowing detection and blocking. External perimeter firewalls with geo-blocking rules are wrong because they only address north-south traffic from the internet. An HTTPS-only policy for all web applications is wrong because HTTPS enforcement is an application-layer control that does not restrict network paths. Multi-factor authentication for all user accounts is wrong because it controls authentication, not network traversal paths between segments.