
An organization wants to prevent users from running unauthorized executables on Windows workstations. Which Microsoft technology provides application whitelisting based on publisher certificate, file hash, and path rules?
Select an answer to reveal the explanation.
Short Explanation
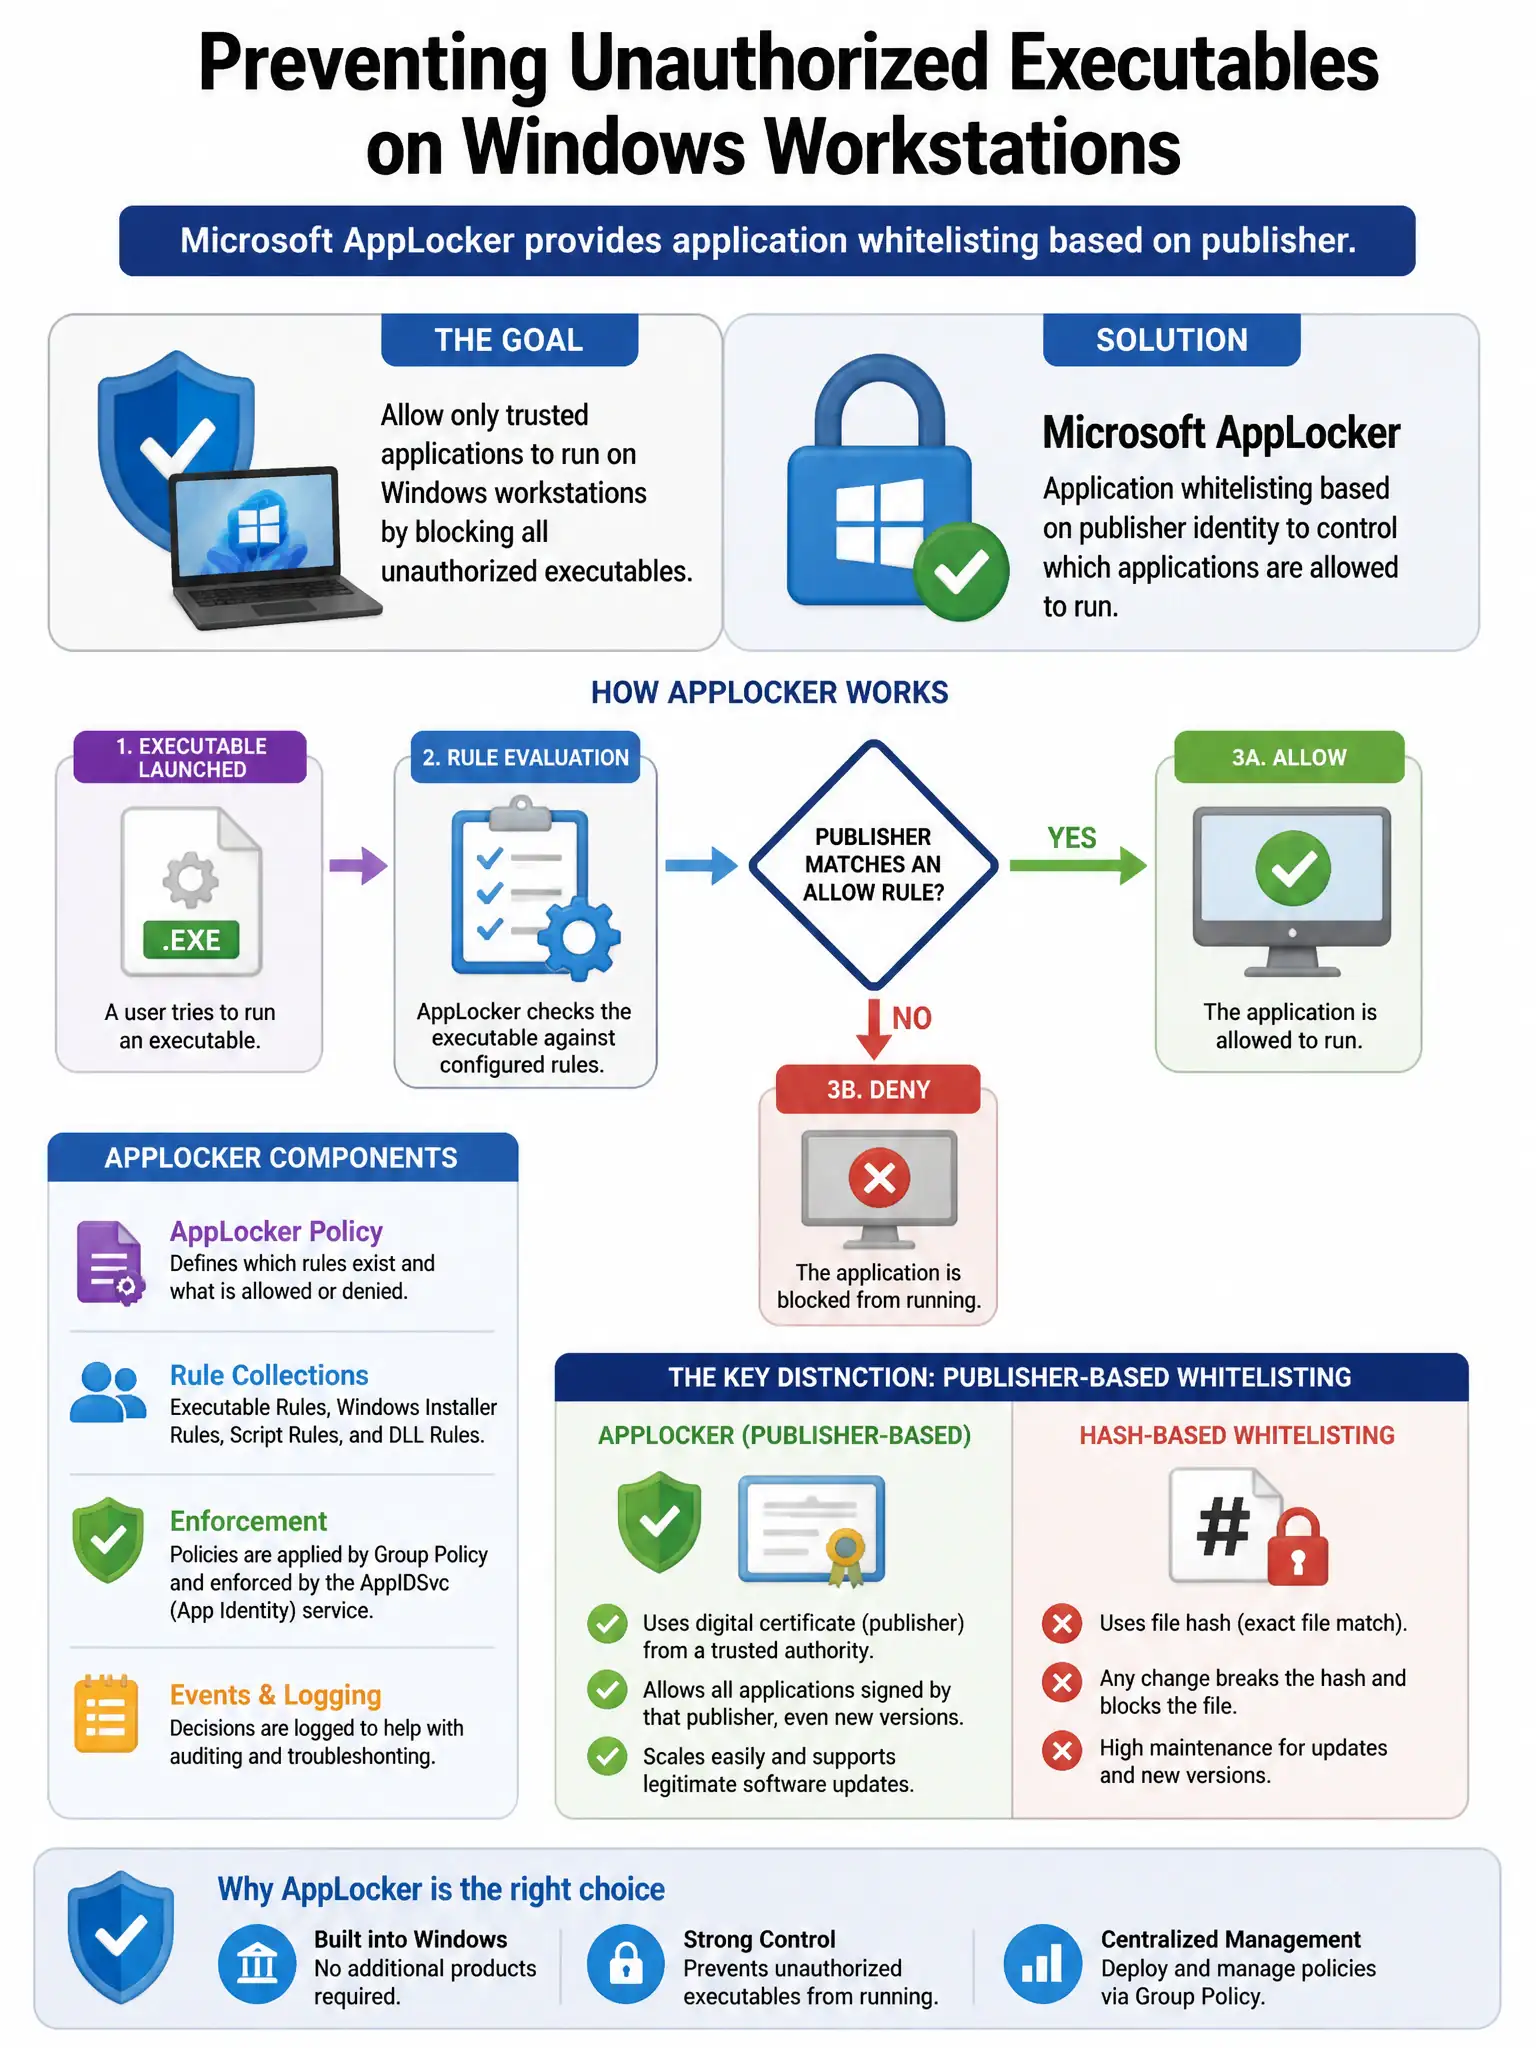
Here's the deal — AppLocker or Windows Defender Application Control (WDAC) is what you want because they enforce allow lists based on publisher signatures, file hashes, and path rules, stopping unauthorized executables from running.
Full Explanation
AppLocker or Windows Defender Application Control (WDAC) is correct because they are Windows application control technologies that enforce allow lists based on publisher signatures, file hashes, and path rules, preventing unauthorized executables from running. Windows Defender Antivirus is wrong because it uses signature and heuristic detection to block known malware, not a comprehensive allow-list model. User Account Control (UAC) is wrong because it prompts for elevation before administrative actions but does not prevent execution of non-elevated unauthorized applications. Windows Firewall with Advanced Security is wrong because it controls network traffic, not process execution.