
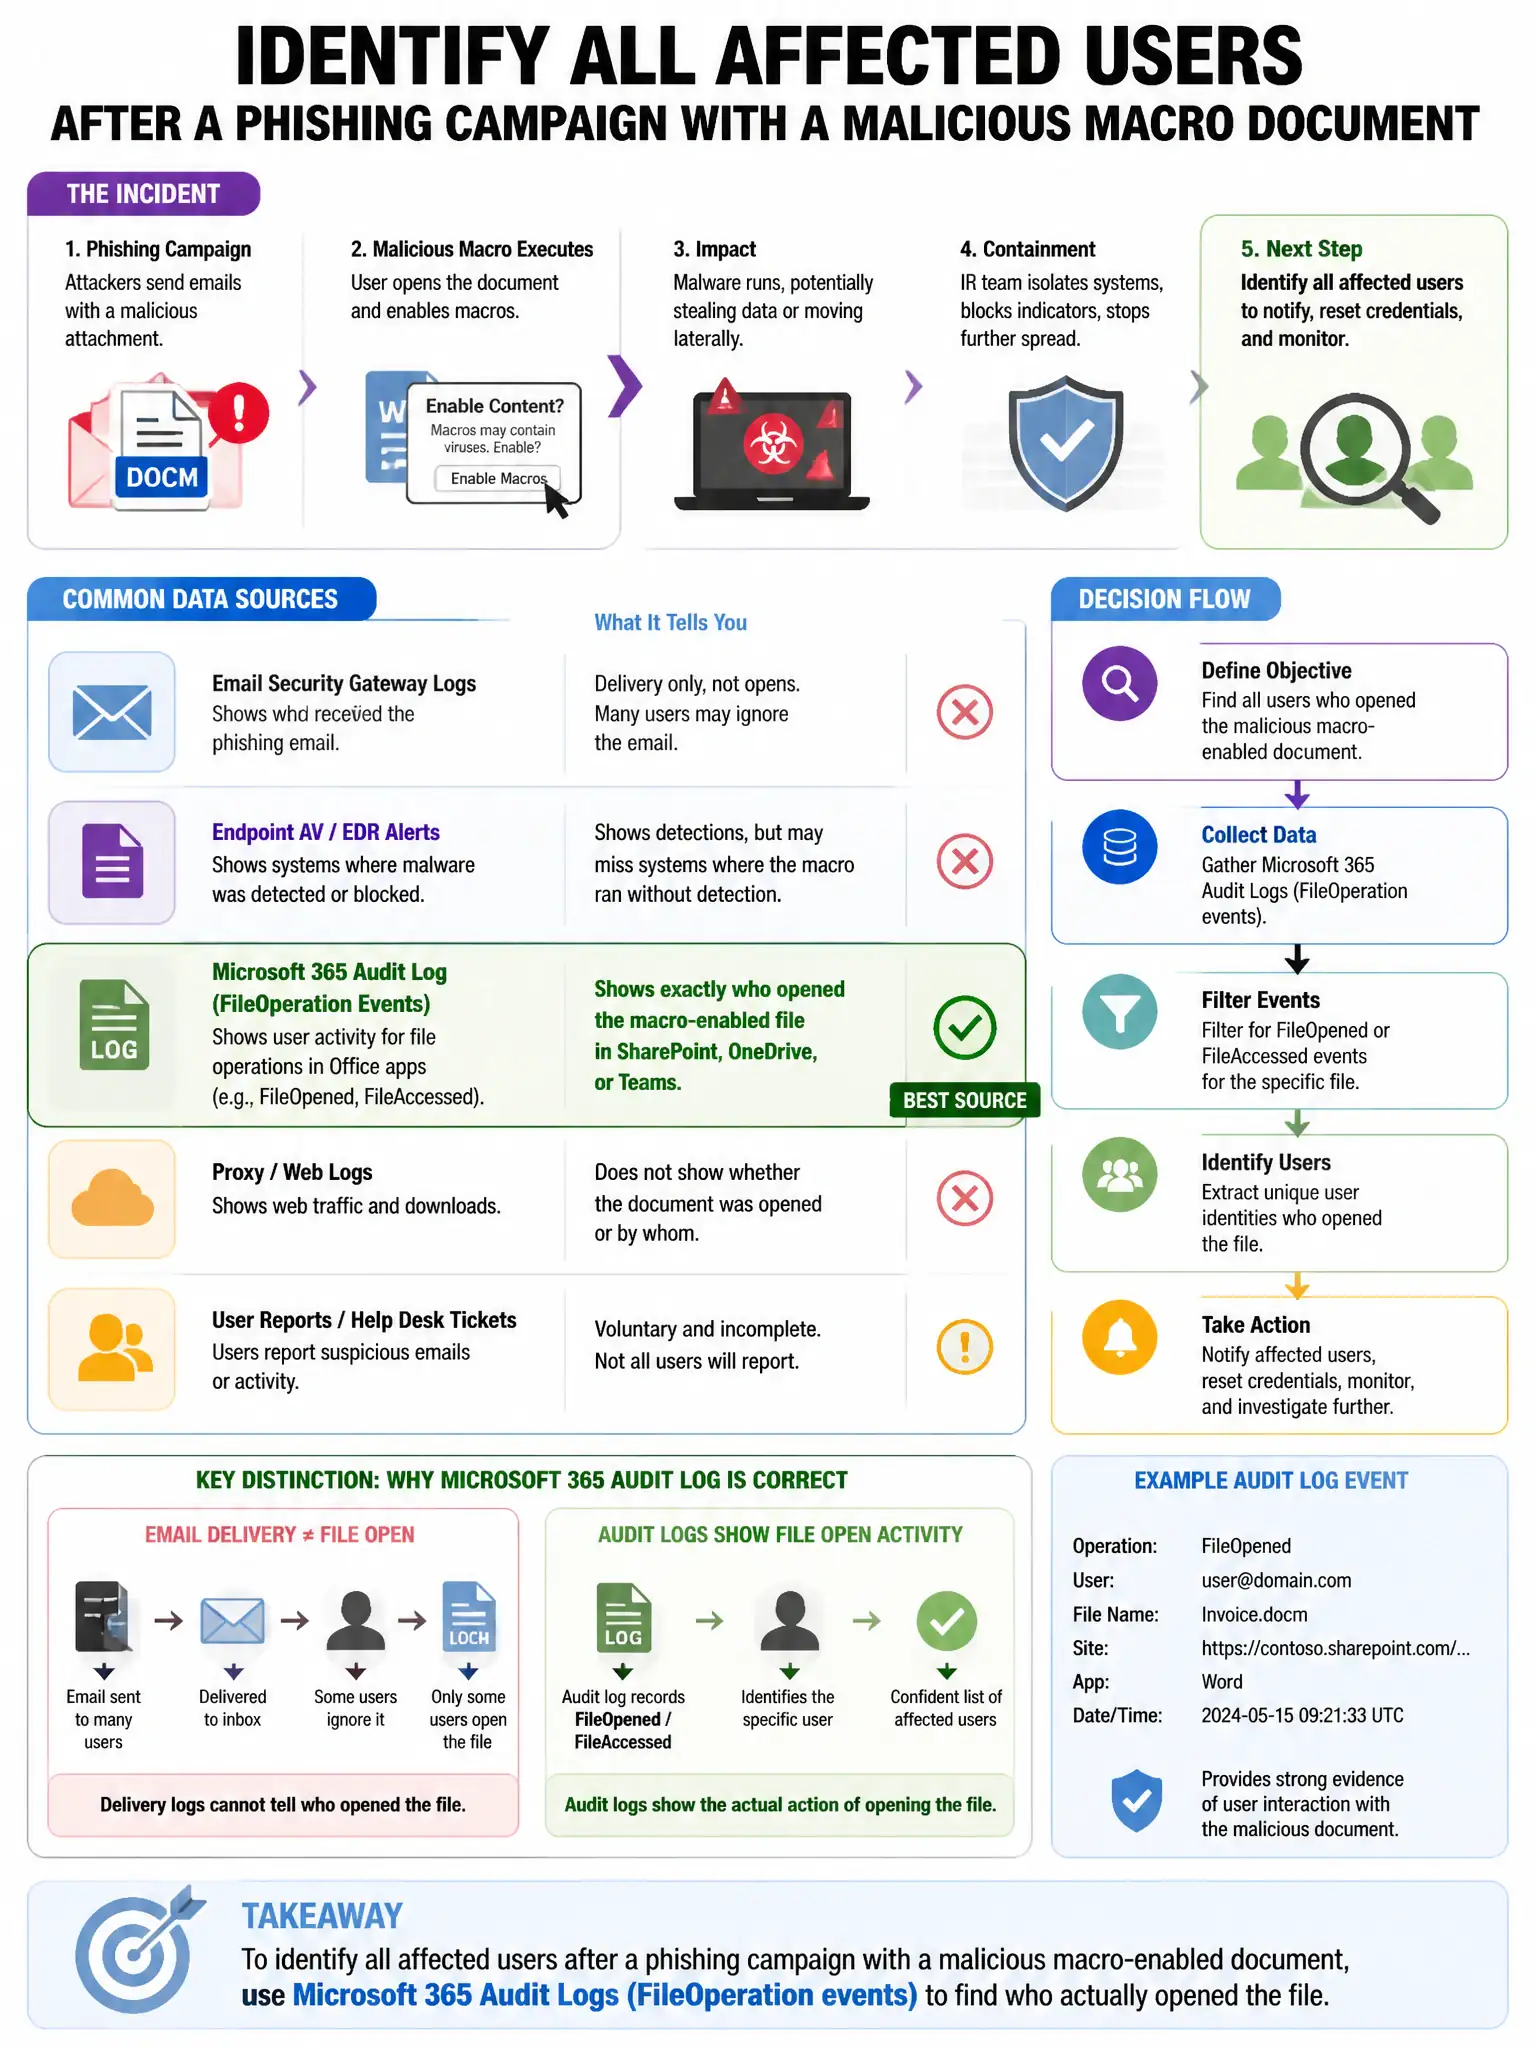
An incident involves a phishing campaign that delivered a malicious macro-enabled document. After containment, the IR team must identify all affected users. Which data source most efficiently identifies who opened the document?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need email gateway logs filtered by attachment name/hash to get every recipient, then endpoint logs like Office Protected View events or macro execution in Windows Event Log 4688 or Sysmon to prove who opened and ran it. User surveys, sent-items searches, and AV-only scans won't give you a reliable affected-user list.
Full Explanation
The correct approach is to review email gateway logs filtered by attachment name/hash to identify all recipients, then correlate with endpoint logs such as Office Protected View events or macro execution in Windows Event Log 4688 or Sysmon to identify who opened and executed it. Gateway logs establish delivery scope, and endpoint telemetry confirms actual opening and execution, producing a definitive affected host list. Asking the help desk to survey employees is wrong because surveys are unreliable; users may not remember or may be reluctant to admit opening a suspicious file. Searching only the email server's sent items folder is wrong because it shows the attacker's sent copies, not delivery to recipients. Running an AV scan on all workstations and reporting only detections is wrong because AV may miss custom or obfuscated payloads, leaving undetected infections out of scope.