
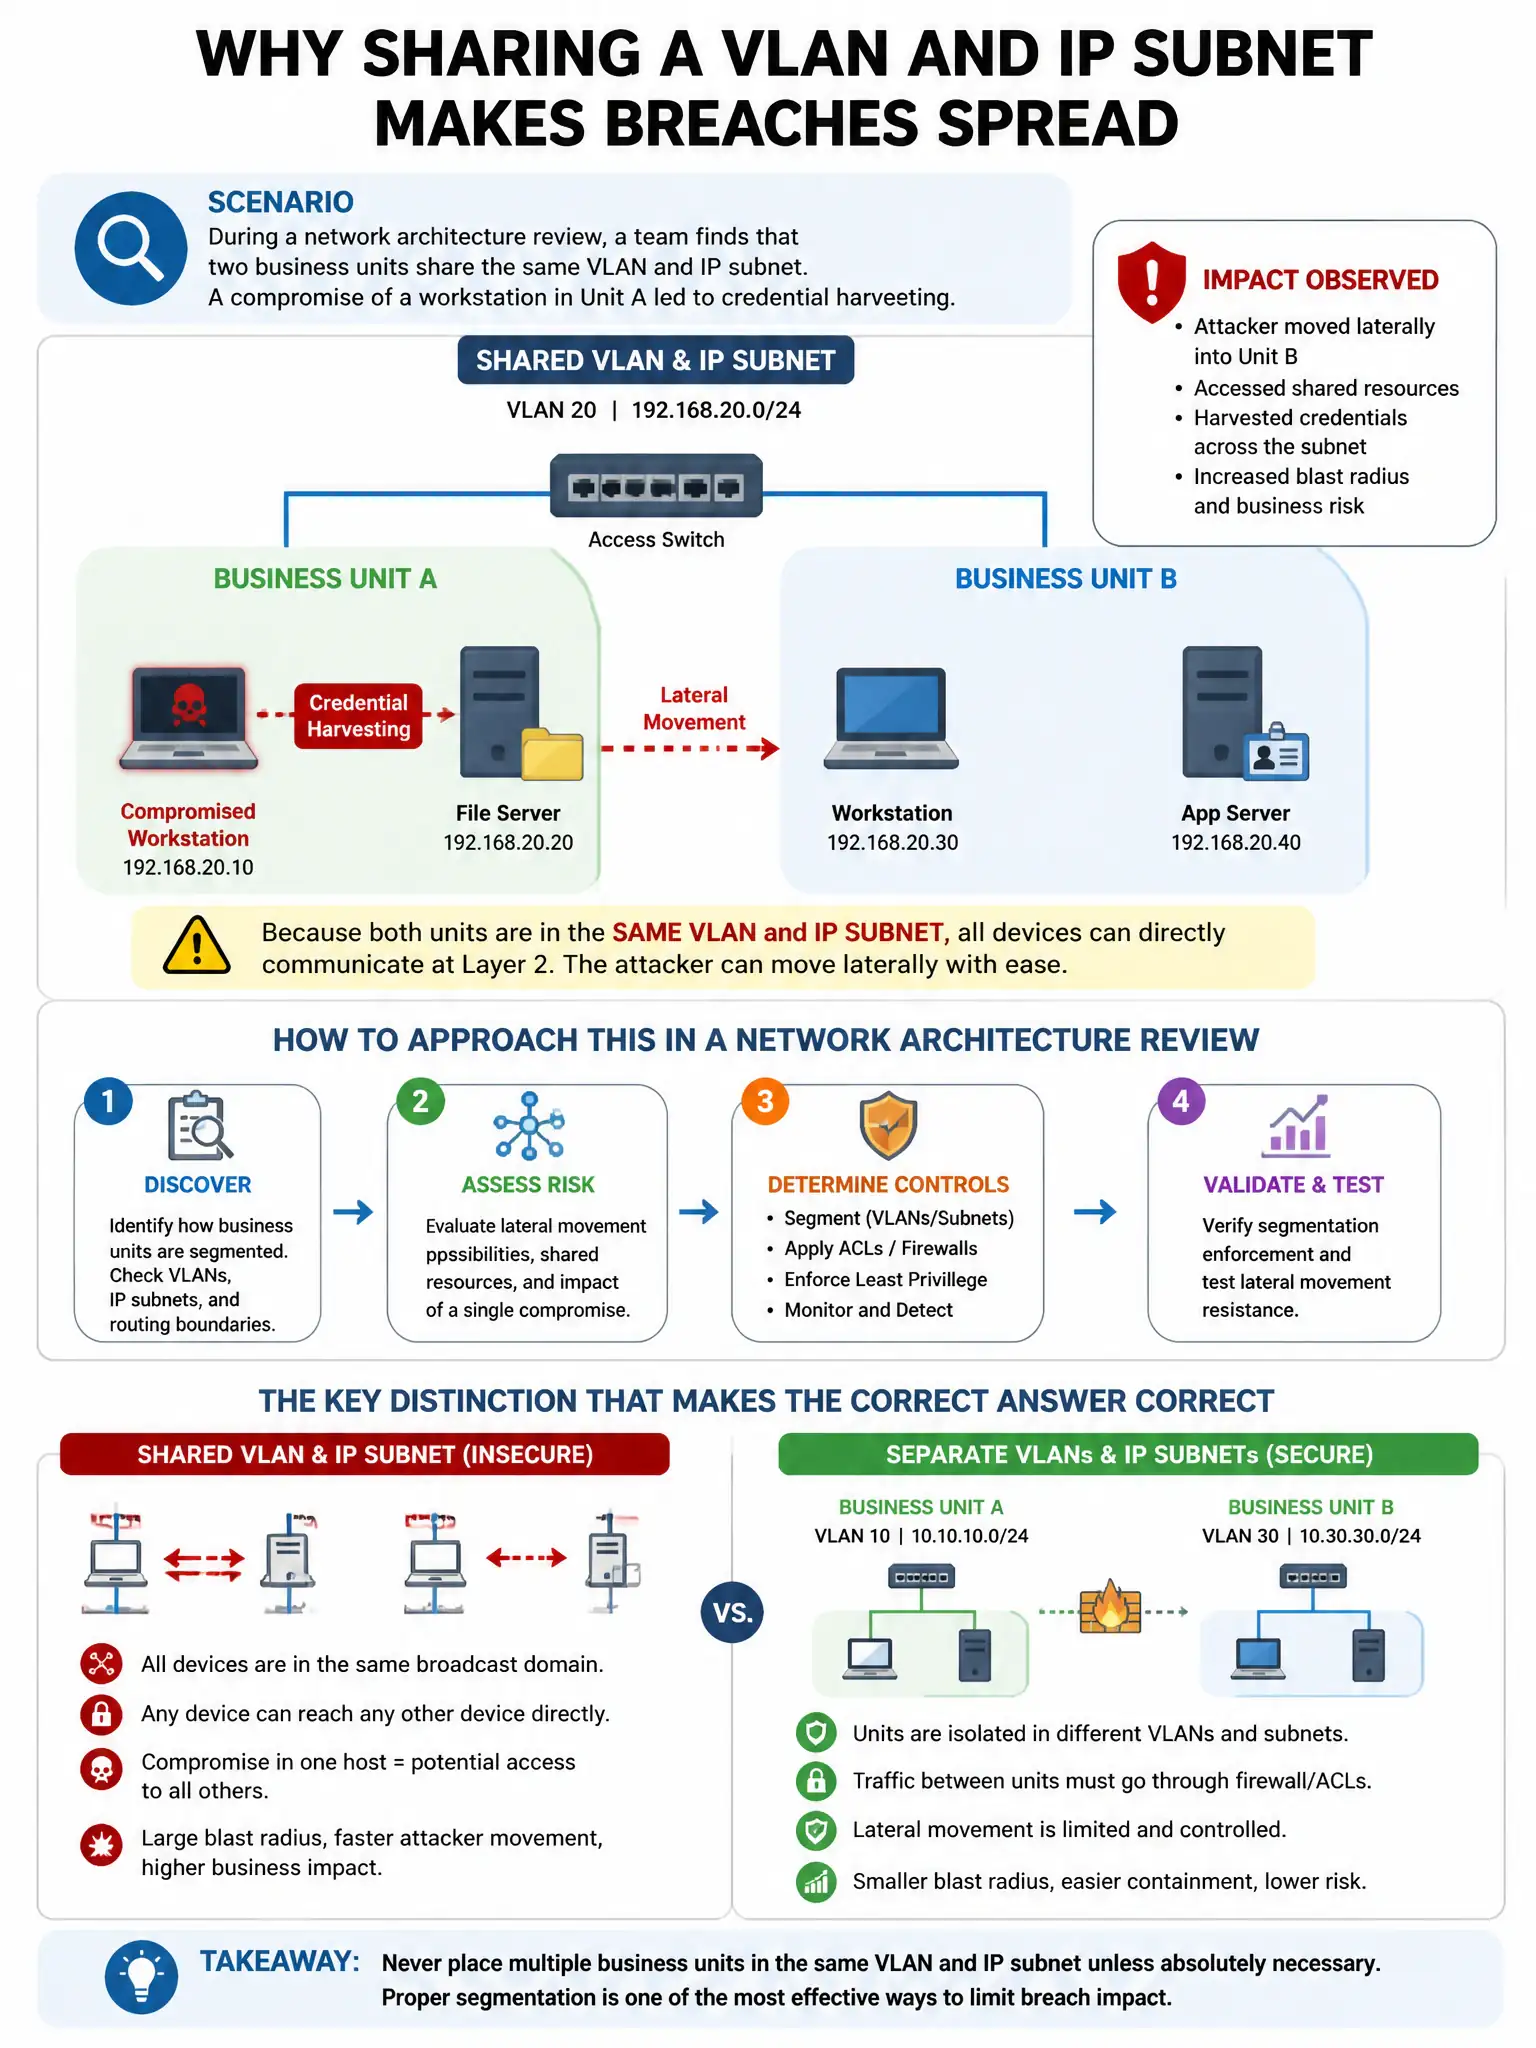
During a network architecture review, a team finds that two business units share the same VLAN and IP subnet. A compromise of a workstation in Unit A led to credential harvesting across Unit B via SMB relay. Which architectural remedy directly addresses this threat?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need micro-segmentation or private VLANs so hosts in different business units can't talk laterally at Layer 2. That kills the SMB relay path without needing separate subnets.
Full Explanation
Implementing micro-segmentation or private VLANs is correct because SMB relay attacks exploit Layer 2 broadcast domains; private VLANs or micro-segmentation prevent host-to-host communication within the same subnet, neutralizing the relay path without requiring separate subnets. Enabling 802.1X port authentication on all switch ports is wrong because 802.1X authenticates devices to the network but does not prevent lateral traffic once authenticated. Deploying endpoint antivirus across all workstations is wrong because antivirus may detect known malware but does not block SMB relay at the network layer. Increasing the perimeter firewall ruleset stringency is wrong because perimeter firewalls typically do not inspect intra-VLAN traffic.