
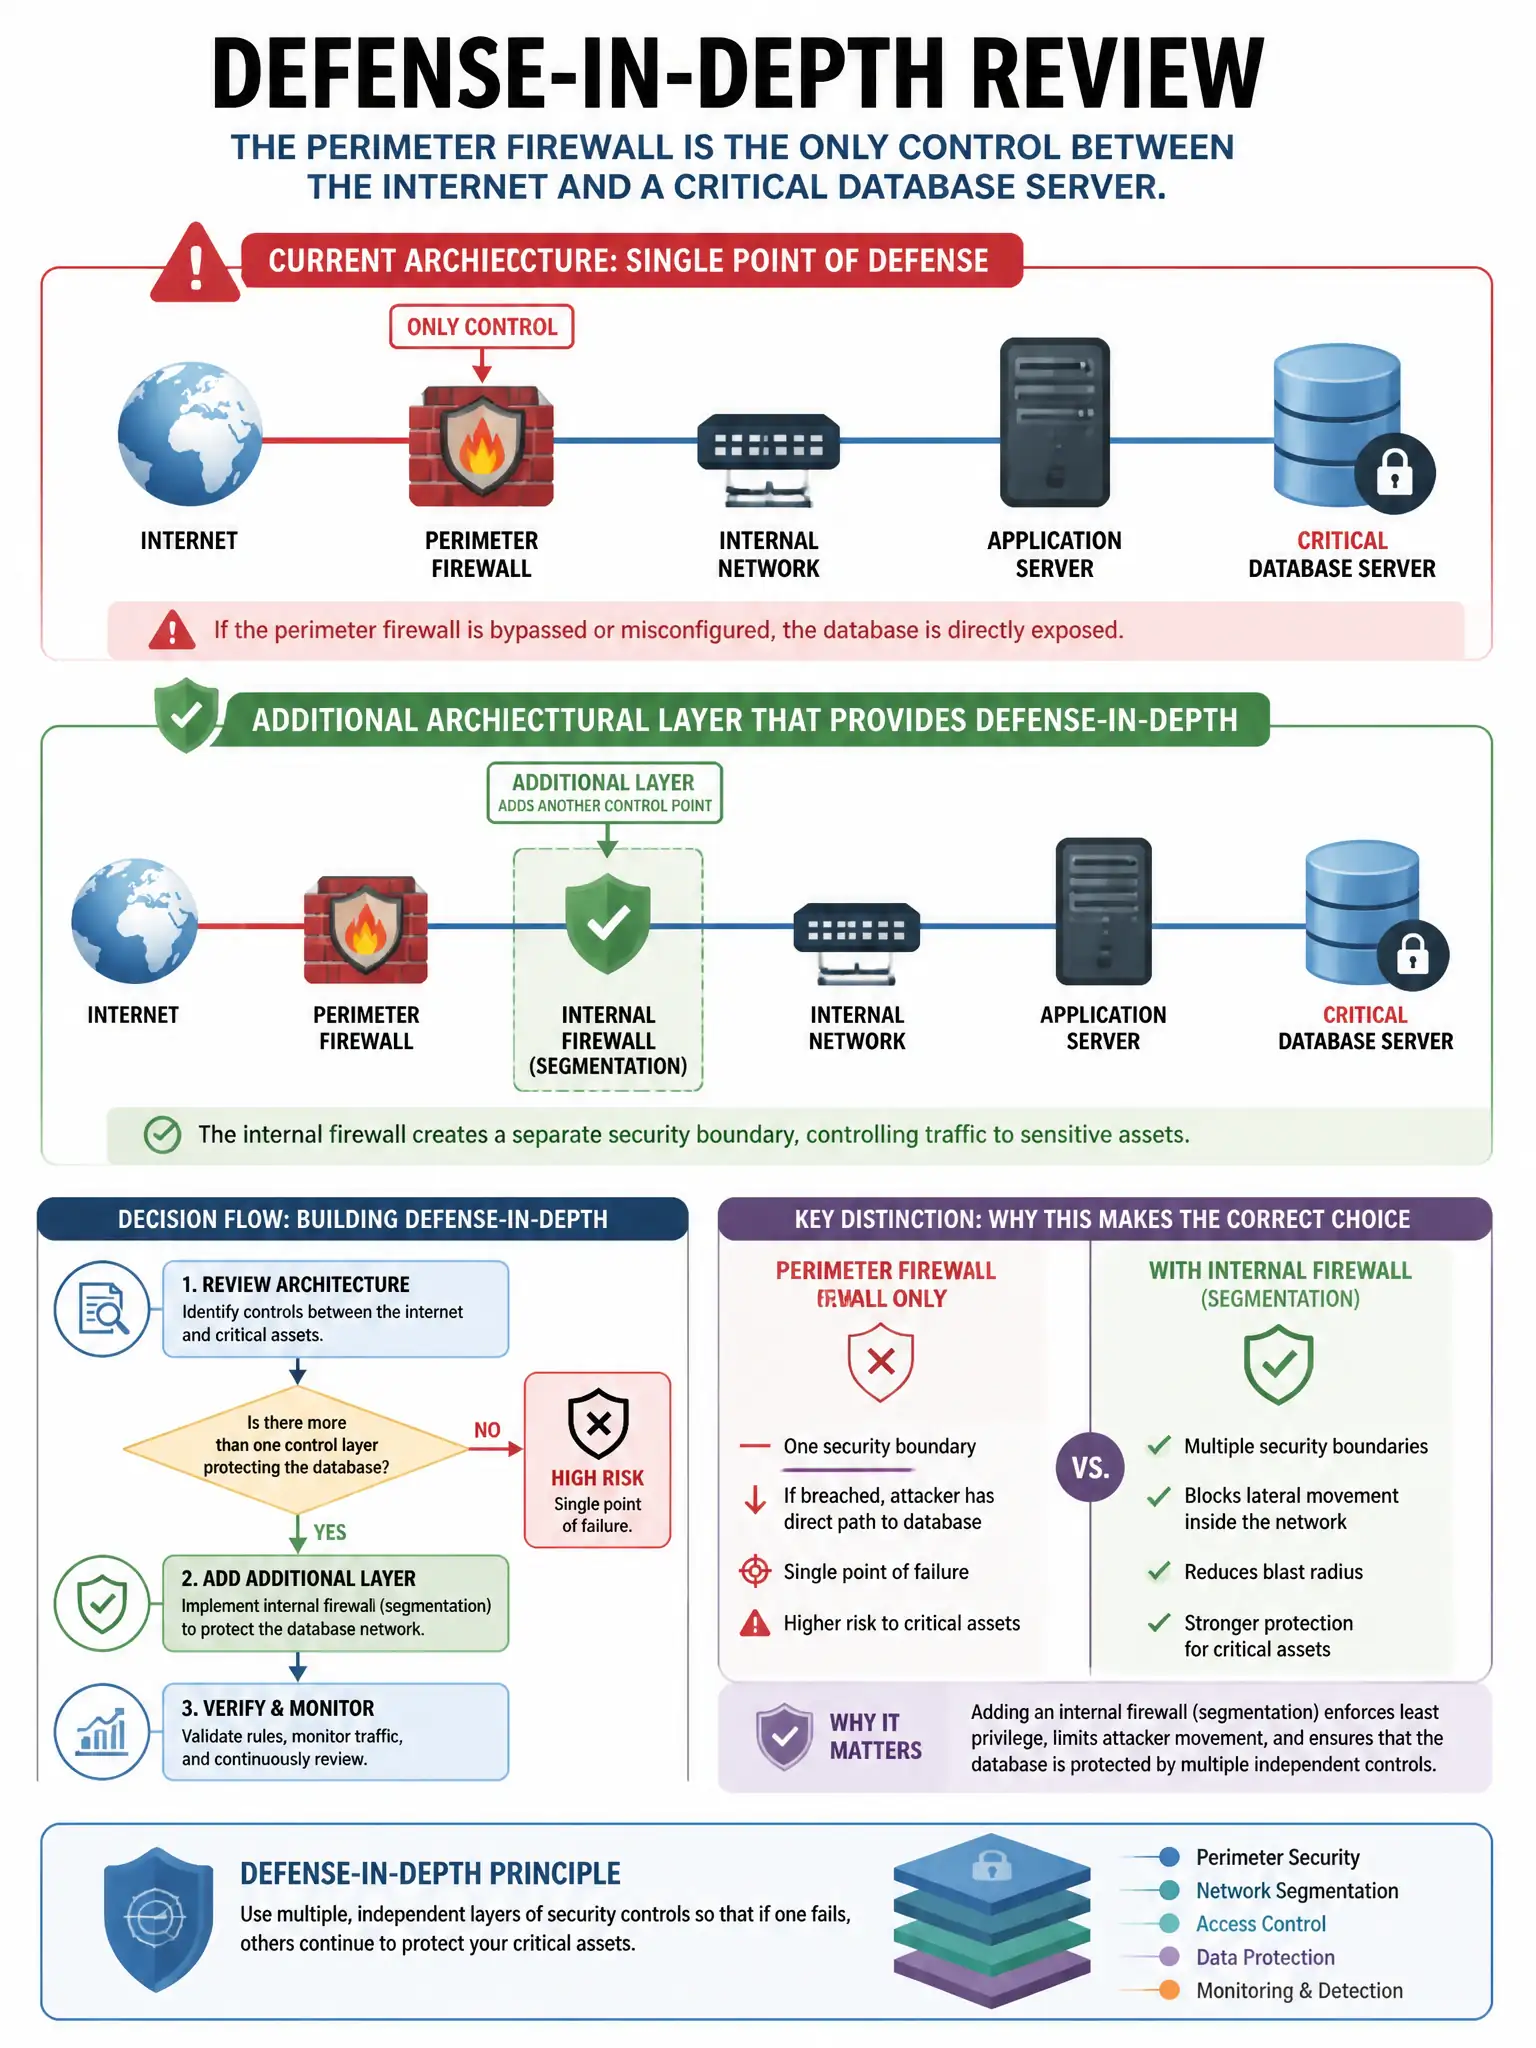
A defense-in-depth review reveals the perimeter firewall is the only control between the internet and a critical database server. Which additional architectural layer provides the most immediate risk reduction?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to place the database behind an application-tier web server in a segmented internal VLAN with a web application firewall in front of the web tier. That forces attackers through two extra layers, the web application firewall and the application server, before they can touch the database. It's real defense in depth, not just more logging or endpoint software.
Full Explanation
Placing the database behind an application-tier web server in a segmented internal VLAN with a web application firewall in front of the web tier is correct because it forces attackers through two additional layers, the web application firewall and the application server, before reaching the database. Adding a second identical perimeter firewall in active-passive high availability is wrong because it improves availability but not security. Enabling logging on the existing perimeter firewall is wrong because logging improves visibility but does not reduce attack surface. Installing antivirus on the database server is wrong because endpoint antivirus does not address direct external reach.