
Your organization must allow vendor remote access to an OT environment for maintenance windows. Which architecture best balances operational need with security?
Select an answer to reveal the explanation.
Short Explanation
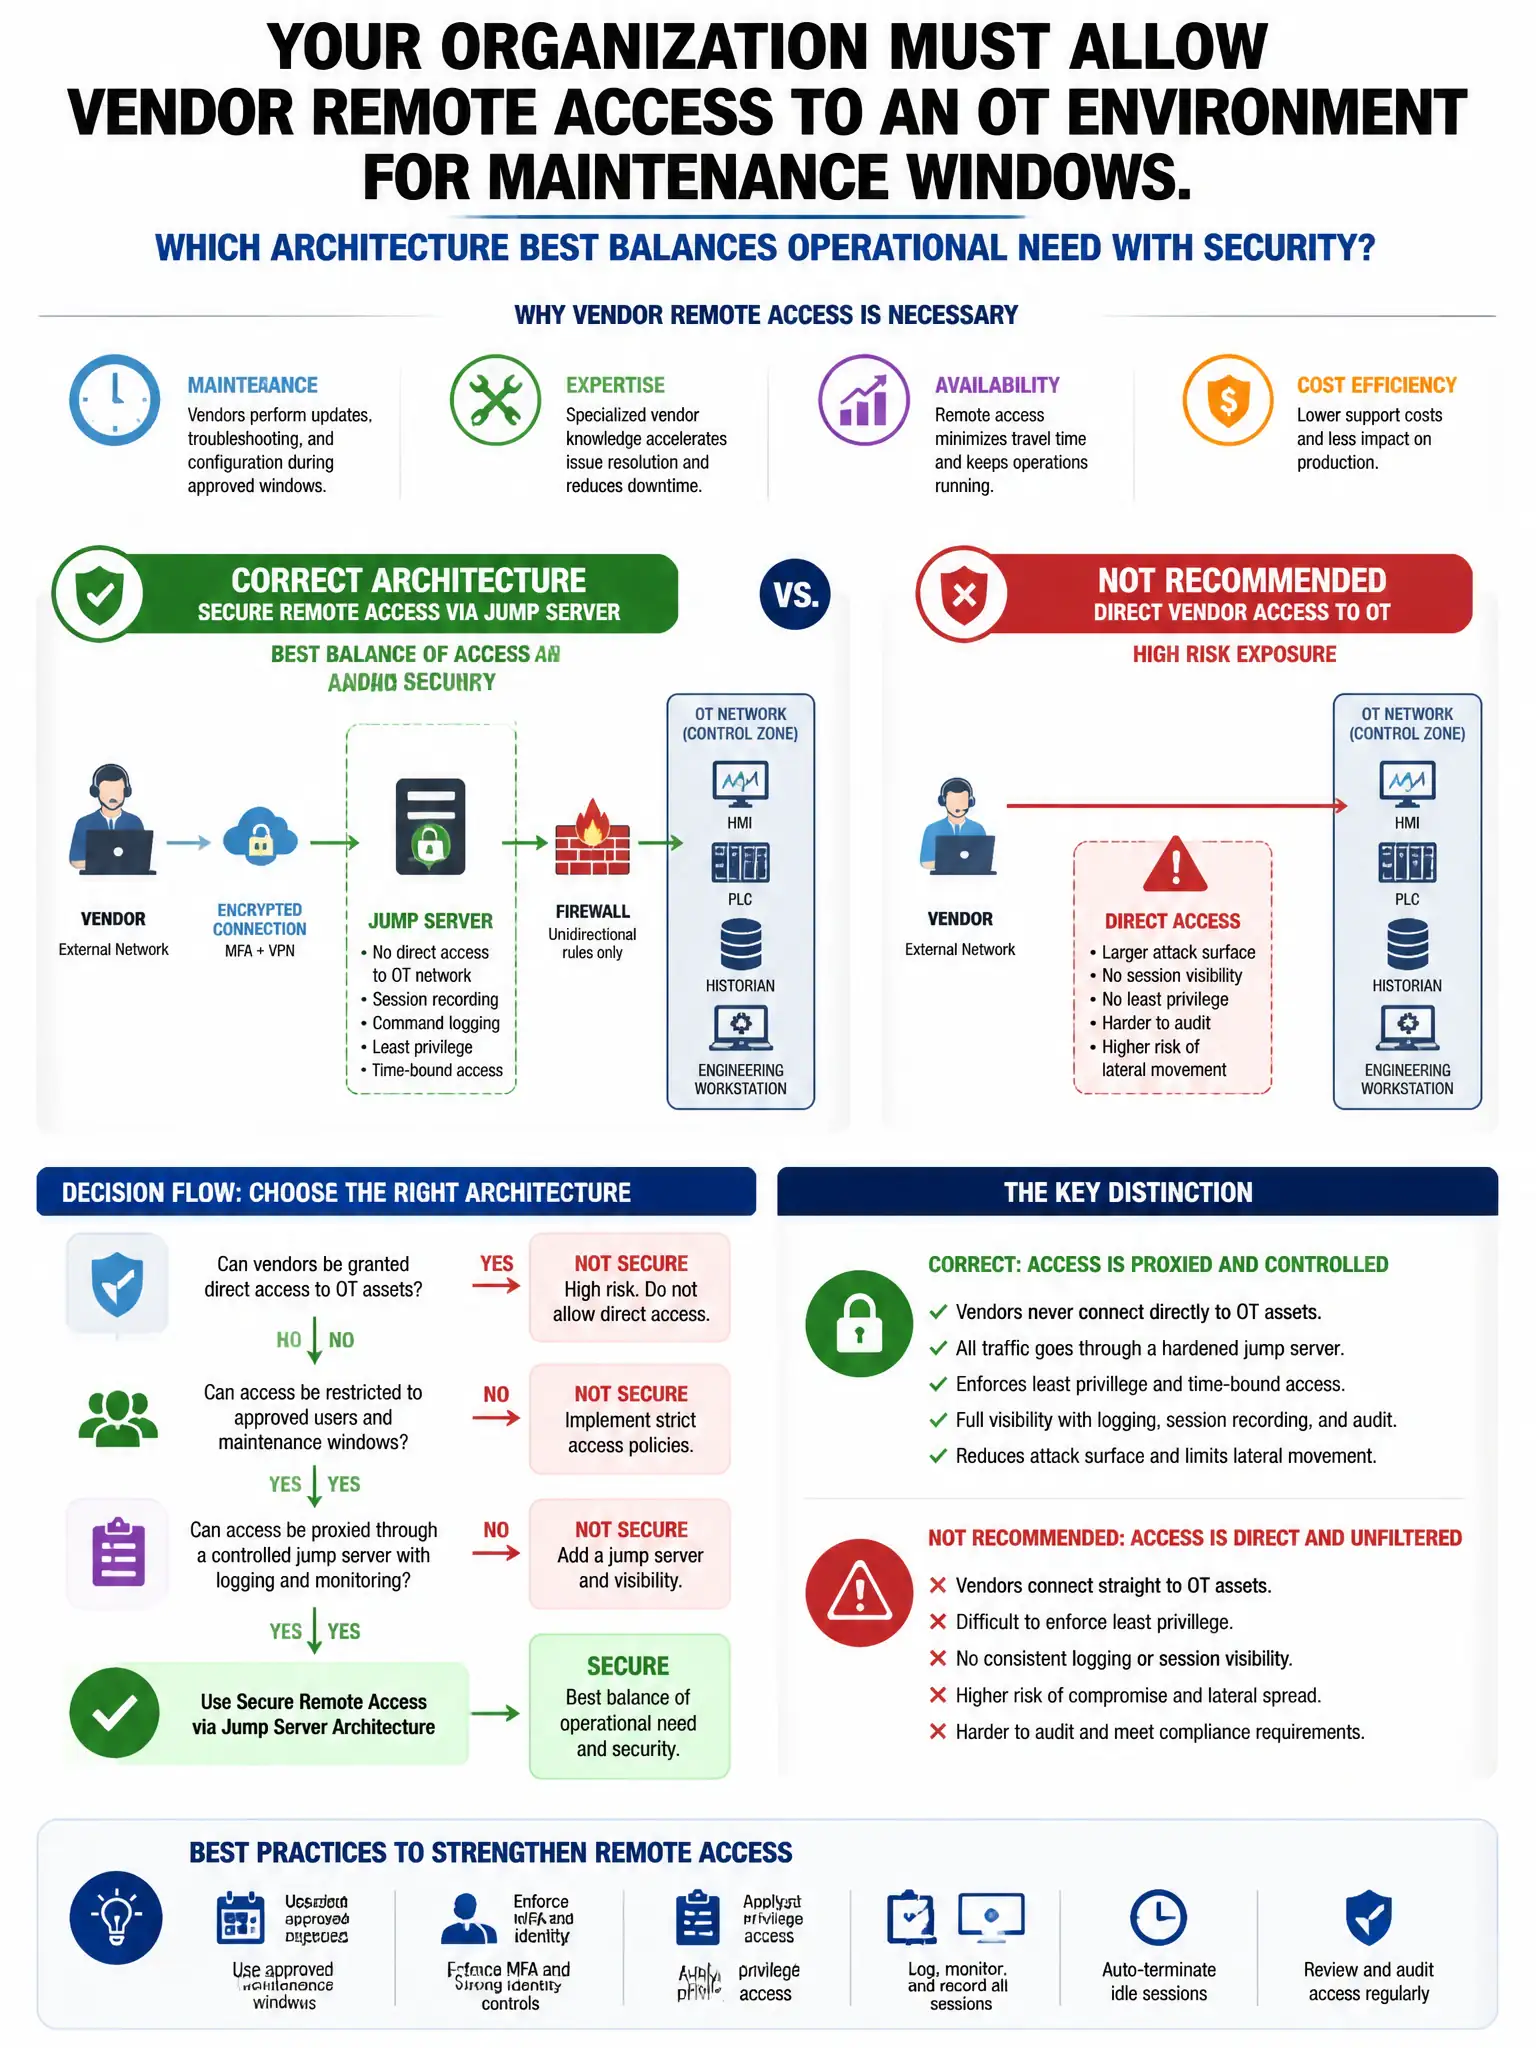
You want a jump server in a dedicated vendor DMZ with multi-factor authentication, recorded sessions, and time-limited approvals. That gives you one controlled entry point and keeps vendor access from becoming permanent. Permanent VPN access or direct RDP just opens a hole you can't quickly close.
Full Explanation
The jump server in a dedicated vendor DMZ, with vendor authentication using multi-factor authentication, recorded sessions, and time-limited access approved per maintenance window, is correct because it enforces a single point of ingress, reduces credential theft risk, provides accountability through session recording, and removes persistent exposure. The permanent VPN credential that connects directly to the OT segment is wrong because permanent credentials with direct OT access violate least privilege and remove the ability to revoke access instantly. The option allowing vendors to use RDP directly over the internet to OT HMI systems is wrong because direct RDP over the internet is highly exposed. The permanent site-to-site VPN between the vendor network and the OT VLAN is wrong because it extends trust to the vendor's entire network indefinitely.