
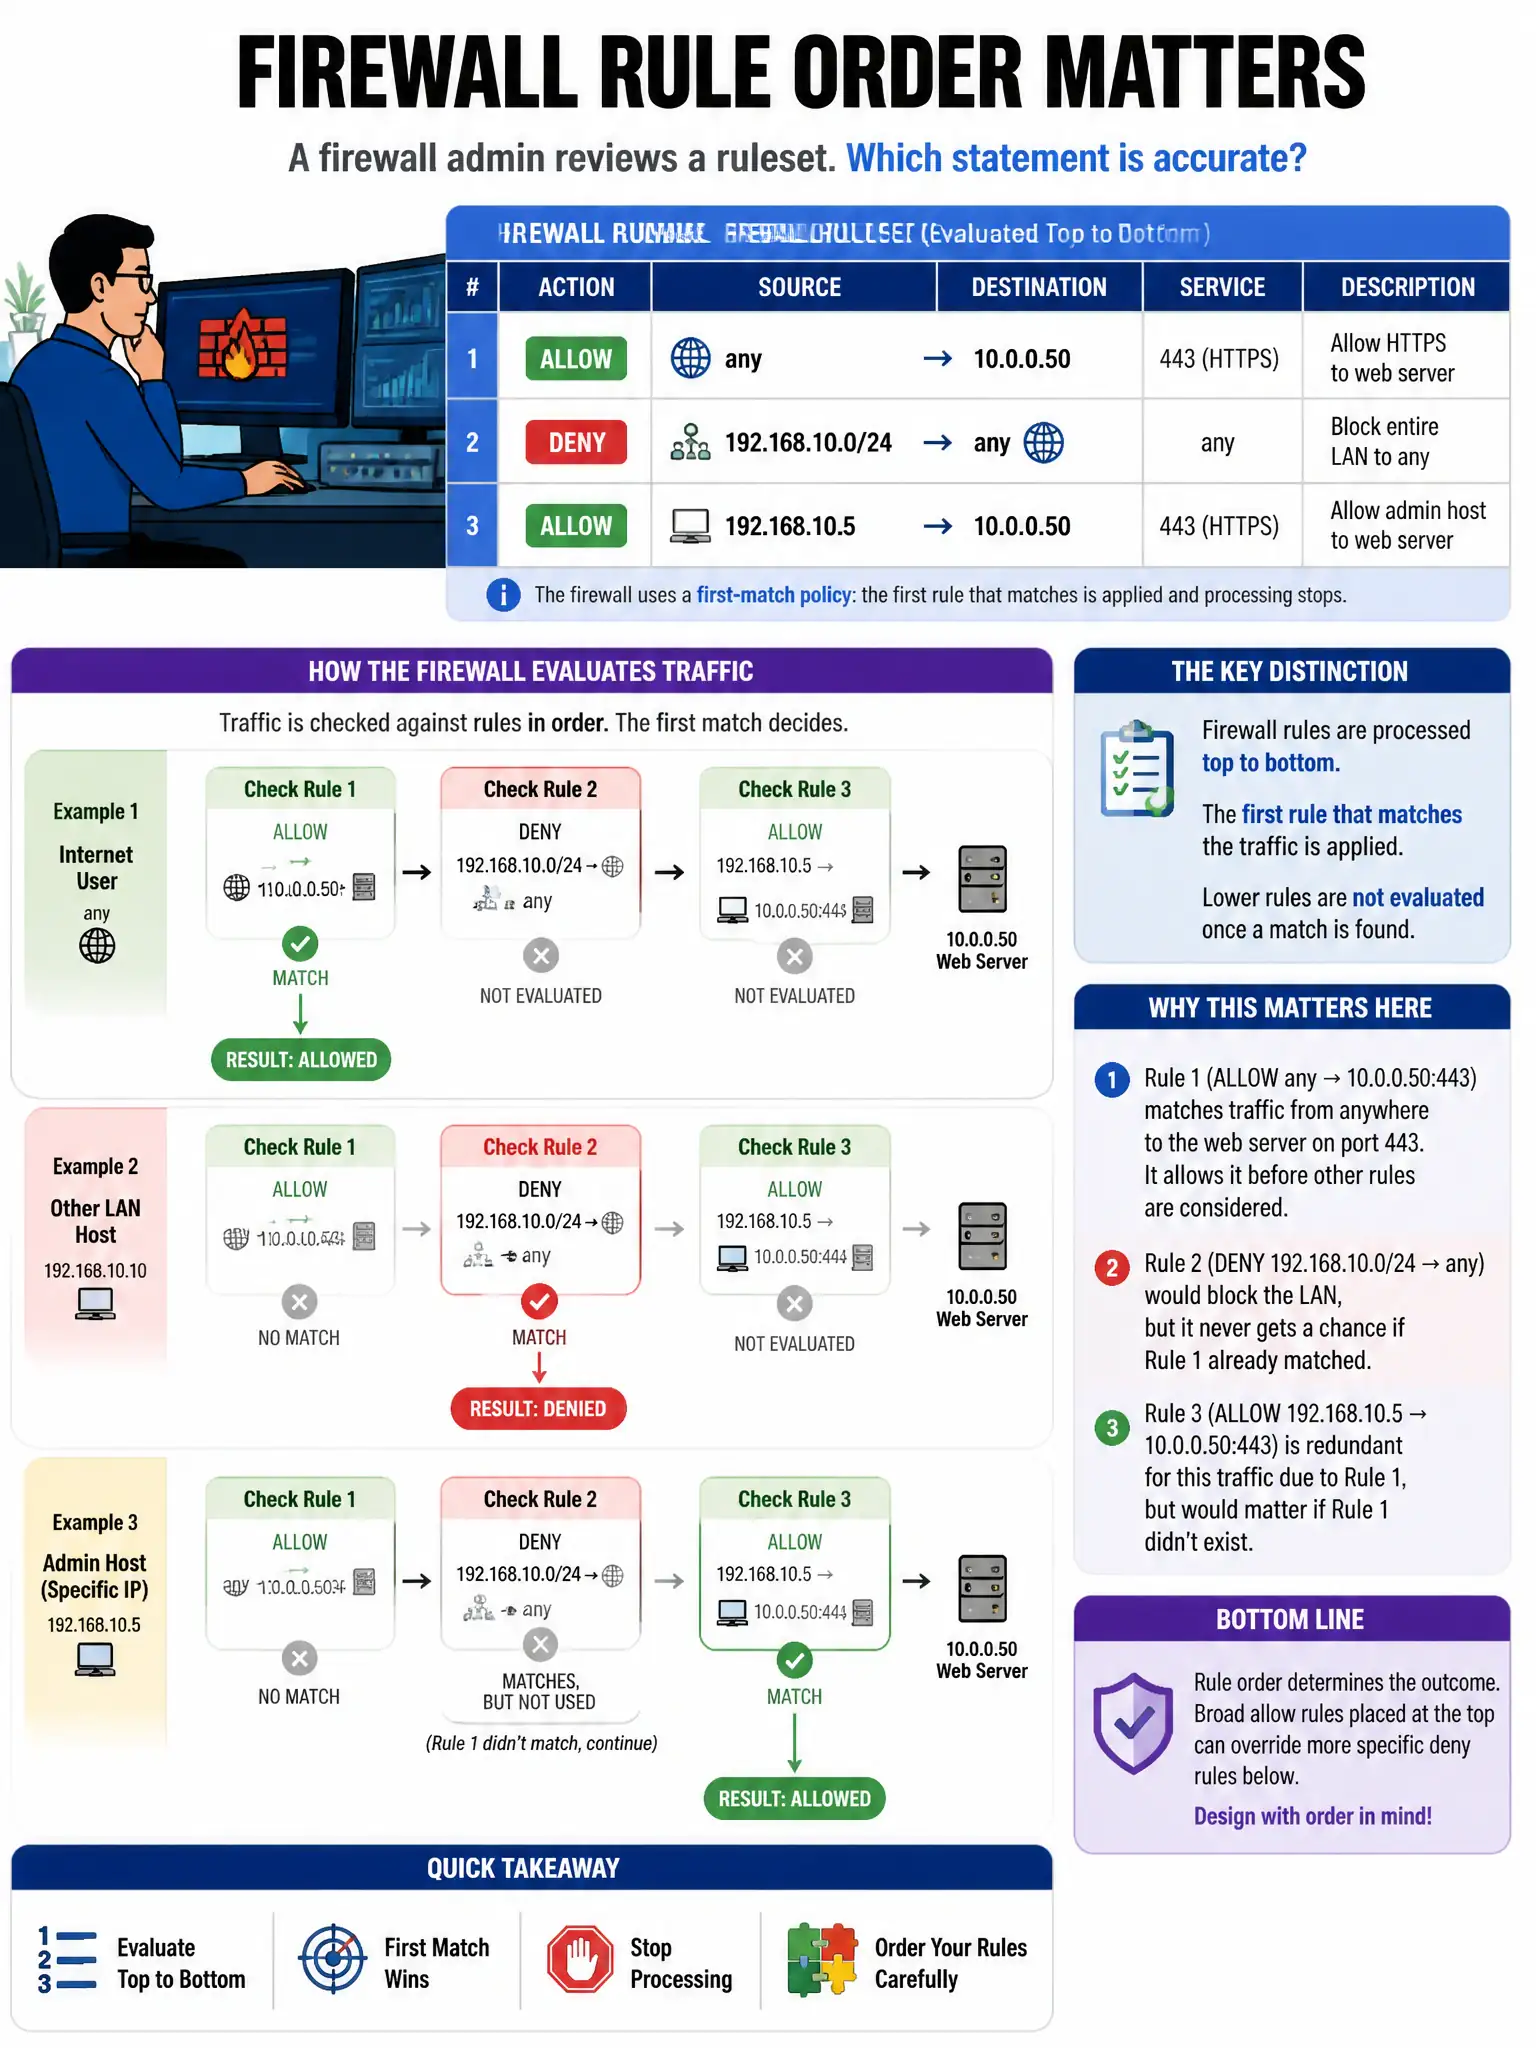
A firewall admin reviews a ruleset and finds: Rule 1 ALLOW any → 10.0.0.50:443, Rule 2 DENY 192.168.10.0/24 → any, Rule 3 ALLOW 192.168.10.5 → 10.0.0.50:443. Which statement is accurate about Rule 3?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — most firewalls evaluate rules top-down and stop at the first match. Rule 2 DENY covers the entire 192.168.10.0/24 subnet including .10.5, so Rule 3 is never reached — it is a shadowed rule.
Full Explanation
The accurate statement is that Rule 3 is shadowed by Rule 2 and never evaluated for 192.168.10.5. Most firewalls evaluate top-down and stop at first match. Rule 2 denies all 192.168.10.0/24, including .5, so Rule 3 is shadowed. The claim that Rule 3 is effective and allows .5 to reach 10.0.0.50:443 is wrong because Rule 2 matches first. The claim that Rule 3 overrides Rule 1 by specificity is wrong because order controls top-down rulesets. The claim that Rule 3 creates a conflict dropping all 192.168.10.0/24 is wrong because there is no conflict; the deny simply takes effect.