
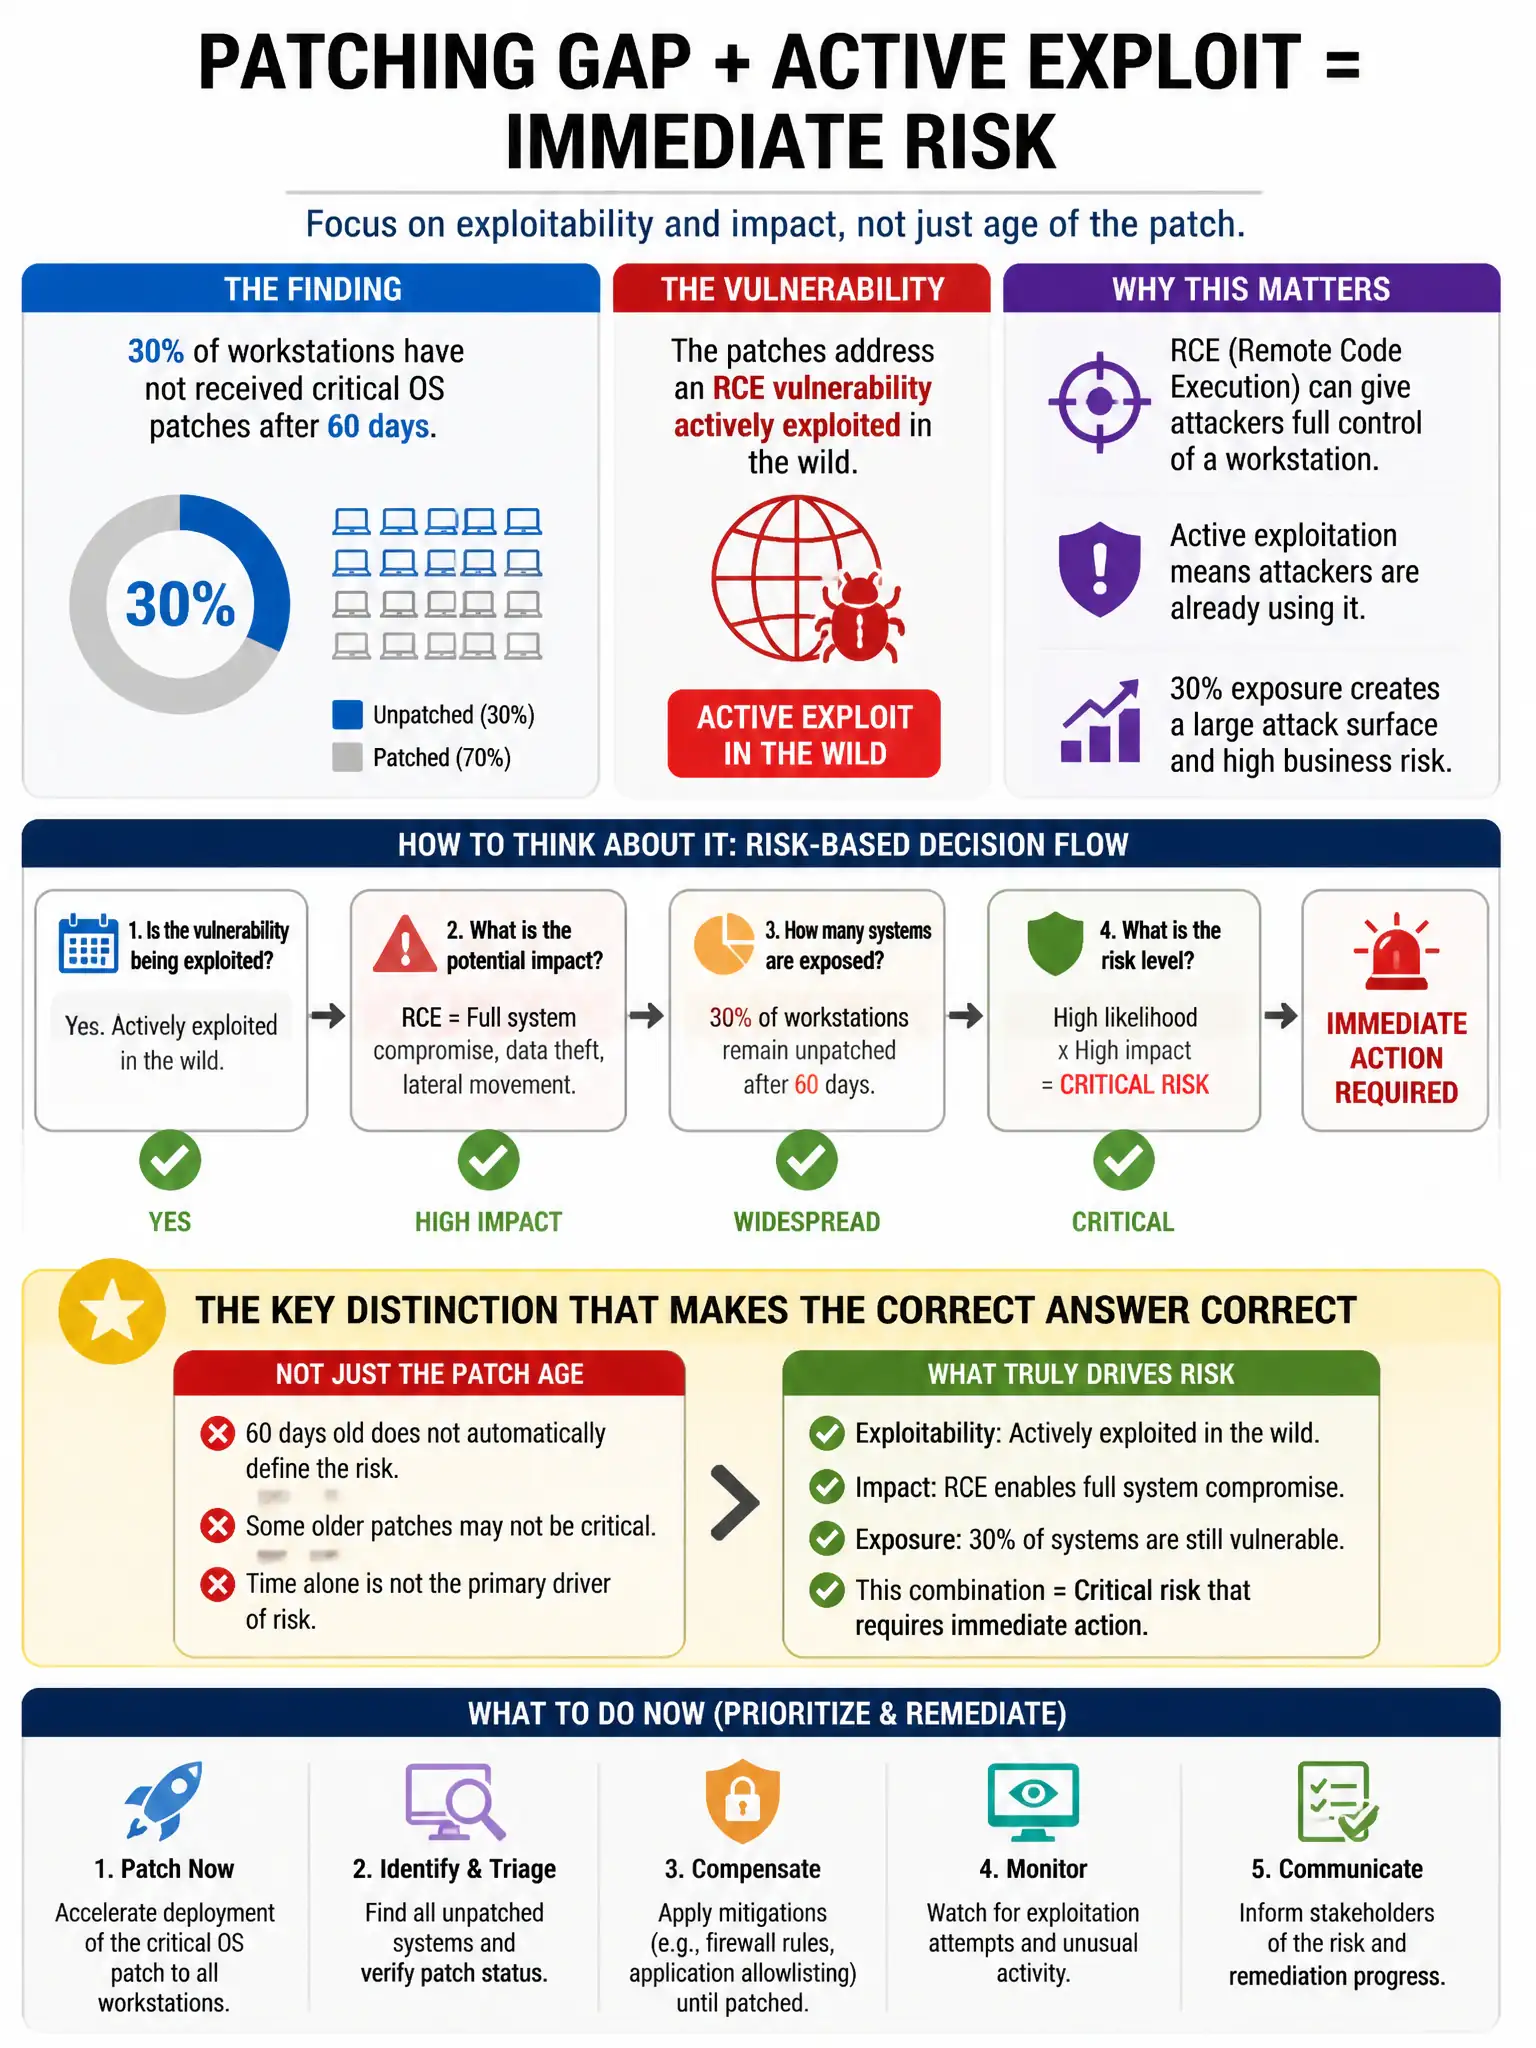
A security engineer finds that 30% of workstations have not received critical OS patches after 60 days. The patches address an RCE vulnerability actively exploited in the wild. What is the BEST immediate remediation approach?
Select an answer to reveal the explanation.
Short Explanation
When a critical RCE is being actively exploited, you can't wait around. Force-deploy the patches now, then use network segmentation and enhanced monitoring to protect systems until patching finishes.
Full Explanation
The force-deploy option is correct because active exploitation of a critical RCE vulnerability requires urgent action. Force-deploying patches addresses the vulnerability directly, while compensating controls such as network segmentation and enhanced monitoring protect unpatched systems until remediation is complete. The reminder-email option is wrong because email reminders are too slow for an actively exploited critical vulnerability. The accept-risk option is wrong because relying on the 70% patched majority still leaves 30% unpatched, which is a significant number of vulnerable entry points for an actively exploited RCE. The scan-and-wait option is wrong because waiting for a scheduled window leaves systems exposed when active exploitation is confirmed.