
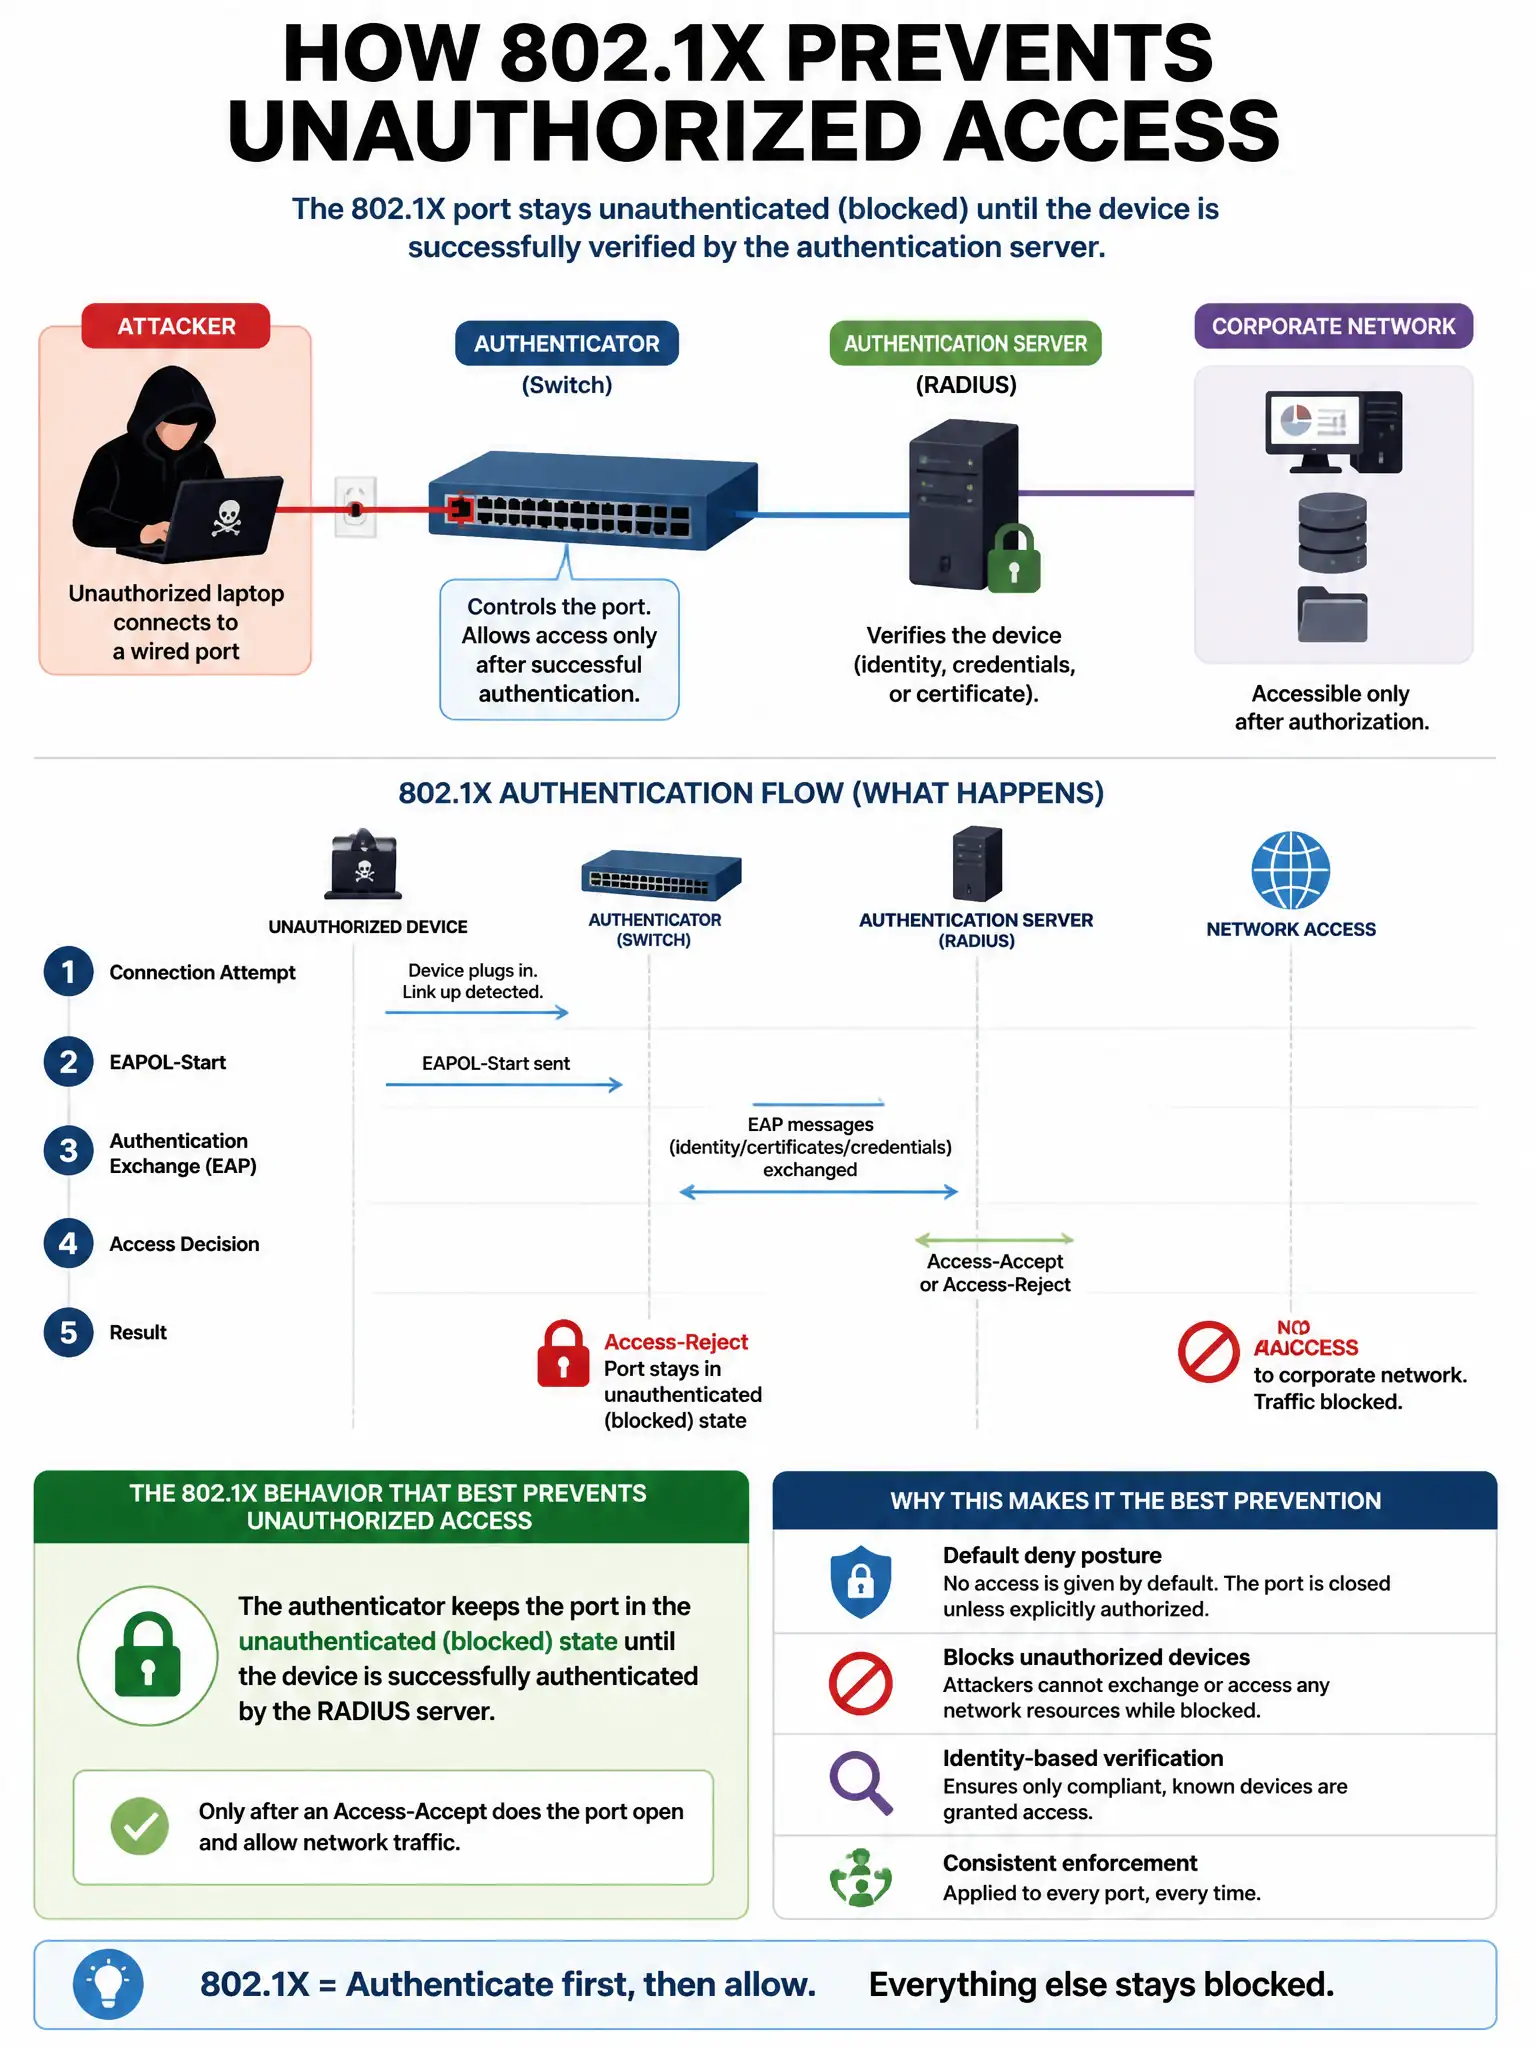
An organization uses 802.1X for network access control. An attacker attempts to connect an unauthorized laptop to a wired port. Which 802.1X behavior BEST prevents unauthorized access?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — 802.1X in enforcing mode blocks all traffic from an unauthenticated supplicant, so you don't get any network access until credentials are validated. Assigning a failed device to a guest VLAN still grants some access, which may not be appropriate.
Full Explanation
The switch blocking all traffic from the port until successful 802.1X authentication is completed is correct because 802.1X enforcing mode blocks all traffic from unauthenticated supplicants, preventing network access until credentials are validated. The guest VLAN assignment after authentication failure is wrong because it still grants some network access, which may not be appropriate. Logging the MAC address and alerting the SIEM is wrong because those are detective controls that do not prevent initial access. Rate limiting the unauthorized device's traffic is wrong because it still allows some traffic, which could be exploited.