
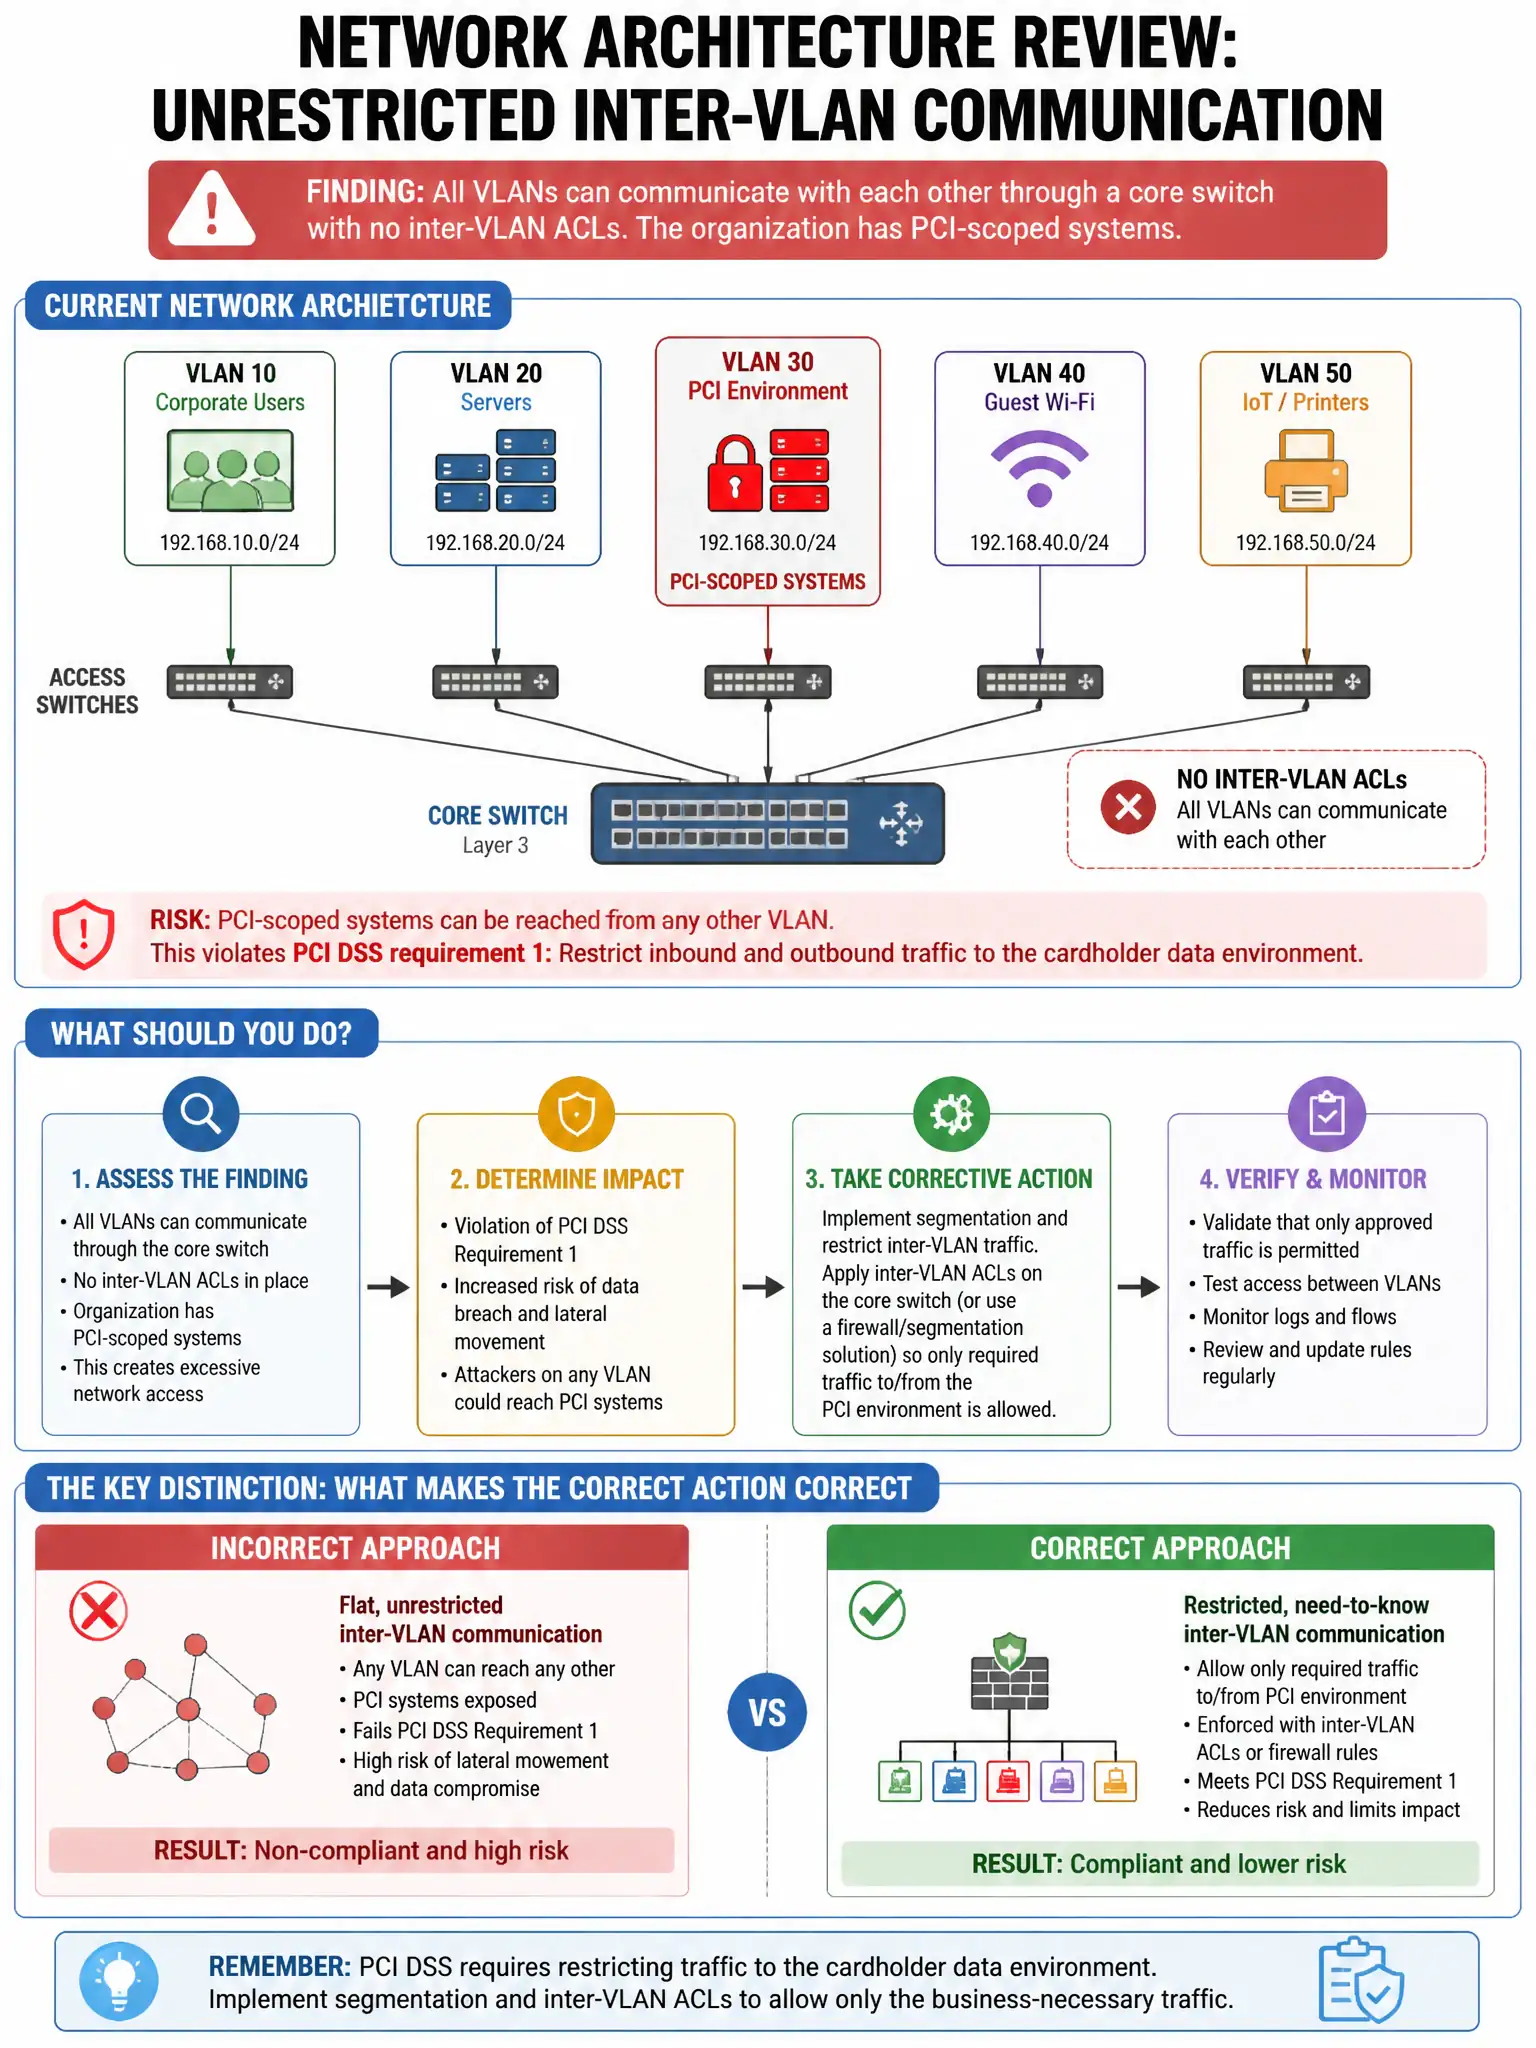
During a network architecture review, you find that all VLANs can communicate with each other through a core switch with no inter-VLAN ACLs. The organization has PCI-scoped systems in VLAN 10 and user workstations in VLAN 20. What is the MOST critical remediation?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need ACLs on the core switch to restrict traffic between VLAN 20 and VLAN 10 because that directly enforces isolation between user workstations and PCI-scoped systems.
Full Explanation
Implementing ACLs on the core switch to restrict traffic between VLAN 20 and VLAN 10 is correct because ACLs between VLANs directly enforce the required isolation between user workstations and PCI-scoped systems, satisfying segmentation requirements. Enabling port security on all access layer switches is wrong because port security prevents unauthorized devices on switch ports but does not restrict inter-VLAN communication. Moving PCI systems to a separate physical network is wrong because physical separation is an option, but ACLs on the existing infrastructure are the most practical immediate remediation. Deploying an IDS sensor on the VLAN 10 segment is wrong because an IDS is a detective control that does not prevent the communication.