
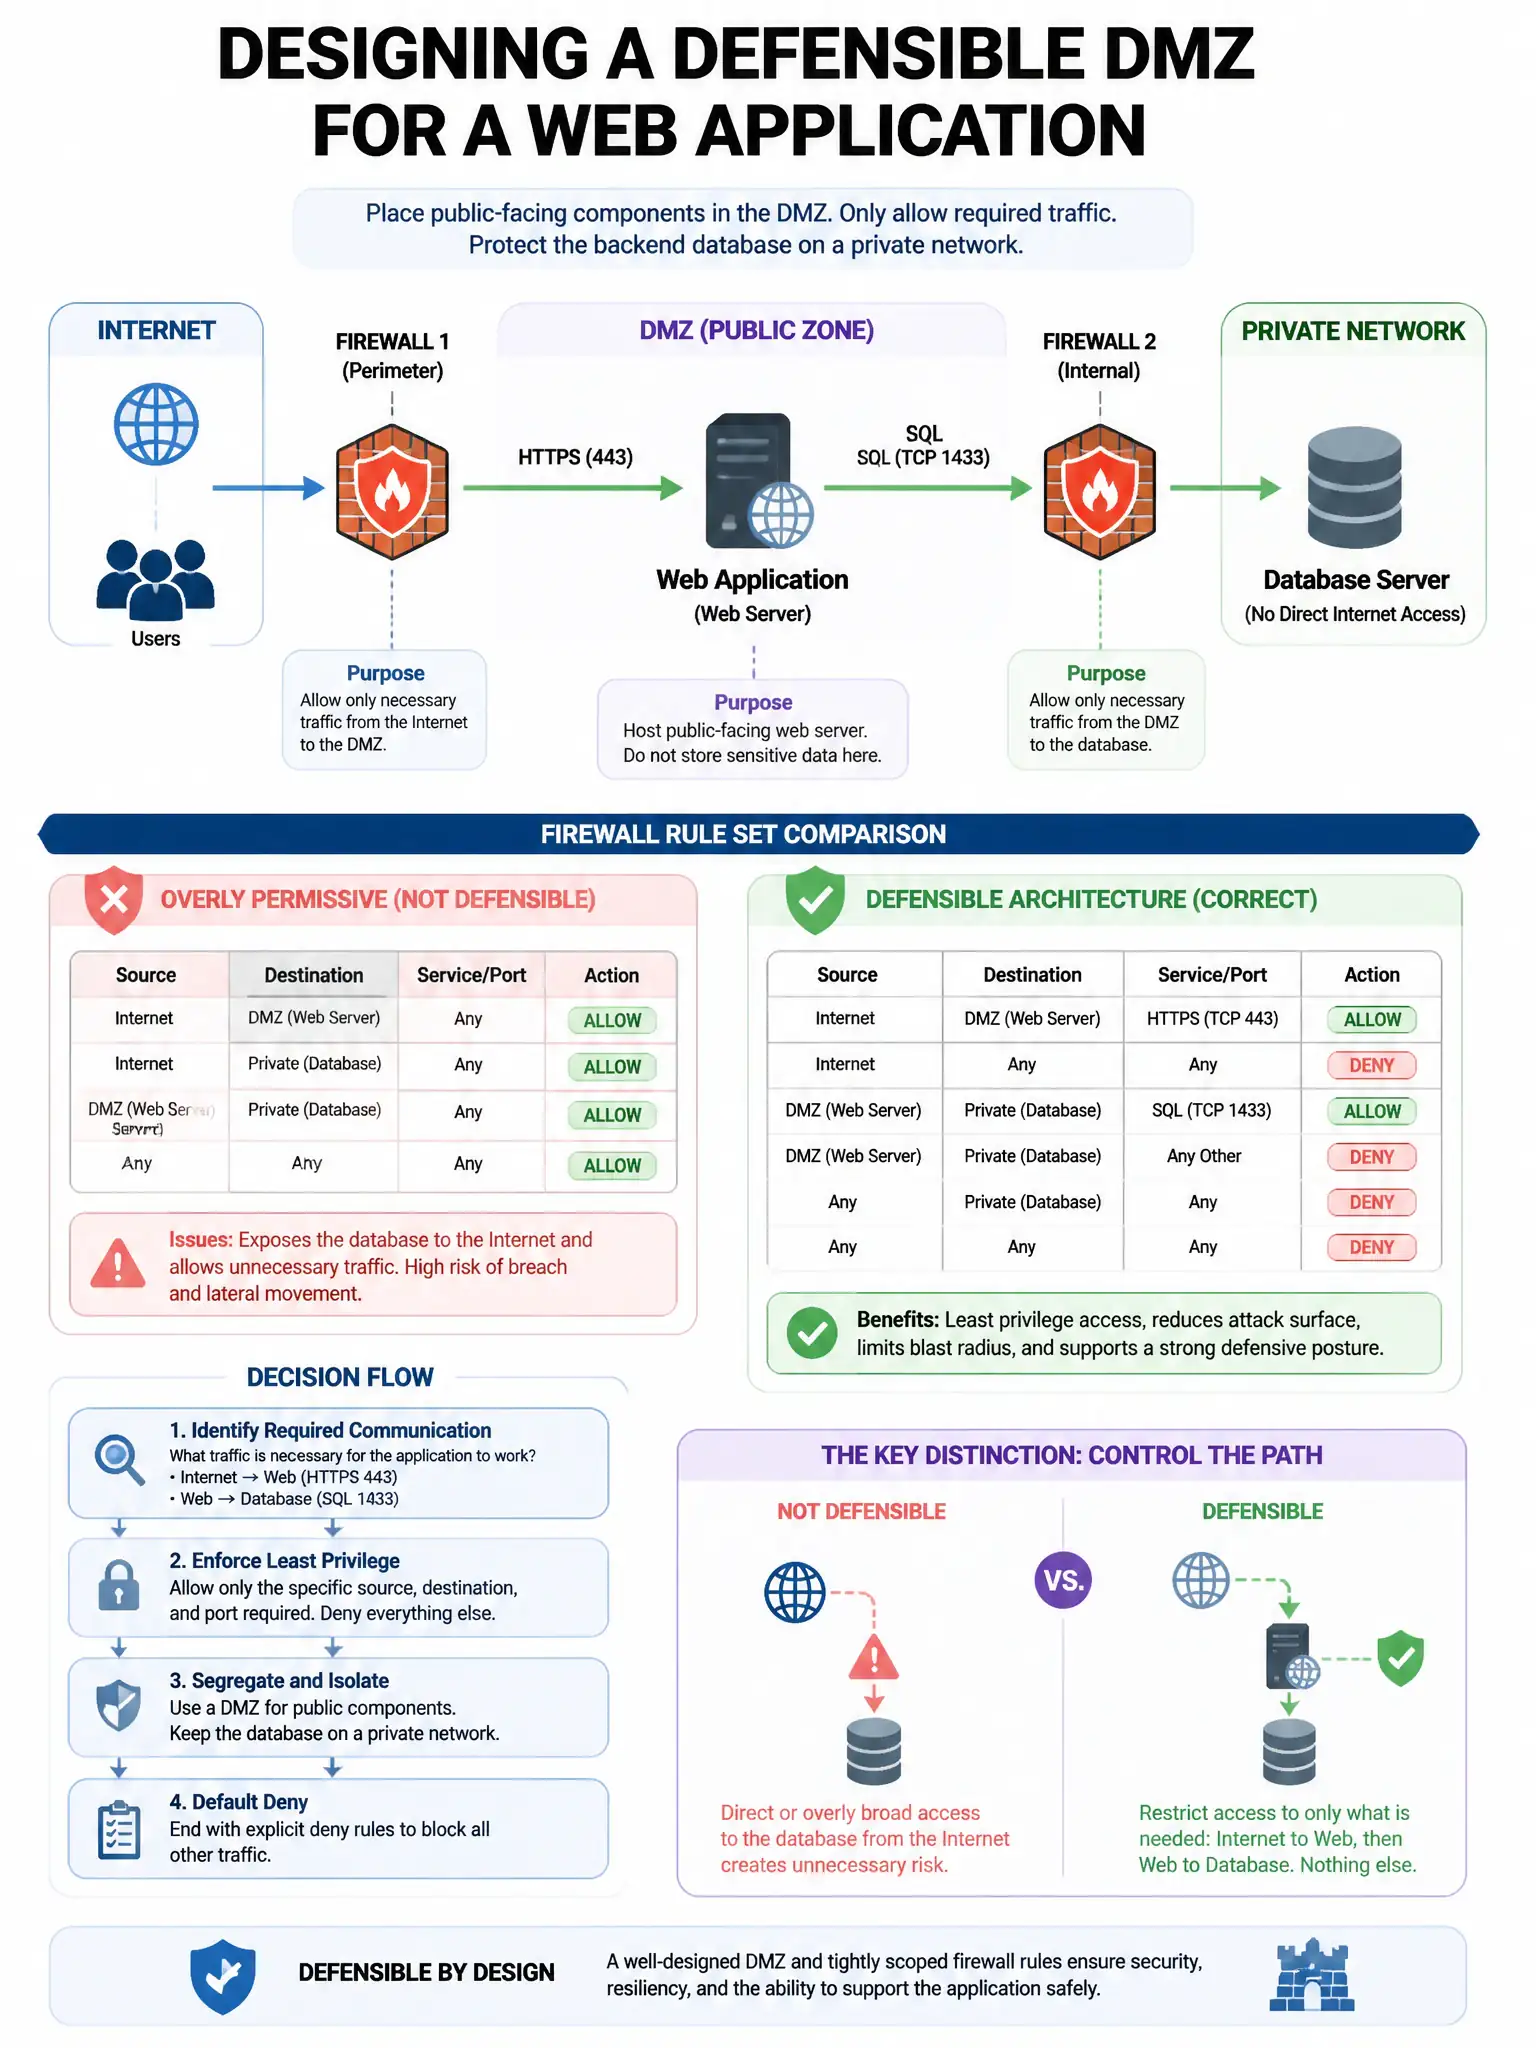
A security architect is designing a DMZ for a web application that must communicate with a backend database. Which firewall rule set best represents defensible architecture?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you want the rule set that allows only HTTPS into the DMZ, lets the DMZ reach the database only on 1433 to the specific database IP, and denies database-initiated connections back to the DMZ. Anything that opens broader paths is too permissive.
Full Explanation
The correct rule set restricts inbound traffic to HTTPS only, limits DMZ-to-DB communication to only the required port and specific IP, and prevents database-initiated connections back to the DMZ. The rule set allowing any DMZ-to-DB traffic is overly permissive. The rule set allowing any internet-to-DMZ traffic is dangerous. The rule set allowing all TCP from DMZ to DB provides excessive access.