
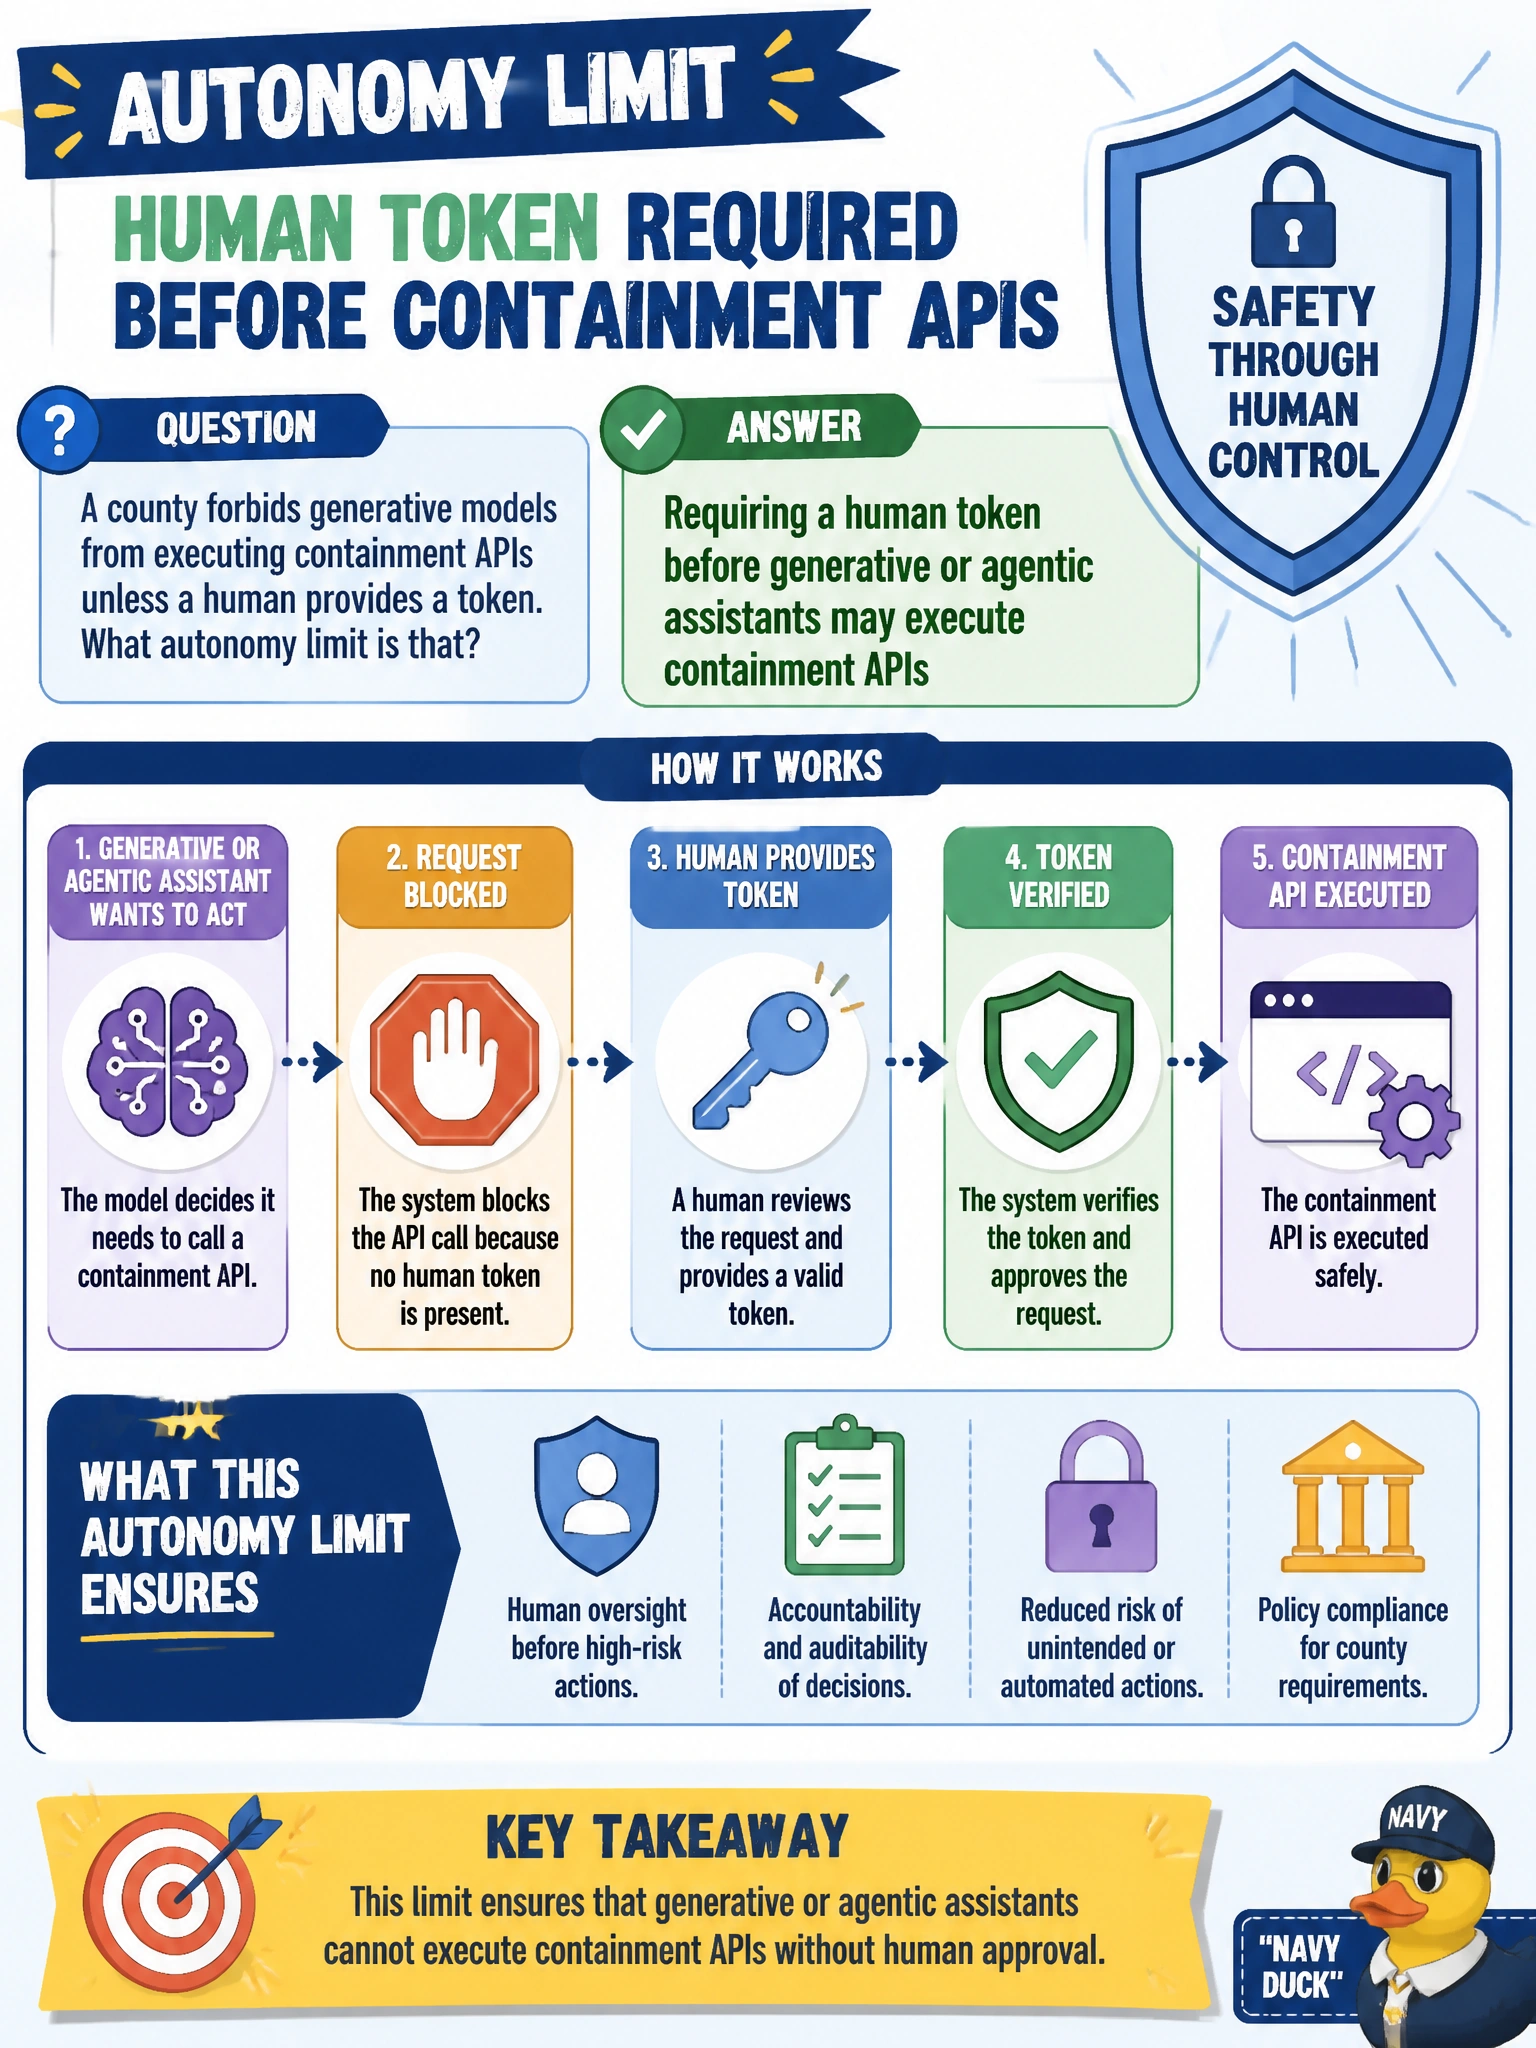
A county forbids generative models from executing containment APIs unless a human provides a token. What autonomy limit is that?
Select an answer to reveal the explanation.
Short Explanation
Containment is the emergency brake—generative helpers may suggest, but a human token turns the key. You're still gating live execution up front, so reviewing a token after it's run, requesting one while it's running, or swapping in a system token don't count since you'll have skipped human approval before you act. Autonomy limits keep agentic IR from driving alone.
Full Explanation
A county that forbids generative models from executing containment APIs unless a human provides a token is requiring a human token before generative or agentic assistants may execute containment APIs. Containment changes system state—isolating hosts, disabling accounts, blocking network paths—and mistaken or hallucinated actions create civic outages. A human-in-the-loop token keeps generative systems in an advisory or draft role until an authorized operator deliberately unlocks write execution for that action. Why the other options fail by concept: Reviewing a human token after generative or agentic assistants may execute containment APIs misses the point because after-the-fact review lets the containment action run first, and it does not satisfy the county’s requirement for a human token before live execution of containment APIs. Requesting a human token while generative or agentic assistants may execute containment APIs is also wrong because a concurrent request does not block execution until approval arrives, so gating while running does not enforce the autonomy limit on actual execution beforehand. Requiring a system token before generative or agentic assistants may execute containment APIs fails for a different reason because a system-issued token is machine authorization without human approval, whereas the county rule specifically gates live containment API execution with a human token. Exam caveat: the human token must be attributable (who approved, when, which action) for audit; a shared break-glass password is not an adequate control. Operational check: verify in the county SOAR/IR integration that containment API calls from generative assistants fail closed without a fresh human approval token, and test that spoofed or missing tokens cannot isolate a lab host.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.