
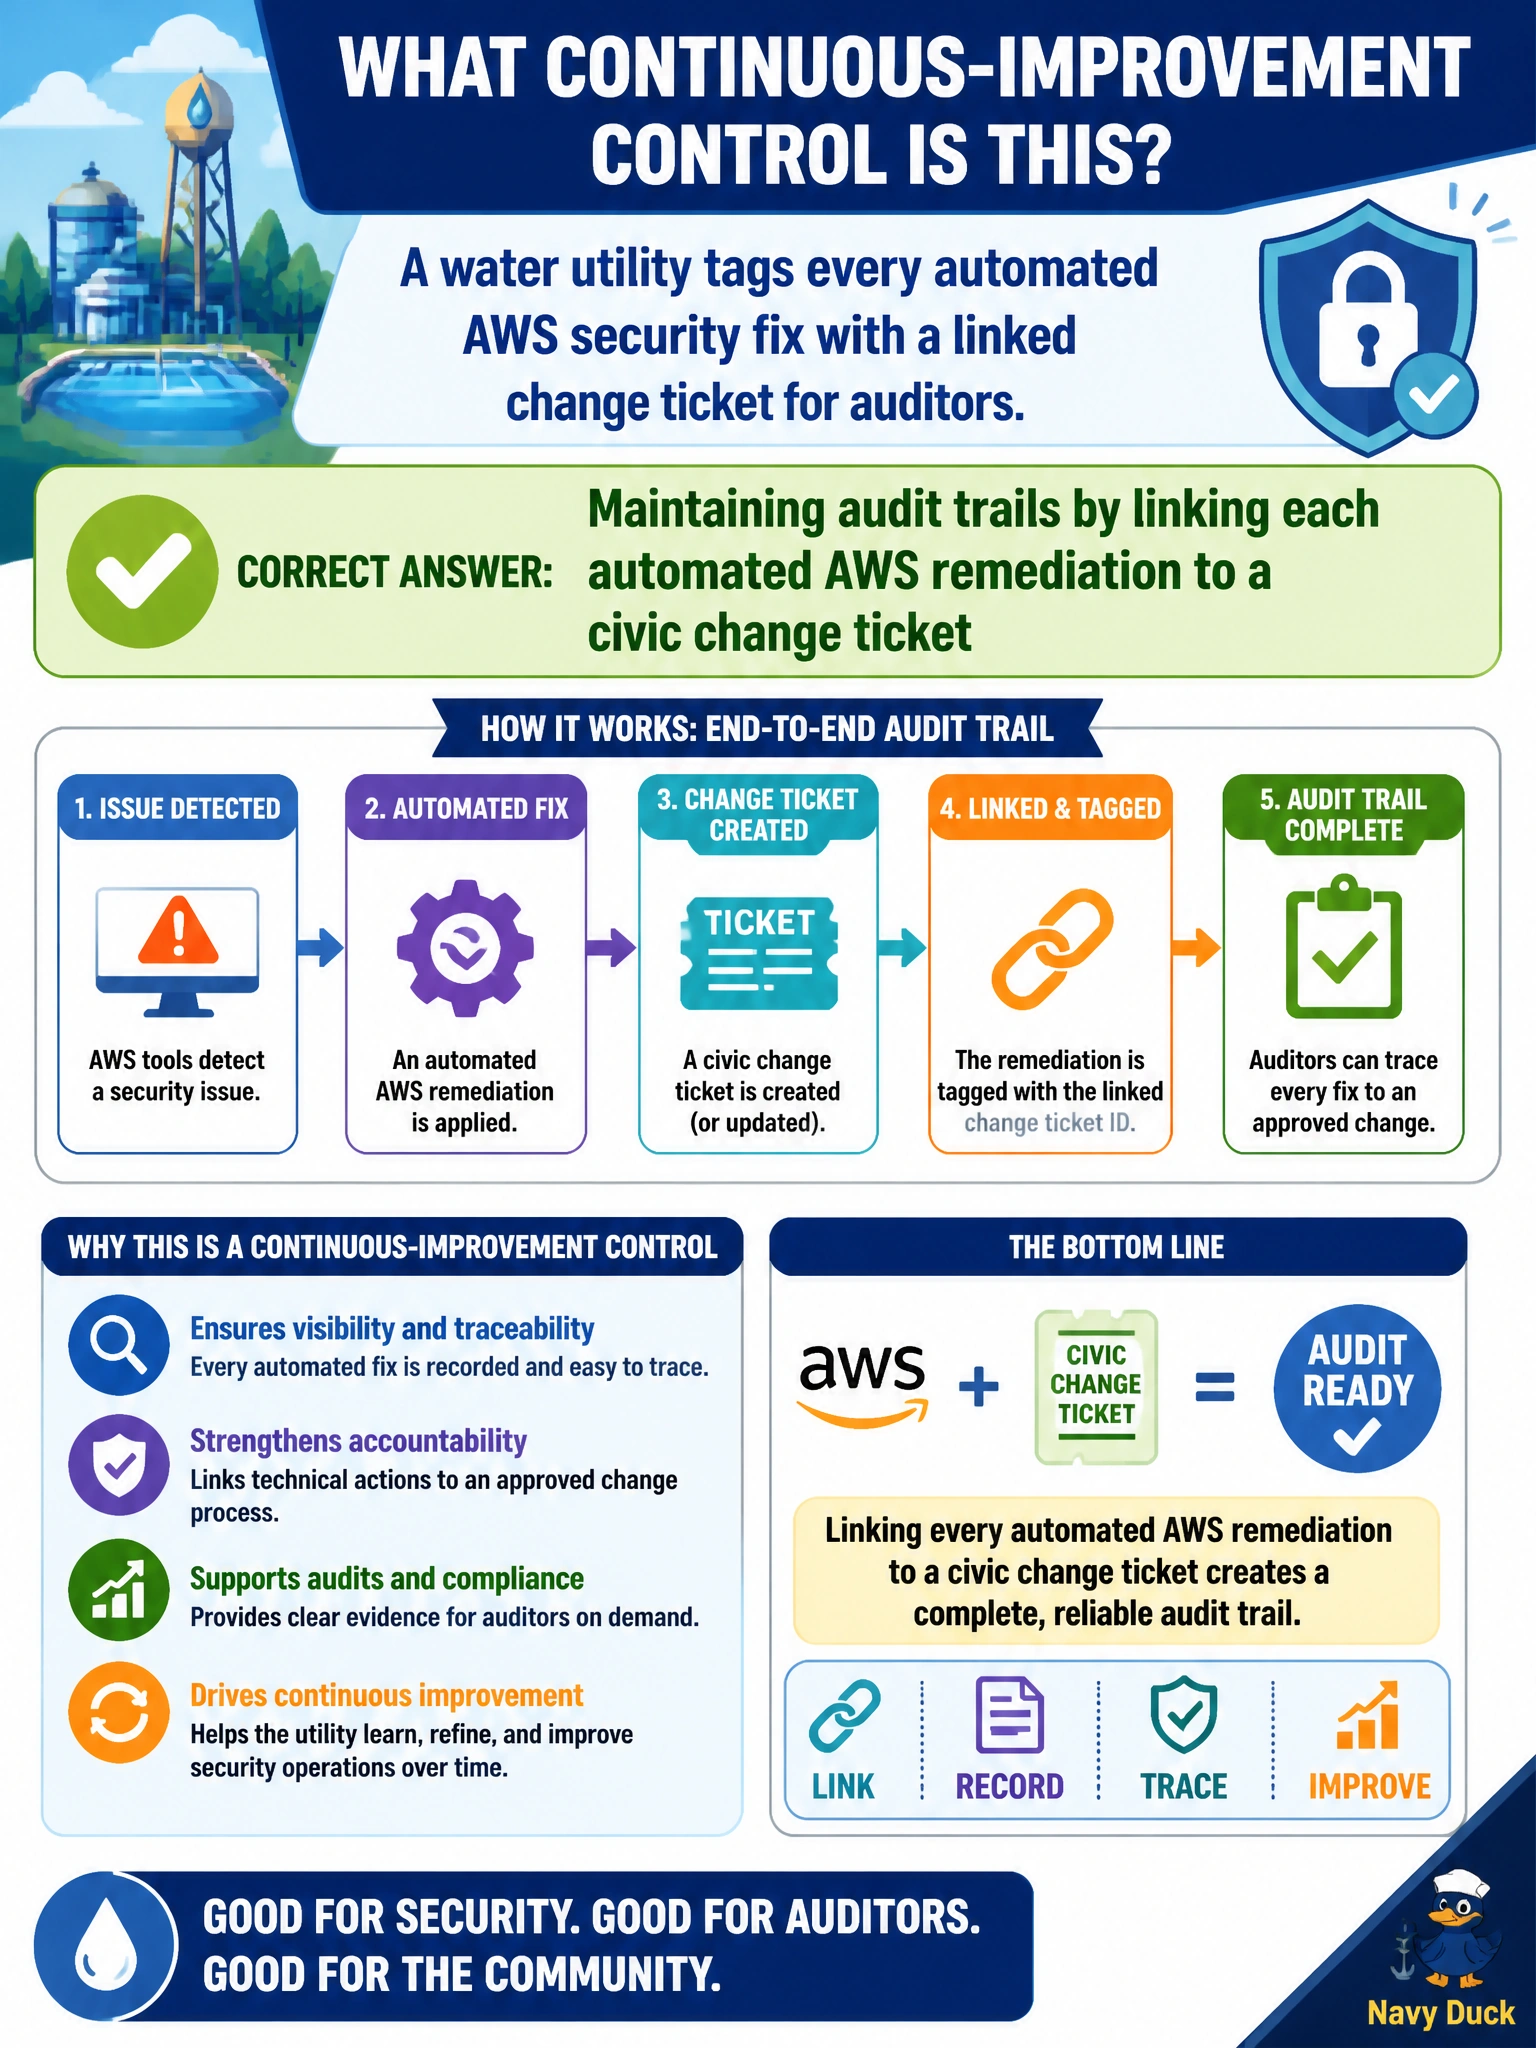
A water utility tags every automated AWS security fix with a linked change ticket for auditors. What continuous-improvement control is that?
Select an answer to reveal the explanation.
Short Explanation
Every automated fix gets a change-ticket collar—auditors and water regulators hate mystery remediations. Vendor billing records, aggregated summaries, and asset records won't give you the per-fix ticket proof you'll need. Tag the changes.
Full Explanation
Maintaining audit trails by linking each automated AWS remediation to a civic change ticket lets a water utility reconstruct who or what changed which control, when, and why—requirements familiar to auditors and water-sector oversight. Tagging automated fixes to tickets preserves narrative and approval context even when the actor is automation. That continuous-improvement control turns rapid remediations into accountable municipal changes rather than unexplained configuration churn.
Maintaining audit trails by linking each automated AWS remediation to a vendor billing record fails because billing records track cost allocation but do not tie each automated remediation to an auditable civic change ticket with approval context. Maintaining audit trails by linking aggregated AWS remediation summaries to a civic change ticket fails because aggregated summaries roll multiple fixes into one ticket and do not provide per-change linkage with resource IDs, rule names, and approval evidence for auditors. Maintaining audit trails by linking each automated AWS remediation to a civic asset record fails because asset records document inventory ownership, not per-change ticketed accountability with narrative and approval context for auditors.
Exam caveat: Link each automated remediation to a change ticket. Vendor billing records, aggregated summaries, and asset records are not audit trails; remediations without individual civic change-ticket links fail regulated municipal accountability.
Operational check for a water utility cloud team: require automation to create or update a change ticket per remediation with resource IDs and rule names, sample a week of automated fixes against ticket links before an audit rehearsal, and reject pipelines that can mutate production security settings without a civic change record.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.