
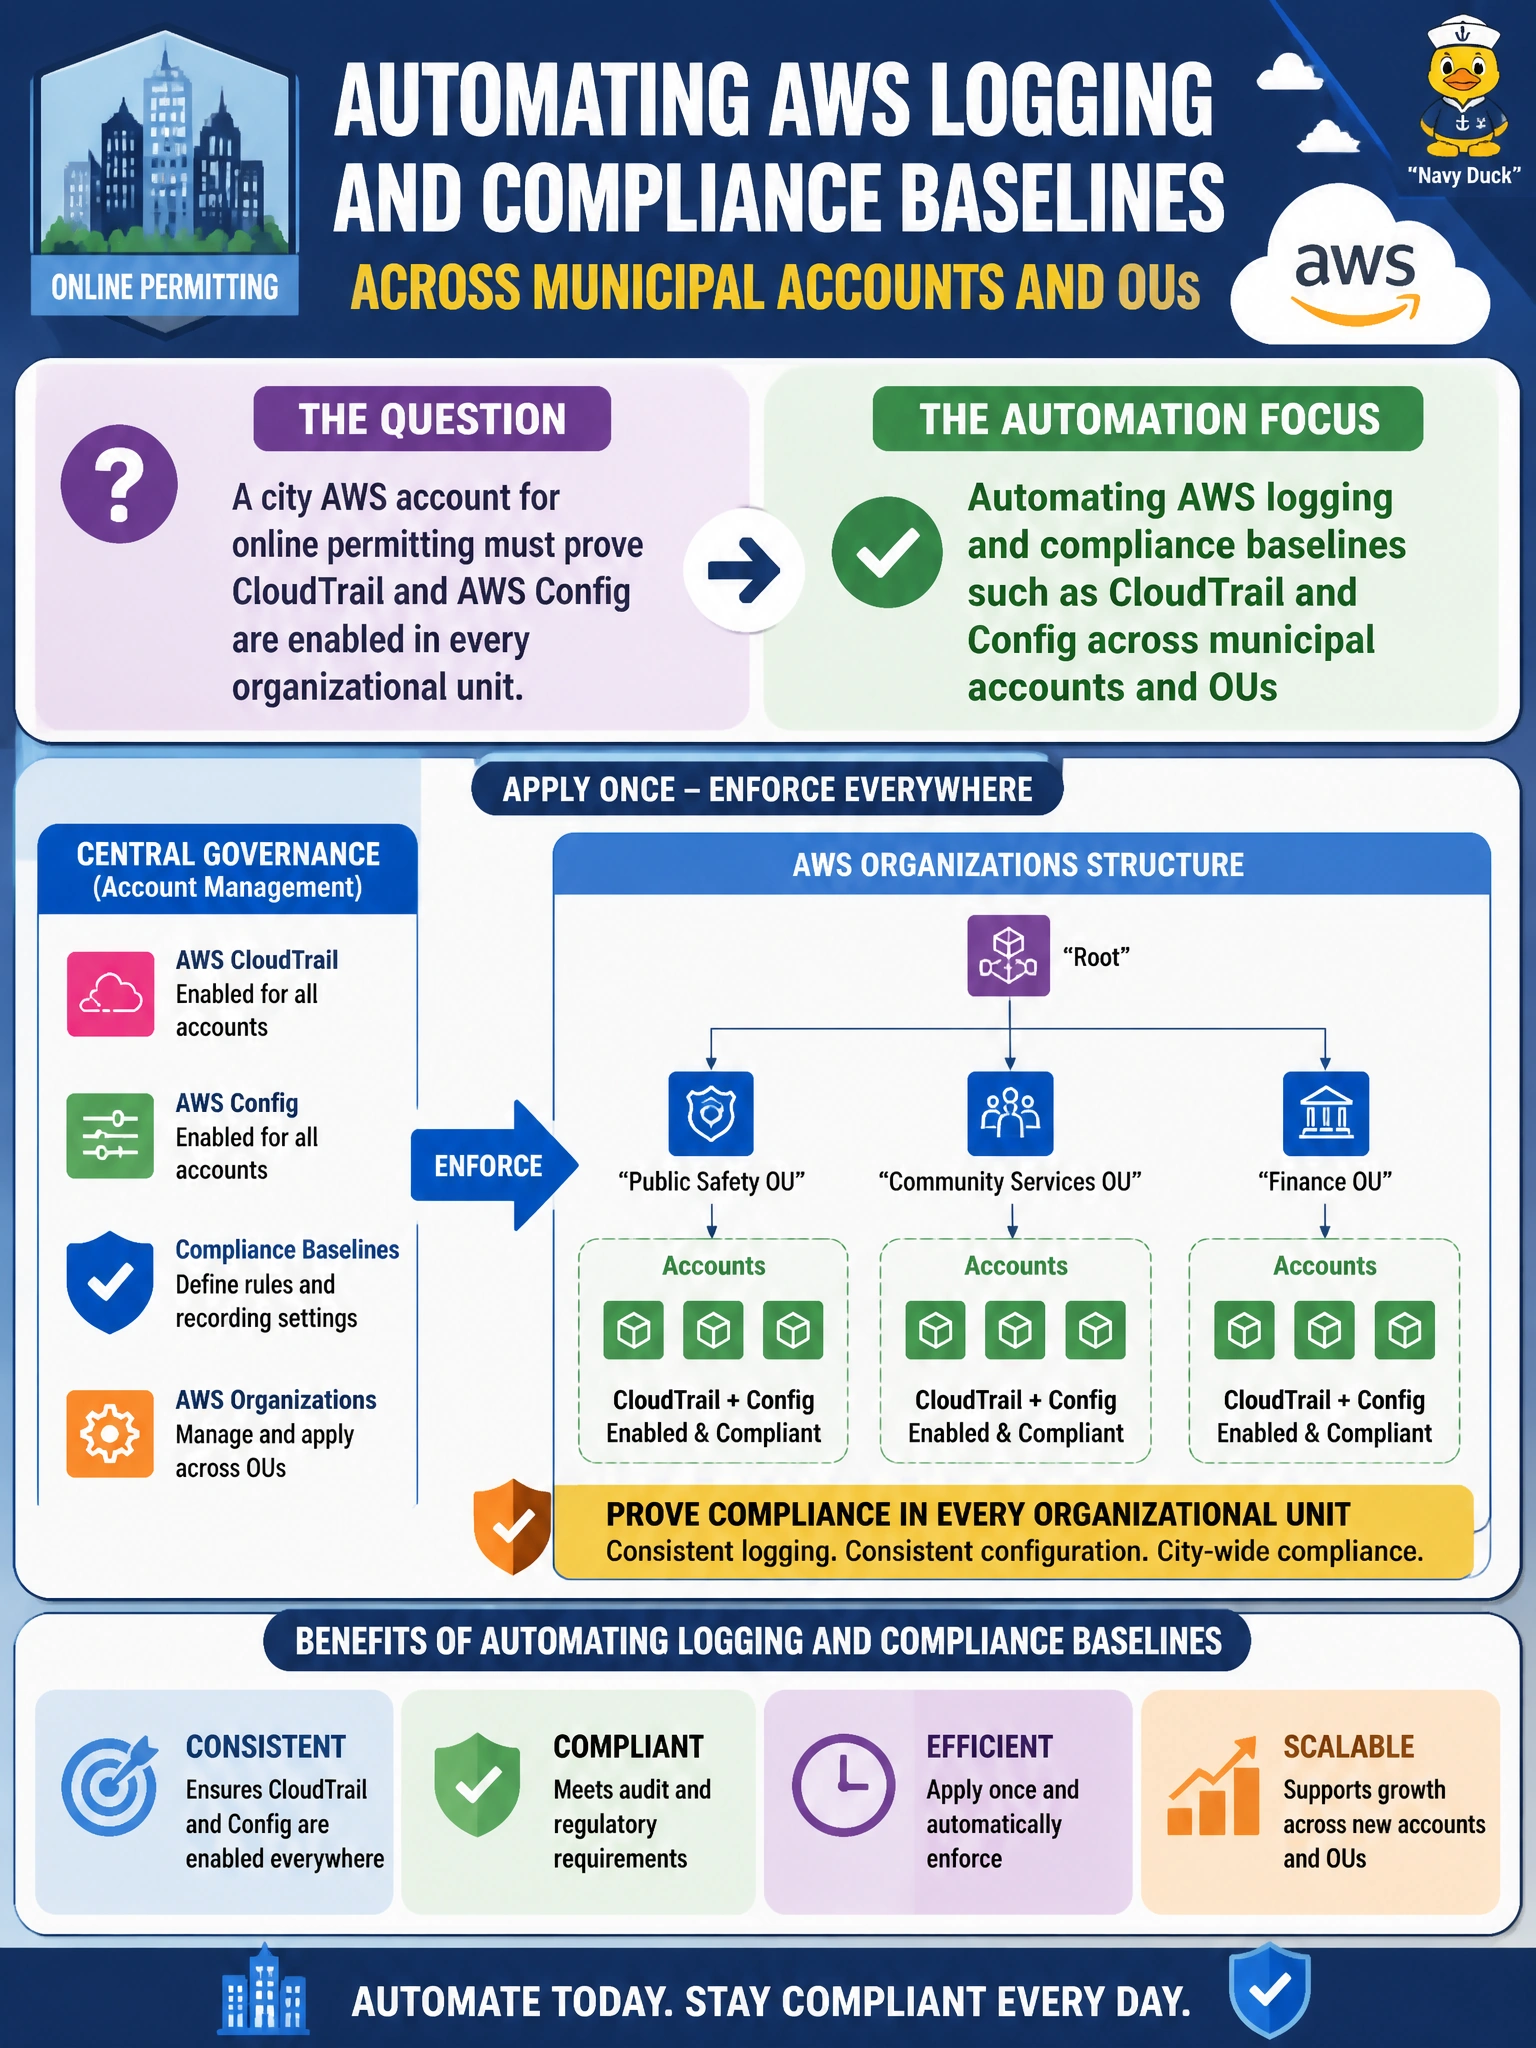
A city AWS account for online permitting must prove CloudTrail and AWS Config are enabled in every organizational unit. What automation focus is that?
Select an answer to reveal the explanation.
Short Explanation
Permit apps need receipts: you've got to have CloudTrail and Config on in every OU, and S3 server access logging won't turn them on. Automate the baseline so municipal accounts stay honest. Trying to run your logging baselines with Organizations SCP enforcement or VPC Flow Log captures won't work because they don't create trails and recorders.
Full Explanation
Automating AWS logging and compliance baselines such as CloudTrail and Config across municipal accounts and OUs gives a city AWS estate for online permitting continuous, organization-scoped evidence that management and data-plane activity is recorded and that configuration posture is evaluated everywhere the org places workloads. Enabling these baselines in every organizational unit prevents silent gaps where a new OU or account for permitting microservices ships without trail or Config coverage. Automation—organization trails, delegated Config aggregators, or policy-as-code checks—keeps civic accountability from depending on seasonal manual effort.
Automating AWS logging and compliance baselines with Organizations SCP enforcement across municipal accounts and OUs fails by concept because SCPs provide preventive guardrails that allow or deny API actions, not organization CloudTrail trails or AWS Config recorders and rules, so enforcement alone cannot provide proof that logging baselines are enabled in every organizational unit. Automating AWS logging and compliance baselines with S3 server access logging across municipal accounts and OUs fails because S3 server access logging records only access to individual S3 buckets and does not enable CloudTrail trails or Config recorders or provide the immutable organization API activity logs and continuous configuration evaluation needed to demonstrate compliance across every OU. Automating AWS logging and compliance baselines with VPC Flow Log captures across municipal accounts and OUs fails because VPC Flow Logs collect network flow metadata for VPC traffic and do not enable CloudTrail trails or AWS Config recorders; they describe packet flows, not whether logging and configuration baselines are enabled organization-wide.
Exam caveat: Distinguish organization-wide CloudTrail and Config baselines from automating AWS logging and compliance baselines with Organizations SCP enforcement across municipal accounts and OUs, automating AWS logging and compliance baselines with S3 server access logging across municipal accounts and OUs, and automating AWS logging and compliance baselines with VPC Flow Log captures across municipal accounts and OUs. GASAE AWS automation items expect continuous logging and compliance coverage across municipal OUs when the stem requires proof in every OU.
Operational check for city cloud security: verify an organization CloudTrail covers all OUs used by permitting, confirm AWS Config recorders and rules are active in each account, run an account-creation or OU-move test to ensure new municipal accounts inherit logging baselines, and sample CloudTrail and Config evidence for a production permitting account during a change window.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.