
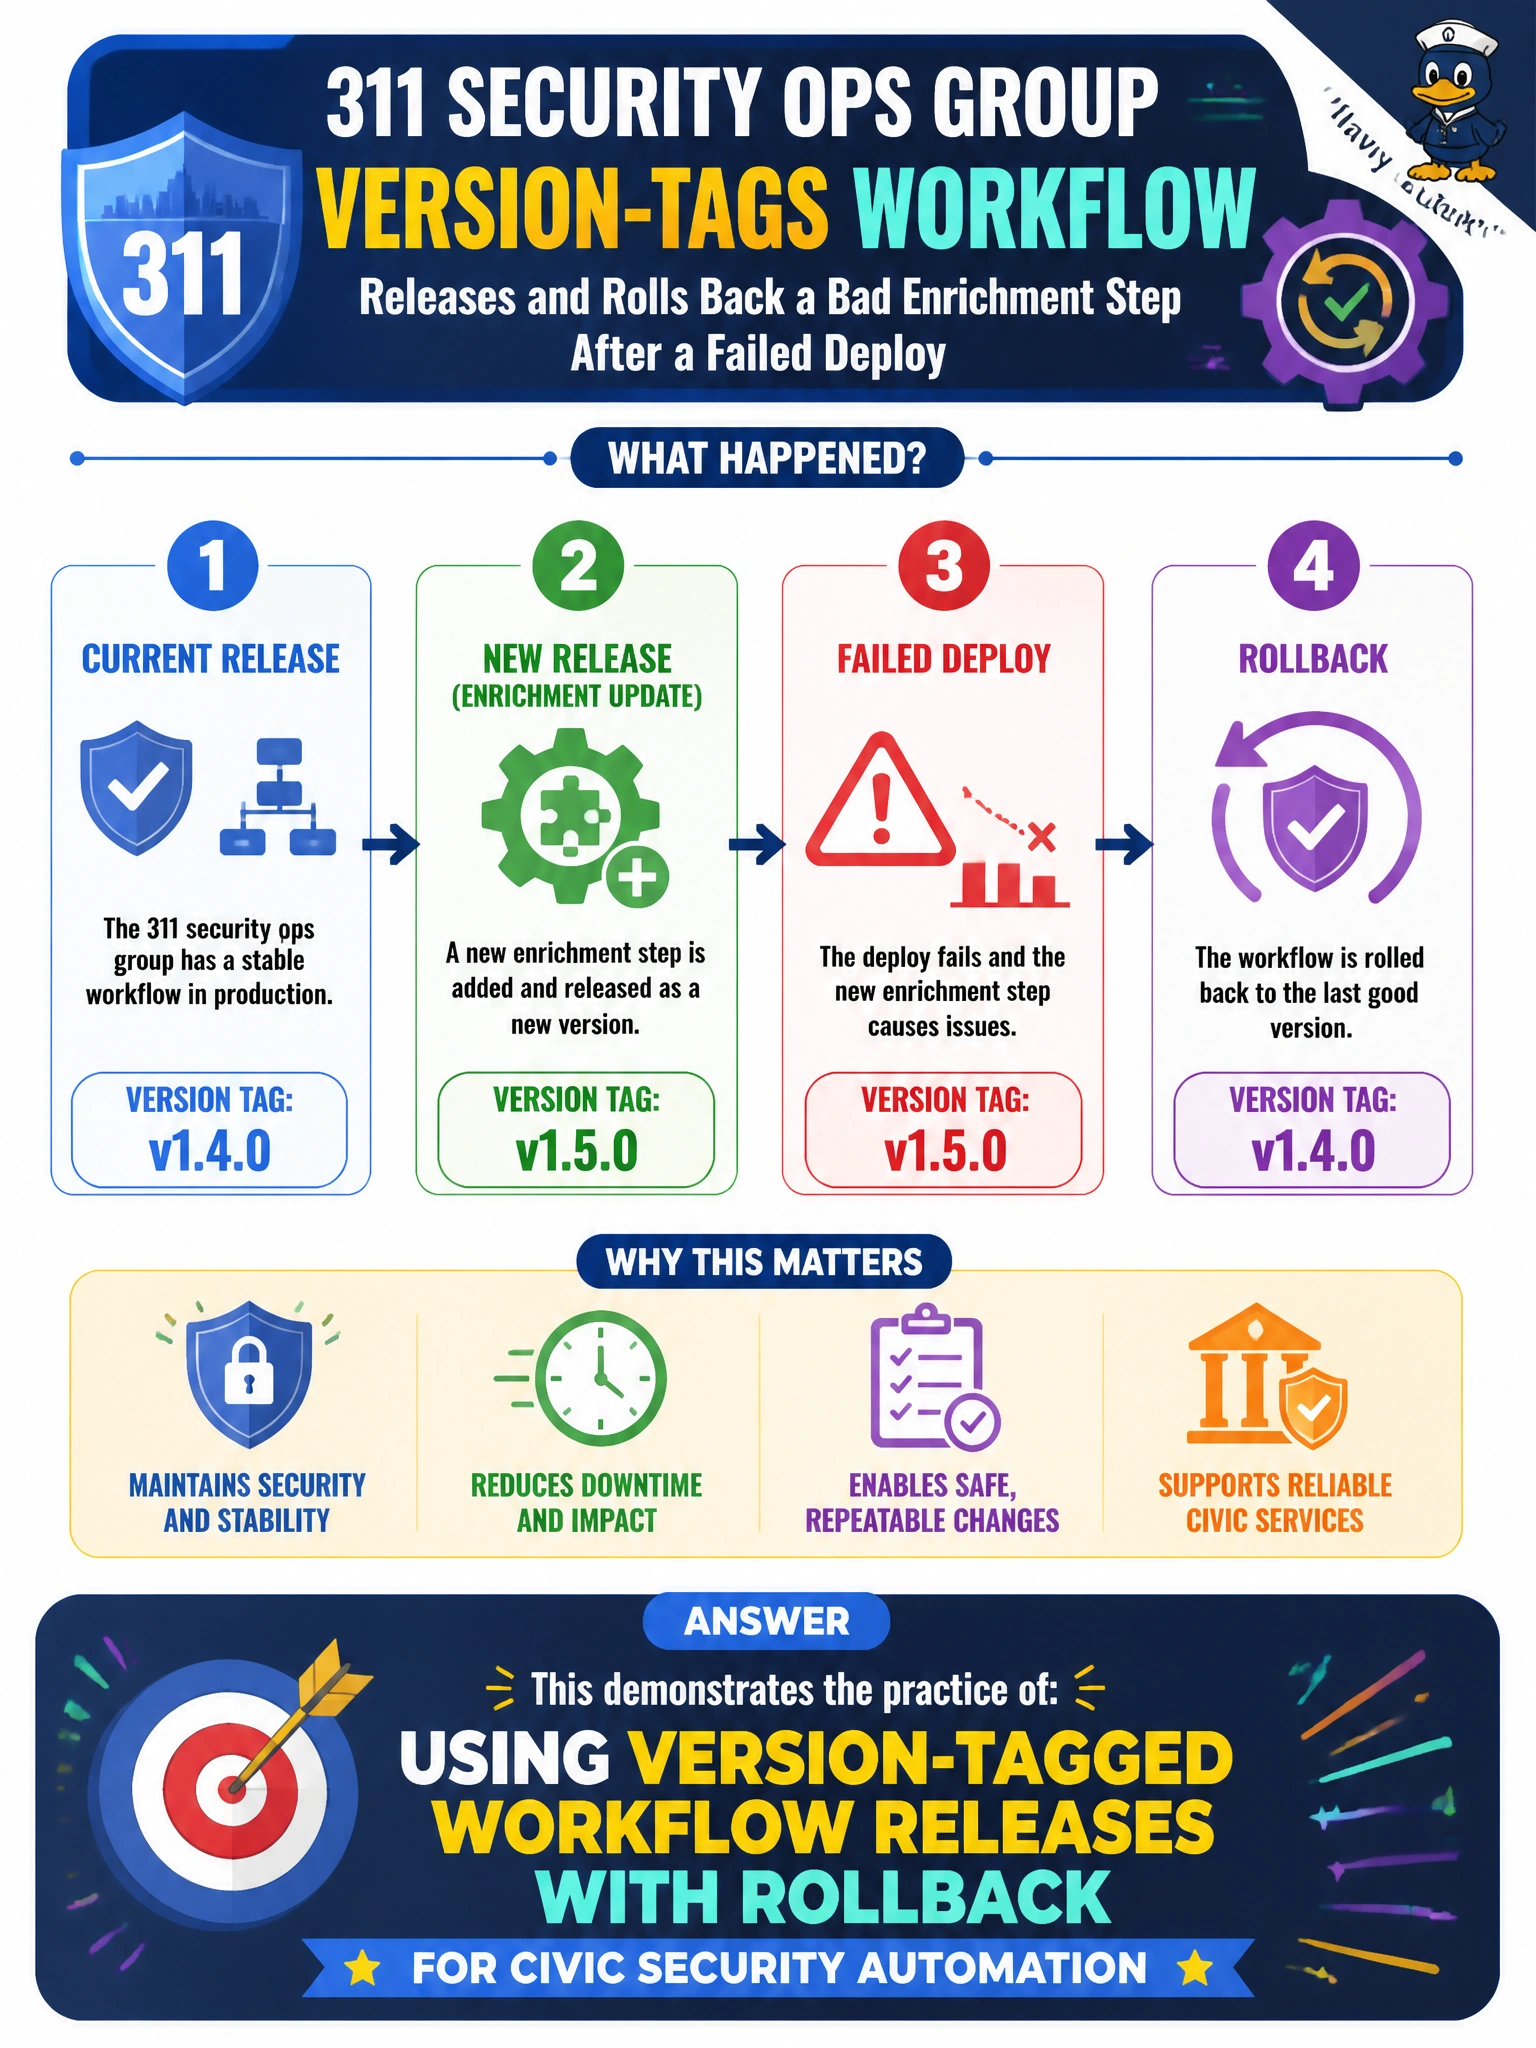
A 311 security ops group version-tags workflow releases and rolls back a bad enrichment step after a failed deploy. What practice does that demonstrate?
Select an answer to reveal the explanation.
Short Explanation
Treat playbooks like software: tag the release, and if enrichment goes sideways, roll it back. It's about automation recovery, and you'll lose that if you limit it to civic security ticket archival. 311 still needs a parachute.
Full Explanation
Using version-tagged workflow releases with rollback for civic security automation treats 311 security playbooks like software: each release is tagged, release notes capture enrichment and action changes, and a failed deploy can restore a prior known-good enrichment step. That discipline protects municipal ops from lasting automation defects when a bad enrichment transform, connector change, or action mapping reaches production. Rollback is part of the practice, not an afterthought, so service desks and security ops can recover quickly without rewriting the workflow from memory.
Using version-tagged workflow releases with rollback for civic security ticket archival fails by purpose because ticket archival moves closed tickets to long-term storage, while the version tags and rollback here restore a prior known-good enrichment step after a failed deploy for civic security automation. Using version-tagged workflow releases with rollback for civic security awareness training fails by purpose because awareness training educates staff to recognize threats, while the tags and rollback here version the workflow release itself to recover a bad enrichment step for civic security automation. Using version-tagged workflow releases with rollback for civic security metrics reporting fails by purpose because metrics reporting aggregates performance data for dashboards, while the tags and rollback here let operators restore a prior workflow version after a failed enrichment deploy for civic security automation.
Exam caveat: Questions about failed workflow deploys usually expect version tags plus rollback for civic security automation, not for civic security ticket archival as the purpose.
Operational check for 311 security ops: tag the current production workflow revision before promoting a new enrichment step, document the change in release notes, promote to a canary or limited queue first, and after a deliberate failed enrichment in staging, execute rollback to the previous tag and confirm tickets again receive correct enrichment fields.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.