
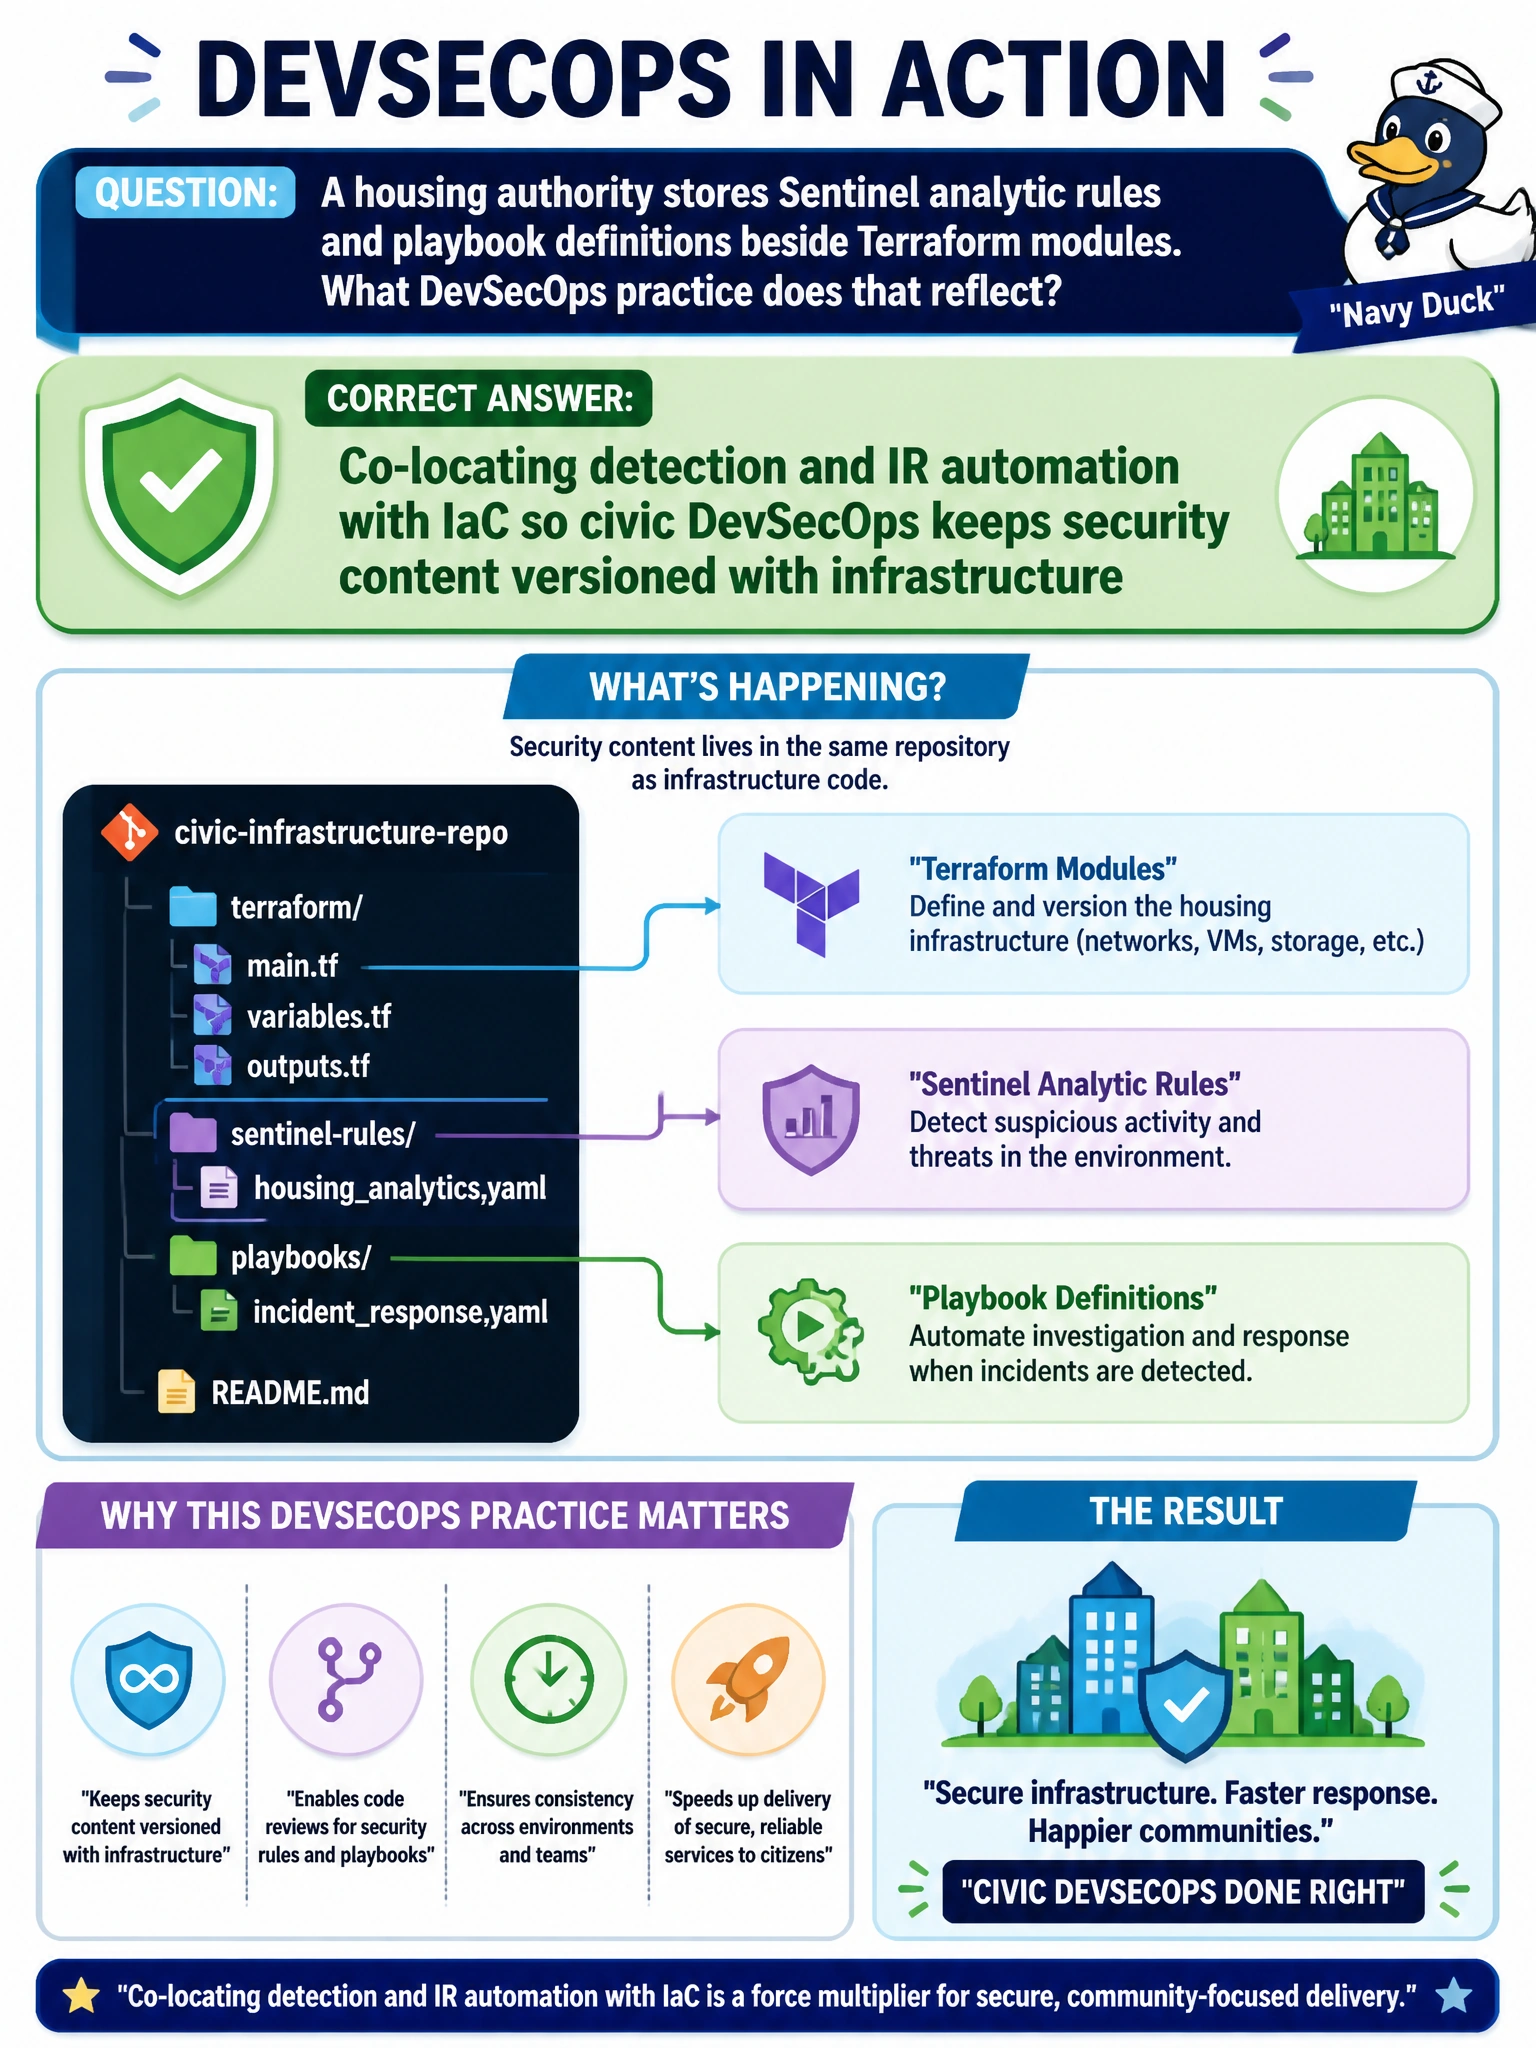
A housing authority stores Sentinel analytic rules and playbook definitions beside Terraform modules. What DevSecOps practice does that reflect?
Select an answer to reveal the explanation.
Short Explanation
Park Sentinel rules and playbooks next to Terraform modules so housing DevSecOps versions detection with the infrastructure—one repo neighborhood. Enforcing HashiCorp policy checks, drift-correcting live content, and vaulting secrets won't version detection with your infrastructure. Co-locate and ship together.
Full Explanation
Co-locating detection and IR automation with IaC so civic DevSecOps keeps security content versioned with infrastructure is what a housing authority practices by storing Sentinel analytic rules and playbook definitions beside Terraform modules. Keeping detections and response automation in the same versioned neighborhood as infrastructure enables coordinated review, rollback, and deployment pipelines. When housing systems change, related Sentinel content can change with them instead of enforcing HashiCorp Sentinel policy checks that evaluate Terraform plans rather than hold Microsoft Sentinel detection queries. Co-locating detection and IR automation with IaC so civic DevSecOps enforces HashiCorp Sentinel policy checks with infrastructure fails by concept: it confuses Microsoft Sentinel analytic rules with HashiCorp Sentinel policy-as-code that gates Terraform runs rather than versioning that detection content beside the Terraform modules it protects. Co-locating detection and IR automation with IaC so civic DevSecOps keeps security content drift-corrected with infrastructure fails by effect: mere co-location versions content alongside modules but does not continuously reconcile live Sentinel content to code the way drift correction does for provisioned resources. Co-locating detection and IR automation with IaC so civic DevSecOps keeps security secrets vaulted with infrastructure fails by concept: it describes vaulting secrets in a secret manager rather than co-locating detection and IR automation with IaC so security content is versioned with infrastructure. Exam caveat: co-location is not automatic quality—rules still need testing against civic log sources and access controls so offensive content is not world-readable in the repo. Operational check: confirm Sentinel rules and playbooks live in the same repo tree as Terraform modules, that CI can lint/deploy them, and that changes appear in pull requests alongside related infrastructure edits.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.