
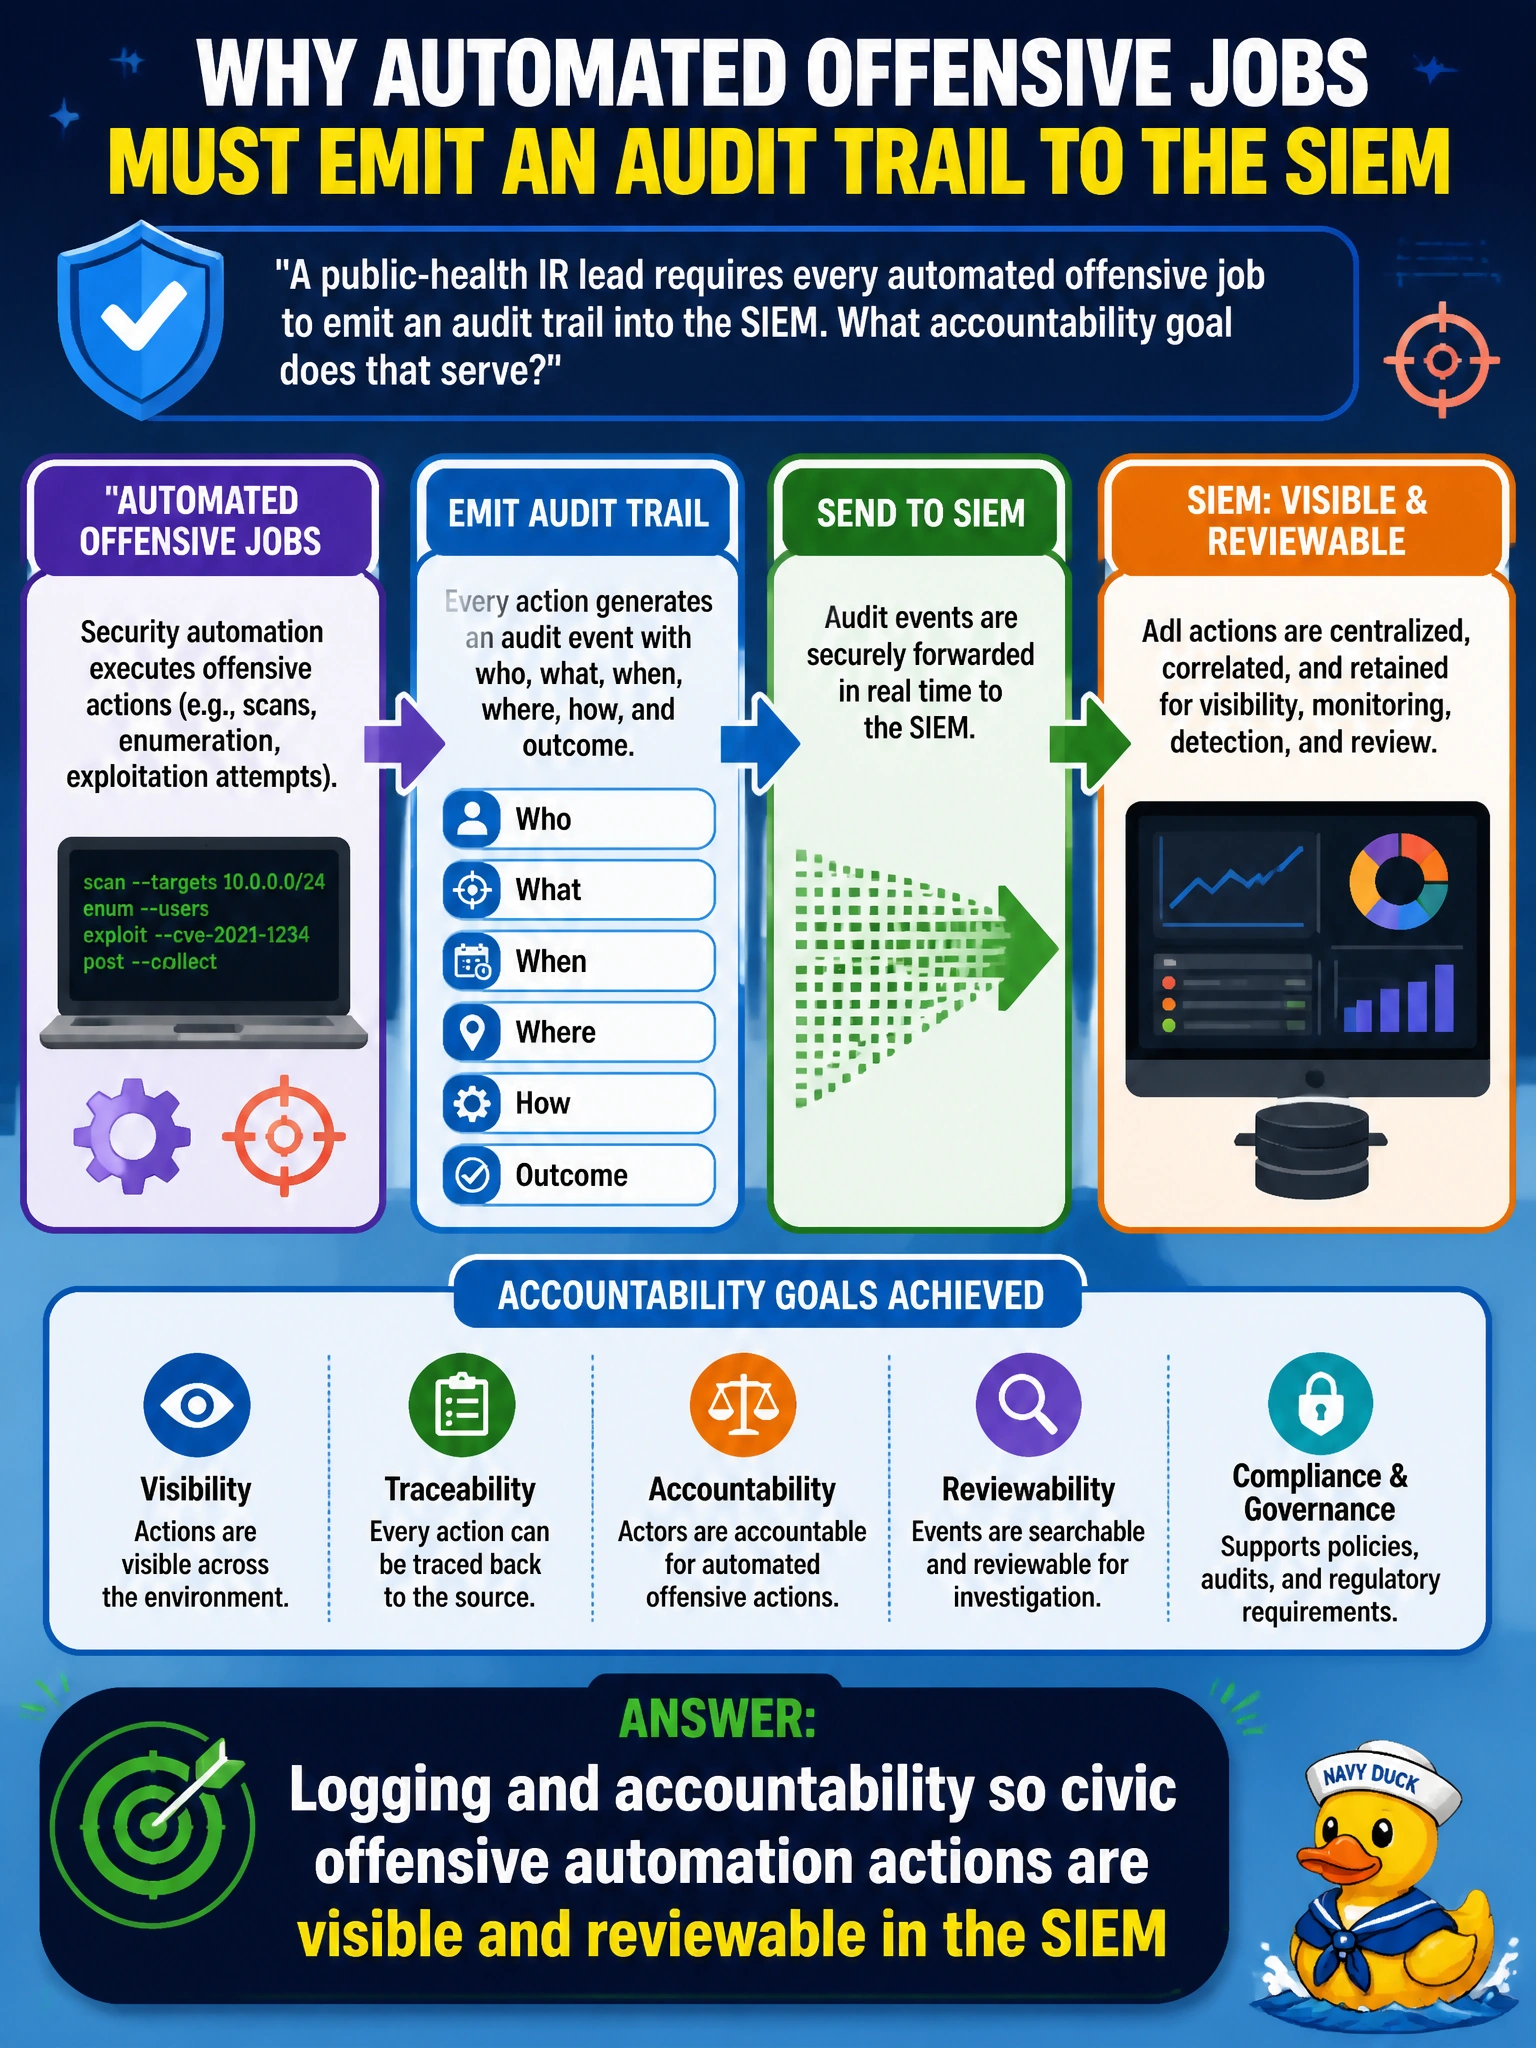
A public-health IR lead requires every automated offensive job to emit an audit trail into the SIEM. What accountability goal does that serve?
Select an answer to reveal the explanation.
Short Explanation
If the automation ran, the SIEM should show the receipt—public-health leads want that paper trail for accountability. Authorizing requests beforehand, making logs tamper-proof for compliance, or blocking actions with guardrails doesn’t give you that reviewable who-did-what trail. Log it where the SOC already looks.
Full Explanation
Public-health IR leads who require every automated offensive job to emit an audit trail into the SIEM are enforcing logging and accountability. Visible, reviewable events let defenders distinguish authorized purple activity from real adversaries, reconstruct what ran, and support compliance reviews. In municipal health environments, that trail also protects the program’s legitimacy when questions arise about who did what to which system.
The correct goal works because offensive automation without telemetry becomes indistinguishable from covert attack activity—or worse, becomes deniable. SIEM-integrated audit events create a shared source of truth for SOC and purple-team after-action work.
Maintaining approval records so civic offensive automation requests are authorized before execution in the SIEM fails because it serves pre-execution authorization, not accountability. Authorizing requests before execution does not make offensive automation actions visible and reviewable for who-did-what oversight.
Keeping tamper-evident logs so civic offensive automation actions are provable for compliance review in the SIEM fails because it serves provability for compliance, not visibility and reviewability—it does not create reviewable records of automated offensive job actions.
Enforcing automated guardrails so civic offensive automation actions are blocked and contained within the SIEM fails because it serves prevention and containment, not accountability—it does not provide a reviewable audit trail of automated offensive job actions.
Exam caveat: Accountability for civic offensive automation means SIEM-visible audit trails—not pre-execution authorization, tamper-evident provability for compliance, or automated blocking and containment.
Operational check: Emit structured start/stop/target/technique events to the SIEM, alert on jobs missing heartbeats, and retain logs per municipal policy for reconstruction.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.