
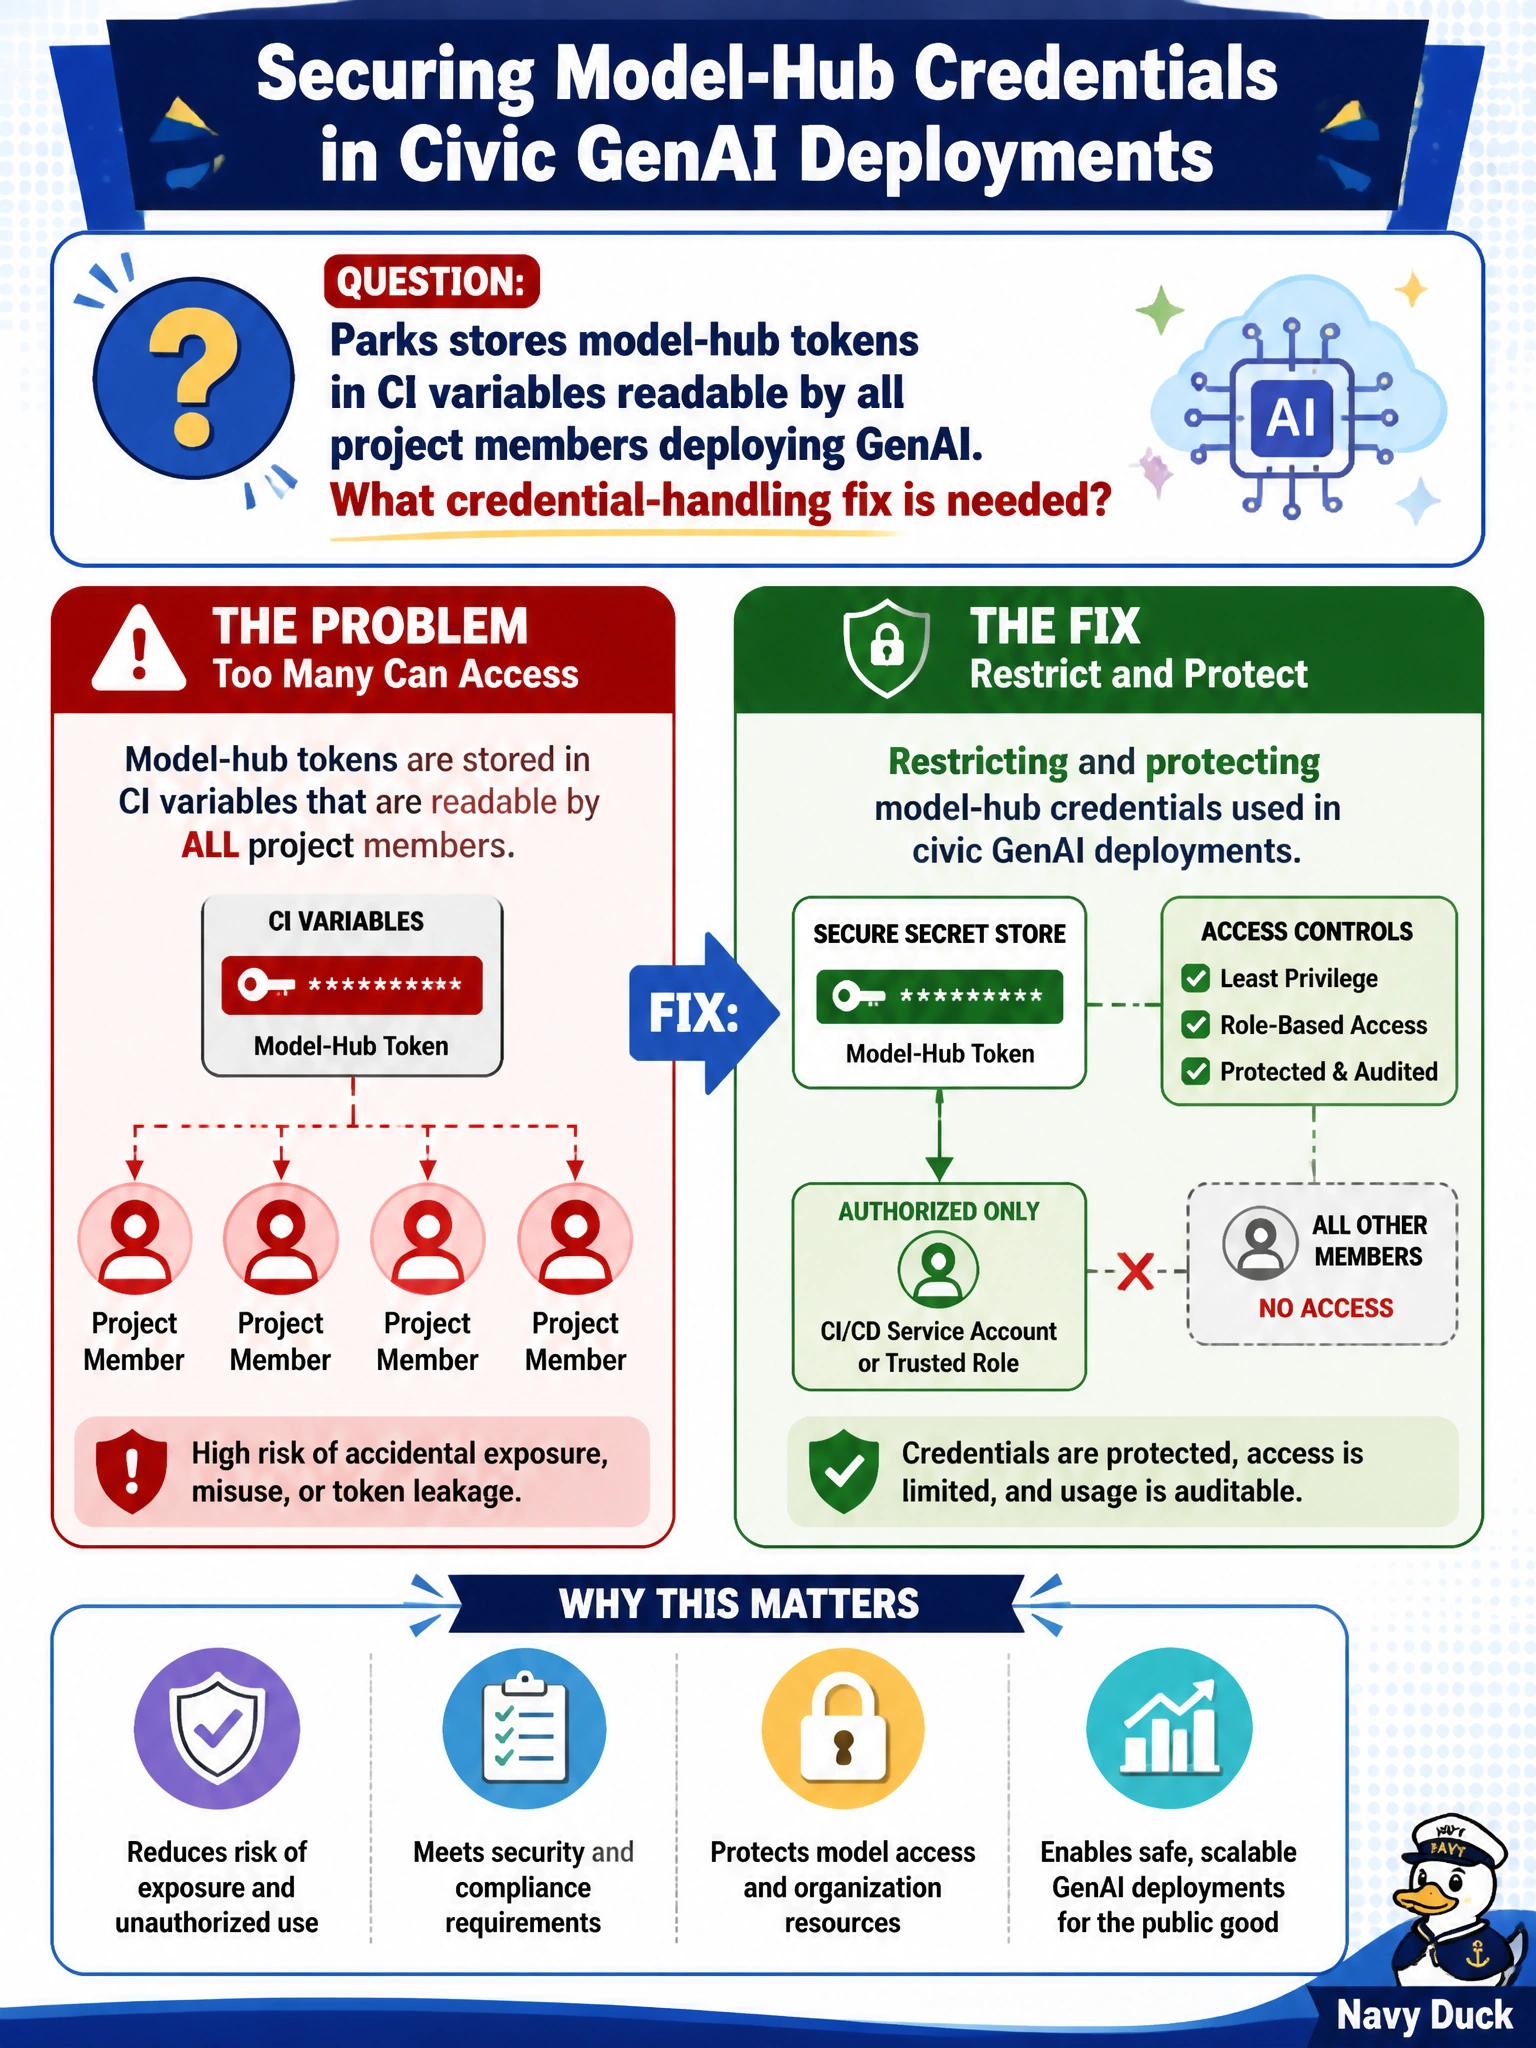
Parks stores model-hub tokens in CI variables readable by all project members deploying GenAI. What credential-handling fix is needed?
Select an answer to reveal the explanation.
Short Explanation
A hub token readable by the whole project is a shared master key for pulling models. Lock it down and protect it. Public git, yearly-only rotation, and baking tokens into image layers are how leaks happen.
Full Explanation
Parks storing model-hub tokens in CI variables readable by all project members creates shared, over-broad credentials for pulling GenAI artifacts into civic deployments. The needed fix is restricting and protecting model-hub credentials used in municipal GenAI pipelines: least-privilege tokens, masked secret CI variables, limited role access to who can read them, short lifetimes, and preferably OIDC federation to the hub instead of long-lived personal access tokens shared across the team.
Committing tokens into a public parks Git mirror maximizes exposure under a false auditability story and places secrets in immutable history. Rotating only when park season ends leaves credentials valid for months after potential leaks or staff changes. Embedding the same hub token in every container image layer bakes secrets into distributable artifacts recoverable from registries, caches, and exported layers.
Exam caveat: read-only scoped tokens still need access control—scope reduction is necessary but not sufficient if every project member can still view and exfiltrate them from CI. Operational check: inventory who can view CI secrets for parks GenAI pipelines, rotate any exposed hub tokens, switch to short-lived federation where the hub supports it, scan images and git history for embedded credentials, and enforce secret-scanning gates on merge.