
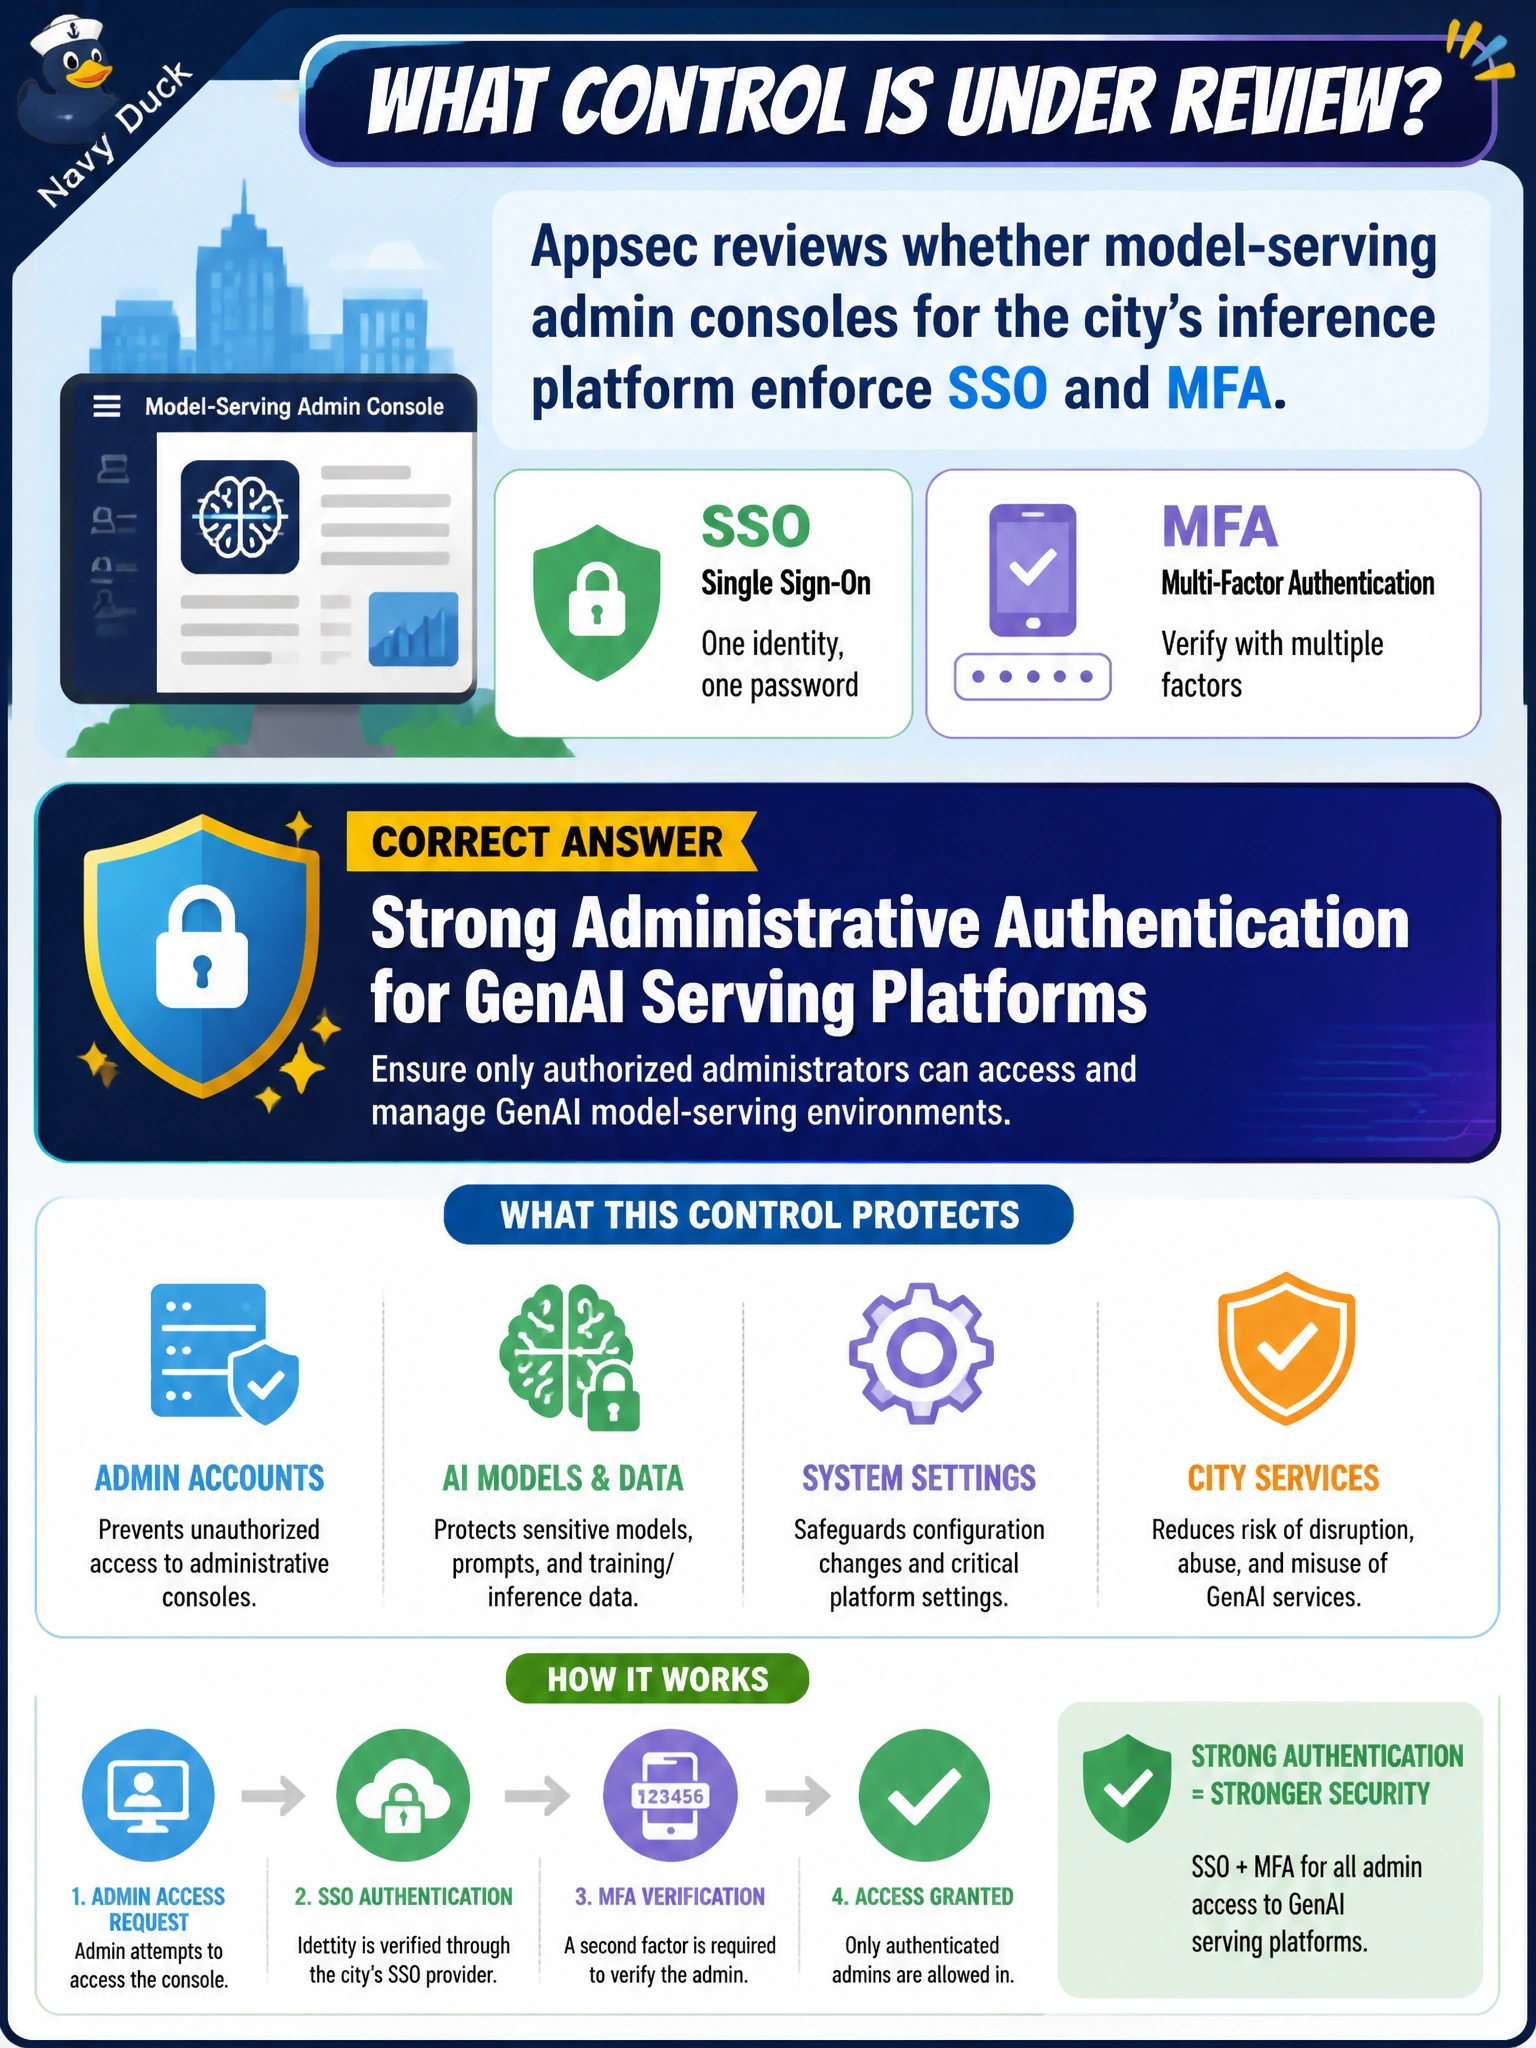
Appsec reviews whether model-serving admin consoles for the city’s inference platform enforce SSO and MFA. What control is under review?
Select an answer to reveal the explanation.
Short Explanation
Admin consoles for model serving are the master switchboard — SSO plus MFA keep random hands off the dials. Branding themes, sticky-note passwords, and longer context windows are not admin auth.
Full Explanation
Appsec reviewing whether model-serving admin consoles for the city’s inference platform enforce SSO and MFA is assessing strong administrative authentication for GenAI serving platforms. Those consoles can change models, scale endpoints, alter routing, or expose configuration secrets; they are high-value municipal infrastructure control planes and need enterprise identity, MFA, and preferably phishing-resistant factors—not shared local passwords left on desks.
Console theme branding is unrelated to authentication strength and does not stop unauthorized admin sessions. Sharing a single break-glass password on sticky notes creates standing shared credentials, destroys individual accountability, and invites reuse outside approved emergencies. Replacing MFA with longer model context windows confuses an application generation parameter with human administrative authentication for the serving control plane.
Exam caveat: SSO and MFA on the console do not replace network restriction, privileged-access workstations, or change auditing—but without strong admin auth those other controls are easier to bypass. Operational check: attempt console login with SSO-only and MFA-challenged paths, disable local password sprawl, require step-up for destructive GenAI platform actions, and review admin session logs for configuration changes on municipal inference services.