
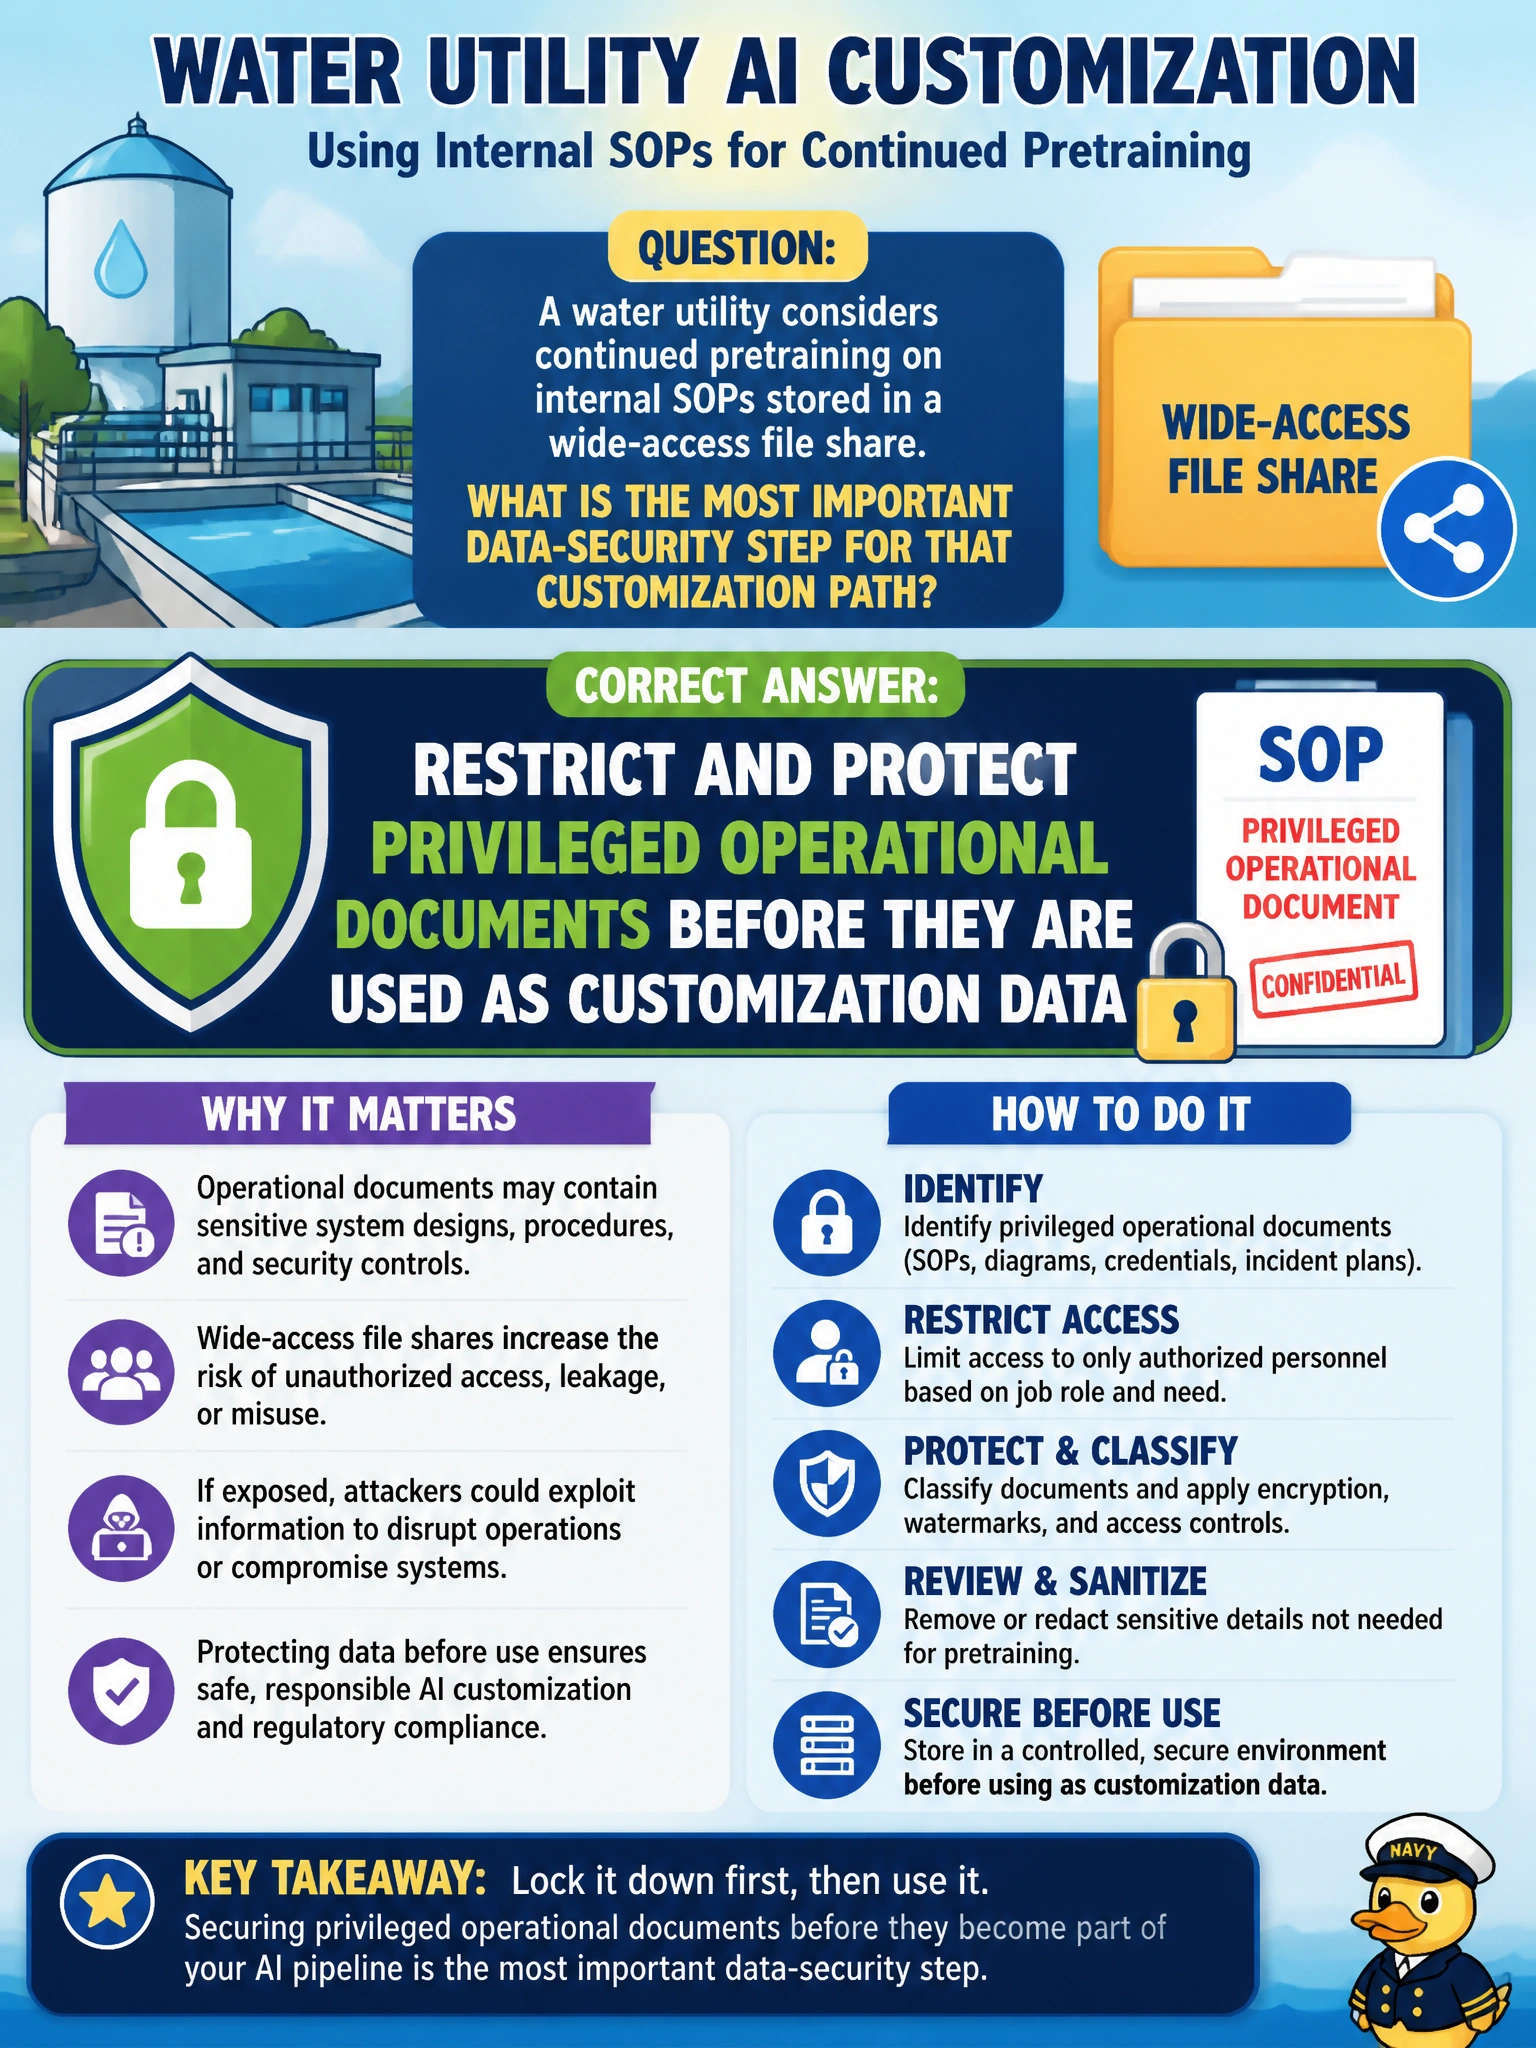
A water utility considers continued pretraining on internal SOPs stored in a wide-access file share. What is the most important data-security step for that customization path?
Select an answer to reveal the explanation.
Short Explanation
Utility SOPs are the playbook for keeping water flowing—not a wide-open cafeteria tray. If continued pretraining drinks from that share, lock the docs down first or you bake ops secrets into the model.
Full Explanation
Continued pretraining on water-utility SOPs stored in a wide-access file share risks baking privileged operational procedures—valve sequences, chemical handling, contingency playbooks—into model weights accessible to a broader audience than the original share intended. The most important data-security step is to restrict and protect those privileged operational documents before they become customization data: tighten ACLs, segregate a curated training extract, and treat the corpus as sensitive critical-infrastructure knowledge.
Granting anonymous internet read access for contractor labeling massively expands disclosure risk for utility operations. Deleting the base model license file to avoid contractual review creates compliance and supply-chain governance problems and does nothing to secure SOP content. Pasting full SOP text into public chat threads for crowdsourcing is active leakage of operational detail.
Exam caveat: Continued pretraining and fine-tuning inherit the sensitivity of their corpora. Wide-access municipal file shares are a weak source of truth for GenAI customization of critical infrastructure content. Licensing hygiene matters, but it is not a substitute for protecting operational documents used as training data.
Operational check: Inventory SOPs marked for pretraining, move approved excerpts into a locked training dataset with least-privilege service identities, remove or redact credentials and site-specific sensitive details not needed for the model objective, enable access logs, and prohibit public-chat pasting. After training, probe the candidate model for verbatim SOP leakage and restrict which internal apps may call the customized checkpoint.