
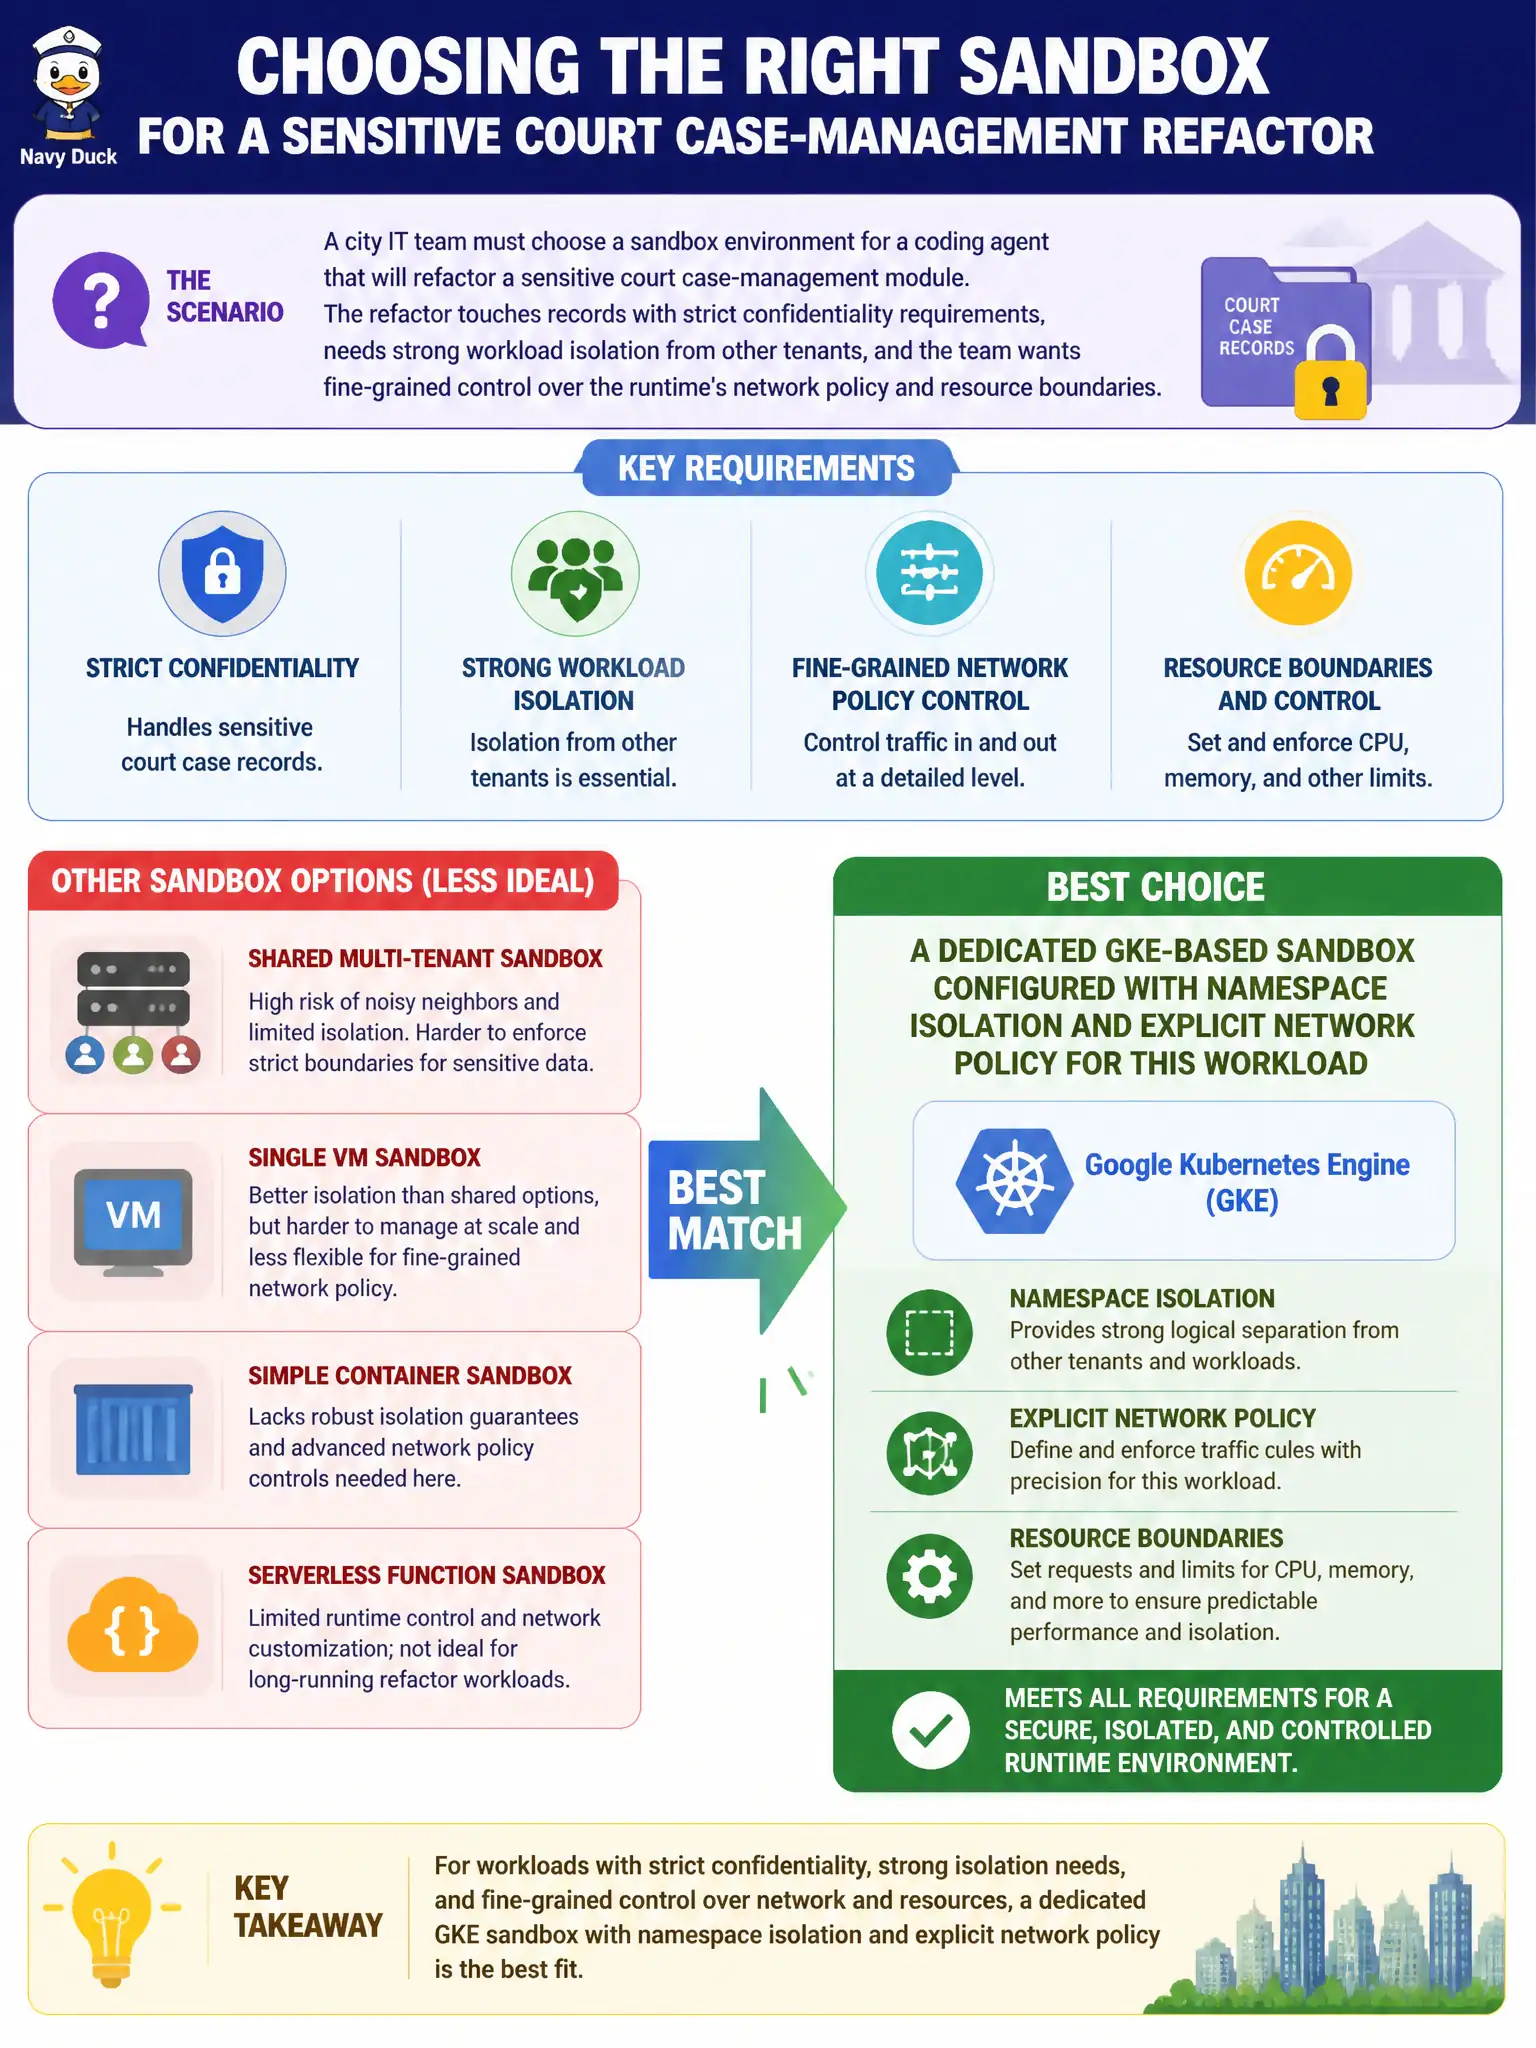
A city IT team must choose a sandbox environment for a coding agent that will refactor a sensitive court case-management module. The refactor touches records with strict confidentiality requirements, needs strong workload isolation from other tenants, and the team wants fine-grained control over the runtime's network policy and resource boundaries. Which sandbox choice best matches these requirements?
Select an answer to reveal the explanation.
Short Explanation
Think of sandbox choice like picking a room for a confidential meeting: a shared open office won't cut it when you need locked doors and controlled access. A dedicated GKE-based sandbox lets you set namespace isolation and network policy specifically for this workload, which is exactly the control a sensitive court-records refactor calls for. Match the isolation level to the sensitivity of the data.
Full Explanation
Coding agents can run in secure sandboxes, and GKE is named specifically because it supports fine-grained isolation primitives: namespaces, network policies, and resource boundaries that can be scoped tightly to a single sensitive workload. For a court case-management refactor involving confidential records, that level of control over network egress and tenant separation is the deciding factor, not just general code-editing convenience. A shared Cloud Workstations environment used across multiple teams fails the isolation requirement because it mixes this sensitive workload's runtime with unrelated development activity, widening the exposure surface. Running the agent with no dedicated sandbox at all removes the containment boundary entirely, leaving the refactor's execution context indistinguishable from the agent's general session, which is the opposite of what a confidentiality-sensitive task needs. A Cloud Workstations environment sized for lightweight prototyping addresses developer convenience for quick iteration, not the workload-isolation and network-policy granularity the task specifically requires, so it is the right tool applied to the wrong job. As an operational check, confirm the sandbox's network policy explicitly denies egress the refactor doesn't need and that the namespace is not shared with any other active workload before the agent begins.