
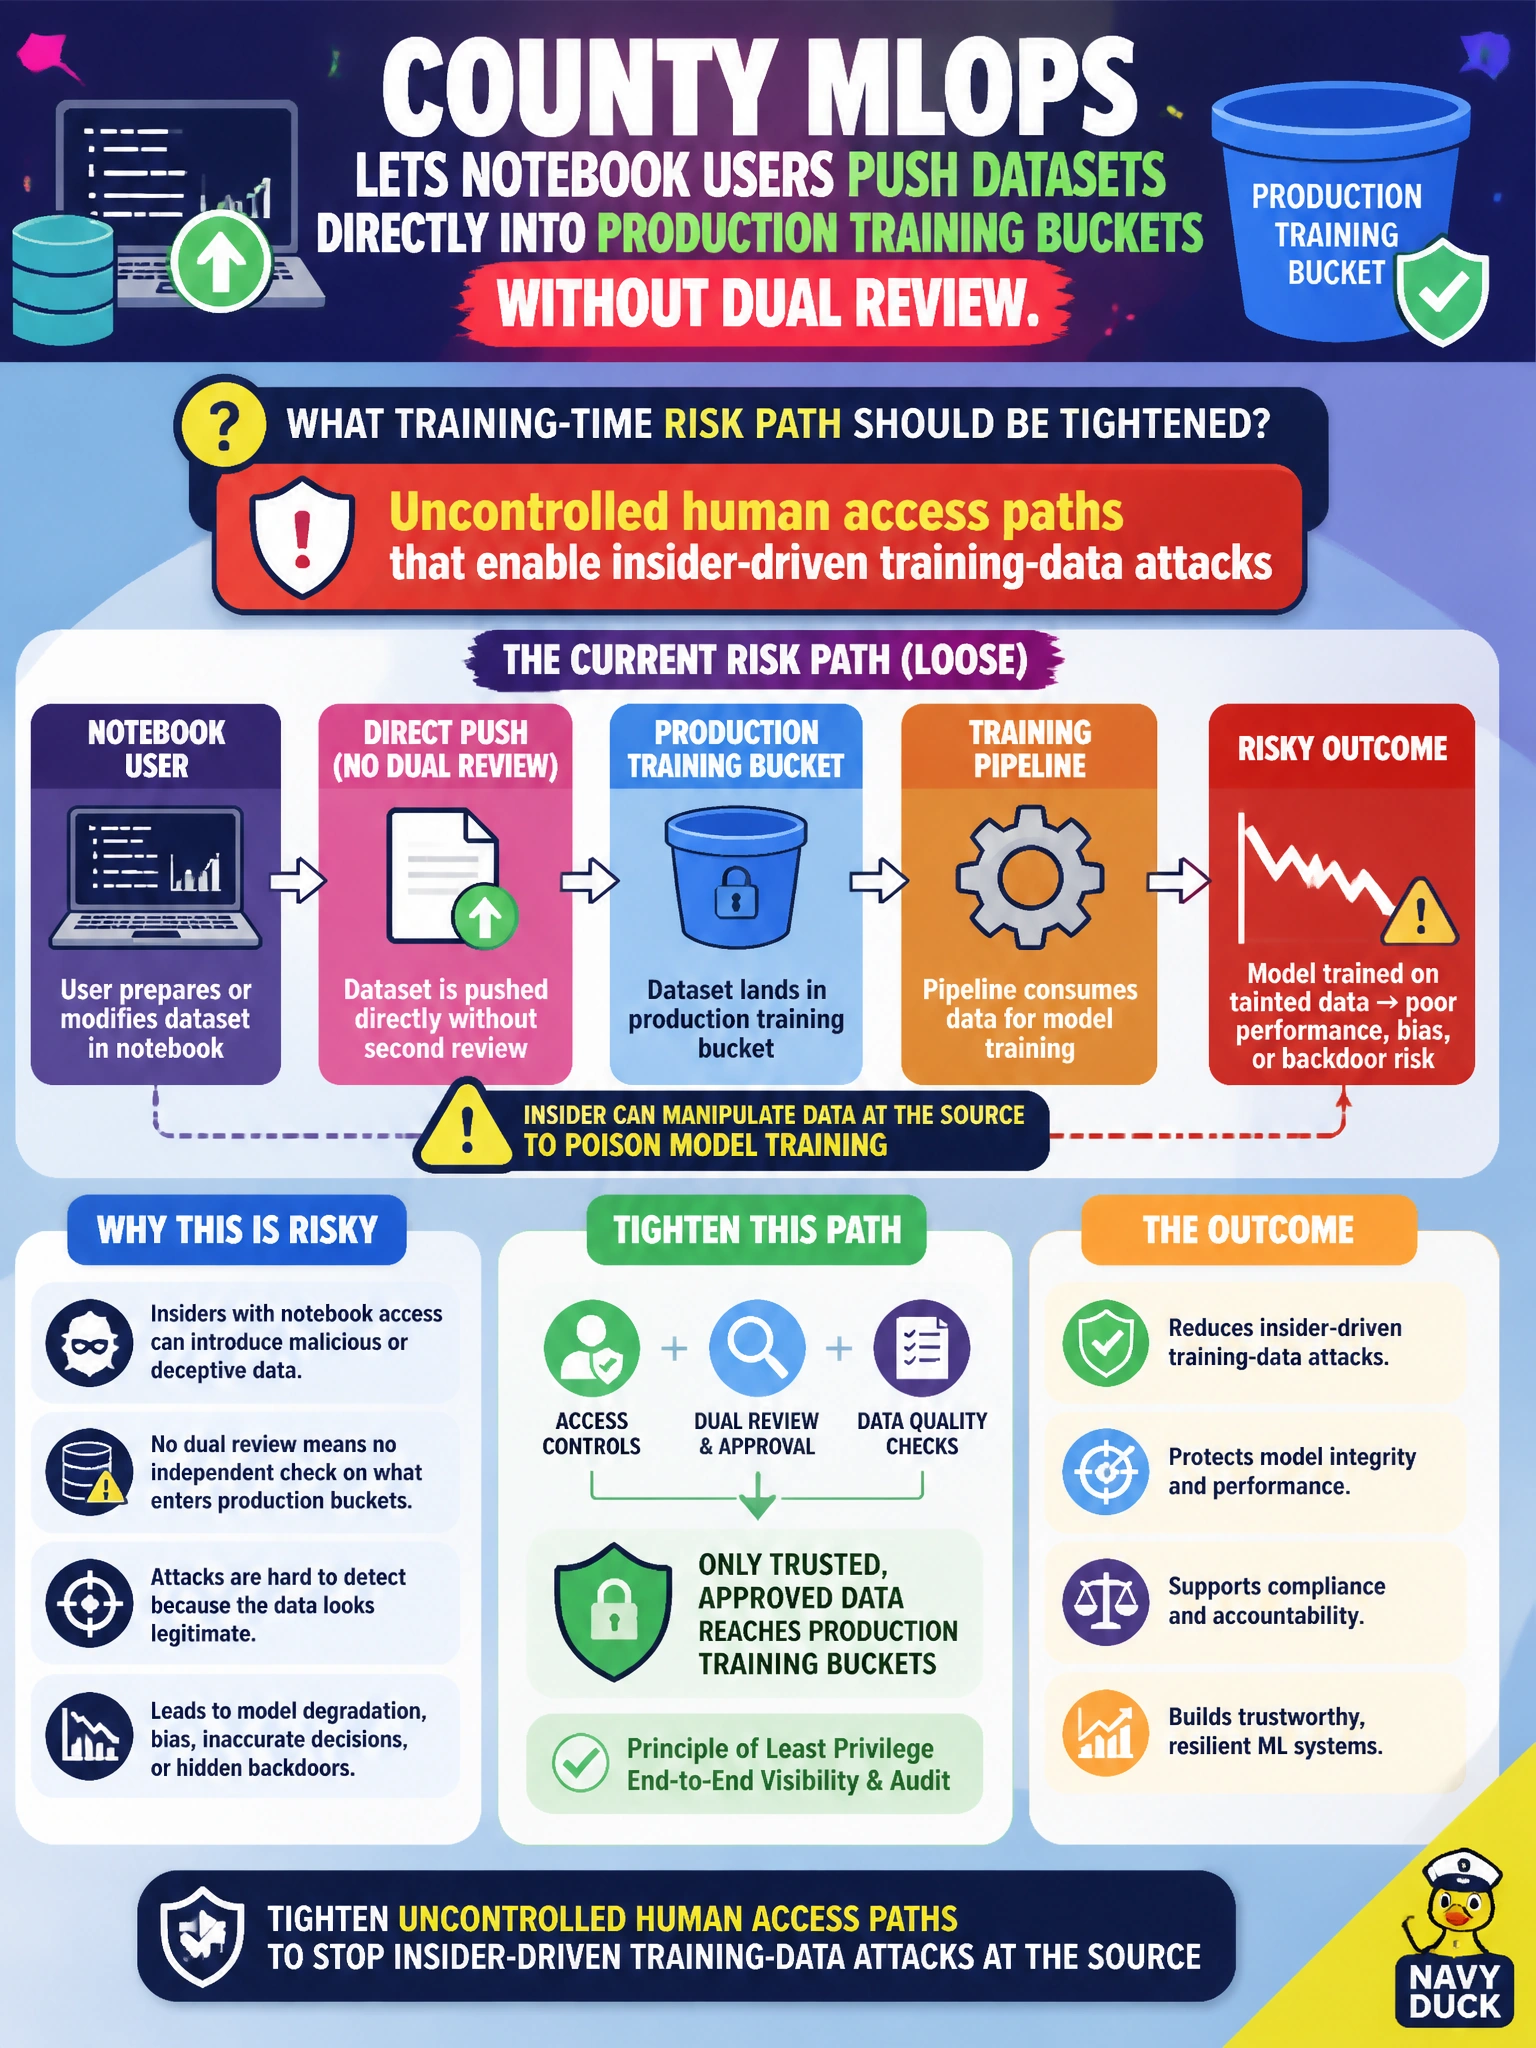
County MLOps lets notebook users push datasets directly into production training buckets without dual review. What training-time risk path should be tightened?
Select an answer to reveal the explanation.
Short Explanation
Anyone who can dump files into the training bucket is a poison path—put dual control on that door.
Full Explanation
County MLOps that lets notebook users push datasets directly into production training buckets without dual review creates uncontrolled human access paths that enable insider-driven training-data attacks. Compromised accounts or malicious insiders can drop poisoned files straight into the corpus that trains civic models. Tightening means staging buckets, mandatory dual control or peer review, identity-aware write policies, immutable audit logs, and promotion jobs that only pull approved artifacts—not relying on notebook culture alone.
Unmonitored external dataset ingestion is an upstream supply-chain issue, not the direct insider write path created when notebook users push files into prod training buckets. Permissive service account scopes concern automated pipeline identities, not the interactive human notebook roles that can drop poisoned files directly into the corpus. Delayed model artifact signing weakens verification of promoted training outputs, but it does not open the human write path that lets notebook users poison training data before training occurs. These options fail because they address external ingestion, service-account automation, or output signing instead of constraining human write paths into training data.
Exam caveat: dual review slows experimentation; apply stricter gates to production training paths while allowing sandboxes that cannot reach prod buckets. Insider risk includes accidental mis-drops as well as malice. Distinguish notebook compute isolation from data-plane promotion controls—both matter.
Operational check: remove direct IAM write from prod training prefixes for interactive notebook roles; require a reviewed promotion ticket that copies from staging after dual approval; alert on any direct put to prod training. Red-team an insider drop in staging to confirm detection. If a single notebook token can still overwrite prod training data, the training-time risk path remains open.