
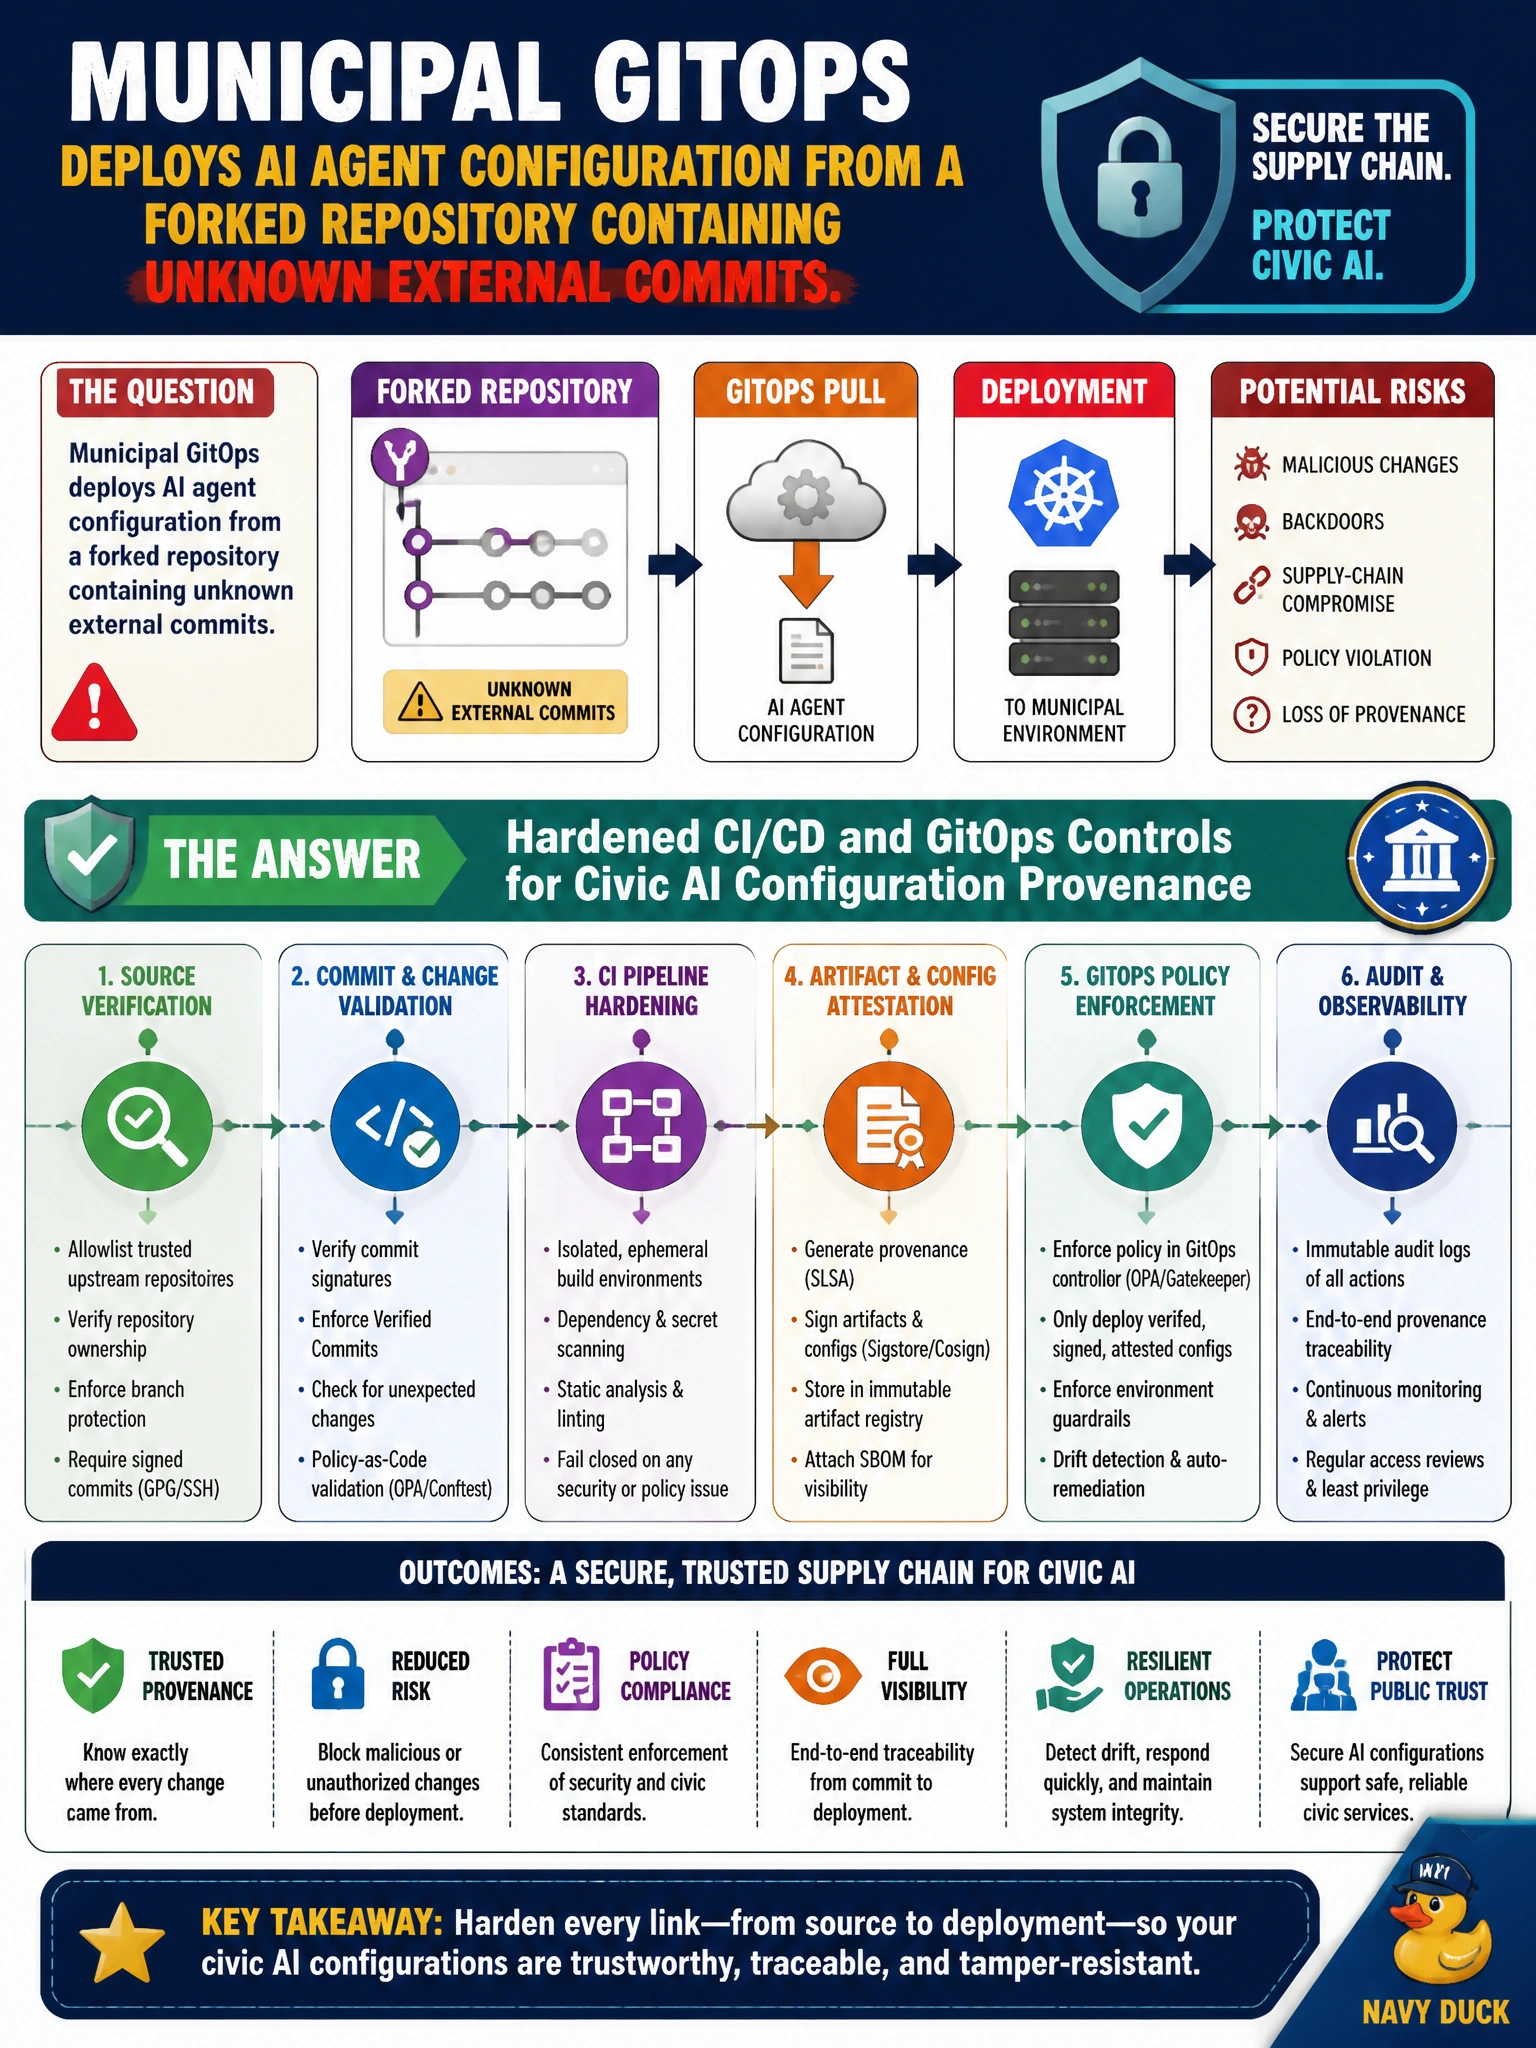
Municipal GitOps deploys AI agent configuration from a forked repository containing unknown external commits. What supply-chain hardening is needed?
Select an answer to reveal the explanation.
Short Explanation
Deploying AI config from mirrored public base container images for civic agent runtime deployment is like wiring the building from a stranger's blueprint. Provenance the repo. Rotated encrypted vault secrets for municipal agent pipeline authentication and enabled runtime observability dashboards for civic agent behavior monitoring don't fix the config source—you need provenance.
Full Explanation
Municipal GitOps that deploys AI agent configuration from a forked repository containing unknown external commits needs hardened CI/CD and provenance controls. Configuration-as-code for civic agents must come from reviewed, trusted sources with protected branches, required reviews, signed commits or verified merge policies, and blocked deploys from untrusted forks. Unknown external commits are CI/CD supply-chain risk that can alter tool permissions, prompts, or endpoints silently. README cosmetics do not establish provenance.
Mirrored public base container images for civic agent runtime deployment, rotated encrypted vault secrets for municipal agent pipeline authentication, and enabled runtime observability dashboards for civic agent behavior monitoring each address unrelated operational areas — they are symptoms of missing CI/CD and GitOps controls, not the comprehensive hardening recommendation itself.
Exam caveat: mirroring public base container images for civic agent runtime deployment without verifying the configuration provenance still fails if external contributors can push—protect the deployment source of truth, not just the mirrored runtime image. Operational check: point GitOps at the city’s protected canonical repo, require signed commits and CODEOWNERS review for agent config paths, deny deploys referencing mirrored container image digests, and reconcile live agent config hashes to the last approved main-branch commit.