
Staff SSID design for city hall requires per-user identity rather than a shared PSK. Which AP security mode should the technician select?
Select an answer to reveal the explanation.
Short Explanation
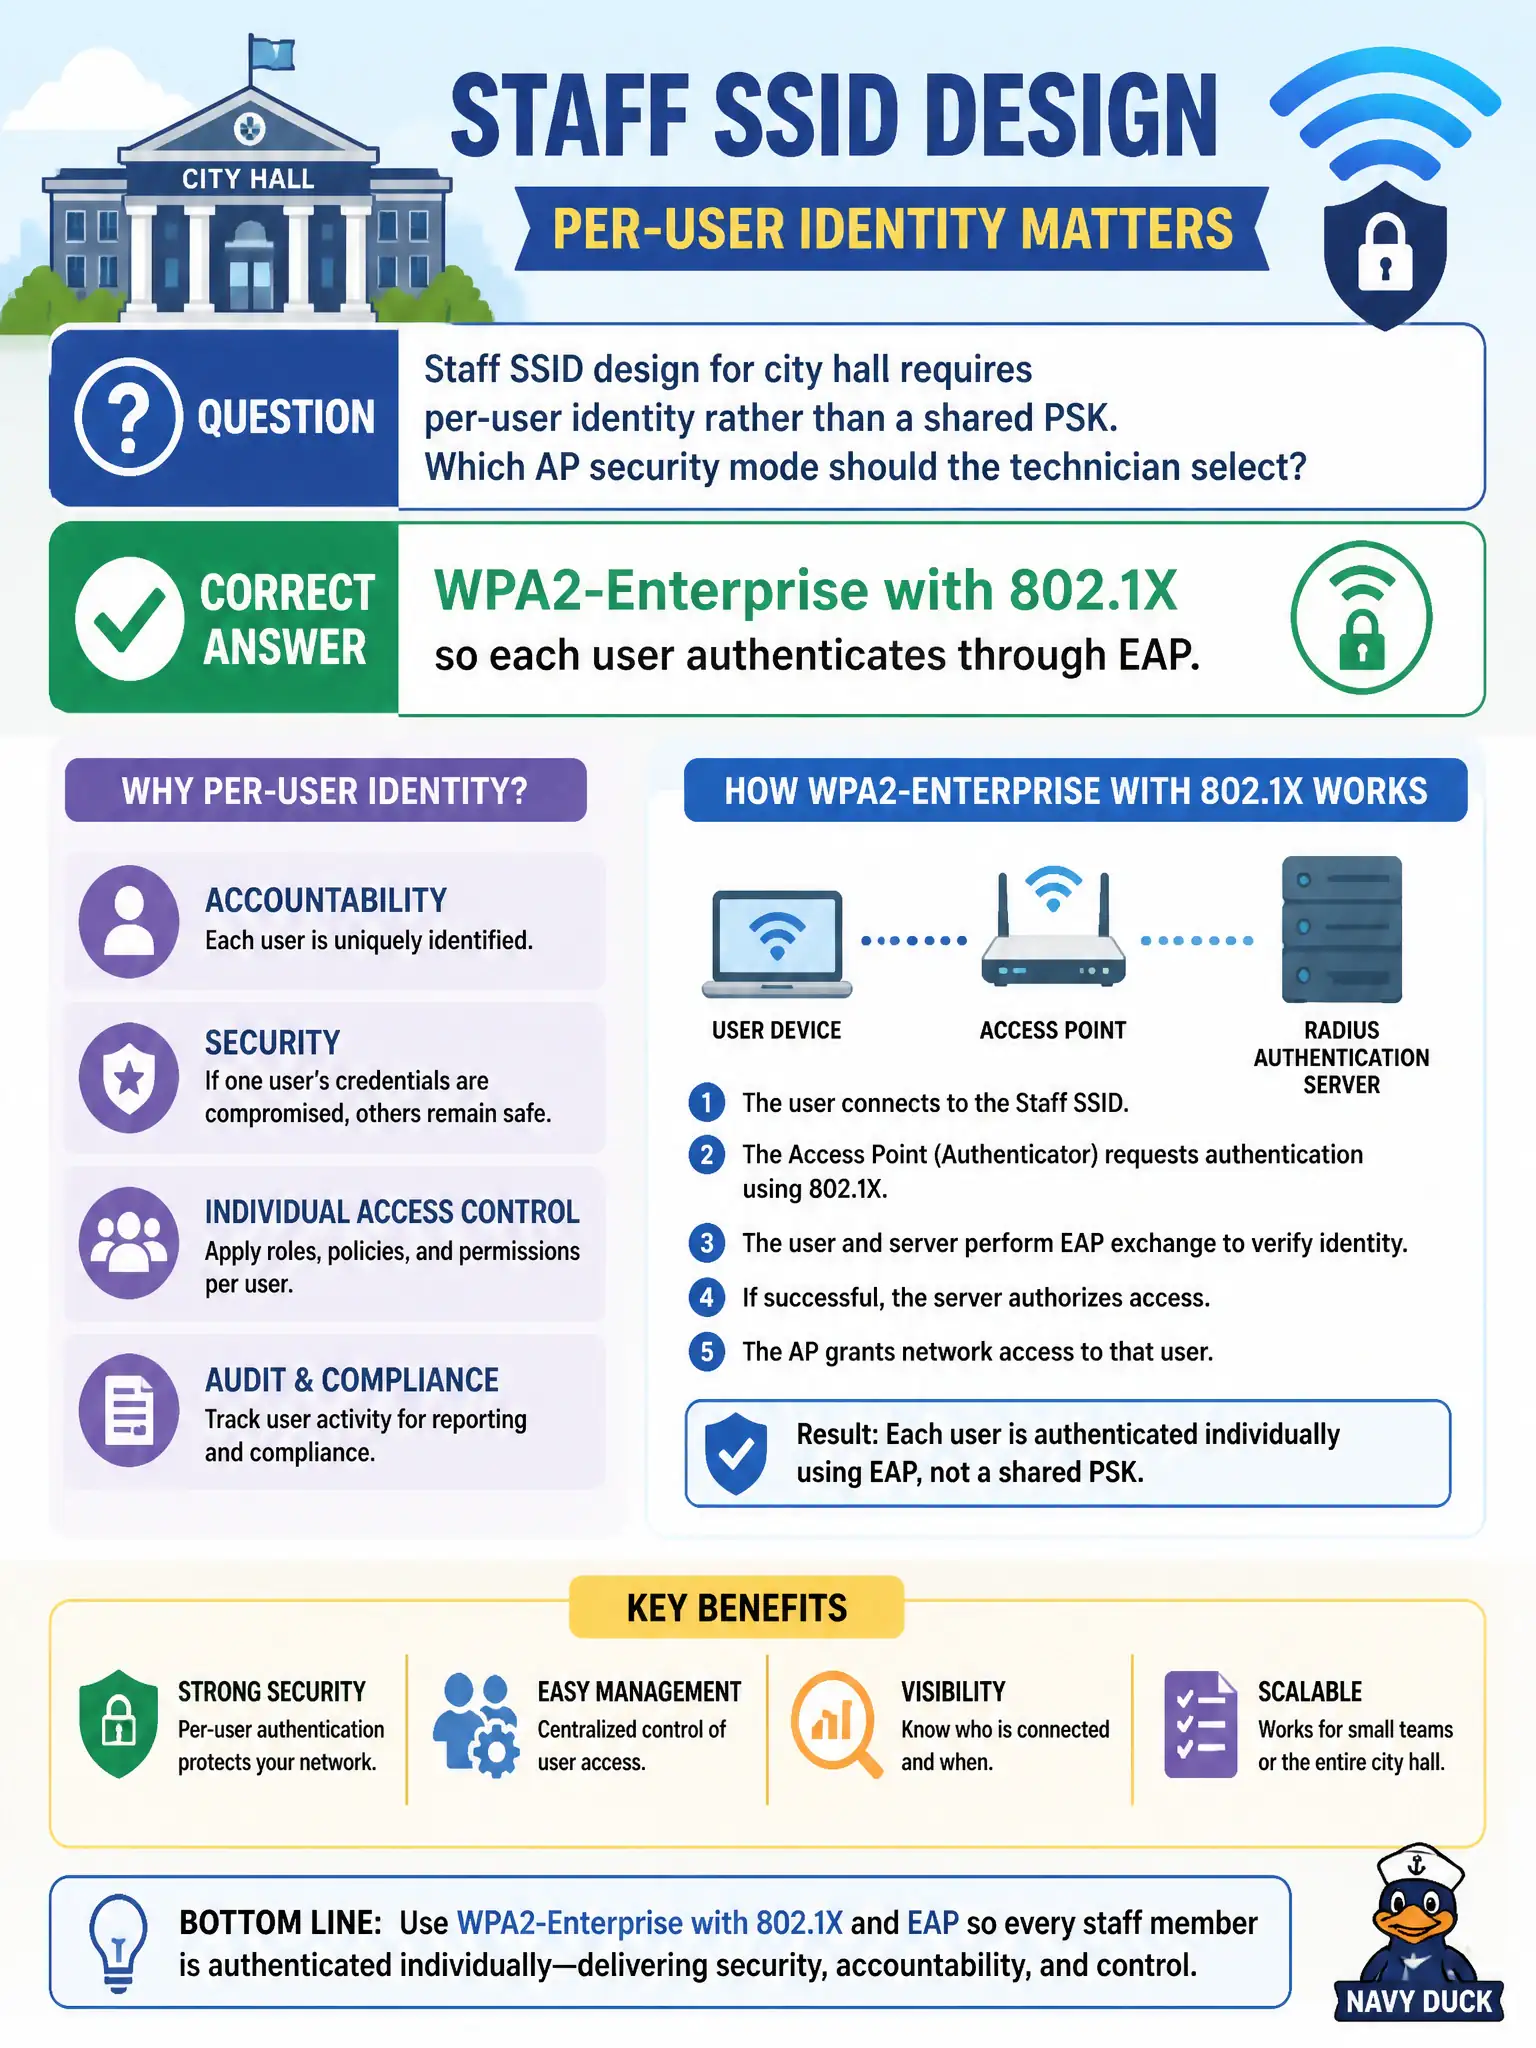
Shared passwords are hallway sticky notes. When staff need individual identity, pick WPA2-Enterprise with 802.1X/EAP so each login is personal—not a break-room PSK.
Full Explanation
Staff SSID designs for city hall that require per-user identity rather than a shared PSK call for WPA2-Enterprise with 802.1X so each user authenticates through EAP. Enterprise mode enables unique credentials, revocation, and accountability appropriate to municipal staff networks. Shared passphrases cannot meet that identity requirement.
WPA2-Personal with one departmental passphrase posted in the break room is shared-secret Personal mode, not per-user Enterprise. Open System with a daily rotating PSK emailed to all employees remains a shared secret with weak operational security. WEP with per-user static keys in a spreadsheet is both deprecated and unmanageable.
Exam caveat: per-user identity on WLAN → 802.1X/EAP Enterprise, not Personal PSKs or WEP key spreadsheets.
Operational check: select WPA2-Enterprise (or WPA3-Enterprise if designed) with 802.1X/EAP, validate a named test user, confirm revocation works when a staff account is disabled, and document RADIUS dependency for city hall ops. Municipal technicians document the verified setting in the as-built packet so the next shift inherits a known-good civic configuration rather than tribal knowledge. Municipal technicians document the verified setting in the as-built packet so the next shift inherits a known-good civic configuration rather than tribal knowledge.