
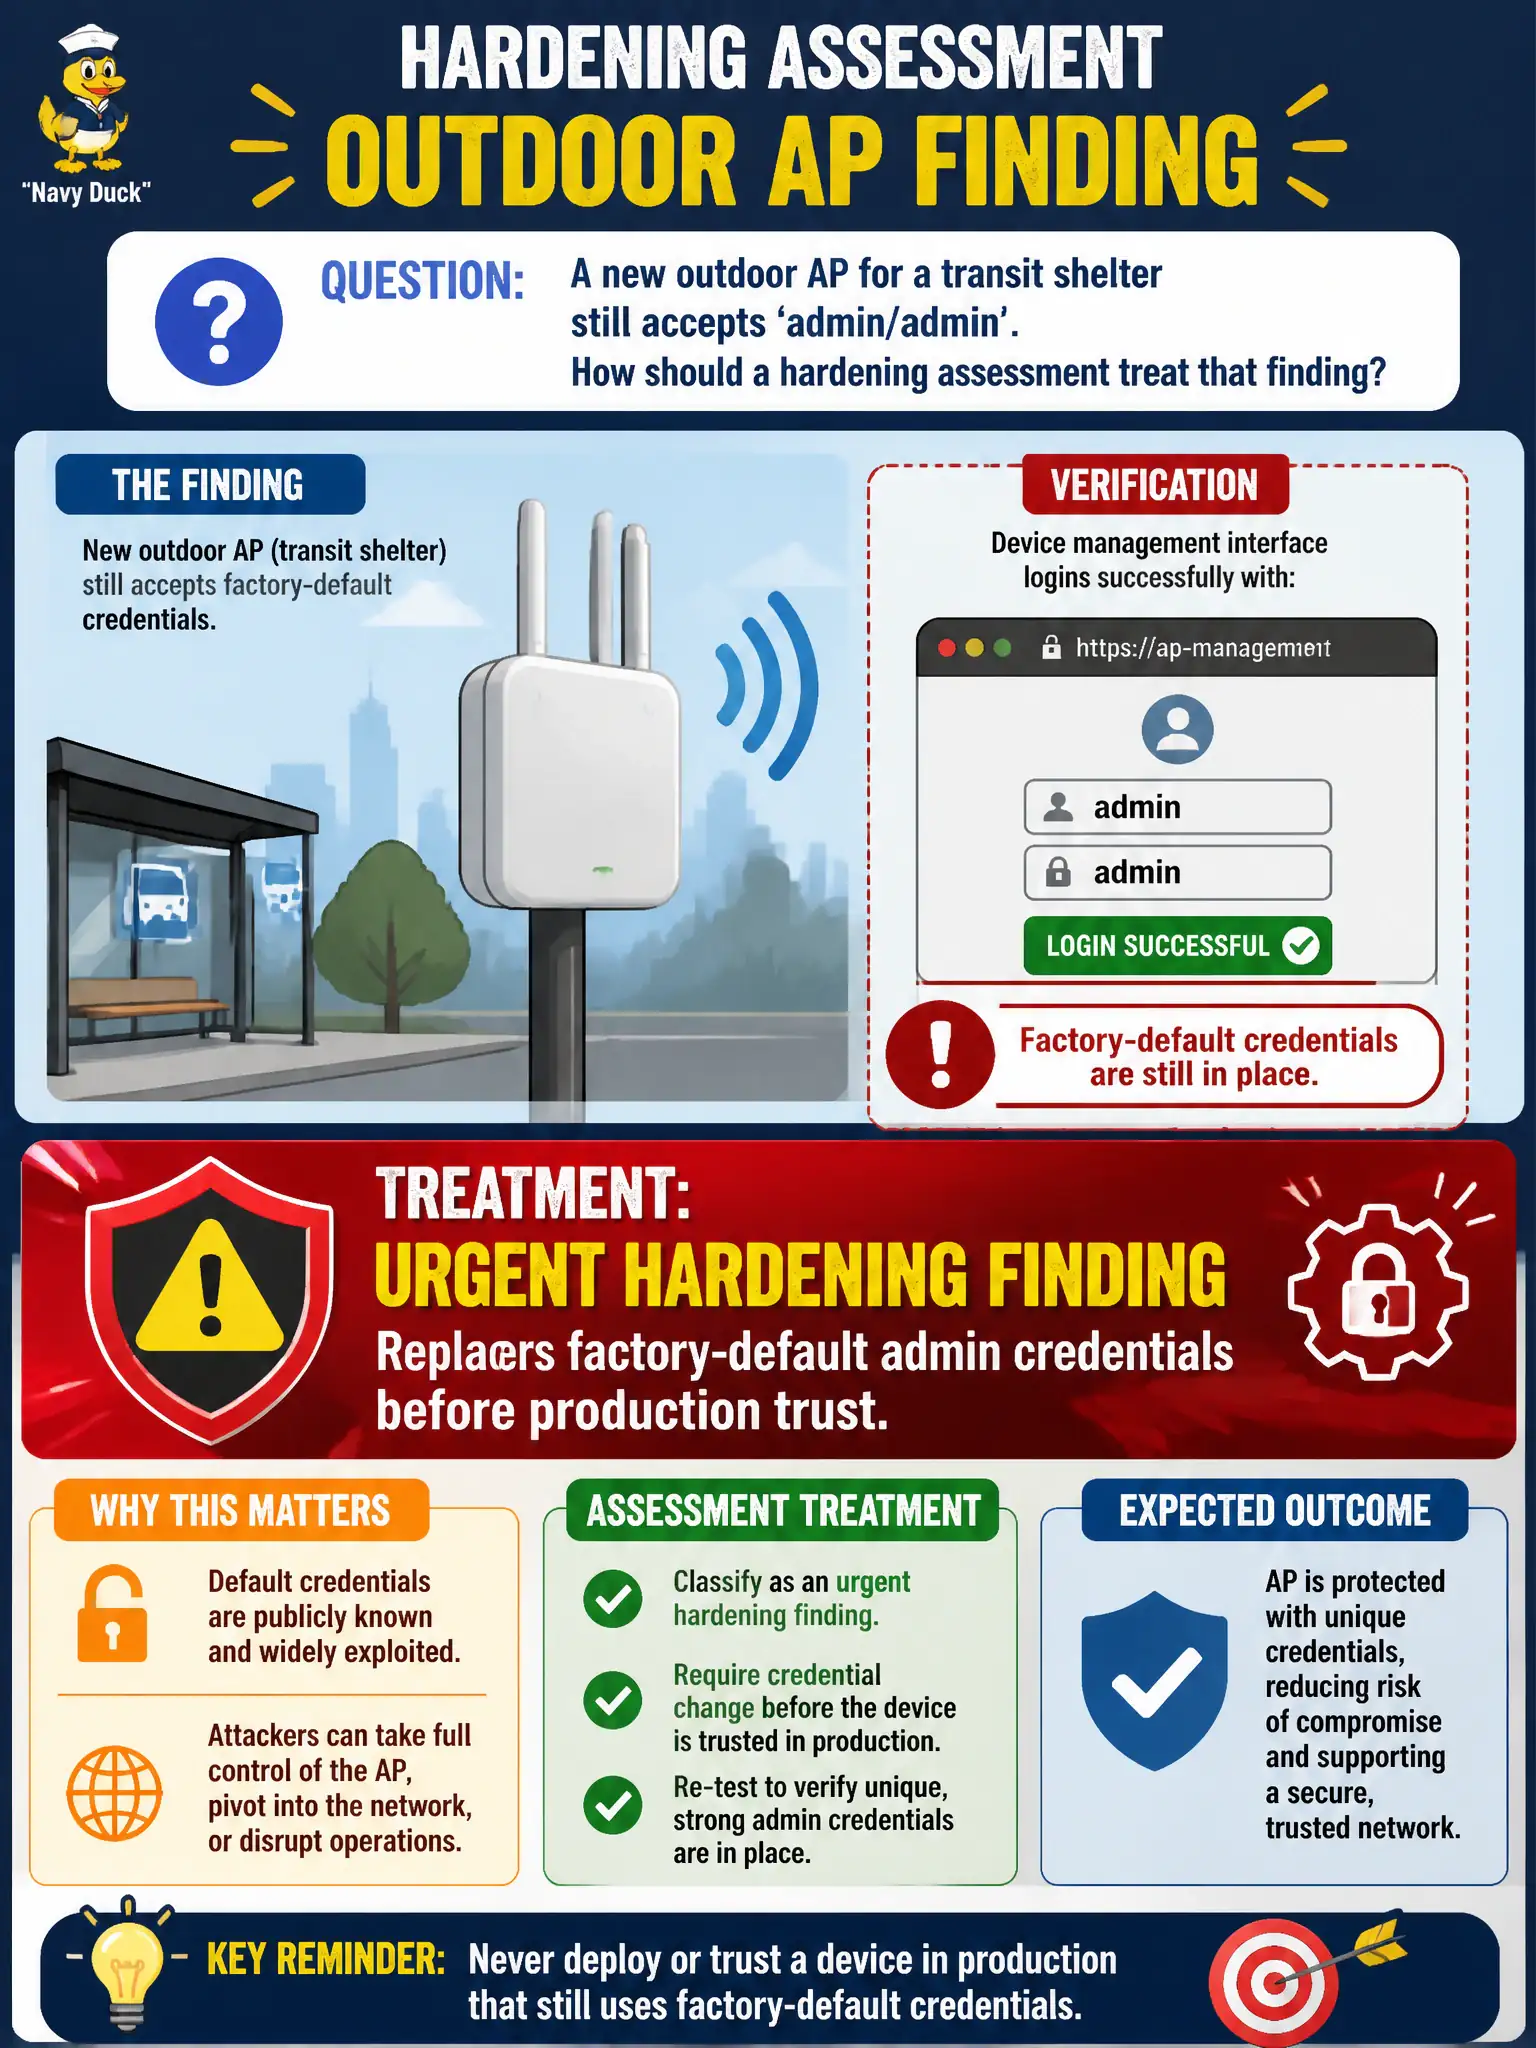
A new outdoor AP for a transit shelter still accepts ‘admin/admin’. How should a hardening assessment treat that finding?
Select an answer to reveal the explanation.
Short Explanation
‘admin/admin’ on a live outdoor AP is a fire alarm, not a sticky note. Client-side WPA3 does not forgive a wide-open management login on city transit gear.
Full Explanation
Factory-default credentials such as 'admin/admin' on outdoor APs deployed in transit shelters represent a critical security risk that must be addressed before production use. These default usernames and passwords are publicly documented and commonly exploited by attackers to gain full administrative control over devices. The correct response is to treat this as an urgent hardening finding and replace the default credentials with strong, unique passwords prior to trusting the device on the network. Considering factory defaults as merely informational ignores the real threat; attackers often scan for devices with default credentials to launch attacks. Assuming low priority because the AP is physically sealed is flawed because physical security controls can be bypassed, and remote attacks remain possible if the device is reachable over the network. Relying on WPA3 on the client SSID does not mitigate the risk of administrative compromise; client authentication does not protect the management interface. A key caveat is that credential changes must be managed securely and documented to prevent lockouts. Operationally, administrators should attempt to log in using default credentials to confirm remediation and ensure that only authorized personnel have access to the management interface with strong passwords.